# Welcome to OpusDNS
OpusDNS is a modern domain wholesale platform built for registrars, hosting
providers, and anyone who manages domains at scale. Our API gives you
programmatic control over the full domain lifecycle — from availability checks
and registration to DNS management, forwarding, and automated renewals.
## What you can do with the API
| Capability | Description |
| --- | --- |
| **Domain management** | Register, transfer, renew, and delete domains across hundreds of TLDs. |
| **DNS hosting** | Create zones, manage records, and enable DNSSEC — all through a single API. |
| **Domain & email forwarding** | Set up HTTP redirects and email aliases with built-in analytics. |
| **Batch operations** | Submit bulk commands and let OpusDNS process them asynchronously. |
| **Events & polling** | Track every change to your domains in real time through the event stream. |
## Environments
OpusDNS provides two environments. Use the sandbox for development and testing
— it's completely isolated from production and free to use.
The sandbox environment is completely free — no charges apply for any operations, including domain registrations and transfers.
| Environment | API base URL | Dashboard |
| --- | --- | --- |
| **Production** | `https://api.opusdns.com` | [app.opusdns.com](https://app.opusdns.com) |
| **Sandbox** | `https://sandbox.opusdns.com` | [app.sandbox.opusdns.com](https://app.sandbox.opusdns.com) |
## Resource IDs
The API uses [TypeIDs](https://github.com/jetify-com/typeid) — type-safe,
globally unique identifiers inspired by Stripe IDs. Every resource ID includes
a human-readable prefix that tells you what kind of resource it belongs to:
```
domain_01jxe1zw90f1t8vgpyfns8qwk1
user_01jxe1z8atfxpabknqbzhkvr3s
organization_01jxe20q5hf9p4bm3kfz7v0w6t
```
This makes debugging easier — you can immediately tell whether you're looking
at a domain, a user, or an organization, without needing to check the context.
Libraries are available for
[many languages](https://github.com/jetify-com/typeid?tab=readme-ov-file#official-implementations-by-jetify)
to work with TypeIDs natively.
## SDKs and tools
We maintain official client libraries and integrations:
- [**OpusDNS Go Client**](https://github.com/OpusDNS/opusdns-go-client) — full
Go client covering every API endpoint.
Check [our GitHub](https://github.com/OpusDNS/) for the latest SDKs, plugins,
and open-source tooling.
## Getting help
- [**Support**](mailto:support@opusdns.com) — open a ticket for any API or
integration questions.
- [**Knowledgebase**](https://help.opusdns.com/) — self-service guides and FAQs.
- [**Status**](https://status.opusdns.com/) — real-time platform availability.
# API Quickstart
Get up and running with the OpusDNS API in under five minutes. By the end of
this guide you'll have made your first authenticated request and confirmed
that your credentials work.
## 1. Create your account
If you don't have an account yet, sign up at
[app.opusdns.com/signup](https://app.opusdns.com/signup). For testing, create
a separate sandbox account at
[app.sandbox.opusdns.com](https://app.sandbox.opusdns.com) — the sandbox is
free and completely isolated from production.
## 2. Generate an API key
Open the dashboard and navigate to
[API Credentials](https://app.opusdns.com/developer/api-credentials). Create a
new credential, then copy and store the API key securely.
Your API key and client secret are only displayed once at creation time. Copy them immediately — they cannot be retrieved later.
## 3. Set up your environment
Export your API key and base URL so the examples below work out of the box:
```bash
export OPUSDNS_API_BASE="https://sandbox.opusdns.com"
export OPUSDNS_API_KEY="opk_your_api_key_here"
```
## 4. Make your first request
Verify your credentials by listing domains on your account:
```bash
curl "$OPUSDNS_API_BASE/v1/domains?page=1&page_size=10" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
A successful response returns a JSON array of domains (or an empty array if
your account is new):
```json
{
"items": [],
"total": 0,
"page": 1,
"page_size": 10
}
```
## 5. Check domain availability
Now try checking whether a domain is available for registration:
```bash
curl --get "$OPUSDNS_API_BASE/v1/domains/check" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "domains=example.com" \
--data-urlencode "domains=example.net"
```
The response contains one result per domain with `available`, `reason`,
`is_premium`, and optional `claims_key` or `premium_pricing` fields.
## 6. Register a domain
Once you've found an available domain, register it:
```bash
curl "$OPUSDNS_API_BASE/v1/domains" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "my-new-domain.com",
"contacts": {
"registrant": "contact_01jxe1z8atfxpabknqbzhkvr3s",
"admin": "contact_01jxe1z8atfxpabknqbzhkvr3s",
"tech": "contact_01jxe1z8atfxpabknqbzhkvr3s",
"billing": "contact_01jxe1z8atfxpabknqbzhkvr3s"
},
"renewal_mode": "renew",
"period": {
"unit": "y",
"value": 1
},
"nameservers": [
{ "hostname": "ns1.opusdns.com" },
{ "hostname": "ns2.opusdns.net" }
],
"create_zone": true
}'
```
In the sandbox, domain registrations are simulated — no real domains are created and no charges apply.
## Next steps
- [Authentication](/introduction/authentication) — learn about OAuth tokens
and when to use them.
- [Register a domain](/products/domains/register) — full registration guide
with contacts, nameservers, and TLD-specific attributes.
- [Transfer a domain](/products/domains/transfer) — move existing domains to
OpusDNS.
- [API Reference](/api-reference) — browse every endpoint.
# Authentication
OpusDNS supports two ways to authenticate API requests: API keys for direct
server-to-server calls, and OAuth tokens for applications that prefer
short-lived bearer tokens.
## API key authentication
API keys are the simplest way to authenticate. Send your key in the
`X-Api-Key` header with every request:
```http
GET /v1/domains HTTP/1.1
Host: api.opusdns.com
X-Api-Key: opk_your_full_api_key_here
```
Or with curl:
```bash
curl "$OPUSDNS_API_BASE/v1/domains" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Creating an API key
1. Open the OpusDNS Dashboard and navigate to
[API Credentials](https://app.opusdns.com/developer/api-credentials).
2. Click **Create API Credential**.
3. Give the credential a name and description, then choose an expiration date.
4. Select the **role** that governs what the key can do — a built-in role (such
as `admin` or `viewer`) or one of your organization's custom roles. The role
defaults to `admin` (full access). See
[Roles & permissions](/account/organizations/roles) for what each role
grants.
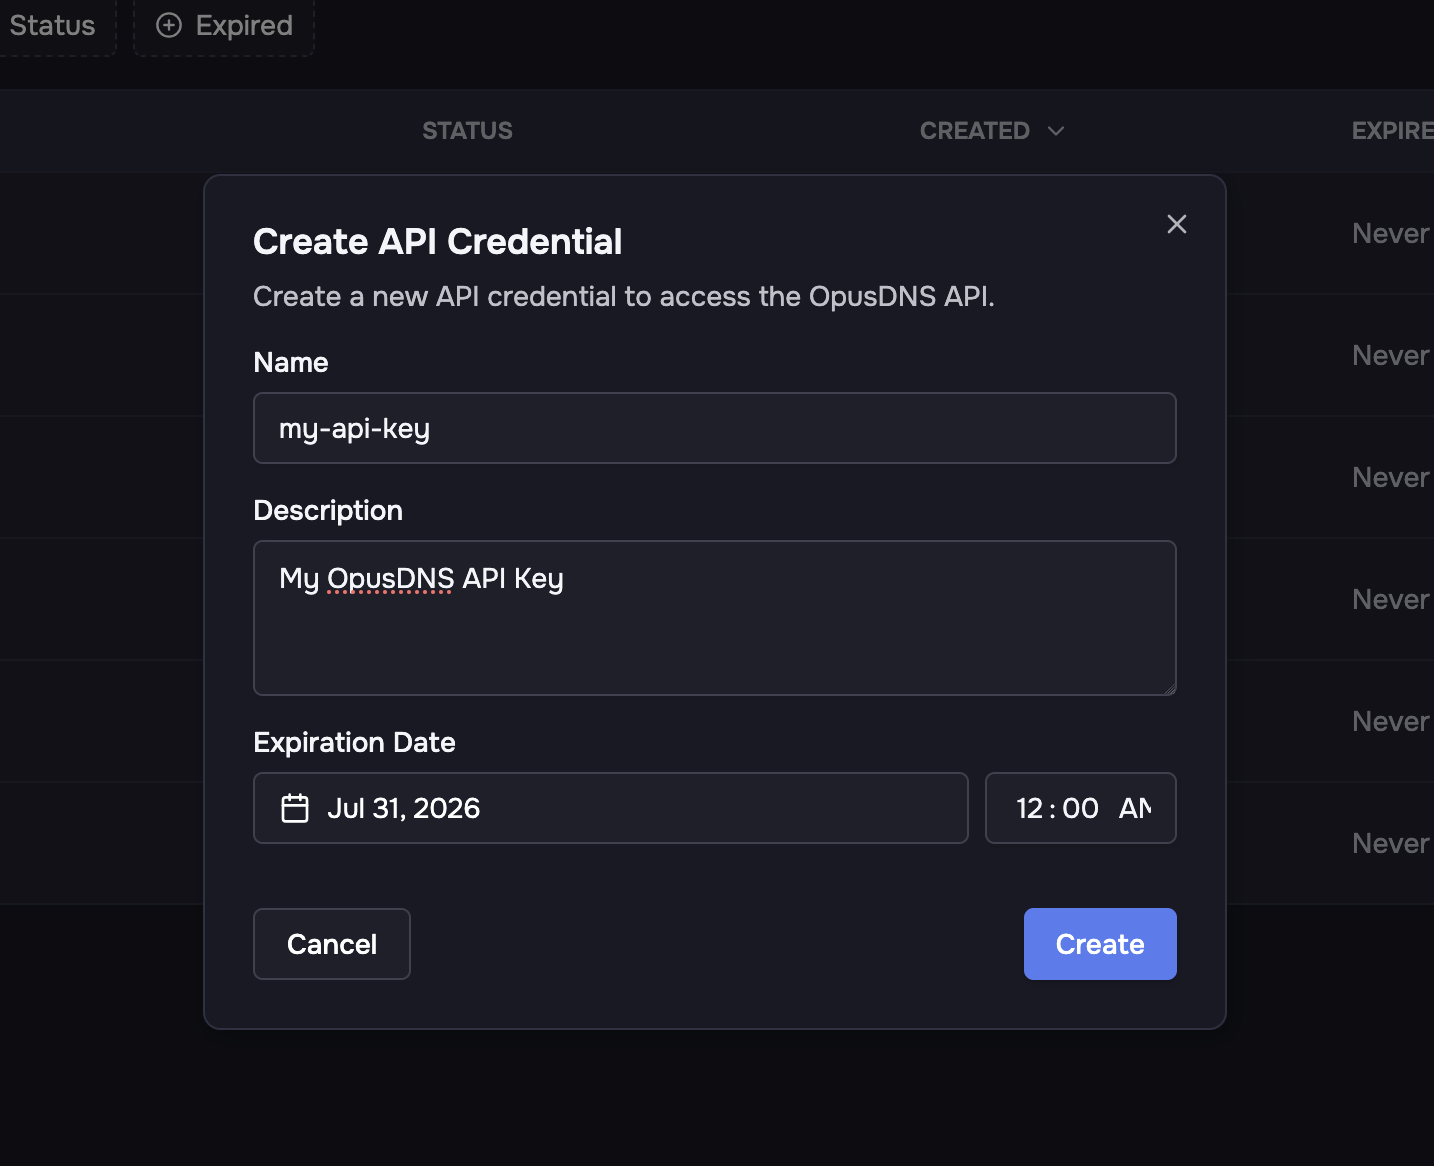
After creation, copy the **client ID**, **API key**, and **client secret**
immediately. The API key and client secret are only displayed once — they
cannot be retrieved later.
An API key carries its own role, independently of the user who created it. Grant each key the narrowest role it needs — for example, a deployment script that only edits DNS can use a key with the `dns_manager` role instead of `admin`.
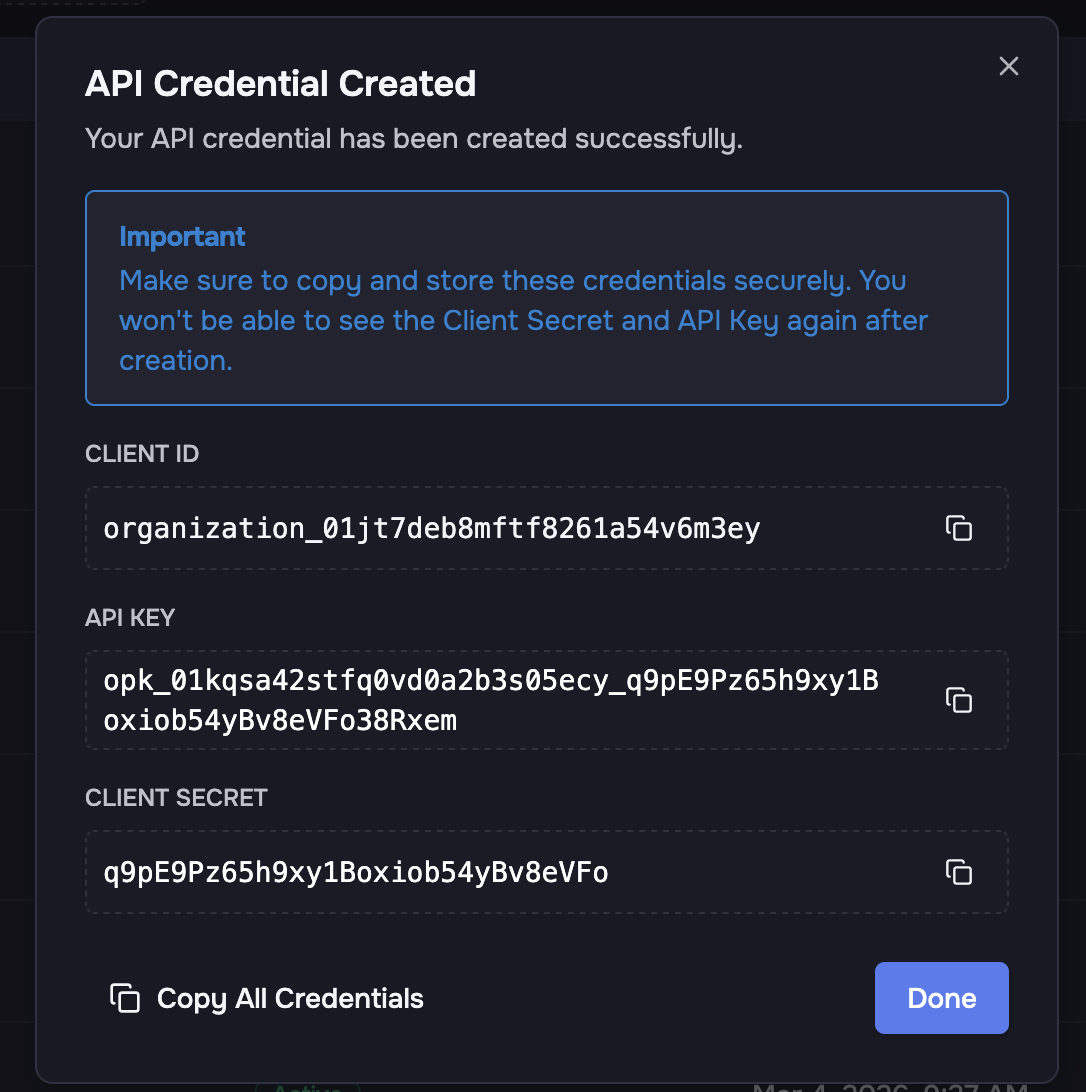 Store credentials in a secrets manager or environment variables. Never commit them to source control. The API key and client secret are shown only once and cannot be retrieved later.
## OAuth token authentication
If your platform prefers standard OAuth-style bearer tokens, you can exchange
your client credentials for a short-lived access token.
### Request a token
The token endpoint accepts both `application/x-www-form-urlencoded` (per the
OAuth 2.0 spec) and `application/json`.
**Form-encoded:**
```bash
curl "$OPUSDNS_API_BASE/v1/auth/token" \
--request POST \
--header "Content-Type: application/x-www-form-urlencoded" \
--data "grant_type=client_credentials&client_id=organization_01jxe20q5hf9p4bm3kfz7v0w6t&client_secret=your_client_secret"
```
**JSON:**
```bash
curl "$OPUSDNS_API_BASE/v1/auth/token" \
--request POST \
--header "Content-Type: application/json" \
--data '{
"grant_type": "client_credentials",
"client_id": "organization_01jxe20q5hf9p4bm3kfz7v0w6t",
"client_secret": "your_client_secret"
}'
```
### Token response
A successful request returns a bearer token with an expiry:
```json
{
"access_token": "eyJ...",
"token_type": "Bearer",
"expires_in": 3600
}
```
### Use the token
Send the token in the `Authorization` header:
```bash
curl "$OPUSDNS_API_BASE/v1/domains" \
--header "Authorization: Bearer eyJ..."
```
### When to use OAuth tokens
- Your HTTP tooling expects `Authorization: Bearer ...` headers.
- You want short-lived tokens instead of sending a long-lived API key on every
request.
- Your platform already implements OAuth client credentials flows.
For most server-to-server integrations, **API keys are simpler and
recommended**. Use OAuth tokens when your architecture specifically benefits
from short-lived, rotatable credentials.
# Upcoming changes
Planned changes to the OpusDNS API that you can prepare for — and, where
available, opt into — before they become the default.
- [Timezone-aware datetimes (RFC 3339)](/upcoming-changes/rfc3339-datetimes) —
datetime fields on the public `/v1` API gain an explicit UTC `Z` designator.
Opt in today with the `X-Datetime-Format: rfc3339` header; the new format
becomes the default per environment on a staged schedule.
# Timezone-aware datetimes (RFC 3339)
The public `/v1` API is standardizing datetime fields on **RFC 3339** with an explicit UTC designator. You can opt in today with a request header, and the new format becomes the default on a staged schedule per environment.
**The cutover is complete.** Sandbox switched to the tz-aware default on 2026-08-18 and production on 2026-09-02. Every environment now serves RFC 3339 datetimes by default; the header below is accepted but no longer changes anything.
## What is changing
All datetimes the API returns represent UTC instants. Today most fields are serialized without a timezone marker; the new format appends `Z`.
**Before:**
```json
{
"domain": "example.com",
"registered_on": "2026-01-15T09:30:00",
"expires_on": "2027-01-15T09:30:00"
}
```
**After:**
```json
{
"domain": "example.com",
"registered_on": "2026-01-15T09:30:00Z",
"expires_on": "2027-01-15T09:30:00Z"
}
```
The values represent the same instants — only the serialization gains the `Z`.
## Why it matters
The naive form (no `Z`, no offset) is not valid RFC 3339 and is **parsed as local time** by several clients. The most common pitfall is JavaScript:
```js
// Response value: "2026-01-15T09:30:00"
new Date("2026-01-15T09:30:00");
// → interpreted in the browser's local timezone, NOT UTC.
// A viewer at UTC-5 sees 09:30 rendered as if it were 09:30 local — a 5-hour error.
// New format: "2026-01-15T09:30:00Z"
new Date("2026-01-15T09:30:00Z");
// → correctly parsed as the UTC instant.
```
Strict RFC 3339 parsers in other languages reject the naive form outright. This is the root cause behind mismatched expiry dates and off-by-hours timestamps in integrations.
## Opt in today
Send this header on any public `/v1` request:
```plaintext
X-Datetime-Format: rfc3339
```
Every datetime in the response is normalized to UTC and serialized with a trailing `Z`. The header:
* affects only the request it is sent on (no account-level state),
* is the exact value `rfc3339` (any other value, or an absent header, keeps today's behavior until the default cutover),
* remains valid forever — after cutover it is a no-op and never returns an error.
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "X-Datetime-Format: rfc3339"
```
Point `$OPUSDNS_API_BASE` at `https://api.opusdns.com` for production. Adding this header is a non-breaking change.
## Migration guidance
1. **Parse `Z` correctly.** Ensure your datetime library treats the trailing `Z` as UTC. Most standard libraries do this natively.
2. **JavaScript:** if you currently compensate for `new Date()` local-time parsing (for example, manually appending `Z`, or subtracting an offset), remove that workaround when you adopt the header — the response already carries `Z`.
3. **Test end to end** with the header before your environment's cutover date, then remove any bespoke naive-datetime handling.
4. **Storage and display:** confirm downstream storage and UI render the corrected instant, not a double-shifted value.
## Cutover schedule
On these dates the tz-aware format becomes the default per environment; no header is required. The header keeps working after cutover and simply becomes a no-op (it is always accepted and never causes an error). Adopt the header before your target date so the switch is a no-op for you.
| Environment | Default cutover date | Status |
| ----------- | --------------------- | --------- |
| Sandbox | Tuesday, 2026-08-18 | Completed |
| Production | Wednesday, 2026-09-02 | Completed |
Both environments serve tz-aware datetimes by default. The header is still accepted everywhere and is a no-op.
## Scope
* Applies to public `/v1` endpoints.
* Jobs, reports, and RDAP endpoints already return tz-aware datetimes and are unchanged.
## Rollback and exceptions
If the cutover causes problems for your integration, we can revert the default for an environment quickly, and we can evaluate a per-account exception on request. If you need either — or more time to migrate — contact us **before** your environment's cutover date at .
# Organizations
OpusDNS uses a two-level organization model. Your account is the **parent
organization**, and you can create **suborganizations** beneath it — one for
each customer, department, or business unit you manage.
## How organizations work
### Parent and suborganizations
When you sign up for OpusDNS, you get a parent organization. This is your
reseller account — it holds your billing plan, account balance, and API
credentials. Underneath it, you create suborganizations to separate and
manage different portfolios:
```
Your Reseller Account (parent organization)
├── Customer A (suborganization)
├── Customer B (suborganization)
├── Customer C (suborganization)
└── Internal Domains (suborganization)
```
The structure is flat — suborganizations sit directly under the parent. There
are no sub-suborganizations.
The organization structure is strictly two-level. You cannot nest suborganizations within other suborganizations.
### What's isolated
Each suborganization has its own:
- **Domains** — registered and managed independently.
- **DNS zones** — zones and records are scoped to the suborganization.
- **Users** — each user belongs to exactly one organization.
- **Contacts** — contacts are per-organization.
- **Settings** — custom attributes, locale, and configuration.
### Billing: consolidated or independent
Each suborganization has one of two **billing modes**, chosen at creation and
permanent thereafter:
- **Consolidated** (default) — billing flows through the parent. When the
suborganization registers a domain, renews, or uses any paid service, the
cost is charged to the parent organization's account balance. Consolidated
suborganizations don't have their own payment methods — the parent pays for
everything. This is the classic reseller model: all charges consolidate on
your single reseller account.
- **Independent** — the suborganization is its own billing customer, with its
own account balance, payment methods, and invoices. Its charges never touch
the parent's balance. Ideal when a suborganization is a separate legal
entity that pays for itself. Available on request: contact support to have
it enabled for your organization.
See [Billing modes](/account/organizations/manage#billing-modes) for how to
create each kind, and [Billing & transactions](/account/organizations/billing)
for tracking spending.
Charges from **consolidated** suborganizations are billed to the parent organization — monitor your account balance to prevent failed operations. **Independent** suborganizations fund themselves: a spending problem there fails their operations, not yours.
### Users and access
Users belong to exactly one organization — either the parent or a specific
suborganization. A user in the parent organization can manage
suborganizations and their resources. A user in a suborganization can only
access that suborganization's resources.
```
Your Reseller Account
├── Admin User (full access to parent + all suborganizations)
├── Billing User (manages invoices and transactions)
│
├── Customer A
│ ├── Customer A Admin (manages Customer A's domains only)
│ └── Customer A Tech (manages Customer A's DNS only)
│
└── Customer B
└── Customer B Admin (manages Customer B's domains only)
```
When creating a suborganization, you can provision users for it in the same
request. You can also create users later via the
[User management](/account/users) API.
## Organization statuses
| Status | Description |
| --- | --- |
| `active` | Organization is operational. |
| `inactive` | Organization is disabled — domains and services are frozen. |
## Roles
Roles determine what permissions users and API keys have within an organization
— through built-in roles or your own custom roles. See
[Roles & permissions](/account/organizations/roles) for the full guide, and
[User management](/account/users) for how to assign a role to a user.
## Related API Reference
- [`POST /v1/organizations`](/api-reference#tag/organization/POST/v1/organizations)
- [`GET /v1/organizations`](/api-reference#tag/organization/GET/v1/organizations)
- [`GET /v1/organizations/{organization_id}`](/api-reference#tag/organization/GET/v1/organizations/{organization_id})
- [`PATCH /v1/organizations/{organization_id}`](/api-reference#tag/organization/PATCH/v1/organizations/{organization_id})
- [`GET /v1/organizations/roles`](/api-reference#tag/organization/GET/v1/organizations/roles)
# Roles & permissions
Roles control what each user and API key can do inside an organization. A role
is a named bundle of **permissions**, and every permission grants a single
**scope** on a single **resource**. OpusDNS ships a set of **built-in roles**
that cover the most common needs, and you can define your own **custom roles**
when you need a more specific set of permissions.
Roles are scoped to an organization. A user or API key in a suborganization can
only ever hold a role defined in — and limited to — that suborganization.
## Permissions
A permission is written as a `resource:scope` string, for example
`domains:read` or `dns:manage`. The scope describes what level of access the
permission grants:
| Scope | Grants |
| --- | --- |
| `read` | View resources of this type (list and get). |
| `manage` | Create and update resources of this type. |
| `delete` | Delete resources of this type. |
Permissions exist for each resource area of the API:
`organization`, `domains`, `contacts`, `dns`, `hosts`, `email_forwards`,
`domain_forwards`, `parking`, `events`, `jobs`, `billing`, `users`, `api_keys`,
`registrar_credentials`, `tags`, `audit_logs`
To retrieve the exact catalog of permissions a custom role may grant, call:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/role-permissions" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
```json
{
"permissions": [
"audit_logs:read",
"billing:manage",
"billing:read",
"contacts:delete",
"contacts:manage",
"contacts:read",
"dns:delete",
"dns:manage",
"dns:read",
"domains:delete",
"domains:manage",
"domains:read"
]
}
```
## Built-in roles
Built-in roles are maintained by OpusDNS and are available in every
organization. They are immutable — you cannot change or delete them.
| Role | What it grants |
| --- | --- |
| `owner` | Full access. The organization's first user / super-admin. Report-only — see below. |
| `admin` | Full access to every resource in the organization. |
| `viewer` | Read-only access across domains, DNS, contacts, hosts, forwarding, parking, events, jobs, and users. |
| `domain_manager` | Full access (read/manage/delete) to domains, DNS, contacts, hosts, email & domain forwarding, parking, events, and jobs. |
| `dns_manager` | Full access to DNS zones, email forwarding, and domain forwarding. |
| `billing_manager` | Read and manage billing. |
`owner` is **report-only**. It identifies the organization's first user and is never assigned through the role API — it is established when the organization is created. The remaining built-in roles are freely assignable.
## Custom roles
When the built-in roles don't fit, create a custom role with exactly the
permissions you need. Custom roles are owned by your organization.
Each custom role has a **label** — a `snake_case` identifier derived from its
display name (for example, the name `Support Staff` produces the label
`support_staff`). The label is unique within the organization and is used as the
URL path parameter for the role.
Custom roles cannot grant the escalation-bearing `admin` or `owner` permissions. Use the built-in `admin` role when full access is required.
### Listing roles
List every role assignable in the organization — the built-in roles plus your
custom roles:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/roles" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
```json
[
{
"label": "admin",
"name": "Admin",
"description": "Full access to the organization.",
"built_in": true,
"permissions": ["organization:manage", "domains:manage", "dns:manage"]
},
{
"label": "support_staff",
"name": "Support Staff",
"description": "Read domains and manage DNS.",
"built_in": false,
"permissions": ["domains:read", "dns:manage"],
"created_on": "2026-06-16T10:00:00Z",
"updated_on": "2026-06-16T10:00:00Z"
}
]
```
### Creating a custom role
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/roles" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "Support Staff",
"description": "Read domains and manage DNS.",
"permissions": ["domains:read", "dns:manage"]
}'
```
| Field | Required | Description |
| --- | --- | --- |
| `name` | Yes | Display name (1–64 chars). The label is derived from this. |
| `description` | No | Free-text description of the role. |
| `permissions` | Yes | List of `resource:scope` strings the role grants. |
The response is the created role, including its generated `label`:
```json
{
"label": "support_staff",
"name": "Support Staff",
"description": "Read domains and manage DNS.",
"built_in": false,
"permissions": ["dns:manage", "domains:read"],
"created_on": "2026-06-16T10:00:00Z",
"updated_on": "2026-06-16T10:00:00Z"
}
```
A name that resolves to a built-in role label, or a duplicate name within the
organization, returns `409 Conflict`.
### Getting a single role
Retrieve any role — built-in or custom — by its label:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/roles/support_staff" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Updating a custom role
Update a custom role's name, description, and/or permissions. Provide only the
fields you want to change. When `permissions` is included it is a **full
replacement** of the role's permission set.
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/roles/support_staff" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"permissions": ["domains:read", "dns:manage", "dns:delete"]
}'
```
Permission changes take effect immediately for every user and API key that holds the role. Built-in roles are immutable and return `409 Conflict` if you attempt to update them.
### Deleting a custom role
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/roles/support_staff" \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
A role cannot be deleted while it is still assigned to any user or API key — reassign those subjects first, or the request returns `409 Conflict`. Built-in roles cannot be deleted.
## Assigning roles
Roles are granted per subject:
- **Users** — assign a role with the
[User management](/account/users) role endpoints.
- **API keys** — every API key carries its own role, granted when the key is
issued (defaulting to `admin`, full access). A key's role governs its
permissions exactly like a user's role, and applies independently of the user
who created the key. Choose or change a key's role from the **API Credentials**
page of the [OpusDNS Dashboard](https://app.opusdns.com/developer/api-credentials).
Grant each key the narrowest role it needs.
You can assign either a built-in role (by name, for example `viewer`) or a
custom role (by its label, for example `support_staff`).
## Related API Reference
- [`GET /v1/organizations/roles`](/api-reference#tag/organization/GET/v1/organizations/roles)
- [`POST /v1/organizations/roles`](/api-reference#tag/organization/POST/v1/organizations/roles)
- [`GET /v1/organizations/role-permissions`](/api-reference#tag/organization/GET/v1/organizations/role-permissions)
- [`GET /v1/organizations/roles/{label}`](/api-reference#tag/organization/GET/v1/organizations/roles/{label})
- [`PATCH /v1/organizations/roles/{label}`](/api-reference#tag/organization/PATCH/v1/organizations/roles/{label})
- [`DELETE /v1/organizations/roles/{label}`](/api-reference#tag/organization/DELETE/v1/organizations/roles/{label})
# Manage suborganizations
Create, list, inspect, and update suborganizations under your parent organization.
## Creating a suborganization
```bash
curl "$OPUSDNS_API_BASE/v1/organizations" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "Customer A",
"country_code": "DE",
"city": "Berlin",
"address_1": "Friedrichstraße 123",
"postal_code": "10117",
"currency": "EUR",
"default_locale": "de"
}'
```
### Organization fields
| Field | Required | Description |
| ----------------- | -------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `name` | Yes | Display name for the organization. |
| `billing_mode` | No | `consolidated` (default) or `independent` — see [Billing modes](#billing-modes). `independent` requires approval for your organization. **Cannot be changed after creation.** |
| `country_code` | No | ISO 3166-1 alpha-2 country code. |
| `city` | No | City. |
| `address_1` | No | First line of the street address. |
| `address_2` | No | Second line of the street address. |
| `postal_code` | No | Postal or ZIP code. |
| `state` | No | State or province. |
| `currency` | No | Default currency for billing. |
| `default_locale` | No | Preferred locale for the organization. |
| `business_number` | No | Business registration number. |
| `tax_id` | No | Tax identification number (e.g., VAT ID). |
| `tax_id_type` | No | Type of tax ID. |
| `tax_rate` | No | Tax rate applied to transactions. |
| `attributes` | No | Custom key-value attributes (see [Attributes](/account/organizations/attributes)). |
| `users` | No | Users to create in the new organization. |
### Provisioning users at creation
You can create the suborganization and its initial users in a single request. Each user is scoped to the new organization — they have no visibility into the parent or other suborganizations:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "Customer A",
"country_code": "DE",
"city": "Berlin",
"address_1": "Friedrichstraße 123",
"postal_code": "10117",
"currency": "EUR",
"users": [
{
"username": "customer-a-admin",
"email": "admin@customer-a.com",
"first_name": "Alice",
"last_name": "Admin",
"locale": "de_DE"
},
{
"username": "customer-a-tech",
"email": "tech@customer-a.com",
"first_name": "Bob",
"last_name": "Tech",
"locale": "de_DE"
}
]
}'
```
Each user requires `username`, `email`, `first_name`, `last_name`, and `locale` (underscore form, e.g. `en_US`). The **first user in the list becomes the organization's owner**; subsequent users are created as admins.
You can add more users later with the [User management](/account/users) API.
## Billing modes
Every suborganization is created in one of two billing modes, set with the `billing_mode` field on the create request:
| | `consolidated` (default) | `independent` |
| ------------------------ | -------------------------------- | -------------------------------------------- |
| Charges & invoices | Roll up to your (parent) account | The suborganization's own account |
| Wallet & payment methods | Yours | Its own wallet, balance, and payment methods |
| Extra required fields | None | `currency`, `country_code` |
**Independent billing is enabled per organization.** Creating a suborganization with `billing_mode: "independent"` is available to top-level organizations that have been approved for the feature; until then the request is rejected with `422 ERROR_INDEPENDENT_BILLING_NOT_APPROVED`. Contact [](mailto:support@opusdns.com) if you would like more information about this feature or to have it enabled.
**`billing_mode` is permanent.** It cannot be changed after creation — an update request that includes `billing_mode` is rejected. Choose deliberately; converting an organization between modes means deleting and recreating it.
### Creating an independent suborganization
```bash
curl "$OPUSDNS_API_BASE/v1/organizations" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "Customer B (self-billed)",
"billing_mode": "independent",
"currency": "EUR",
"country_code": "DE",
"address_1": "Friedrichstraße 123",
"city": "Berlin",
"postal_code": "10117",
"tax_id": "DE123456789",
"users": [
{
"username": "customer-b-owner",
"email": "billing@customer-b.example",
"first_name": "Carol",
"last_name": "Owner",
"locale": "de_DE"
}
]
}'
```
Requirements and behavior:
* **`currency`** is required and must be `EUR` or `USD`. It becomes the organization's billing currency permanently.
* **`country_code`** is required.
* A **billing contact** is needed: the first user in `users[]` is used if present, otherwise your parent organization's owner. Include a full street address at creation — it is required later for checkout and balance top-ups.
* Provisioning is **synchronous and all-or-nothing**: a successful response means the organization's billing account, wallet, and payment setup all exist. If anything fails, nothing is created.
* New independent suborganizations start on **prepaid** terms. Contact support to arrange different payment terms.
### Errors
| HTTP | Error code | Meaning |
| ---- | ---------------------------------------------- | ------------------------------------------------------------------------------------------------------------------------ |
| 422 | `ERROR_INDEPENDENT_BILLING_NOT_APPROVED` | Your organization has not been enabled for independent billing. Contact . |
| 422 | `ERROR_INDEPENDENT_BILLING_NOT_ALLOWED` | Independent billing is only available for suborganizations created directly under your top-level (billing) organization. |
| 422 | `ERROR_INDEPENDENT_BILLING_ATTRIBUTES_INVALID` | `currency` or `country_code` missing or invalid — the response lists every problem in `invalid_fields`. |
| 422 | `ERROR_INDEPENDENT_BILLING_CONTACT_NOT_FOUND` | No billing contact could be resolved — include a user in `users[]`. |
### Viewing an independent suborganization's billing
An independent suborganization sees its own invoices, transactions, and billing data through the normal billing endpoints. As the parent, you can view a suborganization's billing by sending its ID in the `X-Organization-Context` header on those same endpoints:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/organization_01h45.../transactions" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "X-Organization-Context: organization_01h46..."
```
For a consolidated view of spend across your whole organization tree — including independent suborganizations — a monthly **suborganization billing transactions report** is available via the [Reports API](/api-reference#tag/report): each row is one transaction, with columns for the organization that incurred it and the organization that was billed for it.
## Listing suborganizations
List all suborganizations under your current organization:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations?page=1&page_size=25" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Searching and filtering
```bash
curl --get "$OPUSDNS_API_BASE/v1/organizations" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "search=Customer" \
--data-urlencode "country_code=DE" \
--data-urlencode "sort_by=name" \
--data-urlencode "sort_order=asc"
```
| Parameter | Description |
| -------------- | ------------------------------------------------ |
| `search` | Search by organization name. |
| `country_code` | Filter by country code. |
| `sort_by` | Sort by `created_on`, `name`, or `country_code`. |
| `sort_order` | `asc` or `desc`. |
| `page` | Page number (default: 1). |
| `page_size` | Results per page (default: 10, max: 1000). |
## Getting organization details
Retrieve full details including billing data, active plan, and users:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/organization_01h45ytscbebyvny4gc8cr8ma2" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
```json
{
"organization_id": "organization_01h45ytscbebyvny4gc8cr8ma2",
"name": "Customer A",
"status": "active",
"country_code": "DE",
"parent_organization_id": "organization_01h35xrscbebyvny4gc8cr8ma2",
"account_balance": 150.00,
"active_plan": {
"plan_id": "plan_01h45ytscbebyvny4gc8cr8ma2",
"name": "Professional",
"plan_level": 2,
"amount": 29.99,
"currency": "EUR"
},
"billing_metadata": {
"billing_model": "prepaid",
"credit_limit": 500.00,
"customer_number": "CUST-00123"
},
"users": [
{
"user_id": "user_01h45ytscbebyvny4gc8cr8ma2",
"username": "customer-a-admin",
"email": "admin@customer-a.com",
"status": "active"
}
],
"created_on": "2026-01-15T10:00:00Z"
}
```
### Response fields
| Field | Description |
| ------------------------ | ------------------------------------------------------------------------------------ |
| `organization_id` | Unique identifier. |
| `name` | Display name. |
| `status` | `active` or `inactive`. |
| `parent_organization_id` | The parent organization (your reseller account). |
| `account_balance` | Current account balance. |
| `active_plan` | The billing plan — includes plan ID, name, level, amount, and currency. |
| `billing_metadata` | Billing configuration — model (`prepaid`/`postpaid`), credit limit, customer number. |
| `users` | Users that belong to this organization. |
| `created_on` | When the organization was created. |
## Updating an organization
Update any field with a PATCH request. Only include the fields you want to change:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/organization_01h45ytscbebyvny4gc8cr8ma2" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "Customer A - Rebranded",
"city": "Munich",
"default_locale": "en"
}'
```
## Related API Reference
* [`POST /v1/organizations`](/api-reference#tag/organization/POST/v1/organizations)
* [`GET /v1/organizations`](/api-reference#tag/organization/GET/v1/organizations)
* [`GET /v1/organizations/{organization_id}`](/api-reference#tag/organization/GET/v1/organizations/%7Borganization_id%7D)
* [`PATCH /v1/organizations/{organization_id}`](/api-reference#tag/organization/PATCH/v1/organizations/%7Borganization_id%7D)
# Organization attributes
Attributes are custom key-value pairs you can attach to any organization.
Use them to store integration-specific metadata like CRM IDs, customer
tiers, internal notes, or any data your system needs to associate with an
organization.
## How attributes work
Each attribute has a `key` and `value`, plus two visibility flags:
| Field | Description |
| --- | --- |
| `key` | Unique identifier for the attribute within the organization. |
| `value` | The attribute value (string). |
| `private` | If `true`, the attribute is hidden from suborganizations. |
| `protected` | If `true`, the attribute is read-only and cannot be modified via the API. |
Private attributes are useful for storing internal metadata (like a customer
tier or internal notes) that suborganization users should not see. Protected
attributes are typically set by the system or an admin and should not be
changed programmatically.
## Listing attributes
### Current organization
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/attributes" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Specific organization
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/organization_01h45ytscbebyvny4gc8cr8ma2/attributes" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Filter by key
Retrieve only specific attributes by passing `keys[]`:
```bash
curl --get "$OPUSDNS_API_BASE/v1/organizations/attributes" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "keys=crm_id" \
--data-urlencode "keys=tier" \
--data-urlencode "keys=onboarding_status"
```
## Setting attributes
### On the current organization
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/attributes" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"attributes": [
{ "key": "crm_id", "value": "CRM-12345" },
{ "key": "tier", "value": "enterprise" },
{ "key": "internal_notes", "value": "VIP customer - priority support", "private": true }
]
}'
```
### On a specific organization
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/organization_01h45ytscbebyvny4gc8cr8ma2/attributes" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"attributes": [
{ "key": "crm_id", "value": "CRM-67890" },
{ "key": "tier", "value": "standard" }
]
}'
```
Attributes are upserted — if a key already exists, its value is updated. If
it doesn't exist, a new attribute is created.
## Use cases
### Map organizations to your CRM
Store your internal customer IDs alongside OpusDNS organizations:
```json
{ "key": "crm_id", "value": "CRM-12345" }
```
This lets you look up the OpusDNS organization for a given CRM customer
without maintaining a separate mapping table.
### Tag organizations by tier
Track service levels or pricing tiers:
```json
{ "key": "tier", "value": "enterprise" }
```
### Internal metadata
Store notes or flags that suborganization users should not see:
```json
{ "key": "internal_flag", "value": "review_pending", "private": true }
```
## Related API Reference
- [`GET /v1/organizations/attributes`](/api-reference#tag/organization/GET/v1/organizations/attributes)
- [`PATCH /v1/organizations/attributes`](/api-reference#tag/organization/PATCH/v1/organizations/attributes)
- [`GET /v1/organizations/{organization_id}/attributes`](/api-reference#tag/organization/GET/v1/organizations/{organization_id}/attributes)
- [`PATCH /v1/organizations/{organization_id}/attributes`](/api-reference#tag/organization/PATCH/v1/organizations/{organization_id}/attributes)
# IP restrictions
Restrict API access to specific IP addresses or CIDR ranges. When IP restrictions are enabled, requests from unauthorized networks are rejected — adding a security layer on top of API key authentication.
## How it works
IP restrictions are configured per organization. Once you add at least one restriction, only requests originating from an allowed network are accepted. Requests from any other IP address receive a `403 Forbidden` response.
Make sure to add all IP addresses your application uses before enabling restrictions. If you lock yourself out, contact [OpusDNS Support](mailto:support@opusdns.com) for assistance.
## Listing restrictions
View all currently configured IP restrictions:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/ip-restrictions" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Each restriction includes a `last_used_on` timestamp showing when a request last matched that rule — useful for identifying stale restrictions.
## Creating a restriction
Allow a specific IP range:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/ip-restrictions" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{ "ip_network": "203.0.113.0/24" }'
```
Single IP addresses are automatically normalized to `/32` (IPv4) or `/128` (IPv6). For example, submitting `203.0.113.10` is stored as `203.0.113.10/32`.
### Common patterns
**Allow a single server:**
```json
{ "ip_network": "203.0.113.10" }
```
**Allow a subnet:**
```json
{ "ip_network": "10.0.0.0/16" }
```
**Allow an IPv6 range:**
```json
{ "ip_network": "2001:db8::/32" }
```
## Getting a restriction
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/ip-restrictions/ip_restriction_01h45ytscbebyvny4gc8cr8ma2" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Updating a restriction
Change the allowed network range:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/ip-restrictions/ip_restriction_01h45ytscbebyvny4gc8cr8ma2" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{ "ip_network": "203.0.113.0/25" }'
```
## Deleting a restriction
Remove a restriction to stop allowing that network:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/ip-restrictions/ip_restriction_01h45ytscbebyvny4gc8cr8ma2" \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
If you delete the last restriction, IP filtering is effectively disabled and all networks are allowed again.
## Related API Reference
* [`GET /v1/organizations/ip-restrictions`](/api-reference#tag/organization/GET/v1/organizations/ip-restrictions)
* [`POST /v1/organizations/ip-restrictions`](/api-reference#tag/organization/POST/v1/organizations/ip-restrictions)
* [`GET /v1/organizations/ip-restrictions/{ip_restriction_id}`](/api-reference#tag/organization/GET/v1/organizations/ip-restrictions/%7Bip_restriction_id%7D)
* [`PATCH /v1/organizations/ip-restrictions/{ip_restriction_id}`](/api-reference#tag/organization/PATCH/v1/organizations/ip-restrictions/%7Bip_restriction_id%7D)
* [`DELETE /v1/organizations/ip-restrictions/{ip_restriction_id}`](/api-reference#tag/organization/DELETE/v1/organizations/ip-restrictions/%7Bip_restriction_id%7D)
# Billing & transactions
All OpusDNS charges — domain registrations, renewals, transfers, and
services — are billed to the parent organization's account balance.
When a suborganization performs a paid operation, the cost is deducted from
the parent's balance. Suborganizations do not have their own payment methods
or account balances.
For prepaid accounts, operations are rejected when the account balance is insufficient. Make sure to maintain adequate funds to avoid failed registrations or renewals.
## Invoices
List invoices for an organization:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/organization_01h45ytscbebyvny4gc8cr8ma2/billing/invoices?page=1&page_size=25" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Transactions
View the transaction history. Each transaction shows the amount, currency,
timestamp, and which operation triggered it:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/organization_01h45ytscbebyvny4gc8cr8ma2/transactions?page=1&page_size=25" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Transaction detail
Get full details for a specific transaction:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/organization_01h45ytscbebyvny4gc8cr8ma2/transactions/billing_transaction_01h45ytscbebyvny4gc8cr8ma2" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Pricing
Retrieve the product pricing that applies to an organization. This is
useful for displaying costs to your customers or validating expected prices
before submitting operations:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/organization_01h45ytscbebyvny4gc8cr8ma2/pricing/product-type/domain" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Billing metadata
Organization details include billing configuration in the
`billing_metadata` field:
| Field | Description |
| --- | --- |
| `billing_model` | How the organization is billed — e.g., `prepaid` or `postpaid`. |
| `credit_limit` | Maximum credit allowed (for postpaid models). |
| `customer_number` | Your internal customer reference number. |
## Account balance
The `account_balance` on the organization response shows the current funds
available. For prepaid accounts, operations are rejected when the balance
is insufficient. Top up your balance through the
[OpusDNS Dashboard](https://app.opusdns.com).
## Related API Reference
- [`GET /v1/organizations/{organization_id}/billing/invoices`](/api-reference#tag/organization/GET/v1/organizations/{organization_id}/billing/invoices)
- [`GET /v1/organizations/{organization_id}/transactions`](/api-reference#tag/organization/GET/v1/organizations/{organization_id}/transactions)
- [`GET /v1/organizations/{organization_id}/transactions/{transaction_id}`](/api-reference#tag/organization/GET/v1/organizations/{organization_id}/transactions/{transaction_id})
- [`GET /v1/organizations/{organization_id}/pricing/product-type/{product_type}`](/api-reference#tag/organization/GET/v1/organizations/{organization_id}/pricing/product-type/{product_type})
# User management
Every user in OpusDNS belongs to exactly one organization. A user in your
parent organization can manage all suborganizations and their resources. A
user created inside a suborganization is scoped to that suborganization only
— they cannot see or access other organizations.
Each user has a globally unique username and email address, and can hold
custom attributes for your integration needs. Access and security settings are
managed through the
[OpusDNS Dashboard](https://app.opusdns.com).
## Creating a user
Create a new user within your organization. The user will belong to the
organization that your API key is scoped to:
```bash
curl "$OPUSDNS_API_BASE/v1/users" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"username": "jane.doe",
"email": "jane@example.com",
"first_name": "Jane",
"last_name": "Doe",
"locale": "en"
}'
```
### User fields
| Field | Required | Description |
| --- | --- | --- |
| `username` | Yes | Unique username (globally unique across OpusDNS). |
| `email` | No | Email address (globally unique). |
| `first_name` | No | First name. |
| `last_name` | No | Last name. |
| `locale` | No | Preferred locale (e.g., `en`, `de`). |
| `phone` | No | Phone number. |
| `user_attributes` | No | Custom key-value attributes. |
## Listing users
List all users in your organization:
```bash
curl "$OPUSDNS_API_BASE/v1/organizations/users?page=1&page_size=25" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
| Parameter | Description |
| --- | --- |
| `sort_by` | Sort by `created_on`, `username`, or `email`. |
| `sort_order` | `asc` or `desc`. |
## Getting user details
Retrieve the currently authenticated user:
```bash
curl "$OPUSDNS_API_BASE/v1/users/me" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Or get a specific user by ID:
```bash
curl "$OPUSDNS_API_BASE/v1/users/user_01h45ytscbebyvny4gc8cr8ma2" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Both return the user record:
```json
{
"user_id": "user_01h45ytscbebyvny4gc8cr8ma2",
"organization_id": "organization_01h35xrscbebyvny4gc8cr8ma2",
"username": "jane.doe",
"email": "jane@example.com",
"first_name": "Jane",
"last_name": "Doe",
"locale": "en",
"status": "active",
"created_on": "2026-01-15T10:00:00Z"
}
```
You can request specific attributes by passing `attributes[]` query
parameters:
```bash
curl --get "$OPUSDNS_API_BASE/v1/users/user_01h45ytscbebyvny4gc8cr8ma2" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "attributes=department" \
--data-urlencode "attributes=team"
```
## Updating a user
Update user fields with a PATCH request:
```bash
curl "$OPUSDNS_API_BASE/v1/users/user_01h45ytscbebyvny4gc8cr8ma2" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"first_name": "Jane",
"last_name": "Smith",
"locale": "de"
}'
```
Only include the fields you want to change.
## Roles
Each user holds a single role that determines what they can do within the
organization. See [Roles & permissions](/account/organizations/roles) for how
roles and permissions work, and the list of built-in roles.
### Getting a user's role
```bash
curl "$OPUSDNS_API_BASE/v1/users/user_01h45ytscbebyvny4gc8cr8ma2/role" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
```json
{
"role": "domain_manager"
}
```
### Setting a user's role
Assign a role with a `PUT` request, replacing any existing role. Pass either a
built-in role name (for example `viewer`) or the label of a custom role owned by
the user's organization (for example `support_staff`):
```bash
curl "$OPUSDNS_API_BASE/v1/users/user_01h45ytscbebyvny4gc8cr8ma2/role" \
--request PUT \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"role": "support_staff"
}'
```
The `owner` role cannot be assigned through this endpoint — it is report-only and established when the organization is created. Sending `owner` returns a validation error.
## Deleting a user
Remove a user from the organization:
```bash
curl "$OPUSDNS_API_BASE/v1/users/user_01h45ytscbebyvny4gc8cr8ma2" \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
You cannot delete yourself or the last admin user in an organization. These operations return a conflict error.
## Related API Reference
- [`POST /v1/users`](/api-reference#tag/user/POST/v1/users)
- [`GET /v1/users/me`](/api-reference#tag/user/GET/v1/users/me)
- [`GET /v1/users/{user_id}`](/api-reference#tag/user/GET/v1/users/{user_id})
- [`PATCH /v1/users/{user_id}`](/api-reference#tag/user/PATCH/v1/users/{user_id})
- [`DELETE /v1/users/{user_id}`](/api-reference#tag/user/DELETE/v1/users/{user_id})
- [`GET /v1/users/{user_id}/role`](/api-reference#tag/user/GET/v1/users/{user_id}/role)
- [`PUT /v1/users/{user_id}/role`](/api-reference#tag/user/PUT/v1/users/{user_id}/role)
# Account security
OpusDNS uses the OpusDNS Authentication Platform to handle user identity,
login security, and credential management. These features are managed
through the [OpusDNS Dashboard](https://app.opusdns.com) — not through
the API.
## Two-factor authentication (2FA)
Every OpusDNS user must configure two-factor authentication in the Dashboard.
The OpusDNS Authentication Platform enforces 2FA during login and supports:
- **Authenticator apps** — TOTP-based codes from apps like Google
Authenticator, Authy, or 1Password. After scanning the QR code, the
user enters a one-time code on each login.
- **Recovery codes** — single-use backup codes generated when 2FA is
enabled. Store these securely — they're the fallback if the
authenticator device is lost.
**2FA is mandatory.** All OpusDNS users are required to enable two-factor authentication. Users who have not configured 2FA will be prompted to set it up on their next login and cannot proceed until it is activated.
## Passkeys
OpusDNS supports passkey authentication for passwordless login. Passkeys
use device-level biometrics (fingerprint, face recognition) or hardware
security keys (YubiKey, etc.) to authenticate — no password required.
Users can register passkeys from their account security settings in the
Dashboard. Once registered, a passkey can be used as the primary login
method or as a second factor alongside a password.
## Dashboard-only security settings
Credential recovery, access assignments, active sessions, login history, and
security events are handled through the
[OpusDNS Dashboard](https://app.opusdns.com), not through the API.
# The domain object
The domain object represents a registered domain in your OpusDNS account. It is
returned by all domain endpoints — registration, transfer, update, and retrieval.
## Example response
```json
{
"domain_id": "dom_01h45ytscbebyvny4gc8cr8ma2",
"name": "example.com",
"sld": "example",
"tld": "com",
"roid": "12345678_DOMAIN_COM-VRSN",
"owner_id": "org_01h45ytscbebyvny4gc8cr8ma2",
"registry_account_id": "ra_01h45ytscbebyvny4gc8cr8ma2",
"renewal_mode": "renew",
"transfer_lock": false,
"is_premium": false,
"read_only": false,
"registered_on": "2026-01-15T10:30:00Z",
"expires_on": "2027-01-15T10:30:00Z",
"created_on": "2026-01-15T10:30:00Z",
"updated_on": "2026-03-20T14:00:00Z",
"auth_code": "xK9#mP2$vL5nQ8wR",
"auth_code_expires_on": "2026-04-20T14:00:00Z",
"nameservers": [
{ "hostname": "ns1.example.net" },
{ "hostname": "ns2.example.net" }
],
"contacts": [
{ "contact_id": "contact_01h45ytscbebyvny4gc8cr8ma2", "contact_type": "registrant" },
{ "contact_id": "contact_01h45ytscbebyvny4gc8cr8ma2", "contact_type": "admin" },
{ "contact_id": "contact_01h45ytscbebyvny4gc8cr8ma2", "contact_type": "tech" },
{ "contact_id": "contact_01h45ytscbebyvny4gc8cr8ma2", "contact_type": "billing" }
],
"hosts": [],
"registry_statuses": ["ok"],
"tags": [],
"status_tags": []
}
```
## Fields
### Identifiers
| Field | Type | Description |
| --- | --- | --- |
| `domain_id` | `string` | Unique identifier for the domain (TypeID format). |
| `name` | `string` | The fully qualified domain name (e.g., `example.com`). |
| `sld` | `string` | The second-level domain — the part before the TLD (e.g., `example`). |
| `tld` | `string` | The top-level domain (e.g., `com`, `de`, `io`). |
| `roid` | `string` | The registry object identifier assigned by the registry. |
| `owner_id` | `string` | The organization that owns this domain (TypeID format). |
| `registry_account_id` | `string` | The registry account used for this domain (TypeID format). |
### Configuration
| Field | Type | Description |
| --- | --- | --- |
| `renewal_mode` | `string` | How the domain handles expiry. `"renew"` — the domain auto-renews before expiration. `"expire"` — the domain is allowed to expire. |
| `transfer_lock` | `boolean` | Whether the domain is locked to prevent outbound transfers. When `true`, the domain cannot be transferred to another registrar. |
| `is_premium` | `boolean` | Whether this is a premium domain with non-standard pricing. See [Premium domains](/products/domains/premium). |
| `read_only` | `boolean` | Whether the domain is read-only in OpusDNS. When `true`, the domain is listed in your portfolio but cannot be managed — for example while it awaits a migration, is locked for legal reasons, or is managed at an external registrar. The flag is set and removed by OpusDNS; it cannot be changed through the API. |
### Dates
| Field | Type | Description |
| --- | --- | --- |
| `registered_on` | `datetime` | When the domain was originally registered at the registry. |
| `expires_on` | `datetime` | When the domain's current registration period ends. |
| `created_on` | `datetime` | When the domain record was created in OpusDNS. |
| `updated_on` | `datetime` | When the domain record was last modified in OpusDNS. |
| `canceled_on` | `datetime` | When a deletion was requested. Present only if the domain has been deleted. |
| `deleted_on` | `datetime` | When the domain will be permanently removed. Present only if the domain is in a deletion lifecycle. |
### Auth code
| Field | Type | Description |
| --- | --- | --- |
| `auth_code` | `string` | The current authorization code for transferring the domain to another registrar. May be `null` if not yet generated or not applicable. |
| `auth_code_expires_on` | `datetime` | When the current auth code expires. After this time, a new auth code must be requested. |
### Nameservers
The `nameservers` array contains the DNS servers authoritative for this domain.
| Field | Type | Description |
| --- | --- | --- |
| `hostname` | `string` | The nameserver hostname (e.g., `ns1.example.net`). |
| `ip_addresses` | `string[]` | Glue record IP addresses. Only present for subordinate nameservers (nameservers under the domain itself). |
### Contacts
The `contacts` array lists the contacts associated with this domain, each with a role.
| Field | Type | Description |
| --- | --- | --- |
| `contact_id` | `string` | The identifier of the contact (TypeID format). |
| `contact_type` | `string` | The contact role: `registrant`, `admin`, `tech`, or `billing`. |
### Hosts
The `hosts` array contains subordinate hosts (also known as glue records) — nameservers
whose hostnames are under this domain.
| Field | Type | Description |
| --- | --- | --- |
| `host_id` | `string` | The identifier of the subordinate host. |
### Registry statuses
The `registry_statuses` array contains all EPP status codes currently set on the
domain at the registry level. These indicate what operations are allowed or
restricted.
#### Common statuses
| Status | Meaning |
| --- | --- |
| `ok` | The domain is in a normal state with no restrictions. |
| `inactive` | The domain has no nameservers or is not resolving. |
| `addPeriod` | The domain was recently registered and is in the add grace period. |
| `renewPeriod` | The domain was recently renewed and is in the renew grace period. |
| `autoRenewPeriod` | The domain was auto-renewed and is in the auto-renew grace period. |
| `transferPeriod` | The domain was recently transferred and is in the transfer grace period. |
#### Pending statuses
| Status | Meaning |
| --- | --- |
| `pendingCreate` | A registration is being processed. |
| `pendingTransfer` | An inbound or outbound transfer is in progress. |
| `pendingUpdate` | A domain update is being processed at the registry. |
| `pendingRenew` | A renewal is being processed. |
| `pendingDelete` | The domain is scheduled for deletion. |
| `pendingRestore` | A restore from redemption is being processed. |
#### Server-side restrictions
These are set by the registry and cannot be removed by the registrar.
| Status | Meaning |
| --- | --- |
| `serverTransferProhibited` | The registry has blocked transfers. |
| `serverUpdateProhibited` | The registry has blocked updates. |
| `serverDeleteProhibited` | The registry has blocked deletion. |
| `serverRenewProhibited` | The registry has blocked renewal. |
| `serverRestoreProhibited` | The registry has blocked restores. |
| `serverHold` | The domain is suspended by the registry — it will not resolve. |
#### Client-side restrictions
These are set by the registrar (OpusDNS) at your request or automatically.
| Status | Meaning |
| --- | --- |
| `clientTransferProhibited` | Transfers are locked. Corresponds to `transfer_lock: true`. |
| `clientUpdateProhibited` | Updates are locked. |
| `clientDeleteProhibited` | Deletion is locked. |
| `clientRenewProhibited` | Renewal is locked. |
| `clientHold` | The domain is suspended — it will not resolve. |
#### Lifecycle statuses
| Status | Meaning |
| --- | --- |
| `redemptionPeriod` | The domain has been deleted and is in the redemption grace period. It can still be restored. |
| `deleted` | The domain has been permanently deleted. |
#### Other statuses
| Status | Meaning |
| --- | --- |
| `free` | The domain is available. |
| `connect` | The domain is part of a registry lock service. |
| `failed` | An operation on the domain has failed. |
| `invalid` | The domain is in an invalid state. |
### Tags
The `tags` array contains user-created tags assigned to this domain. The
`status_tags` array contains system-managed status tags that reflect domain
conditions requiring attention. Both fields are only included in the response
when you request them with `?include=tags`.
See [User tags](/automation/tags/user-tags) and
[Status tags](/automation/tags/status-tags) for details.
| Field | Type | Description |
| --- | --- | --- |
| `tags[].tag_id` | `string` | The tag identifier. |
| `tags[].label` | `string` | The tag's display name. |
| `tags[].color` | `string` | The tag's display color (`color-1` through `color-10`). Colors are intentionally generic so that API consumers can map them to values that fit their own branding. |
| `status_tags[].tag_type` | `string` | The status tag type identifier (e.g. `VERIFICATION_REQUIRED`). |
| `status_tags[].label` | `string` | Human-readable display label. |
| `status_tags[].description` | `string` | Optional description of the status condition. |
| `status_tags[].color` | `string` | Display color for UI rendering. Colors are intentionally generic (e.g. `color-1`) so that API consumers can map them to values that fit their own branding. |
## Related API Reference
- [`GET /v1/domains/{domain_reference}`](/api-reference#tag/domain/GET/v1/domains/{domain_reference})
- [`GET /v1/domains`](/api-reference#tag/domain/GET/v1/domains)
- [`POST /v1/domains`](/api-reference#tag/domain/POST/v1/domains)
- [`PATCH /v1/domains/{domain_reference}`](/api-reference#tag/domain/PATCH/v1/domains/{domain_reference})
# Register a domain
This guide walks you through registering a new domain with the OpusDNS API, from checking availability to confirming the registration is complete.
## Flow overview
1. Check whether the domain is available.
2. Prepare contacts for the required roles.
3. Check TLD requirements (optional but recommended).
4. Register the domain.
5. Confirm the result and monitor events.
## 1. Check availability
Before submitting a registration, check one or more domains with `GET /v1/domains/check`. You can check multiple domains in a single request:
```bash
curl --get "$OPUSDNS_API_BASE/v1/domains/check" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "domains=example.com" \
--data-urlencode "domains=example.net" \
--data-urlencode "domains=example.de"
```
The response returns one result per domain:
```json
{
"results": [
{
"domain": "example.com",
"available": true,
"reason": null,
"is_premium": false
},
{
"domain": "example.net",
"available": false,
"reason": "already_registered",
"is_premium": false
}
]
}
```
The `is_premium` flag indicates whether the domain carries premium pricing. When `true`, a `premium_pricing` object is included with prices per action — see [Premium domains](/products/domains/premium) for details.
### Availability fields
| Field | Meaning |
| ----------------- | --------------------------------------------------------------------------------------------------- |
| `available` | Whether the domain can be registered through OpusDNS. |
| `reason` | Registry or validation reason when the domain is not available, or `null` when no reason is needed. |
| `claims_key` | Present when trademark claims acceptance is required. |
| `is_premium` | Whether the domain carries premium pricing. |
| `premium_pricing` | Premium prices per action when pricing is available. |
Continue only when `available` is `true`. If `claims_key` is present, follow the [Trademarked Domains](/products/domains/trademarked-domains) workflow before registering.
## 2. Prepare contacts
Domain registrations require contact data. Contacts represent the people or organizations responsible for the domain.
### Contact roles
| Role | Purpose | Required? |
| ------------ | ---------------------- | --------------------- |
| `registrant` | Legal domain holder | Always required |
| `admin` | Administrative contact | Required by most TLDs |
| `tech` | Technical contact | Required by most TLDs |
| `billing` | Billing contact | Required by some TLDs |
Check the [TLD specifications](/products/tlds/specifications) to see which contact roles a specific TLD requires.
### Create a contact
If you do not have contacts yet, create them with `POST /v1/contacts`:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"first_name": "Jane",
"last_name": "Smith",
"email": "jane@example.com",
"phone": "+49.1234567890",
"street": "Musterstraße 1",
"city": "Berlin",
"postal_code": "10115",
"country": "DE",
"org": "Example GmbH",
"disclose": false
}'
```
The response includes a `contact_id` that you use in the registration request. You can reuse the same contact for multiple roles if appropriate.
### Registry-specific attributes
Some TLDs require additional contact attributes — for example, `.us` requires a nexus category and application purpose, `.de` may require specific general request fields. See [Registry-specific attributes](/products/domains/registry-attributes) for details on creating and linking attribute sets.
## 3. Check TLD requirements (recommended)
Before registering, query the TLD specification to understand any specific requirements:
```bash
curl "$OPUSDNS_API_BASE/v1/tlds/com" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
This tells you:
* Which contact roles are required
* Allowed registration periods (minimum and maximum)
* Nameserver requirements (minimum and maximum count)
* Whether DNSSEC is supported
* Whether registry-specific attributes are needed
## 4. Register the domain
Register the domain with `POST /v1/domains`:
```bash
curl "$OPUSDNS_API_BASE/v1/domains" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "example.com",
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2",
"admin": "contact_01h45ytscbebyvny4gc8cr8ma2",
"tech": "contact_01h45ytscbebyvny4gc8cr8ma2",
"billing": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "renew",
"period": {
"unit": "y",
"value": 1
},
"nameservers": [
{ "hostname": "ns1.example.net" },
{ "hostname": "ns2.example.net" }
],
"create_zone": true
}'
```
### Request fields
| Field | Required | Description |
| ------------------------------- | -------- | --------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `name` | Yes | The fully qualified domain name to register (e.g., `example.com`). |
| `contacts` | Yes | Contact IDs keyed by role. At minimum, a `registrant` is always required. |
| `renewal_mode` | Yes | `"renew"` for automatic renewal or `"expire"` to let the domain expire. |
| `period` | Yes | Registration length. Uses `unit` (`y` for years, `m` for months, `d` for days) and `value`. |
| `nameservers` | No | Array of nameserver objects with `hostname`. If omitted, the domain is registered without nameservers. See [Using OpusDNS Nameservers](/products/domains/nameservers) for the OpusDNS nameserver hostnames. Hostnames subordinate to a domain in your account must exist as [host objects](/products/domains/host-objects) first. |
| `create_zone` | No | Set to `true` to automatically provision a DNS zone on OpusDNS nameservers. |
| `expected_price` | No | Price confirmation for [premium domains](/products/domains/premium). |
| `attributes` | No | [Registry-specific attributes](/products/domains/registry-attributes) required by certain TLDs. |
| `claims_notice_acceptance_hash` | No | Required when the availability check returns a `claims_key` during a claims phase. |
### DNS zone and nameserver behavior
The `create_zone` and `nameservers` fields are independent — each triggers a separate post-registration job. See [Using OpusDNS Nameservers](/products/domains/nameservers) for the full breakdown and when to use each option.
### Trademark Claims (TMCH)
If the availability check returns a `claims_key`, the domain matches a trademark in the Trademark Clearinghouse and requires claims acceptance. See [Trademarked Domains](/products/domains/trademarked-domains) for the full claims notice workflow.
## 5. Confirm the result
The registration returns a `DomainResponse` with the full domain details:
```json
{
"domain_id": "dom_01h45ytscbebyvny4gc8cr8ma2",
"name": "example.com",
"sld": "example",
"tld": "com",
"roid": "12345678_DOMAIN_COM-VRSN",
"renewal_mode": "renew",
"transfer_lock": false,
"is_premium": false,
"read_only": false,
"registered_on": "2026-05-04T10:30:00Z",
"expires_on": "2027-05-04T10:30:00Z",
"nameservers": [
{ "hostname": "ns1.example.net" },
{ "hostname": "ns2.example.net" }
],
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2",
"admin": "contact_01h45ytscbebyvny4gc8cr8ma2",
"tech": "contact_01h45ytscbebyvny4gc8cr8ma2",
"billing": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"registry_statuses": ["ok"]
}
```
You can retrieve the domain at any time by name or ID:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Monitor registration events
Registration may trigger asynchronous events. Poll the events endpoint to track the outcome:
```bash
curl --get "$OPUSDNS_API_BASE/v1/events" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "object_type=DOMAIN" \
--data-urlencode "type=REGISTRATION"
```
See the [Events overview](/products/events/overview) for details on event types and acknowledgment.
## Common scenarios
### Register with OpusDNS nameservers
The simplest approach — let OpusDNS handle DNS:
```bash
curl "$OPUSDNS_API_BASE/v1/domains" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "example.com",
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "renew",
"period": { "unit": "y", "value": 1 },
"nameservers": [
{ "hostname": "ns1.opusdns.com" },
{ "hostname": "ns2.opusdns.net" }
],
"create_zone": true
}'
```
### Register with external nameservers
Point to your own DNS infrastructure:
```bash
curl "$OPUSDNS_API_BASE/v1/domains" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "example.com",
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "renew",
"period": { "unit": "y", "value": 1 },
"nameservers": [
{ "hostname": "ns1.yourdns.com" },
{ "hostname": "ns2.yourdns.com" }
]
}'
```
### Register without automatic renewal
Use `"expire"` if you do not want the domain to auto-renew:
```bash
curl "$OPUSDNS_API_BASE/v1/domains" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "example.com",
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "expire",
"period": { "unit": "y", "value": 2 }
}'
```
You can always change the renewal mode later. See [Manage a domain](/products/domains/manage).
## Next steps
* [Manage a domain](/products/domains/manage) — update nameservers, contacts, and settings
* [Premium domains](/products/domains/premium) — handling premium-priced registrations
* [Registry-specific attributes](/products/domains/registry-attributes) — additional data required by certain TLDs
* [Managing DNSSEC](/products/domains/dnssec) — enable DNSSEC after registration
## Related API Reference
* [`GET /v1/domains/check`](/api-reference#tag/domain/GET/v1/domains/check)
* [`POST /v1/domains`](/api-reference#tag/domain/POST/v1/domains)
* [`POST /v1/contacts`](/api-reference#tag/contact/POST/v1/contacts)
* [`GET /v1/domains/{domain_reference}`](/api-reference#tag/domain/GET/v1/domains/%7Bdomain_reference%7D)
* [`GET /v1/tlds/{tld}`](/api-reference#tag/tld/GET/v1/tlds/%7Btld%7D)
# Transfer a domain
This guide walks you through transferring a domain to OpusDNS from another registrar, including preparation, monitoring, and handling edge cases. It also covers [outbound transfers](#outbound-transfers) — approving or rejecting a transfer of a domain away from OpusDNS.
## Flow overview
1. Prepare the domain at the current registrar (unlock, get auth code).
2. Create or select contacts.
3. Start the transfer with `POST /v1/domains/transfer`.
4. Monitor the transfer status.
5. Handle completion or cancel if needed.
## Before you begin
Transferring a domain involves coordination between the losing registrar (where the domain currently lives) and OpusDNS (the gaining registrar). A few things must be true before you can start:
* The domain must be **unlocked** at the current registrar (no `clientTransferProhibited` status).
* You need the **auth code** (also called EPP code or transfer key) from the current registrar.
* The domain must have been registered for at least **60 days** (ICANN policy for most gTLDs).
* The domain must not have been transferred within the last **60 days**.
* The domain must not be in a **redemption** or **pending delete** state.
Transfer policies vary by TLD. Some ccTLDs (country-code domains) have different requirements. Check the [TLD specifications](/products/tlds/specifications) for specifics.
## 1. Collect the auth code
Contact your current registrar to obtain the domain's authorization code. This code proves you have the right to transfer the domain.
* Most registrars provide this through their control panel or support team.
* Auth codes typically expire after a set period (often 5–14 days).
* Some TLDs use alternative transfer mechanisms — see [.uk operations](/products/tld-operations/uk) for `.uk` releases and [.eu operations](/products/tld-operations/eu) / [.be operations](/products/tld-operations/be) for auth code requests.
## 2. Prepare contacts
Most transfers require `contacts` alongside `renewal_mode`. You can reuse existing contacts or create new ones with `POST /v1/contacts`.
The `contacts` section is **optional** for TLDs that do not require any contacts to be supplied for an inbound transfer (i.e. every supported contact role has a minimum of `0` in the TLD specification, for example `.ca` and `.ch`). For those TLDs you can omit `contacts` entirely. TLDs that require one or more contact roles still reject transfers submitted without them.
```bash
curl "$OPUSDNS_API_BASE/v1/contacts" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"first_name": "Jane",
"last_name": "Smith",
"email": "jane@example.com",
"phone": "+49.1234567890",
"street": "Musterstraße 1",
"city": "Berlin",
"postal_code": "10115",
"country": "DE",
"org": "Example GmbH"
}'
```
Check which contact roles the TLD requires before submitting the transfer. See [TLD specifications](/products/tlds/specifications).
## 3. Start the transfer
Use `POST /v1/domains/transfer` to initiate the inbound transfer:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/transfer" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "example.com",
"auth_code": "xK9#mP2$vL5nQ8wR",
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2",
"admin": "contact_01h45ytscbebyvny4gc8cr8ma2",
"tech": "contact_01h45ytscbebyvny4gc8cr8ma2",
"billing": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "renew",
"period": {
"unit": "y",
"value": 1
},
"nameservers": [
{ "hostname": "ns1.example.net" },
{ "hostname": "ns2.example.net" }
],
"create_zone": true
}'
```
### Request fields
| Field | Required | Description |
| ---------------- | ----------- | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `name` | Yes | The fully qualified domain name to transfer (e.g., `example.com`). |
| `auth_code` | Yes | The authorization code from the current registrar. |
| `contacts` | Conditional | Contact IDs keyed by role. Required for most TLDs (a `registrant` is the minimum). Optional for TLDs where every supported contact role has a minimum of `0` (e.g. `.ca`, `.ch`). |
| `renewal_mode` | Yes | `"renew"` for automatic renewal or `"expire"` to let the domain expire. |
| `period` | No | Additional registration period added on transfer completion. If omitted, the registry default policy applies. |
| `nameservers` | No | Nameservers to set after transfer completes. If omitted, the existing nameservers from the previous registrar are imported. See [Nameservers](/products/domains/nameservers) for the OpusDNS nameserver hostnames. Hostnames subordinate to a domain in your account must exist as [host objects](/products/domains/host-objects) first. |
| `create_zone` | No | Set to `true` to provision a DNS zone on OpusDNS nameservers after transfer. |
| `expected_price` | No | Price confirmation for [premium domains](/products/domains/premium). |
| `attributes` | No | [Registry-specific attributes](/products/domains/registry-attributes) required by certain TLDs. |
### Registration period behavior
The `period` field in transfer requests works differently from registrations:
* **Provided:** The specified period is added to the domain's existing expiry date upon transfer completion. Most gTLDs add 1 year by default.
* **Omitted:** The registry's default transfer policy applies. For most gTLDs, this adds 1 year to the current expiry.
## 4. Monitor the transfer
The initial response is a `DomainResponse` with a `pendingTransfer` status. Transfers do not complete instantly — they require registry processing and potentially approval from the losing registrar.
### Check the transfer status
Poll the domain to see the current state:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Transfer timeline
| Phase | Duration | What happens |
| --------- | -------------- | -------------------------------------------------------------------------------------------------- |
| Initiated | Immediate | OpusDNS sends the transfer request to the registry. |
| Pending | 1–5 days | The losing registrar can approve or reject. If no action, auto-approval kicks in (for most gTLDs). |
| Completed | After approval | The domain moves to OpusDNS. Status changes to `ok`. |
| Failed | Varies | Auth code invalid, domain locked, or losing registrar rejected. |
Some TLDs complete the transfer instantly without a pending period. For example, **.de domains** are transferred immediately — once the transfer request is submitted with a valid auth code, the domain moves to your account right away with no approval wait time.
### Monitor via events
You can also track transfer progress through the events system:
```bash
curl --get "$OPUSDNS_API_BASE/v1/events" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "object_type=DOMAIN" \
--data-urlencode "type=TRANSFER"
```
Events will notify you when the transfer succeeds or fails. See the [Events overview](/products/events/overview) for details.
## 5. Cancel if needed
If a transfer must be stopped while it is still pending, use `DELETE /v1/domains/{domain_reference}/transfer`:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com/transfer" \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
This cancels the in-progress transfer and removes the domain object from your account. Cancellation is only possible while the transfer is in `pendingTransfer` status — once the registry completes the transfer, it cannot be reversed through the API.
## What happens after a successful transfer
Once the transfer completes:
* The domain no longer has status `pendingTransfer` — it transitions to its normal state.
* The expiry date is extended by the transfer period (typically 1 year).
* Contacts are set to those provided in the transfer request.
* Nameservers are updated if provided, otherwise the existing nameservers are imported from the previous registrar.
* A DNS zone is created if `create_zone` was set to `true`.
* Registry DNSSEC data is reconciled automatically: if the domain ends up on OpusDNS nameservers, stale DS records imported from the previous provider are removed or replaced so DNS resolution is not disrupted. Domains on external nameservers are left untouched. See [Automatic DNSSEC reconciliation](/products/domains/dnssec#automatic-dnssec-reconciliation).
* A transfer event is created (check `/v1/events`).
## Outbound transfers
When another registrar initiates a transfer of a domain **out of** your account, the domain enters `pendingTransfer` status. As the losing side you can resolve the pending transfer explicitly with `POST /v1/domains/{domain_reference}/transfer/outbound`:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com/transfer/outbound" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{ "action": "approve" }'
```
| Field | Required | Description |
| -------- | -------- | ------------------------------------------------------------------------------------------------------------------- |
| `action` | Yes | `"approve"` to release the domain to the gaining registrar, or `"reject"` to deny the transfer and keep the domain. |
A few things to know:
* **Approving acknowledges the transfer at the registry — it does not complete it.** The domain remains in your account until the registry confirms the transfer has completed; only then is it removed and its subscription ended.
* **Rejecting** denies the request and the domain stays in your account unchanged.
* **If you do nothing**, most gTLD registries auto-approve the transfer after the pending period (typically 5 days).
* The domain must currently have a **pending outbound transfer**; otherwise the request fails with `400`.
* Explicit resolution is only available for TLDs whose registry allows the losing registrar to act on transfers. For other TLDs the request fails with `422`.
## Troubleshooting
### Common transfer failures
| Issue | Cause | Resolution |
| ----------------- | ---------------------------------------------------------- | ------------------------------------------------------- |
| Invalid auth code | The code is wrong or has expired. | Get a fresh auth code from the current registrar. |
| Domain is locked | `clientTransferProhibited` is set at the losing registrar. | Ask the current registrar to unlock the domain. |
| Transfer rejected | The losing registrar or registrant rejected the transfer. | Confirm consent with the domain owner and retry. |
| Domain too new | The domain was registered less than 60 days ago. | Wait until the 60-day period has passed. |
| Recent transfer | The domain was transferred within the last 60 days. | Wait until 60 days have passed since the last transfer. |
### TLD-specific transfer mechanisms
Not all TLDs follow the standard auth-code-based transfer process:
* **.uk domains** require a registrar tag change (release). See [.uk operations](/products/tld-operations/uk).
* **.eu / .be domains** have specific auth code request endpoints. See [.eu operations](/products/tld-operations/eu) and [.be operations](/products/tld-operations/be).
## Next steps
* [Manage a domain](/products/domains/manage) — update settings after transfer
* [Managing DNSSEC](/products/domains/dnssec) — configure DNSSEC on your transferred domain
* [Events overview](/products/events/overview) — track transfer events
## Related API Reference
* [`POST /v1/domains/transfer`](/api-reference#tag/domain/POST/v1/domains/transfer)
* [`GET /v1/domains/{domain_reference}`](/api-reference#tag/domain/GET/v1/domains/%7Bdomain_reference%7D)
* [`DELETE /v1/domains/{domain_reference}/transfer`](/api-reference#tag/domain/DELETE/v1/domains/%7Bdomain_reference%7D/transfer)
* [`POST /v1/domains/{domain_reference}/transfer/outbound`](/api-reference#tag/domain/POST/v1/domains/%7Bdomain_reference%7D/transfer/outbound)
* [`POST /v1/contacts`](/api-reference#tag/contact/POST/v1/contacts)
# Manage a domain
After registering or transferring a domain, you can update its configuration at any time using the OpusDNS API. This guide covers the most common management tasks.
## Update nameservers
Replace the nameservers on a domain with `PATCH /v1/domains/{domain_reference}`. Pass the full set of nameservers you want — the existing list is replaced entirely. See [Using OpusDNS Nameservers](/products/domains/nameservers) for the OpusDNS nameserver hostnames.
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"nameservers": [
{ "hostname": "ns1.newprovider.net" },
{ "hostname": "ns2.newprovider.net" }
]
}'
```
If you set `create_zone: true` during registration, the domain already points to OpusDNS nameservers and a DNS zone was provisioned automatically.
## Update contacts
Change any contact role by providing the contact ID for that role:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2",
"admin": "contact_01j7abc123def456ghi789jkl"
}
}'
```
You only need to include the roles you want to change. Roles you omit remain unchanged.
## Change renewal mode
Set `renewal_mode` to control what happens when the domain approaches its expiry date:
| Mode | Behavior |
| -------- | ---------------------------------------------------- |
| `renew` | Automatically renews before expiration |
| `expire` | Domain is not renewed and will eventually be deleted |
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"renewal_mode": "expire"
}'
```
## Manage domain statuses
Domain statuses control what operations are allowed. You can manage them in two ways:
### Option 1: Declarative replacement
Set `statuses` to replace the entire status list. This is useful when you know the exact set of statuses you want:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"statuses": ["clientTransferProhibited"]
}'
```
### Option 2: Delta changes
Use `status_changes` to add or remove individual statuses without affecting others:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"status_changes": {
"add": ["clientTransferProhibited"],
"remove": ["clientDeleteProhibited"]
}
}'
```
You cannot use `statuses` and `status_changes` in the same request. The `add` and `remove` lists must not overlap.
### Transfer lock
The `transfer_lock` field in the domain response is derived from the `clientTransferProhibited` status. To lock or unlock a domain for transfers, add or remove that status.
### Blocking statuses
Certain statuses prevent domain updates entirely. If any of these are active, you must remove them before making other changes:
* `clientUpdateProhibited`
* `serverUpdateProhibited`
* `pendingTransfer`
* `pendingRestore`
* `pendingDelete`
* `redemptionPeriod`
### Read-only domains
A domain with `read_only: true` cannot be managed at all — updates, renewals, and deletions are rejected. OpusDNS sets this flag on domains that are listed in your portfolio but not manageable, for example while they await a migration, are locked for legal reasons, or are managed at an external registrar. The flag is removed by OpusDNS when management becomes available; it cannot be changed through the API. To find affected domains, filter with the `read_only` query parameter on `GET /v1/domains`.
## Rotate auth code
Generate a new authorization code for a domain:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"auth_code": "NEW-AUTH-CODE-VALUE"
}'
```
The auth code is required when transferring the domain to another registrar.
## Retrieve domain details
Fetch the current state of a domain by name or ID:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
The response includes all domain details: nameservers, contacts, statuses, registration and expiry dates, renewal mode, and more.
## Related API Reference
* [`PATCH /v1/domains/{domain_reference}`](/api-reference#tag/domain/PATCH/v1/domains/%7Bdomain_reference%7D)
* [`GET /v1/domains/{domain_reference}`](/api-reference#tag/domain/GET/v1/domains/%7Bdomain_reference%7D)
# Renew a domain
Domains with `renewal_mode: "renew"` are renewed automatically before they expire. If you need to renew a domain manually — for example to extend it further in advance — use the renew endpoint.
## Renew a domain
Send a `POST` request to `/v1/domains/{domain_reference}/renew`:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com/renew" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"period": {
"unit": "y",
"value": 1
},
"current_expiry_date": "2026-03-15"
}'
```
### Request fields
| Field | Required | Description |
| --------------------- | -------- | --------------------------------------------------------------------------------------------------------------------------------- |
| `period` | Yes | How long to extend the domain. Uses `unit` (`y`, `m`, or `d`) and `value`. |
| `current_expiry_date` | Yes | The domain's current expiry date. Acts as a safety check to prevent accidental double renewals. |
| `expected_price` | No | Price confirmation for [premium domains](/products/domains/premium). Required for premium domains; rejected for standard domains. |
### Response
A successful renewal returns:
```json
{
"name": "example.com",
"new_expiry_date": "2027-03-15",
"period_extended": {
"unit": "y",
"value": 1
}
}
```
For premium domains, include `expected_price` to confirm the renewal price. See [Premium domains](/products/domains/premium) for details.
## Domain reference
You can use either the domain name or the domain ID as the path parameter:
```plaintext
POST /v1/domains/example.com/renew
POST /v1/domains/dom_01h45ytscbebyvny4gc8cr8ma2/renew
```
## Related API Reference
* [`POST /v1/domains/{domain_reference}/renew`](/api-reference#tag/domain/POST/v1/domains/%7Bdomain_reference%7D/renew)
* [`GET /v1/domains/{domain_reference}`](/api-reference#tag/domain/GET/v1/domains/%7Bdomain_reference%7D)
# Delete a domain
When you no longer need a domain, you can delete it through the OpusDNS API. This guide explains the deletion process and the domain lifecycle stages that follow.
## Delete a domain
Send a `DELETE` request to `/v1/domains/{domain_reference}`:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com" \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
A successful deletion returns a `204 No Content` response.
## Domain lifecycle after deletion
After you delete a domain, it goes through several stages before it becomes available for registration again. The exact timing depends on the TLD and registry policies.
```plaintext
Active → Pending Delete → Redemption Period → Pending Purge → Available
```
| Stage | Description |
| --------------------- | ---------------------------------------------------------------------------------- |
| **Active** | The domain is registered and functioning normally. |
| **Pending Delete** | The deletion has been requested. The domain may still be recoverable. |
| **Redemption Period** | A grace period during which the domain can be restored (usually at a higher cost). |
| **Pending Purge** | The domain is queued for final removal from the registry. It cannot be restored. |
| **Available** | The domain is released and can be registered by anyone. |
Redemption period lengths and restore fees vary by TLD. Check the [TLD specifications](/products/tlds/specifications) for details on specific extensions.
## Prerequisites
Before a domain can be deleted, make sure it does not have any blocking statuses. The following statuses prevent deletion:
* `clientDeleteProhibited`
* `serverDeleteProhibited`
* `pendingTransfer`
If any of these are active, remove them first using the [domain update endpoint](/products/domains/manage).
## Cancellation vs. deletion
* **Deletion** removes the domain from your account and begins the registry deletion process.
* If you want to keep the domain but stop automatic renewal, change the `renewal_mode` to `"expire"` instead of deleting it. The domain will remain active until its expiry date.
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"renewal_mode": "expire"
}'
```
## Restoring a deleted domain
If a domain is in the redemption period, you can still restore it. See the [Restore a domain](/products/domains/restore) guide.
## Related API Reference
* [`DELETE /v1/domains/{domain_reference}`](/api-reference#tag/domain/DELETE/v1/domains/%7Bdomain_reference%7D)
* [`PATCH /v1/domains/{domain_reference}`](/api-reference#tag/domain/PATCH/v1/domains/%7Bdomain_reference%7D)
* [`POST /v1/domains/{domain_reference}/restore`](/api-reference#tag/domain/POST/v1/domains/%7Bdomain_reference%7D/restore)
# Restore a domain
If a domain has been deleted and is in the redemption period, you can restore it to bring it back to active status. Restoring a domain is typically more expensive than a standard renewal and must be done within the registry's grace period.
## Restore a domain
Send a `POST` request to `/v1/domains/{domain_reference}/restore`:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com/restore" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"reason": "Domain deleted in error",
"expected_price": "80.00"
}'
```
### Request fields
| Field | Required | Description |
| ----------------- | -------- | --------------------------------------------------------------------------------------------------------------------------------- |
| `reason` | No | A short explanation for the restore request. Some registries require this. |
| `additional_info` | No | Extra context about the restore, if needed. |
| `expected_price` | No | Price confirmation for [premium domains](/products/domains/premium). Required for premium domains; rejected for standard domains. |
### Response
A successful restore returns:
```json
{
"domain_id": "dom_01h45ytscbebyvny4gc8cr8ma2",
"name": "example.com",
"restored_at": "2026-01-15T10:30:00Z"
}
```
## When can you restore?
A domain can only be restored while it is in the **redemption period**. This is the grace period after deletion during which the registry holds the domain before permanently releasing it.
| Domain status | Can restore? |
| ----------------- | -------------------------- |
| Active | No — domain is not deleted |
| Pending Delete | Depends on registry policy |
| Redemption Period | **Yes** |
| Pending Purge | No — too late |
Redemption period length and restore pricing vary by TLD. Check the [TLD specifications](/products/tlds/specifications) for details on specific extensions.
For premium domains, include `expected_price` to confirm the restore price. See [Premium domains](/products/domains/premium) for details.
## Related API Reference
* [`POST /v1/domains/{domain_reference}/restore`](/api-reference#tag/domain/POST/v1/domains/%7Bdomain_reference%7D/restore)
* [`DELETE /v1/domains/{domain_reference}`](/api-reference#tag/domain/DELETE/v1/domains/%7Bdomain_reference%7D)
* [`GET /v1/domains/{domain_reference}`](/api-reference#tag/domain/GET/v1/domains/%7Bdomain_reference%7D)
# Premium domains
Some domain names carry premium pricing set by the registry. These are typically short, memorable, or high-value names that cost more than the standard price for their TLD. Premium prices apply to registration and may also affect renewals, transfers, and restores.
## Identifying premium domains
When you check domain availability with `GET /v1/domains/check`, each result includes an `is_premium` flag and, when applicable, a `premium_pricing` object with prices per action.
```bash
curl --get "$OPUSDNS_API_BASE/v1/domains/check" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "domains=luxury.com"
```
A premium domain returns pricing information in the response:
```json
{
"results": [
{
"domain": "luxury.com",
"available": true,
"reason": null,
"is_premium": true,
"premium_pricing": {
"prices": [
{ "action": "registration", "price": "2500.00", "currency": "USD" },
{ "action": "renewal", "price": "250.00", "currency": "USD" },
{ "action": "transfer", "price": "2500.00", "currency": "USD" },
{ "action": "restore", "price": "350.00", "currency": "USD" }
]
}
}
]
}
```
A standard-priced domain has `is_premium: false` and no `premium_pricing`.
## The `expected_price` field
When you register, renew, transfer, or restore a premium domain, include the `expected_price` field in your request. This acts as a price confirmation — if the actual registry price does not match, the API rejects the request instead of charging you a different amount.
```json
{
"name": "luxury.com",
"expected_price": "2500.00",
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "renew",
"period": { "unit": "y", "value": 1 }
}
```
* If `expected_price` is **missing** for a premium domain, the API returns an error requiring you to confirm the price.
* If `expected_price` **does not match** the registry price, the API returns a mismatch error.
* If `expected_price` is provided for a **non-premium** domain, the API returns an error indicating that price confirmation is not applicable.
Always check `premium_pricing` in the availability response before submitting a registration, transfer, or other operation on a premium domain. Use the returned price as your `expected_price` value.
## Supported operations
Premium pricing and the `expected_price` field are supported on:
| Operation | Endpoint | Notes |
| ------------ | ------------------------------------------------------------------------------------------------------------------------- | ------------------------------------------------------------- |
| Registration | [`POST /v1/domains`](/api-reference#tag/domain/POST/v1/domains) | Include `expected_price` in the request body. |
| Renewal | [`POST /v1/domains/{domain_reference}/renew`](/api-reference#tag/domain/POST/v1/domains/%7Bdomain_reference%7D/renew) | Premium renewals may cost more than standard renewals. |
| Transfer | [`POST /v1/domains/transfer`](/api-reference#tag/domain/POST/v1/domains/transfer) | The transfer price may differ from the registration price. |
| Restore | [`POST /v1/domains/{domain_reference}/restore`](/api-reference#tag/domain/POST/v1/domains/%7Bdomain_reference%7D/restore) | Restore fees for premium domains can be significantly higher. |
## Registering a premium domain
```bash
curl "$OPUSDNS_API_BASE/v1/domains" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "luxury.com",
"expected_price": "2500.00",
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2",
"admin": "contact_01h45ytscbebyvny4gc8cr8ma2",
"tech": "contact_01h45ytscbebyvny4gc8cr8ma2",
"billing": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "renew",
"period": { "unit": "y", "value": 1 }
}'
```
## Renewing a premium domain
```bash
curl "$OPUSDNS_API_BASE/v1/domains/luxury.com/renew" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"period": { "unit": "y", "value": 1 },
"current_expiry_date": "2026-06-01",
"expected_price": "250.00"
}'
```
## Restoring a premium domain
```bash
curl "$OPUSDNS_API_BASE/v1/domains/luxury.com/restore" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"reason": "Domain deleted in error",
"expected_price": "350.00"
}'
```
## Filtering domains by premium status
Use the `is_premium` query parameter on `GET /v1/domains` to filter your domain list:
```bash
# List only premium domains
curl --get "$OPUSDNS_API_BASE/v1/domains" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "is_premium=true"
```
```bash
# List only standard-priced domains
curl --get "$OPUSDNS_API_BASE/v1/domains" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "is_premium=false"
```
Each domain in the response includes `is_premium` so you can identify premium domains without a separate availability check.
## Related API Reference
* [`GET /v1/domains/check`](/api-reference#tag/domain/GET/v1/domains/check)
* [`POST /v1/domains`](/api-reference#tag/domain/POST/v1/domains)
* [`POST /v1/domains/{domain_reference}/renew`](/api-reference#tag/domain/POST/v1/domains/%7Bdomain_reference%7D/renew)
* [`POST /v1/domains/{domain_reference}/restore`](/api-reference#tag/domain/POST/v1/domains/%7Bdomain_reference%7D/restore)
* [`GET /v1/domains`](/api-reference#tag/domain/GET/v1/domains)
# Trademarked Domains
Some domain names are protected by trademarks registered in the **Trademark Clearinghouse (TMCH)**. When you attempt to register one of these domains, the registry requires you to acknowledge a claims notice before the registration can proceed.
## How it works
The TMCH is a centralized database of verified trademarks, mandated by ICANN for all new generic TLDs (gTLDs). During a TLD's **claims period** — typically the first 90 days after general availability — any registration attempt for a domain matching a registered trademark triggers a claims notice.
Claims periods are set by each TLD's registry. Some TLDs extend claims indefinitely. Check the [TLD specifications](/products/tlds/specifications) for details on a specific TLD's policies.
## Identifying trademarked domains
When you check domain availability with `GET /v1/domains/check`, a trademarked domain returns a `claims_key`:
```json
{
"results": [
{
"domain": "brandname.shop",
"available": true,
"reason": null,
"is_premium": false,
"claims_key": "claims_key_from_check_response"
}
]
}
```
The `claims_key` field means the domain **is available** for registration, but trademark claims must be acknowledged first. Submit the same value as `claims_notice_acceptance_hash` after the registrant has accepted the notice.
```bash
curl --get "$OPUSDNS_API_BASE/v1/domains/check" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "domains=brandname.shop"
```
## Registration workflow
Registering a trademarked domain requires three steps beyond a normal registration:
### 1. Detect the claims requirement
After the availability check returns a non-null `claims_key`, keep that value. You need it when submitting the registration.
### 2. Present the notice to the registrant
ICANN policy requires that the claims notice is presented to the registrant **in full** and that the registrant explicitly acknowledges it before you proceed. Programmatically accepting notices without genuine registrant acknowledgment violates ICANN's Registrar Accreditation Agreement.
The registrant must review the trademark information and confirm they understand that:
* The domain they are registering matches a registered trademark.
* They have a legitimate right or interest in the domain name.
* They are not registering the domain in bad faith.
### 3. Submit the registration with the acceptance hash
Once the registrant has acknowledged the notice, include the returned `claims_key` as `claims_notice_acceptance_hash` in your registration request:
```bash
curl "$OPUSDNS_API_BASE/v1/domains" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "brandname.shop",
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "renew",
"period": { "unit": "y", "value": 1 },
"claims_notice_acceptance_hash": "claims_key_from_check_response"
}'
```
Claims notice acceptance hashes expire. If the hash has expired when you submit the registration, the request will be rejected and you must run the availability check again to receive a fresh claims key.
## Bulk registration with TMCH
When using the [Jobs API](/automation/jobs/overview) for bulk domain registration, you can include the `claims_notice_acceptance_hash` per instance:
```json
{
"command": "domain_create_bulk",
"payload": {
"template": {
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "renew",
"period": { "unit": "y", "value": 1 }
},
"instances": [
{
"name": "brand-one.shop",
"claims_notice_acceptance_hash": "claims_key_for_brand_one"
},
{
"name": "brand-two.store",
"claims_notice_acceptance_hash": "claims_key_for_brand_two"
}
]
}
}
```
## Related guides
* [Register a domain](/products/domains/register) — full registration workflow
* [Premium domains](/products/domains/premium) — handling premium-priced names
* [TLD specifications](/products/tlds/specifications) — TLD policies and phases
* [Jobs: Domain commands](/automation/jobs/domain-commands) — bulk registration
## Related API Reference
* [`GET /v1/domains/check`](/api-reference#tag/domain/GET/v1/domains/check)
* [`POST /v1/domains`](/api-reference#tag/domain/POST/v1/domains)
# Managing DNSSEC
DNSSEC (Domain Name System Security Extensions) adds a layer of trust to DNS responses by cryptographically signing records. The OpusDNS API lets you manage DNSSEC data for your domains.
## Check DNSSEC status
Retrieve the current DNSSEC records for a domain:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com/dnssec" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
The response returns an array of DNSSEC data records (DS or KEY records) currently published at the registry.
## Enable DNSSEC
If your domain's TLD supports DNSSEC, enable it with:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com/dnssec/enable" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
This activates DNSSEC signing for the domain. The API will return an error if the TLD does not support DNSSEC or if DNSSEC is already enabled.
## Disable DNSSEC
To remove DNSSEC protection from a domain:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com/dnssec/disable" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Manage DNSSEC records
### Add or replace DNSSEC data
Use `PUT` to set the DNSSEC records. This replaces any existing records with the ones you provide:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com/dnssec" \
--request PUT \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '[
{
"key_tag": 12345,
"algorithm": 13,
"digest_type": 2,
"digest": "49FD46E6C4B45C55D4AC..."
}
]'
```
### DS record fields
When providing DS (Delegation Signer) records:
| Field | Type | Description |
| ------------- | ------- | ------------------------------------- |
| `key_tag` | integer | Identifier for the DNSKEY record |
| `algorithm` | integer | Cryptographic algorithm number |
| `digest_type` | integer | Hash algorithm used for the digest |
| `digest` | string | Hex-encoded hash of the DNSKEY record |
### KEY record fields
Some registries accept KEY records instead of DS records:
| Field | Type | Description |
| ------------ | ------- | -------------------------------------- |
| `flags` | integer | DNSKEY flags field (e.g., 257 for KSK) |
| `protocol` | integer | Protocol number (always 3 for DNSSEC) |
| `algorithm` | integer | Cryptographic algorithm number |
| `public_key` | string | Base64-encoded public key |
Whether to use DS or KEY records depends on the TLD's registry. Check the [TLD specifications](/products/tlds/specifications) for DNSSEC mode details.
### Remove all DNSSEC data
Delete all published DNSSEC records:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com/dnssec" \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Automatic DNSSEC reconciliation
When a domain transfers to OpusDNS, any DNSSEC records already published at the registry are imported along with the rest of the domain data. If those records point to keys held by a previous DNS provider, resolvers expect DNSSEC-signed responses that the new nameservers cannot produce, and the domain stops resolving (`SERVFAIL`).
To prevent this, OpusDNS automatically reconciles the registry DNSSEC data with your zone's DNSSEC state after an inbound transfer completes and after a domain's nameservers change:
| Nameservers | Zone DNSSEC status | Action |
| ---------------------- | --------------------------- | ----------------------------------------------------------------------------------------- |
| External (not OpusDNS) | — | DNSSEC data is left untouched — you manage it yourself. |
| OpusDNS | Enabled | The zone's current DNSSEC data is published to the registry, replacing any stale records. |
| OpusDNS | Disabled, or no zone exists | All DNSSEC data is removed from the registry. |
Reconciliation runs asynchronously after the transfer or nameserver update completes, so there may be a short delay before the registry records reflect the final state. It is skipped for TLDs that do not support DNSSEC.
If reconciliation fails, a domain event with type `MODIFICATION` and subtype `FAILURE` is created — see the [Events overview](/products/events/overview). You can always inspect the current registry records with `GET /v1/domains/{domain_reference}/dnssec` and correct them manually.
## TLD support
Not all TLDs support DNSSEC. The TLD specification includes:
* Whether DNSSEC is **allowed** for the TLD
* Whether DNSSEC is **mandatory**
* The DNSSEC **mode** (DS records, KEY records, or both)
Query the TLD specification to check support before enabling DNSSEC:
```bash
curl "$OPUSDNS_API_BASE/v1/tlds/com" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Look for the `dns_configuration.dnssec` section in the response.
## Related API Reference
* [`GET /v1/domains/{domain_reference}/dnssec`](/api-reference#tag/domain/GET/v1/domains/%7Bdomain_reference%7D/dnssec)
* [`PUT /v1/domains/{domain_reference}/dnssec`](/api-reference#tag/domain/PUT/v1/domains/%7Bdomain_reference%7D/dnssec)
* [`DELETE /v1/domains/{domain_reference}/dnssec`](/api-reference#tag/domain/DELETE/v1/domains/%7Bdomain_reference%7D/dnssec)
* [`POST /v1/domains/{domain_reference}/dnssec/enable`](/api-reference#tag/domain/POST/v1/domains/%7Bdomain_reference%7D/dnssec/enable)
* [`POST /v1/domains/{domain_reference}/dnssec/disable`](/api-reference#tag/domain/POST/v1/domains/%7Bdomain_reference%7D/dnssec/disable)
# Registry-specific attributes
Some TLDs require additional information about contacts beyond the standard
fields like name, address, and email. These are called **registry-specific
attributes** — things like entity type, tax IDs, nexus categories, or legal
status declarations mandated by the registry operator.
The OpusDNS API handles these through **contact attribute sets**: reusable
bundles of key–value pairs that you create once and link to one or more
contacts.
## Flow overview
1. Query the TLD specification to discover which attributes are required.
2. Create a contact attribute set with the correct values.
3. Link the attribute set to a contact.
## 1. Discover required attributes
Use the TLD specifications endpoint to check whether a TLD requires
registry-specific attributes. The `contacts.possible_attributes` array lists
every attribute the registry accepts or requires.
```bash
curl "$OPUSDNS_API_BASE/v1/tlds/us" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
The response includes a `contacts.possible_attributes` array. Each entry is a
`ContactAttributeDefinition`:
```json
{
"contacts": {
"possible_attributes": [
{
"key": "US_NEXUS_CATEGORY",
"type": "enum",
"values": ["C11", "C12", "C21", "C31", "C32"],
"required": true,
"contact_roles": ["registrant"]
},
{
"key": "US_APP_PURPOSE",
"type": "enum",
"values": ["P1", "P2", "P3", "P4", "P5"],
"required": true,
"contact_roles": ["registrant"]
},
{
"key": "US_NEXUS_COUNTRY_CODE",
"type": "country_code",
"required": true,
"contact_roles": ["registrant"],
"conditions": [
{
"field": "US_NEXUS_CATEGORY",
"operator": "in",
"value": ["C31", "C32"]
}
]
}
]
}
}
```
### Attribute definition fields
| Field | Description |
| --- | --- |
| `key` | Unique attribute identifier (e.g. `US_NEXUS_CATEGORY`, `DE_CONTACT_TYPE`) |
| `type` | Data type — `enum`, `string`, `boolean`, `datetime`, `integer`, or `country_code` |
| `values` | Allowed values when `type` is `enum` |
| `required` | Whether the attribute is required when its conditions are met |
| `contact_roles` | Roles this attribute applies to (e.g. `registrant`, `admin`). `null` means all roles |
| `conditions` | Conditions that must all be true for this attribute to apply. `null` means always active |
### Conditional attributes
Some attributes only apply when another attribute has a specific value. For
example, `US_NEXUS_COUNTRY_CODE` is only required when `US_NEXUS_CATEGORY` is
`C31` or `C32`. Conditions use operators like `equals`, `not_equals`, `in`, and
`not_in`.
## 2. Create an attribute set
Once you know which attributes are needed, create a contact attribute set with
`POST /v1/contacts/attribute-sets`. Each set is scoped to a single TLD.
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "US registrant - personal",
"tld": "us",
"attributes": {
"US_NEXUS_CATEGORY": "C11",
"US_APP_PURPOSE": "P1"
}
}'
```
The response includes the created set with its ID:
```json
{
"contact_attribute_set_id": "cas_01j5...",
"organization_id": "org_01h4...",
"label": "US registrant - personal",
"tld": "us",
"attributes": {
"US_NEXUS_CATEGORY": "C11",
"US_APP_PURPOSE": "P1"
},
"linked_contacts": 0,
"created_on": "2025-01-15T10:30:00Z",
"updated_on": "2025-01-15T10:30:00Z"
}
```
The `label` must be unique per TLD within your organization. The `tld` field
accepts formats like `us`, `.us`, or `US` — it is normalized automatically.
The API validates that the provided attribute keys are valid for the given TLD.
If the TLD has no `possible_attributes` or you supply an invalid key, the
request is rejected.
## 3. Link the attribute set to a contact
After creating the set, link it to a contact with
`PATCH /v1/contacts/{contact_id}/link/{contact_attribute_set_id}`.
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/contact_01h45ytscbebyvny4gc8cr8ma2/link/cas_01j5..." \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
A contact can only have one attribute set linked per TLD. Attempting to link a
second set for the same TLD returns a `409` conflict.
Once linked, the attribute values are automatically applied when the contact is
used for domain operations on that TLD.
## List attribute sets
Retrieve all attribute sets in your organization with
`GET /v1/contacts/attribute-sets`. You can filter by `tld` or `label`.
```bash
curl --get "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "tld=us"
```
## Update an attribute set
Update the label of an existing attribute set with
`PATCH /v1/contacts/attribute-sets/{contact_attribute_set_id}`.
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets/cas_01j5..." \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "US registrant - business"
}'
```
## Delete an attribute set
Remove an attribute set with
`DELETE /v1/contacts/attribute-sets/{contact_attribute_set_id}`.
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets/cas_01j5..." \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Supported TLDs and attributes
The following TLDs currently require or accept registry-specific attributes.
Use `GET /v1/tlds/{tld}` for the authoritative, up-to-date list, and each TLD's
[TLD Knowledge Base](/tld-knowledge-base) page for what its attributes mean.
| TLD | Registry | Key attributes | Roles |
| --- | --- | --- | --- |
| `.us` | GoDaddy (Neustar) | `US_NEXUS_CATEGORY`, `US_APP_PURPOSE`, `US_NEXUS_COUNTRY_CODE` | registrant |
| `.de` | DENIC | `DE_CONTACT_TYPE` | registrant |
| `.eu` | EURid | `eurid:type` | registrant, tech |
| `.be` | DNS Belgium | `dnsbe:type` | registrant, tech |
| [`.fr`](/tld-knowledge-base/cctlds/fr#contact-attributes) | AFNIC | `AFNIC_CONTACT_TYPE`, `AFNIC_PP_FIRST_NAME`, `AFNIC_PM_LEGAL_STATUS`, `AFNIC_PM_SIREN`, and more | registrant, admin, tech |
| [`.re`](/tld-knowledge-base/cctlds/re#contact-attributes), [`.pm`](/tld-knowledge-base/cctlds/pm#contact-attributes), [`.wf`](/tld-knowledge-base/cctlds/wf#contact-attributes), [`.yt`](/tld-knowledge-base/cctlds/yt#contact-attributes), [`.tf`](/tld-knowledge-base/cctlds/tf#contact-attributes) | AFNIC | Same as `.fr` | registrant, admin, tech |
| `.uk` | Nominet | `NOMINET_CONTACT_TYPE`, `NOMINET_CO_NO`, `NOMINET_TRAD_NAME` | registrant |
| `.ca` | CIRA | `CIRA_CPR` | registrant, admin |
| `.nl` | SIDN | `SIDN_LEGAL_FORM`, `SIDN_LEGAL_REG_NO` | registrant, admin, tech |
| `.ro` | ROTLD | `ROTLD_CONTACT_TYPE`, `ROTLD_CNP_FISCAL_CODE`, `ROTLD_ID_NUMBER`, `ROTLD_REGISTRATION_NUMBER` | registrant, admin, tech, billing |
| [`.se`](/tld-knowledge-base/cctlds/se#contact-attributes), [`.nu`](/tld-knowledge-base/cctlds/nu#contact-attributes) | Internetstiftelsen | `REGISTRY_SE_ORG_NO`, `REGISTRY_SE_VAT_NO` | registrant |
### Example: .fr registration (AFNIC)
AFNIC TLDs distinguish between natural persons (`PP`) and legal entities
(`PM`). A natural person requires `AFNIC_CONTACT_TYPE` and
`AFNIC_PP_FIRST_NAME`. A legal entity requires `AFNIC_PM_LEGAL_STATUS` and,
depending on the status, identifiers like `AFNIC_PM_SIREN` or association
details. AFNIC requires these attributes on the administrative and technical
contacts too, not only the registrant — see
[Contact attributes on `.fr`](/tld-knowledge-base/cctlds/fr#contact-attributes)
for the full set and the rules that govern it.
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "FR registrant - company",
"tld": "fr",
"attributes": {
"AFNIC_CONTACT_TYPE": "PM",
"AFNIC_PM_LEGAL_STATUS": "company",
"AFNIC_PM_SIREN": "123456789"
}
}'
```
### Example: .de registration (DENIC)
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "DE registrant - person",
"tld": "de",
"attributes": {
"DE_CONTACT_TYPE": "PERSON"
}
}'
```
## Related API Reference
- [`GET /v1/tlds/{tld}`](/api-reference#tag/tld/GET/v1/tlds/{tld})
- [`POST /v1/contacts/attribute-sets`](/api-reference#tag/contact/POST/v1/contacts/attribute-sets)
- [`GET /v1/contacts/attribute-sets`](/api-reference#tag/contact/GET/v1/contacts/attribute-sets)
- [`PATCH /v1/contacts/{contact_id}/link/{contact_attribute_set_id}`](/api-reference#tag/contact/PATCH/v1/contacts/{contact_id}/link/{contact_attribute_set_id})
# Using OpusDNS Nameservers
When you host DNS with OpusDNS, your domains should point to the OpusDNS nameservers. We operate separate nameserver infrastructure for production and sandbox environments.
## Production nameservers
Use these nameservers for live domains:
| Nameserver | Hostname |
| ---------- | ----------------- |
| Primary | `ns1.opusdns.com` |
| Secondary | `ns2.opusdns.net` |
Set them when registering or transferring a domain:
```json
"nameservers": [
{ "hostname": "ns1.opusdns.com" },
{ "hostname": "ns2.opusdns.net" }
]
```
## Sandbox nameservers
The sandbox environment uses its own nameservers. Domains registered in the sandbox should use these instead:
| Nameserver | Hostname |
| ---------- | ------------------------- |
| Primary | `ns1.sandbox.opusdns.com` |
| Secondary | `ns2.sandbox.opusdns.net` |
```json
"nameservers": [
{ "hostname": "ns1.sandbox.opusdns.com" },
{ "hostname": "ns2.sandbox.opusdns.net" }
]
```
Production and sandbox nameservers are not interchangeable. Using production nameservers in the sandbox (or vice versa) will result in DNS resolution failures.
## Using your own nameservers
You are not limited to OpusDNS nameservers — any nameserver hostname can be set on a domain. If the nameserver hostname is subordinate to a domain in your account (e.g. `ns1.example.com` serving `example.com`), the registry requires a host object with glue records before domains can reference it. Create one with the host endpoints first — see [Host objects (glue records)](/products/domains/host-objects).
## When to set nameservers
You can set nameservers at several points:
* **During registration** — pass `nameservers` in the `POST /v1/domains` request. See [Register a domain](/products/domains/register).
* **During transfer** — pass `nameservers` in the `POST /v1/domains/transfer` request. See [Transfer a domain](/products/domains/transfer).
* **After registration** — update nameservers with `PATCH /v1/domains/{domain_reference}`. See [Manage a domain](/products/domains/manage).
* **In bulk** — use `domain_create_bulk`, `domain_transfer_bulk`, or `domain_update_bulk` in the [Jobs API](/automation/jobs/overview).
When a domain's nameservers change, OpusDNS automatically reconciles the DNSSEC data published at the registry with the zone's DNSSEC state, so stale records from a previous provider cannot break resolution. See [Automatic DNSSEC reconciliation](/products/domains/dnssec#automatic-dnssec-reconciliation).
## Nameservers vs. zones
Setting nameservers and creating a DNS zone are independent operations:
| `create_zone` | `nameservers` provided | Result |
| ------------- | ---------------------- | ------------------------------------------------------------------------- |
| `true` | Yes | Creates a DNS zone **and** points the domain to the provided nameservers. |
| `true` | No | Creates a DNS zone only. Nameservers are not changed at the registry. |
| `false` | Yes | Points the domain to the provided nameservers. No zone is created. |
| `false` | No | No DNS action. |
Setting `create_zone: true` provisions a zone on OpusDNS infrastructure but does not automatically set nameservers at the registry. Always provide both if you want OpusDNS to handle DNS end-to-end.
# Host Objects (Glue Records)
A host object represents a nameserver hostname registered at a registry. When a nameserver hostname is subordinate to a domain in your portfolio — for example `ns1.example.com` serving `example.com` — the registry requires a host object carrying one or more IP addresses, commonly known as **glue records**, so that resolvers can reach the nameserver even though its address lives inside the zone it serves.
## When you need a host object
You need a host object when you want to use your own nameservers whose hostnames sit under a domain you manage with OpusDNS:
1. Create the host object with its IP addresses (`POST /v1/hosts`).
2. Point your domains at the new nameserver hostname, e.g. via `PATCH /v1/domains/{domain_reference}`. See [Manage a domain](/products/domains/manage).
You do **not** need a host object for external nameservers (e.g. your DNS provider's hostnames such as `ns1.yourdns.com`) — simply reference them by hostname when setting a domain's nameservers.
The host endpoints manage **subordinate** host objects: the parent domain of the hostname must be managed in your OpusDNS account. Requests for hostnames whose parent domain is not in your account are rejected with `ERROR_PARENT_DOMAIN_NOT_FOUND`.
## Create a host object
Provide the hostname and at least one IP address. The host object is created at the registry of the parent domain:
```bash
curl "$OPUSDNS_API_BASE/v1/hosts" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"hostname": "ns1.example.com",
"ip_addresses": ["192.0.2.53", "2001:db8::53"]
}'
```
| Field | Required | Notes |
| -------------- | -------- | ------------------------------------------------ |
| `hostname` | Yes | Must be subordinate to a domain in your account. |
| `ip_addresses` | Yes | One or more IPv4 and/or IPv6 addresses. |
The response returns the host object:
```json
{
"host_id": "host_01h455vb4pex5vsknk084sn02q",
"hostname": "ns1.example.com",
"ip_addresses": ["192.0.2.53", "2001:db8::53"],
"created_on": "2026-06-12T09:00:00Z",
"updated_on": "2026-06-12T09:00:00Z"
}
```
## Retrieve a host object
`GET`, `PUT`, and `DELETE` accept either the host ID (`host_...`) or the hostname as the `{host_reference}` path parameter:
```bash
curl "$OPUSDNS_API_BASE/v1/hosts/ns1.example.com" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Update a host object
`PUT /v1/hosts/{host_reference}` replaces the host's IP addresses with the provided list:
```bash
curl "$OPUSDNS_API_BASE/v1/hosts/ns1.example.com" \
--request PUT \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"ip_addresses": ["192.0.2.54", "2001:db8::54"]
}'
```
If the provided addresses already match the current state at the registry, the request succeeds without performing a registry update.
## Delete a host object
```bash
curl "$OPUSDNS_API_BASE/v1/hosts/ns1.example.com" \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
A host that is still in use as a nameserver by one or more domains cannot be deleted and returns `ERROR_HOST_IN_USE`. Update the affected domains to use different nameservers first.
## Errors
| Code | Status | Meaning |
| ---------------------------------- | ------ | ------------------------------------------------------------------------------------ |
| `ERROR_PARENT_DOMAIN_NOT_FOUND` | 404 | The parent domain of the hostname is not managed in your account. |
| `ERROR_HOST_NOT_FOUND` | 404 | No host object matches the given reference. |
| `ERROR_HOST_ALREADY_EXISTS` | 409 | A host object with this hostname already exists. |
| `ERROR_HOST_IN_USE` | 409 | The host is referenced as a nameserver by one or more domains and cannot be deleted. |
| `ERROR_HOST_OBJECTS_NOT_SUPPORTED` | 422 | The TLD of the parent domain does not use host objects. |
## Related API Reference
* [`POST /v1/hosts`](/api-reference#tag/host/POST/v1/hosts)
* [`GET /v1/hosts/{host_reference}`](/api-reference#tag/host/GET/v1/hosts/%7Bhost_reference%7D)
* [`PUT /v1/hosts/{host_reference}`](/api-reference#tag/host/PUT/v1/hosts/%7Bhost_reference%7D)
* [`DELETE /v1/hosts/{host_reference}`](/api-reference#tag/host/DELETE/v1/hosts/%7Bhost_reference%7D)
# Contact verification
Certain registries require domain holders to verify their identity. When a
registry flags one of your contacts for verification, OpusDNS detects the
requirement, notifies you, and provides API endpoints to submit the required
attestations before the registry-imposed deadlines.
This guide explains what contact verification is, when it applies, and what
the key concepts are. For step-by-step instructions, see the
[Attestation workflow](/products/contacts/attestation-workflow).
## How verification works
1. A registry (e.g., DENIC for `.de` domains) determines that a contact's
identity needs to be verified.
2. OpusDNS receives the verification requirement and flags all affected domains
and contacts.
3. You receive an email notification and a
[`VERIFICATION`](/automation/events/event-object) event with details about the
affected contacts and domains.
4. You submit attestations via the API to prove the contact's identity claims.
5. Once all claims are verified, the registry clears the deadlines and OpusDNS
removes the verification flags automatically.
Verification deadlines are enforced by the registry. If you do not complete verification in time, your domain may be de-delegated (DNS stops resolving) or ultimately deleted. Always act promptly when you receive a verification notification.
## Claims
Claims represent what the registry needs verified about a contact:
| Claim | Description |
| --- | --- |
| `NAME` | The contact's first and last name. |
| `ADDRESS` | The contact's postal address. |
| `EMAIL` | The contact's email address. |
| `PHONE` | The contact's phone number. |
| `LEGAL_ENTITY` | The organization or company name. |
## Verification methods
How the identity claim is proven:
| Method | Description |
| --- | --- |
| `AUTH` | Authentication-based verification. |
| `VDIG` | Video identification (online ID check). |
| `ELECTRONIC_DOCUMENT` | Electronic or digital document verification. |
| `PHYSICAL_DOCUMENT` | Physical document verification (scanned or photographed). |
| `BVR` | Postal verification via registered letter. |
| `PVR` | Postal verification via standard mail. |
| `DATA` | Data-based verification (cross-referencing authoritative databases). |
| `REACHABILITY` | Reachability check (e.g., confirming email or phone access). |
## Verification proofs
The specific type of evidence used:
| Proof | Description |
| --- | --- |
| `IDCARD` | National identity card. |
| `PASSPORT` | Passport. |
| `POPULATION_REGISTER` | Population or civil register extract. |
| `RESIDENCE_PERMIT` | Residence permit. |
| `PROOF_OF_ARRIVAL` | Proof of arrival / registration confirmation. |
| `DRIVERS_LICENCE` | Driver's licence. |
| `COMPANY_REGISTER` | Commercial register extract. |
| `COMPANY_STATEMENT` | Company statement or declaration. |
| `BANK_ACCOUNT` | Bank account verification. |
| `ONLINE_PAYMENT_ACCOUNT` | Online payment account verification. |
| `UTILITY_ACCOUNT` | Utility provider account. |
| `BANK_STATEMENT` | Bank statement. |
| `TAX_STATEMENT` | Tax statement. |
| `WRITTEN_ATTESTATION` | Written attestation or declaration. |
| `DIGITAL_ATTESTATION` | Digital attestation. |
| `POSTAL_VER_TRANSACTION_LOG` | Postal verification transaction log. |
| `EMAIL_VER_TRANSACTION_LOG` | Email verification transaction log. |
| `ADDRESS_DATABASE` | Address database verification. |
## Common attestation examples
| Use case | Method | Proof |
| --- | --- | --- |
| Verify name with a passport | `PHYSICAL_DOCUMENT` | `PASSPORT` |
| Verify name with an ID card | `PHYSICAL_DOCUMENT` | `IDCARD` |
| Verify address with a utility bill | `DATA` | `UTILITY_ACCOUNT` |
| Verify email via confirmation link | `REACHABILITY` | `EMAIL_VER_TRANSACTION_LOG` |
| Verify company via commercial register | `DATA` | `COMPANY_REGISTER` |
| Verify identity via video call | `VDIG` | `IDCARD` or `PASSPORT` |
## Verification states
Each claim on a contact has a verification state:
| State | Meaning |
| --- | --- |
| `UNVERIFIED` | Claim has not been verified. Attestation is required. |
| `IN_PROGRESS` | Attestation submitted, awaiting confirmation from the registry. |
| `VERIFIED` | Claim successfully verified. No action needed. |
| `EXPIRED` | Previous verification has expired. Re-attestation is required. |
## Deadlines
Verification deadlines are set by the registry. Missing them has real
consequences for your domains:
| Deadline type | What happens |
| --- | --- |
| `dedelegation` | The domain's DNS delegation is removed — it stops resolving. This is reversible once verification is completed. |
| `deletion` | The domain is permanently deleted from the registry. This cannot be undone. |
Deadlines follow a predictable sequence:
1. **Notification** — you are informed that verification is required.
2. **De-delegation** — if not resolved, DNS is removed and the domain goes
offline.
3. **Deletion** — the domain is permanently removed from the registry.
Always complete verification well before the de-delegation deadline to avoid any service interruption. Once a domain is deleted by the registry, it cannot be recovered through OpusDNS.
## Notifications
When verification is required, OpusDNS sends an email notification to your
organization with details about the affected contacts and domains.
You can configure where these notifications are sent in your organization
settings:
| Setting | Description |
| --- | --- |
| **Verification notification email** | A specific email address to receive verification notifications. |
| **Enable/disable notifications** | Toggle verification email notifications on or off. |
If no specific email is configured, notifications are sent to your
organization's admin users.
## Next steps
- [Attestation workflow](/products/contacts/attestation-workflow) — respond to
registry-initiated verification requests step by step
- [Initialize verification](/products/contacts/initialize-verification) —
proactively register and verify contacts before a registry requires it
- [Events](/automation/events/event-object) — monitor verification events
- [Tags](/products/tags/overview) — filter domains and contacts by status tags
## Related API reference
- [`GET /v1/contacts/{contact_id}/verifications`](/api-reference#tag/contact/GET/v1/contacts/{contact_id}/verifications)
- [`POST /v1/contacts/{contact_id}/verifications/attest`](/api-reference#tag/contact/POST/v1/contacts/{contact_id}/verifications/attest)
- [`GET /v1/contacts`](/api-reference#tag/contact/GET/v1/contacts)
- [`GET /v1/domains/{domain_reference}`](/api-reference#tag/domain/GET/v1/domains/{domain_reference})
- [`GET /v1/domains`](/api-reference#tag/domain/GET/v1/domains)
- [`GET /v1/events`](/api-reference#tag/event/GET/v1/events)
# Attestation workflow
When a registry flags one of your contacts for verification, follow this workflow to identify the affected domains, review the required claims, and submit attestations through the API.
For background on verification concepts (claims, methods, proofs, deadlines), see the [Contact verification overview](/products/contacts/verification).
## Flow overview
1. Identify domains and contacts requiring verification.
2. Check which claims need to be attested for the affected contact.
3. Submit attestations with the appropriate method, proof, and reference.
4. Confirm the attestation result and track status tag removal.
## 1. Identify affected domains and contacts
When verification is required, both the affected **domains** and **contacts** are tagged with `VERIFICATION_REQUIRED`. Domains also include a `verification_required` field in their response containing the specific claims and deadlines.
### Filter domains by status tag
List all domains currently requiring verification:
```bash
curl --get "$OPUSDNS_API_BASE/v1/domains" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "status_tags=VERIFICATION_REQUIRED"
```
### Filter contacts by status tag
List all contacts currently requiring verification:
```bash
curl --get "$OPUSDNS_API_BASE/v1/contacts" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "status_tags=VERIFICATION_REQUIRED" \
--data-urlencode "include=tags"
```
The response includes a `status_tags` field on each contact when `include=tags` is specified:
```json
{
"contact_id": "contact_01jxe1nzrmf78scaqbkjx0va0f",
"first_name": "Jane",
"last_name": "Smith",
"status_tags": [
{
"label": "VERIFICATION REQUIRED",
"type": "VERIFICATION_REQUIRED"
}
]
}
```
You can combine `status_tags` with `status_tag_mode` (`match_any`, `match_all`, or `match_none`) to control how multiple status tag filters are combined.
### Check the verification\_required field on domains
Every domain response includes a `verification_required` field. When verification is needed, it contains the pending claims and deadlines. When no verification is required, it is `null`.
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.de" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
```json
{
"domain_id": "domain_01jxe1nzrmf78scaqbkjx0va0f",
"name": "example.de",
"verification_required": {
"claims": ["email", "name", "address"],
"deadlines": [
{
"type": "dedelegation",
"date": "2026-07-15T00:00:00Z"
},
{
"type": "deletion",
"date": "2026-08-15T00:00:00Z"
}
]
}
}
```
When no verification is pending, the field is `null`:
```json
{
"domain_id": "domain_01jxe1nzrmf78scaqbkjx0va0f",
"name": "example.de",
"verification_required": null
}
```
### Verification fields
| Field | Type | Description |
| ---------------------------------------- | ---------------- | --------------------------------------------------------------------------------------- |
| `verification_required` | `object \| null` | Present when verification is required, `null` otherwise. |
| `verification_required.claims` | `string[]` | Identity claims that require verification. Values: `name`, `address`, `email`, `phone`. |
| `verification_required.deadlines` | `object[]` | Registry-imposed deadlines with consequences if verification is not completed. |
| `verification_required.deadlines[].type` | `string` | `dedelegation` — DNS stops resolving. `deletion` — domain is permanently removed. |
| `verification_required.deadlines[].date` | `string` | ISO 8601 UTC timestamp of the deadline. |
## 2. Check verification status
Retrieve the current verification state for a contact. This returns the status of each individual claim:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/$CONTACT_ID/verifications" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Response
```json
{
"verifications": [
{
"claim": "NAME",
"state": "VERIFIED",
"method": "PHYSICAL_DOCUMENT",
"proof": "PASSPORT",
"attestation_reference": "REF-2026-001",
"verified_on": "2026-05-10T14:30:00Z",
"expires_on": "2027-05-10T14:30:00Z"
},
{
"claim": "ADDRESS",
"state": "UNVERIFIED",
"method": null,
"proof": null,
"attestation_reference": null,
"verified_on": null,
"expires_on": null
},
{
"claim": "EMAIL",
"state": "IN_PROGRESS",
"method": "REACHABILITY",
"proof": "EMAIL_VER_TRANSACTION_LOG",
"attestation_reference": "email-verif-20260518",
"verified_on": null,
"expires_on": null
}
]
}
```
### Error responses
| Status | Meaning |
| ------ | ----------------------------------------------------------------------------------------------------------------------------- |
| `404` | Contact has not yet been flagged for verification. This typically means verification has not been initiated for this contact. |
| `502` | The verification service is temporarily unavailable. Retry later. |
## 3. Submit attestations
Submit one or more attestations to verify identity claims for a contact:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/$CONTACT_ID/verifications/attest" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"attestations": [
{
"claim": "NAME",
"method": "PHYSICAL_DOCUMENT",
"proof": "PASSPORT",
"attestation_reference": "REF-2026-001"
},
{
"claim": "ADDRESS",
"method": "PHYSICAL_DOCUMENT",
"proof": "PASSPORT",
"attestation_reference": "REF-2026-001"
}
]
}'
```
### Request fields
| Field | Required | Description |
| -------------------------------------- | -------- | ----------------------------------------------------------------------------------------------------- |
| `attestations` | Yes | Array of attestation objects (max 50 per request). |
| `attestations[].claim` | Yes | The claim being verified. See [Claims](/products/contacts/verification#claims). |
| `attestations[].method` | Yes | How the claim is being verified. See [Methods](/products/contacts/verification#verification-methods). |
| `attestations[].proof` | Yes | The specific evidence type used. See [Proofs](/products/contacts/verification#verification-proofs). |
| `attestations[].attestation_reference` | Yes | Your reference identifier for the attestation (max 255 characters). |
### Registry-specific constraints
Some registries impose extra rules on top of the request format above. These constraints apply only when the contact is a registrant on domains of that TLD that currently require verification — for every other TLD, the standard request format applies.
| TLD | Registry | Constraint |
| ----- | -------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `.de` | DENIC | All attestations in a single request must share the same `method`, `proof`, and `attestation_reference`. Submit one request per method/proof combination if the claims need different ones. |
Violating a registry-specific constraint rejects the **entire** request — no attestation in it is submitted. Check the table above before batching attestations for a contact.
### Response
The response returns the updated verification state for all claims — same format as the GET endpoint.
### Error responses
| Status | Code | Meaning |
| ------ | ----------------------------------------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `400` | `ERROR_DOMAIN_VERIFICATION_INCONSISTENT_METHOD_PROOF` | Multiple attestations in one request use different methods or proofs, which the registry does not allow. See [Registry-specific constraints](#registry-specific-constraints). |
| `404` | `ERROR_CONTACT_VERIFICATION_UPSTREAM_NOT_FOUND` | Contact has not been registered for verification. |
| `502` | `ERROR_CONTACT_VERIFICATION_UPSTREAM_ERROR` | Verification service temporarily unavailable. |
## 4. After attestation
The attest endpoint returns the updated verification state for all claims directly in the response. You can immediately see whether each claim moved to `VERIFIED` or `IN_PROGRESS`.
Once all claims reach the `VERIFIED` state, the registry clears the deadlines. OpusDNS automatically:
* Removes the `VERIFICATION_REQUIRED` status tag from:
* the **contact**: immediately after successful attestation
* affected **domains**: on the next domain sync.
* Sets `verification_required` to `null` on affected domain responses.
If any claims are still `IN_PROGRESS` after attestation (awaiting registry confirmation), you can check back later using the GET endpoint:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/$CONTACT_ID/verifications" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
You can also monitor verification-related events through the events API:
```bash
curl --get "$OPUSDNS_API_BASE/v1/events" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "object_type=CONTACT" \
--data-urlencode "type=VERIFICATION"
```
By default, the events API returns only pending (unacknowledged) events. Pass `acknowledged=true` to list events you have already acknowledged.
## Troubleshooting
| Issue | Cause | Resolution |
| ------------------------------------------------------ | ----------------------------------------------------------------------------------------------------- | --------------------------------------------------------------------------------------------------------------------------------- |
| `404` on GET verification status | Contact hasn't been flagged for verification yet. | Wait for the verification process to initialize, or check that you're using the correct contact ID. |
| `400` inconsistent method/proof | Multiple attestations use different methods or proofs in one request (`.de` restriction). | Submit separate requests — one per method/proof combination. See [Registry-specific constraints](#registry-specific-constraints). |
| Claims stuck in `IN_PROGRESS` | Registry hasn't confirmed the attestation yet. | Wait and poll again. Registry confirmation can take time. |
| Contact tag removed but domain tag remains | Contact tag is removed immediately after attestation; domain tags are cleared on the next sync cycle. | Wait a few minutes for the domain sync to run. |
| `verification_required` still present after `VERIFIED` | Domain hasn't synced yet. | The field is cleared on the next domain sync cycle. This typically happens within minutes. |
## Next steps
* [Contact verification overview](/products/contacts/verification) — claims, methods, proofs, and deadline reference
* [Initialize verification](/products/contacts/initialize-verification) — proactively register contacts for verification
# Initialize verification
This feature is coming soon and is under active development.
In addition to responding to registry-initiated verification requests, OpusDNS
will allow you to **trigger verification processes directly** — initiating
email confirmations, identity checks, and other verification flows for your
contacts without waiting for a registry to require them.
## Why verify proactively?
When a registry like DENIC flags a contact for verification, you are working
against a deadline. By triggering verification ahead of time, you can:
- **Avoid deadline pressure** — contacts are already verified when the registry
eventually requires it, so your domains are never at risk.
- **Stay NIS2 compliant** — meet identity verification requirements without
waiting for registry enforcement.
## Verification flows
OpusDNS will support triggering the following verification processes directly
for your registrants:
- **Email verification** — sends a confirmation email to the contact. Once the
registrant confirms, the `EMAIL` claim is verified automatically.
- **Identity verification** — initiates an identity check session (e.g., video
identification or document upload) where the registrant verifies their name
and address directly.
These flows are managed end-to-end by OpusDNS — you trigger them, the
registrant completes the required steps, and the claim states update
automatically.
You can also combine triggered flows with
[external attestations](/products/contacts/attestation-workflow) — for example,
trigger an email verification for the `EMAIL` claim while submitting a document
attestation for the `NAME` claim.
## Next steps
- [Contact verification overview](/products/contacts/verification) — claims,
methods, proofs, and deadline reference
- [Attestation workflow](/products/contacts/attestation-workflow) — respond to
verification requests step by step
# Postal codes
The `postal_code` of a contact is validated against the country's published
postal format and stored in that country's canonical notation. Validation runs
when the contact is written — with `POST /v1/contacts`, or with the
`contact_create` and `contact_create_bulk`
[job commands](/automation/jobs/dns-commands) — so a postal code a registry
would refuse fails immediately, with the field named, instead of failing at the
registry after the contact has been stored.
## Validated countries
An invalid postal code is refused for these countries:
| Country | Example format |
| --- | --- |
| `AT` Austria | `1010` |
| `BE` Belgium | `4000` |
| `CA` Canada | `H3Z 2Y7` |
| `CH` Switzerland | `2544` |
| `CZ` Czechia | `100 00` |
| `DE` Germany | `26133` |
| `DK` Denmark | `8660` |
| `ES` Spain | `28039` |
| `FR` France | `33380` |
| `GB` United Kingdom | `EC1Y 8SY` |
| `IT` Italy | `00144` |
| `LU` Luxembourg | `4750` |
| `NL` Netherlands | `1234 AB` |
| `NO` Norway | `0025` |
| `SE` Sweden | `11455` |
| `US` United States | `95014` |
Contacts in any other country accept whatever you submit. One rule applies
everywhere: a postal code containing non-ASCII characters is rejected for every
country, because it cannot be transmitted to a registry.
## Rejected postal codes
An invalid postal code returns `422` with a `request-validation-failed` problem
that names the field, so it can be mapped back to a form field:
```json
{
"type": "request-validation-failed",
"title": "Request validation error.",
"status": 422,
"errors": [
{
"type": "invalid_postal_code",
"loc": ["body", "postal_code"],
"msg": "'93053' is not a valid postal code for country 'NL', expected a format like '1234 AB'",
"input": "93053",
"ctx": {
"message": "'93053' is not a valid postal code for country 'NL', expected a format like '1234 AB'"
}
}
]
}
```
`type` is `invalid_postal_code` — a stable key for this rejection — and `msg`
quotes the value you submitted together with an example of the expected format.
## What gets stored
Postal codes are canonicalized on write, so the stored value can differ from
what you submitted:
| Submitted | Country | Stored |
| --- | --- | --- |
| `1234AB` | `NL` | `1234 AB` |
| `1234 ab` | `NL` | `1234 AB` |
| `D-26133` | `DE` | `26133` |
| `NL-1234AB` | `NL` | `1234 AB` |
| `12345 6789` | `US` | `12345-6789` |
| `100 00` | `CZ` | `100 00` |
- Dutch postal codes are stored in the official national notation — four
digits, a space, two upper-case letters. Both `1234AB` and `1234 ab` are
accepted.
- The cross-border country prefix (`D-`, `NL-`, `F-`, …) is not part of a postal
code and is stripped. It is only stripped when it matches the contact's own
country: `F-26133` on a `DE` contact keeps the `F-` and is rejected as an
invalid German postal code.
- US ZIP+4 is stored in the hyphenated form.
- Where a space is part of the national format, as in `CZ` and `GB`, it is kept.
## Registry-specific formats
Some registries require a different form than the national notation — SIDN, for
example, requires a `.nl` postal code without the space. OpusDNS applies those
rules when it builds the registry request. Store and submit the national format
and never pre-format a postal code for a registry; the value you read back from
the API is always the canonical national form.
## Imported contacts
Contacts mirrored from another registrar or registry — domain import,
transfer-in, and registrar sync — are canonicalized where possible but are
never rejected for their postal code format, so an off-format value held at the
losing registrar cannot fail an import.
## Registry rejections
A registry can still refuse an address for its own reasons. Where the registry
reports which field was at fault, that text is included in the `detail` of the
resulting problem, after the generic result code:
```
2308: Validation of the transaction failed. Contact address group: A postcode has to be four numbers and two letters.
```
## Errors
| Code | Status | Meaning |
| --- | --- | --- |
| `invalid_postal_code` | 422 | The postal code is not valid for the contact's country. Returned as an error `type` inside a `request-validation-failed` problem, with `loc` naming `postal_code`. |
| `ERROR_REGISTRY_POLICY` | 422 | The registry rejected the request. `detail` carries the registry's field-level message where the registry provides one. |
## Related API Reference
- [`POST /v1/contacts`](/api-reference#tag/contact/POST/v1/contacts)
- [`GET /v1/contacts`](/api-reference#tag/contact/GET/v1/contacts)
- [`GET /v1/contacts/{contact_id}`](/api-reference#tag/contact/GET/v1/contacts/{contact_id})
# TLD specifications
Every Top-Level Domain (TLD) has its own rules for registration, transfers,
DNS configuration, and more. The OpusDNS API provides endpoints to query these
specifications so you can build TLD-aware workflows.
## List your supported TLDs
Retrieve the TLDs available to your organization:
```bash
curl "$OPUSDNS_API_BASE/v1/tlds/portfolio" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
This returns the list of TLDs enabled for your account. Only these TLDs can be
used for domain registration and availability checks.
## List all TLD specifications
Query the full specification catalog:
```bash
curl "$OPUSDNS_API_BASE/v1/tlds/" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
You can filter the response to specific TLDs or fields:
```bash
curl --get "$OPUSDNS_API_BASE/v1/tlds/" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "tlds=com" \
--data-urlencode "tlds=net" \
--data-urlencode "fields=domain_lifecycle" \
--data-urlencode "fields=transfer_policies"
```
## Get a single TLD specification
Retrieve the full specification for one TLD:
```bash
curl "$OPUSDNS_API_BASE/v1/tlds/com" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Specification categories
A TLD specification contains the following sections:
### Domain lifecycle
Defines registration, renewal, and expiration rules:
- **Registration periods** — minimum and maximum registration length
- **Renewal periods** — allowed renewal durations
- **Grace periods** — time after expiration before the domain enters redemption
- **Redemption period** — window to restore a deleted domain
- **Auto-renew behavior** — whether the registry auto-renews and when
### Transfer policies
Rules governing domain transfers:
- **Auth code requirements** — whether an authorization code is needed
- **Transfer lock** — minimum lock period after registration or transfer
- **Transfer timing** — how long transfers take to complete
- **Renewal on transfer** — whether the domain is renewed when transferred
- **Post-transfer requirements** — actions needed after a transfer completes
### DNS configuration
Nameserver and DNSSEC rules:
- **Nameserver limits** — minimum and maximum number of nameservers
- **DNSSEC support** — whether DNSSEC is allowed, mandatory, or unsupported
- **DNSSEC mode** — DS records, KEY records, or both
- **Host object rules** — constraints on glue records and host objects
### Contact requirements
What contact information the registry requires:
- **Required roles** — which contact roles must be provided (registrant, admin,
tech, billing)
- **Local presence** — whether a local address or representative is required
- **Registry-specific attributes** — additional fields like tax ID, company
registration number, or intended use
### Premium domains
- **Premium support** — whether the TLD has premium-priced domains
- **Pricing source** — where premium pricing comes from
- **Affected operations** — which operations (register, renew, transfer) can
have premium pricing
### Launch phases
For new TLDs or TLDs with special registration periods:
- **Landrush** — early registration before general availability
- **Early Access Program (EAP)** — registration at decreasing premium prices
- **General Availability** — open registration for everyone
### Other features
- **IDN support** — whether internationalized domain names are available
- **Registry lock** — enhanced security lock at the registry level
- **Reserved domains** — domains the registry has reserved
- **Legal requirements** — terms, dispute resolution, and compliance rules
## Example: checking before registration
Before registering a domain, query the TLD spec to understand requirements:
```bash
# Check what contacts are needed for .de domains
curl "$OPUSDNS_API_BASE/v1/tlds/de" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
| jq '.contacts'
```
This helps you prepare the correct contact data and registration parameters
before submitting your request.
## Related API Reference
- [`GET /v1/tlds/`](/api-reference#tag/tld/GET/v1/tlds/)
- [`GET /v1/tlds/portfolio`](/api-reference#tag/tld/GET/v1/tlds/portfolio)
- [`GET /v1/tlds/{tld}`](/api-reference#tag/tld/GET/v1/tlds/{tld})
# .eu domain operations
`.eu` domains are managed by [EURid](https://eurid.eu), the registry for the
European Union. The OpusDNS API provides a dedicated endpoint for requesting
auth codes from the registry.
## Request an auth code
Request a new authorization code for a `.eu` domain directly from EURid. The
auth code is returned in the API response.
```bash
curl "$OPUSDNS_API_BASE/v1/domains/tld-specific/eu/example.eu/auth_code/request" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Response
```json
{
"name": "example.eu",
"success": true,
"auth_code": "aBcDeFgH1234",
"auth_code_expires_on": "2026-06-04T10:30:00Z"
}
```
| Field | Type | Description |
| --- | --- | --- |
| `name` | `string` | The domain name. |
| `success` | `boolean` | Whether the auth code was successfully generated. |
| `auth_code` | `string` | The authorization code. Only present when `success` is `true`. |
| `auth_code_expires_on` | `datetime` | When the auth code expires. Only present when `success` is `true`. |
| `detail` | `string` | Error details. Only present when `success` is `false`. |
## Transfer behavior
`.eu` transfers follow the standard EPP transfer process once you have the auth
code. The losing registrar has 5 days to approve or reject the transfer. If no
action is taken, the transfer is auto-approved.
## Related API Reference
- [`POST /v1/domains/tld-specific/eu/{domain_reference}/auth_code/request`](/api-reference#tag/domain_tld_specific/POST/v1/domains/tld-specific/eu/{domain_reference}/auth_code/request)
# .be domain operations
`.be` domains are managed by [DNS Belgium](https://www.dnsbelgium.be), the
registry for Belgium. The OpusDNS API provides a dedicated endpoint for
requesting auth codes from the registry.
## Request an auth code
`.be` domains require you to explicitly request a new authorization code from
DNS Belgium. The code is sent to the registrant's email address on file.
```bash
curl "$OPUSDNS_API_BASE/v1/domains/tld-specific/be/example.be/auth_code/request" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Response
```json
{
"name": "example.be",
"success": true
}
```
| Field | Type | Description |
| --- | --- | --- |
| `name` | `string` | The domain name. |
| `success` | `boolean` | Whether the request was successfully submitted to DNS Belgium. |
| `detail` | `string` | Error details. Only present when `success` is `false`. |
> **Note:** This endpoint submits the request to DNS Belgium — it does not
> return the auth code directly. The registrant will receive the code via email
> from the registry.
### Prerequisites
The domain must not have `transfer_lock` enabled. Unlock it first via
`PATCH /v1/domains/{domain_reference}` with `"transfer_lock": false`.
## Transfer behavior
`.be` transfers follow the standard EPP transfer process once the registrant
has received the auth code via email.
## Related API Reference
- [`POST /v1/domains/tld-specific/be/{domain_reference}/auth_code/request`](/api-reference#tag/domain_tld_specific/POST/v1/domains/tld-specific/be/{domain_reference}/auth_code/request)
# .cz domain operations
`.cz` domains are managed by [CZ.NIC](https://www.nic.cz), the registry for the
Czech Republic. CZ.NIC runs the FRED registry system, which exposes auth code
delivery as a registry-level extension command rather than as part of the
standard domain lifecycle.
## Request an auth code
CZ.NIC generates the authorization code on demand and never discloses its value
over EPP, so it cannot be read back through the standard domain endpoints. You
request it explicitly, and the registry mails it to the registrant and to every
administrative contact on the domain.
```bash
curl "$OPUSDNS_API_BASE/v1/domains/tld-specific/cz/example.cz/auth_code/request" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Response
```json
{
"name": "example.cz",
"success": true,
"recipients": ["j*****@d*****.*"]
}
```
| Field | Type | Description |
| --- | --- | --- |
| `name` | `string` | The domain name. |
| `success` | `boolean` | Whether the request was successfully submitted to CZ.NIC. |
| `recipients` | `string[]` | Masked addresses the registry sent the code to. Empty when the registry does not disclose them. |
| `detail` | `string` | Error details. Only present when `success` is `false`. |
> **Note:** This endpoint submits the request to CZ.NIC, it does not return the
> auth code directly. The recipients receive the code via email from the
> registry, and `recipients` only ever contains masked addresses.
### Prerequisites
The domain must not carry the `serverTransferProhibited` status. CZ.NIC accepts
the command and answers with a success code in that case, but sends nothing, so
the request is rejected before it reaches the registry.
## Transfer behavior
`.cz` transfers follow the standard EPP transfer process once the holder has
received the auth code via email.
| Policy | Value |
| --- | --- |
| Auth code required | Yes, generated by the registry rather than chosen by the registrar |
| Auth code validity | 14 days from the moment it is generated |
| Transfer acknowledgement | None, transfers complete immediately |
| Transfer lock | Cannot be set by the registrar. The registry may still apply `serverTransferProhibited` |
| Transfer renews the domain | No |
Two consequences worth planning around:
- The code expires after 14 days, so request it close to when the transfer will
actually be started.
- Completing a transfer invalidates the code that was used, and the registry
issues a fresh one for the new sponsoring registrar.
## Related API Reference
- [`POST /v1/domains/tld-specific/cz/{domain_reference}/auth_code/request`](/api-reference#tag/domain_tld_specific/POST/v1/domains/tld-specific/cz/{domain_reference}/auth_code/request)
# .de domain operations
`.de` domains are managed by [DENIC](https://www.denic.de), the registry for
Germany. The OpusDNS API provides a dedicated transit endpoint for `.de` domains.
## Transit
The transit operation disconnects a `.de` domain from its current registrar,
putting it into a transit state at the registry. The domain remains functional
and continues to resolve, but is no longer managed by any registrar.
```bash
curl "$OPUSDNS_API_BASE/v1/domains/tld-specific/de/example.de/transit" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"disconnect": true
}'
```
### Request fields
| Field | Type | Required | Description |
| --- | --- | --- | --- |
| `disconnect` | `boolean` | Yes | Set to `true` to disconnect the domain from the current registrar and update to DENIC nameservers. |
### Response
```json
{
"name": "example.de",
"success": true
}
```
### What happens during transit
1. The domain is disconnected from OpusDNS as the managing registrar.
2. DENIC takes over nameserver resolution using their default nameservers.
3. The domain enters a transit state and can be picked up by any
DENIC-accredited registrar.
> **Note:** Transit is specific to DENIC's registry model. It is commonly used
> when the domain holder wants to switch registrars without a traditional
> auth-code-based transfer.
## Transfer behavior
`.de` domain transfers are **immediate**. When you transfer a `.de` domain into
OpusDNS using `POST /v1/domains/transfer`, the transfer completes right away —
there is no pending period or approval wait time. The domain moves to your
account as soon as the transfer request is processed.
## Related API Reference
- [`POST /v1/domains/tld-specific/de/{domain_reference}/transit`](/api-reference#tag/domain_tld_specific/POST/v1/domains/tld-specific/de/{domain_reference}/transit)
# .at domain operations
`.at` domains are managed by [nic.at](https://www.nic.at), the registry for
Austria. The OpusDNS API provides a dedicated withdraw endpoint for `.at`
domains.
## Withdraw
The withdraw operation removes a `.at` domain from the registry. This is
different from a standard deletion — it signals to the registry that the
registrar is withdrawing the domain.
```bash
curl "$OPUSDNS_API_BASE/v1/domains/tld-specific/at/example.at/withdraw" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"zone_delete": true
}'
```
### Request fields
| Field | Type | Required | Description |
| --- | --- | --- | --- |
| `zone_delete` | `boolean` | Yes | Whether to inform the registry that the DNS zone for the domain has already been deleted. |
### Response
```json
{
"name": "example.at",
"success": true
}
```
> **Note:** The `zone_delete` field informs nic.at whether the nameservice for
> the domain has already been stopped. This is part of nic.at's registry
> protocol.
## Related API Reference
- [`POST /v1/domains/tld-specific/at/{domain_reference}/withdraw`](/api-reference#tag/domain_tld_specific/POST/v1/domains/tld-specific/at/{domain_reference}/withdraw)
# .uk domain operations
`.uk` domains (including `.co.uk`, `.org.uk`, `.me.uk`, `.ltd.uk`, `.plc.uk`, and `.net.uk`) are managed by [Nominet](https://www.nominet.uk). The `.uk` namespace uses a tag-based transfer system that differs from the standard EPP auth code model used by most other TLDs.
OpusDNS's Nominet tag is **OPUSDNS**.
## Transfer in
To transfer a `.uk` domain into OpusDNS, the process works differently from other TLDs. You must first create the transfer request in OpusDNS, then have the current registrar release the domain to OpusDNS's Nominet tag.
### Step 1: Submit the transfer request
Create the transfer in OpusDNS first so we are ready to receive the domain:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/transfer" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "example.co.uk",
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "renew",
"create_zone": true
}'
```
For `.uk` domains no auth code is needed because Nominet uses a tag-based transfer system.
### Step 2: Request the tag release
Ask the current registrar to release the domain to OpusDNS's Nominet tag, **`OPUSDNS`**. Once they push the domain to our tag, the transfer completes and the domain appears in your account.
> **Note:** `.uk` transfers are typically **immediate** — once the domain is released to OpusDNS's tag, it moves to your account without a pending period.
## Transfer out
To transfer a `.uk` domain away from OpusDNS, the domain must be released to the receiving registrar's Nominet tag. This transfer-out release is not currently exposed through the public API.
Use the dashboard or contact support when you need to push a `.uk` domain to another registrar. You will need the receiving registrar's Nominet tag.
## Supported extensions
The following `.uk` extensions are managed by Nominet and support these operations:
| Extension | Supported |
| --------- | --------- |
| `.uk` | ✅ |
| `.co.uk` | ✅ |
| `.org.uk` | ✅ |
| `.me.uk` | ✅ |
| `.ltd.uk` | ✅ |
| `.plc.uk` | ✅ |
| `.net.uk` | ✅ |
## Related API Reference
* [`POST /v1/domains/transfer`](/api-reference#tag/domain/POST/v1/domains/transfer)
# .se and .nu domain operations
`.se` and `.nu` domains are managed by
[Internetstiftelsen](https://internetstiftelsen.se), the Swedish Internet
Foundation. Both TLDs run on the same registry platform and follow the same
rules, and each has its own endpoint for generating auth codes at the registry.
## Request an auth code
`.se` and `.nu` auth codes are owned by the registry. A registrar cannot choose
the value: the registry generates it and returns it when the domain is
registered, and it is not exposed in a later domain info request. This endpoint
requests a fresh code from the registry and stores it, which is how a code
consumed by a transfer is replaced.
```bash
curl "$OPUSDNS_API_BASE/v1/domains/tld-specific/se/example.se/auth_code/request" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
`.nu` has its own path, and each endpoint accepts only names within its own TLD:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/tld-specific/nu/example.nu/auth_code/request" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Response
```json
{
"name": "example.se",
"success": true,
"auth_code": "TEST-260908-OPUSDN-7d146e3b-f6df-4302-ad95-cf28574e4354"
}
```
| Field | Type | Description |
| --- | --- | --- |
| `name` | `string` | The domain name. |
| `success` | `boolean` | Whether the registry generated a fresh auth code. |
| `auth_code` | `string` | The code generated by the registry. Only present when `success` is `true`. |
| `detail` | `string` | Error details. Only present when `success` is `false`. |
> **Note:** Unlike registries that email the code to the registrant, this
> endpoint returns it directly. Requesting a new code **invalidates the previous
> one**, so only call it when the current code is unusable.
### Prerequisites
The domain must be sponsored by your account. The endpoint requires the same
permission as a domain update.
## Transfer behavior
`.se` and `.nu` transfers are **immediate**. There is no pending period, no
approval and no rejection: a transfer request either completes at once or fails.
This has two consequences worth planning for:
- the gaining registrar learns the outcome from the transfer response itself,
with no notification to wait for;
- the losing registrar is notified after the fact and cannot prevent the
transfer.
Transfers do not extend the registration period, and the auth code is consumed
in the process. Request a new one through the endpoint above if the domain needs
to be transferable again.
## Registrant verification
Internetstiftelsen may hold a new registration while it verifies the
registrant's data. The domain is created, but the registry applies `serverHold`,
`serverTransferProhibited` and `serverRenewProhibited` until the check clears, so
it does not resolve and cannot be transferred or renewed in the meantime.
The check clears when the registry accepts the registrant data, or when the
registrant is replaced with one that passes. In either case the registry reports
the outcome and the statuses are reconciled onto the domain automatically.
## Contact attributes
Every registrant needs `REGISTRY_SE_ORG_NO`, a personal or organization number
prefixed with a bracketed country code. See
[`.se`](/tld-knowledge-base/cctlds/se#contact-attributes) or
[`.nu`](/tld-knowledge-base/cctlds/nu#contact-attributes) in the TLD Knowledge
Base for the format and its validation rules.
## Related API Reference
- [`POST /v1/domains/tld-specific/se/{domain_reference}/auth_code/request`](/api-reference#tag/domain_tld_specific/POST/v1/domains/tld-specific/se/{domain_reference}/auth_code/request)
- [`POST /v1/domains/tld-specific/nu/{domain_reference}/auth_code/request`](/api-reference#tag/domain_tld_specific/POST/v1/domains/tld-specific/nu/{domain_reference}/auth_code/request)
# The zone object
A zone represents a DNS zone hosted on the OpusDNS nameserver infrastructure.
Zones contain resource record sets (RRsets), each holding one or more DNS
records.
## Example response
```json
{
"dns_zone_id": "zone_01h45ytscbebyvny4gc8cr8ma2",
"name": "example.com",
"dnssec_status": "enabled",
"domain_parts": {
"domain": "example",
"subdomain": null,
"suffix": "com"
},
"rrsets": [
{
"name": "example.com.",
"type": "A",
"ttl": 3600,
"protected": false,
"protected_reason": null,
"records": [
{ "rdata": "93.184.216.34", "protected": false, "protected_reason": null }
]
},
{
"name": "example.com.",
"type": "SOA",
"ttl": 3600,
"protected": true,
"protected_reason": "SYSTEM_MANAGED_SOA",
"records": [
{ "rdata": "ns1.opusdns.com. hostmaster.example.com. 2026050401 3600 900 1209600 300", "protected": true, "protected_reason": "SYSTEM_MANAGED_SOA" }
]
},
{
"name": "example.com.",
"type": "NS",
"ttl": 3600,
"protected": true,
"protected_reason": "SYSTEM_MANAGED_NS",
"records": [
{ "rdata": "ns1.opusdns.com.", "protected": true, "protected_reason": "SYSTEM_MANAGED_NS" },
{ "rdata": "ns2.opusdns.net.", "protected": true, "protected_reason": "SYSTEM_MANAGED_NS" }
]
}
],
"tags": null,
"created_on": "2026-01-15T10:30:00Z",
"updated_on": "2026-01-15T10:30:00Z"
}
```
## Fields
| Field | Type | Description |
| --- | --- | --- |
| `dns_zone_id` | `string` | Unique identifier (TypeID format, prefixed with `zone_`). |
| `name` | `string` | The zone name (e.g., `example.com`). |
| `dnssec_status` | `string` | DNSSEC signing status: `enabled` or `disabled`. |
| `domain_parts` | `object` | Parsed components of the zone name. |
| `domain_parts.domain` | `string \| null` | The second-level domain label (e.g., `example`). |
| `domain_parts.subdomain` | `string \| null` | The subdomain label, if any. |
| `domain_parts.suffix` | `string \| null` | The TLD suffix (e.g., `com`). |
| `rrsets` | `array` | Resource record sets in the zone. See [RRset structure](#rrset-structure). |
| `tags` | `array \| null` | Tags assigned to the zone. Only included when `?include=tags` is specified. |
| `created_on` | `datetime` | When the zone was created. |
| `updated_on` | `datetime` | When the zone was last modified. |
## RRset structure
Each RRset groups DNS records of the same name and type.
| Field | Type | Description |
| --- | --- | --- |
| `name` | `string` | The fully-qualified record name (e.g., `example.com.`). |
| `type` | `string` | The record type. See [Supported record types](#supported-record-types). |
| `ttl` | `integer` | Time-to-live in seconds. |
| `records` | `array` | Individual DNS records. See [Record structure](#record-structure). |
| `protected` | `boolean` | Whether the RRset is system-managed. |
| `protected_reason` | `string \| null` | Why the RRset is protected. See [Protected records](#protected-records). |
## Record structure
Each record within an RRset holds a single `rdata` value.
| Field | Type | Description |
| --- | --- | --- |
| `rdata` | `string` | The record data (e.g., an IP address, hostname, or TXT value). |
| `protected` | `boolean` | Whether this individual record is system-managed. |
| `protected_reason` | `string \| null` | Why the record is protected. |
## Supported record types
OpusDNS supports 21 DNS record types:
| Type | Description | Example rdata |
| --- | --- | --- |
| `A` | IPv4 address | `93.184.216.34` |
| `AAAA` | IPv6 address | `2606:2800:220:1:248:1893:25c8:1946` |
| `ALIAS` | ANAME/alias record (zone apex CNAME alternative) | `other.example.com.` |
| `CAA` | Certificate Authority Authorization | `0 issue "letsencrypt.org"` |
| `CERT` | Certificate record | `PKIX 1 SHA-256 ...` |
| `CNAME` | Canonical name | `www.example.com.` |
| `DNSKEY` | DNSSEC public key | `257 3 13 ...` |
| `DS` | Delegation signer | `12345 13 2 ...` |
| `HTTPS` | HTTPS service binding | `1 . alpn="h2,h3"` |
| `MX` | Mail exchange | `10 mail.example.com.` |
| `NAPTR` | Naming Authority Pointer | `100 10 "u" "sip+E2U" "!^.*$!sip:info@example.com!" .` |
| `NS` | Nameserver | `ns1.opusdns.com.` |
| `PTR` | Pointer (reverse DNS) | `host.example.com.` |
| `TXT` | Text record | `"v=spf1 include:_spf.example.com ~all"` |
| `SOA` | Start of Authority | `ns1.opusdns.com. hostmaster.example.com. ...` |
| `SRV` | Service locator | `10 5 5060 sip.example.com.` |
| `SMIMEA` | S/MIME certificate association | `3 1 1 ...` |
| `SSHFP` | SSH fingerprint | `2 1 123456...` |
| `SVCB` | Service binding | `1 . alpn="h2"` |
| `TLSA` | TLS certificate association | `3 1 1 ...` |
| `URI` | Uniform Resource Identifier | `10 1 "https://example.com"` |
## Protected records
Certain records are system-managed and cannot be modified through the API.
Protected records and RRsets have `protected: true` and a `protected_reason`:
| Reason | Description |
| --- | --- |
| `SYSTEM_MANAGED_SOA` | The SOA record is automatically managed by OpusDNS. |
| `SYSTEM_MANAGED_NS` | NS records at the zone apex are managed by OpusDNS. |
| `EMAIL_FORWARD` | Records created for email forwarding configuration. |
| `DOMAIN_FORWARD` | Records created for domain forwarding (HTTP redirects). |
| `GENERIC` | Other system-managed records. |
Attempting to modify a protected record will result in an error. To change
email or domain forwarding records, use the respective forwarding APIs instead.
## Related API Reference
- [`GET /v1/dns`](/api-reference#tag/dns/GET/v1/dns)
- [`GET /v1/dns/{zone_name}`](/api-reference#tag/dns/GET/v1/dns/{zone_name})
- [`POST /v1/dns`](/api-reference#tag/dns/POST/v1/dns)
# Manage zones
A DNS zone is the authoritative container for all DNS records of a domain. You
can create zones independently or have them created automatically during
domain registration by setting `create_zone: true`.
## Create a zone
```bash
curl "$OPUSDNS_API_BASE/v1/dns" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "example.com"
}'
```
### Request fields
| Field | Type | Required | Description |
| --- | --- | --- | --- |
| `name` | `string` | Yes | The zone name (e.g., `example.com`). |
| `rrsets` | `array` | No | Initial RRsets to create with the zone. |
| `dnssec_status` | `string` | No | `enabled` or `disabled` (default: `disabled`). |
### Create with initial records
You can provision a zone with records in a single request:
```bash
curl "$OPUSDNS_API_BASE/v1/dns" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "example.com",
"dnssec_status": "enabled",
"rrsets": [
{
"name": "example.com.",
"type": "A",
"ttl": 3600,
"records": [{ "rdata": "93.184.216.34" }]
},
{
"name": "www.example.com.",
"type": "CNAME",
"ttl": 3600,
"records": [{ "rdata": "example.com." }]
},
{
"name": "example.com.",
"type": "MX",
"ttl": 3600,
"records": [
{ "rdata": "10 mail.example.com." },
{ "rdata": "20 mail2.example.com." }
]
}
]
}'
```
### Automatic zone creation
When registering or transferring a domain, you can set `create_zone: true` in
the request body. This creates a DNS zone for the domain on the OpusDNS
nameserver infrastructure. Note that `create_zone` and setting `nameservers`
are independent operations — see
[Register a domain](/products/domains/register) for details.
## List zones
Retrieve a paginated list of zones:
```bash
curl "$OPUSDNS_API_BASE/v1/dns?page=1&page_size=25" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Filter and sort options
| Parameter | Description |
| --- | --- |
| `name` | Filter by exact zone name. |
| `search` | Search zones by name (partial match). |
| `suffix` | Filter by TLD suffix (e.g., `com`, `de`). |
| `dnssec_status` | Filter by DNSSEC status: `enabled` or `disabled`. |
| `tag_ids` | Filter by tag IDs (comma-separated). |
| `tag_mode` | Tag matching mode when filtering by multiple tags. |
| `created_after` | Zones created after this date. |
| `created_before` | Zones created before this date. |
| `updated_after` | Zones updated after this date. |
| `updated_before` | Zones updated before this date. |
| `sort_by` | Sort field: `name`, `created_on`, `updated_on`, or `dnssec_status`. |
| `sort_order` | Sort direction: `asc` or `desc`. |
| `include` | Include additional data: `tags`. |
Example — list all DNSSEC-enabled `.de` zones:
```bash
curl --get "$OPUSDNS_API_BASE/v1/dns" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "suffix=de" \
--data-urlencode "dnssec_status=enabled" \
--data-urlencode "sort_by=name" \
--data-urlencode "sort_order=asc"
```
## Get a zone
Retrieve a single zone with all its records:
```bash
curl "$OPUSDNS_API_BASE/v1/dns/example.com" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
To include tags:
```bash
curl "$OPUSDNS_API_BASE/v1/dns/example.com?include=tags" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Get zones summary
Get aggregate statistics about your zones:
```bash
curl "$OPUSDNS_API_BASE/v1/dns/summary" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Returns the total number of zones and a breakdown by DNSSEC status:
```json
{
"total_zones": 142,
"zones_by_dnssec": {
"enabled": 89,
"disabled": 53
}
}
```
## Delete a zone
Remove a zone and all its records:
```bash
curl "$OPUSDNS_API_BASE/v1/dns/example.com" \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Deleting a zone removes all DNS records. This does not affect the domain registration itself — the domain will continue to exist but will no longer resolve through OpusDNS nameservers.
## Related API Reference
- [`GET /v1/dns`](/api-reference#tag/dns/GET/v1/dns)
- [`POST /v1/dns`](/api-reference#tag/dns/POST/v1/dns)
- [`GET /v1/dns/{zone_name}`](/api-reference#tag/dns/GET/v1/dns/{zone_name})
- [`GET /v1/dns/summary`](/api-reference#tag/dns/GET/v1/dns/summary)
- [`DELETE /v1/dns/{zone_name}`](/api-reference#tag/dns/DELETE/v1/dns/{zone_name})
# Manage DNS records
OpusDNS provides two approaches for modifying DNS records within a zone:
**RRset-level** operations that manage entire record sets at once, and
**record-level** operations that target individual records within an RRset.
## Concepts
An **RRset** (Resource Record Set) is a group of DNS records that share the
same name and type. For example, two A records for `example.com.` form a
single RRset.
A **record** is a single entry within an RRset, identified by its `rdata`
value.
## RRset-level operations
Use `PATCH /v1/dns/{zone_name}/rrsets` to add, replace, or remove entire
RRsets. Each operation specifies an `op` (`upsert` or `remove`) and the full
RRset definition.
### Upsert an RRset
Upserting creates the RRset if it does not exist, or replaces it entirely if
it does:
```bash
curl "$OPUSDNS_API_BASE/v1/dns/example.com/rrsets" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"ops": [
{
"op": "upsert",
"rrset": {
"name": "example.com.",
"type": "A",
"ttl": 3600,
"records": [
{ "rdata": "93.184.216.34" },
{ "rdata": "93.184.216.35" }
]
}
}
]
}'
```
### Remove an RRset
Removes the entire RRset (all records of that name and type):
```bash
curl "$OPUSDNS_API_BASE/v1/dns/example.com/rrsets" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"ops": [
{
"op": "remove",
"rrset": {
"name": "staging.example.com.",
"type": "A",
"ttl": 3600,
"records": []
}
}
]
}'
```
### Multiple operations in one request
You can combine multiple upsert and remove operations:
```bash
curl "$OPUSDNS_API_BASE/v1/dns/example.com/rrsets" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"ops": [
{
"op": "upsert",
"rrset": {
"name": "example.com.",
"type": "MX",
"ttl": 3600,
"records": [
{ "rdata": "10 mail.example.com." },
{ "rdata": "20 mail2.example.com." }
]
}
},
{
"op": "remove",
"rrset": {
"name": "old.example.com.",
"type": "CNAME",
"ttl": 3600,
"records": []
}
}
]
}'
```
## Record-level operations
Use `PATCH /v1/dns/{zone_name}/records` to add or remove individual records
without replacing the entire RRset. Each operation targets a single record
identified by name, type, and rdata.
### Add a single record
```bash
curl "$OPUSDNS_API_BASE/v1/dns/example.com/records" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"ops": [
{
"op": "upsert",
"record": {
"name": "example.com.",
"type": "A",
"ttl": 3600,
"rdata": "93.184.216.36"
}
}
]
}'
```
This adds the record to the existing A RRset for `example.com.` without
affecting other records in the set.
### Remove a single record
```bash
curl "$OPUSDNS_API_BASE/v1/dns/example.com/records" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"ops": [
{
"op": "remove",
"record": {
"name": "example.com.",
"type": "A",
"ttl": 3600,
"rdata": "93.184.216.36"
}
}
]
}'
```
## Full zone replacement
Use `PUT /v1/dns/{zone_name}/rrsets` to replace all non-protected RRsets in a
zone at once. This is useful for syncing zone data from an external source.
```bash
curl "$OPUSDNS_API_BASE/v1/dns/example.com/rrsets" \
--request PUT \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"rrsets": [
{
"name": "example.com.",
"type": "A",
"ttl": 3600,
"records": [{ "rdata": "93.184.216.34" }]
},
{
"name": "www.example.com.",
"type": "CNAME",
"ttl": 3600,
"records": [{ "rdata": "example.com." }]
}
]
}'
```
This replaces all modifiable RRsets. Any existing RRsets not included in the request body will be removed. Protected records (SOA, NS) are not affected.
## Common examples
### Add an A record
```json
{
"ops": [{
"op": "upsert",
"record": { "name": "app.example.com.", "type": "A", "ttl": 300, "rdata": "10.0.1.1" }
}]
}
```
### Add MX records
```json
{
"ops": [{
"op": "upsert",
"rrset": {
"name": "example.com.", "type": "MX", "ttl": 3600,
"records": [
{ "rdata": "10 mail.example.com." },
{ "rdata": "20 backup-mail.example.com." }
]
}
}]
}
```
### Add a CNAME record
```json
{
"ops": [{
"op": "upsert",
"record": { "name": "www.example.com.", "type": "CNAME", "ttl": 3600, "rdata": "example.com." }
}]
}
```
### Add a TXT record (SPF)
```json
{
"ops": [{
"op": "upsert",
"record": { "name": "example.com.", "type": "TXT", "ttl": 3600, "rdata": "\"v=spf1 include:_spf.google.com ~all\"" }
}]
}
```
### Add a SRV record
```json
{
"ops": [{
"op": "upsert",
"record": { "name": "_sip._tcp.example.com.", "type": "SRV", "ttl": 3600, "rdata": "10 5 5060 sip.example.com." }
}]
}
```
## Protected records
Certain records are system-managed and cannot be modified:
- **SOA** and **NS** records at the zone apex are managed by OpusDNS.
- Records created by **email forwarding** or **domain forwarding** are
managed through their respective APIs.
NS records **below** the apex are not protected — they delegate a subdomain to
other nameservers and are managed like any other record type. See
[Delegate a subdomain](/products/dns/subzone-delegation).
Attempting to modify a protected record returns an error. See
[the zone object](/products/dns/zone-object#protected-records) for the full
list of protection reasons.
## Choosing an approach
| Scenario | Recommended approach |
| --- | --- |
| Add or remove a single record | Record-level `PATCH .../records` |
| Replace all records of a name+type | RRset-level `PATCH .../rrsets` with `upsert` |
| Sync entire zone from external source | `PUT .../rrsets` (full replacement) |
| Batch multiple changes atomically | RRset-level `PATCH .../rrsets` with multiple ops |
## Related API Reference
- [`PATCH /v1/dns/{zone_name}/records`](/api-reference#tag/dns/PATCH/v1/dns/{zone_name}/records)
- [`PATCH /v1/dns/{zone_name}/rrsets`](/api-reference#tag/dns/PATCH/v1/dns/{zone_name}/rrsets)
- [`PUT /v1/dns/{zone_name}/rrsets`](/api-reference#tag/dns/PUT/v1/dns/{zone_name}/rrsets)
# Delegate a subdomain
Sub-zone delegation hands authority for a subdomain to a different set of
nameservers, while the parent zone stays on OpusDNS. This is done with **NS
records below the zone apex** — for example, delegating `internal.example.com`
to your own infrastructure, or `shop.example.com` to another provider.
Delegation NS RRsets are ordinary records: create them at zone creation or with
any of the [record management endpoints](/products/dns/manage-records), and
remove them the same way. This is different from changing the nameservers of
the **whole domain** — for that, update the
[domain's nameservers](/products/domains/nameservers) instead. NS records *at* the zone apex are
system-managed by OpusDNS and cannot be modified through the zone endpoints.
## Delegate a subdomain
Add an NS RRset at the subdomain you want to delegate:
```bash
curl "$OPUSDNS_API_BASE/v1/dns/example.com/rrsets" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"ops": [
{
"op": "upsert",
"rrset": {
"name": "internal.example.com.",
"type": "NS",
"ttl": 3600,
"records": [
{ "rdata": "ns1.other-provider.net." },
{ "rdata": "ns2.other-provider.net." }
]
}
}
]
}'
```
From that moment, OpusDNS nameservers answer queries for
`internal.example.com` (and every name below it) with a **referral** to
`ns1.other-provider.net.` and `ns2.other-provider.net.` — those nameservers
are now authoritative for the delegated subtree.
You can also include delegation NS RRsets directly in the `rrsets` array when
[creating a zone](/products/dns/manage-zones).
## Remove a delegation
Remove the NS RRset and the parent zone becomes authoritative for the subtree
again:
```bash
curl "$OPUSDNS_API_BASE/v1/dns/example.com/rrsets" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"ops": [
{
"op": "remove",
"rrset": {
"name": "internal.example.com.",
"type": "NS",
"ttl": 3600,
"records": []
}
}
]
}'
```
Individual nameservers can be added or removed one at a time with the
record-level endpoint (`PATCH /v1/dns/{zone_name}/records`), like any other
record type.
## What to know before delegating
- **Records below a delegation point stop resolving publicly.** Once
`internal.example.com` is delegated, any records the parent zone holds at or
below that name — including [domain forwards](/products/dns/domain-forwarding),
[email forwards](/products/dns/email-forwarding), and parking — are no longer
served; the delegated nameservers are authoritative for that subtree. The
records remain stored in the zone and resolve again if the delegation is
removed.
- **Delegations from DNSSEC-signed zones are insecure delegations.** Child DS
records are not supported, so the delegated subtree is not covered by the
parent's chain of trust. The delegation itself works — resolvers simply treat
the subtree as unsigned. DS RRsets in zone payloads are rejected.
- **The delegated nameservers must be set up separately.** OpusDNS publishes
the referral; serving the actual records for the subtree is up to the
nameservers you delegate to.
# DNSSEC for zones
OpusDNS can sign your DNS zones with DNSSEC, providing cryptographic
authentication of DNS responses. Zone-level DNSSEC is managed separately from
the domain-level DNSSEC records published at the registry.
## Two levels of DNSSEC
| Level | What it does | API |
| --- | --- | --- |
| **Zone signing** | Signs DNS responses from OpusDNS nameservers. | `POST /v1/dns/{zone_name}/dnssec/enable` |
| **Registry DS records** | Publishes DS records at the parent zone via the domain registrar. | `PUT /v1/domains/{domain_reference}/dnssec` |
When you use OpusDNS nameservers, enabling zone signing also handles the DS
record publication at the registry automatically. You typically only need to
manage registry DS records manually when using external nameservers.
For managing DS records at the registry level, see
[Managing DNSSEC](/products/domains/dnssec).
## Enable DNSSEC on a zone
```bash
curl "$OPUSDNS_API_BASE/v1/dns/example.com/dnssec/enable" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
This signs the zone and begins serving DNSSEC-authenticated responses. You
can also enable DNSSEC when creating a zone by setting
`"dnssec_status": "enabled"` in the create request.
## Disable DNSSEC on a zone
```bash
curl "$OPUSDNS_API_BASE/v1/dns/example.com/dnssec/disable" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
This removes zone signing. DNS responses will no longer include DNSSEC
signatures.
## Check DNSSEC status
The `dnssec_status` field on the zone object indicates the current signing
status:
```bash
curl "$OPUSDNS_API_BASE/v1/dns/example.com" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
```json
{
"dns_zone_id": "zone_01h45ytscbebyvny4gc8cr8ma2",
"name": "example.com",
"dnssec_status": "enabled",
...
}
```
## Filter zones by DNSSEC status
List all zones with a specific signing status:
```bash
curl --get "$OPUSDNS_API_BASE/v1/dns" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "dnssec_status=enabled"
```
The [zones summary](/products/dns/manage-zones#get-zones-summary) endpoint
also provides a breakdown by DNSSEC status.
## Related API Reference
- [`POST /v1/dns/{zone_name}/dnssec/enable`](/api-reference#tag/dns/POST/v1/dns/{zone_name}/dnssec/enable)
- [`POST /v1/dns/{zone_name}/dnssec/disable`](/api-reference#tag/dns/POST/v1/dns/{zone_name}/dnssec/disable)
- [`GET /v1/domains/{domain_reference}/dnssec`](/api-reference#tag/domain/GET/v1/domains/{domain_reference}/dnssec)
- [`PUT /v1/domains/{domain_reference}/dnssec`](/api-reference#tag/domain/PUT/v1/domains/{domain_reference}/dnssec)
# Vanity nameservers
By default, every DNS zone hosted at OpusDNS answers from the shared OpusDNS nameservers (`ns1.opusdns.com` / `ns2.opusdns.net`). **Vanity nameservers** let you present your zones under nameserver names on your own domain — for example `ns1.example.com` and `ns2.example.com` — so your brand appears in the delegation and `NS` records. OpusDNS still answers the DNS from its anycast network; only the _names_ change.
A group of branded nameservers is a **vanity nameserver set**. A set has:
* a **name** for your own reference;
* a **parent domain** — the domain the nameserver hostnames live under (e.g. `example.com` for `ns1.example.com`);
* two or more **nameserver hostnames** (e.g. `ns1.example.com`, `ns2.example.com`);
* an **SOA responsible name** (`soa_rname`) — the contact stamped into the `SOA` record of every zone the set brands, in DNS format (e.g. `hostmaster.example.com`).
Once a set is **active**, you can point your DNS zones at it: new zones can use it automatically (if it is your organization default), or any zone — new or existing — can be branded with a specific set explicitly.
## How it works: where is the parent domain registered?
How much you have to do yourself depends on **where the parent domain is registered**. The API behaves the same either way; the difference is the setup you are responsible for.
| Parent domain | What OpusDNS does | What you do |
| --------------------------- | ---------------------------------------------------------------------------------------------------------------------------------------------- | ---------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| **Registered with OpusDNS** | Provisions the zone, assigns anycast addresses, and registers the nameserver glue at the registry automatically. The set activates on its own. | Nothing extra — just create the set. |
| **Registered elsewhere** | Assigns anycast addresses and verifies that the nameservers resolve to them. | Publish `A` / `AAAA` records for the nameserver hostnames pointing at the assigned anycast addresses, and register glue at your registrar if needed (see [Glue records](#glue-records)). |
Use the [`/check` diagnostic](#check-the-status-of-a-set) at any time to see exactly which prerequisites are satisfied and which are still outstanding. It returns more detail when OpusDNS manages the parent domain, because we can read the registry directly.
## Create a vanity nameserver set
```bash
curl "$OPUSDNS_API_BASE/v1/vanity-nameserver-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "Example brand nameservers",
"parent_domain_name": "example.com",
"soa_rname": "hostmaster.example.com",
"hostnames": ["ns1.example.com", "ns2.example.com"]
}'
```
A vanity nameserver set carries a fee to **create**, a recurring fee to **renew** annually, and a fee to **restore** during its grace period. See your pricing information for exact figures.
### Request fields
| Field | Type | Required | Description |
| -------------------- | -------- | -------- | ----------------------------------------------------------------------------------------------------- |
| `name` | `string` | Yes | A human-readable label for the set. |
| `parent_domain_name` | `string` | Yes | The apex domain the hostnames live under. Every hostname must be a subdomain of it. |
| `soa_rname` | `string` | Yes | The `SOA` responsible name stamped into branded zones, in DNS format (e.g. `hostmaster.example.com`). |
| `hostnames` | `array` | Yes | Two or more fully-qualified nameserver hostnames, ordered by intended position. |
The call returns **`202 Accepted`** with the created set. The set starts in status `provisioning` and activates asynchronously (see [What to expect after creating](#what-to-expect-after-creating)).
```json
{
"set_id": "vns_01kvn2kr1qep2bd7e60tt65fxn",
"organization_id": "organization_01kvn2kr34e9ts01z1330tkvfx",
"name": "Example brand nameservers",
"parent_domain_name": "example.com",
"soa_rname": "hostmaster.example.com",
"status": "provisioning",
"is_default": false,
"nameservers": [
{ "hostname": "ns1.example.com", "position": 0 },
{ "hostname": "ns2.example.com", "position": 1 }
]
}
```
The nameserver in `position` `0` becomes the primary (`SOA` `MNAME`) for zones branded with the set.
## What to expect after creating
Activation happens **asynchronously** — the `202` response means the request was accepted, not that the set is live. OpusDNS sets up the zone, confirms the nameservers are correctly in place, and only then moves the set to `active`. A set will not activate until its prerequisites actually check out, and what is required depends on where the parent domain is registered:
* **Parent domain managed by OpusDNS** — provisioning and glue registration are automatic and usually complete within a minute or two. Registry steps can take longer to settle and are retried for a period to allow for registry propagation.
* **Parent domain registered elsewhere** — OpusDNS repeatedly checks that the nameserver hostnames resolve to the assigned anycast addresses, for a limited window. Publish your `A` / `AAAA` records before creating the set, or shortly after, so the check succeeds inside that window.
A set has one of the following statuses:
| Status | Meaning |
| -------------- | ----------------------------------------------------------------------------------------------------------- |
| `provisioning` | Being set up; not yet serving as a vanity delegation. |
| `active` | Live and usable to brand zones. |
| `suspended` | Temporarily inactive (see [Lifecycle](#lifecycle-renewal-grace-and-deletion)). Existing zones keep working. |
| `failed` | Activation did not complete in time. |
| `deleting` | Being torn down. |
A `failed` set is **not** permanent. Once the prerequisites are in place — for example, after you finish publishing your records — [retry the set](#retry-a-failed-set) to re-run activation for the same set, with no need to delete it and start over. Use `/check` first to confirm what was missing is now resolved.
## The anycast addresses to publish
If your parent domain is **registered with OpusDNS**, you do not need to publish anything — OpusDNS sets up the nameserver `A` / `AAAA` records and registers the glue at the registry automatically. The rest of this section applies only when your parent domain is registered elsewhere.
If your parent domain is registered elsewhere, point **every** nameserver hostname in the set at OpusDNS's shared anycast pool. Publish all of the following records for **each** hostname (e.g. for both `ns1.example.com` and `ns2.example.com`), and use the same addresses when you register glue at your registrar:
| Type | Value |
| ------ | -------------------- |
| `A` | `192.174.68.145` |
| `A` | `176.97.158.145` |
| `AAAA` | `2001:67c:1bc::145` |
| `AAAA` | `2001:67c:10b8::145` |
So each nameserver hostname resolves to both IPv4 addresses (two `A` records) and both IPv6 addresses (two `AAAA` records).
The [`/check` diagnostic](#check-the-status-of-a-set) reports the exact addresses your set must publish under each check's `observed.required_records`. If that output ever differs from the list above, treat `/check` as authoritative.
## Use a set for your DNS zones
There are three ways to make a zone use a vanity NS set.
### Set it as your organization default
```bash
curl "$OPUSDNS_API_BASE/v1/vanity-nameserver-sets/$SET_ID/default" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
After this, **new** zones created with no explicit set are automatically branded with it.
* When the **first** set in your organization becomes active, it automatically becomes the default.
* With **multiple** active sets, only one is the default at a time; selecting a new default changes which set brands newly created zones, but does not change existing zones.
* Changing the default only affects zones created _after_ the change. Each zone remembers the set it was branded with.
To stop a set from being applied to new zones while leaving existing zones working, make sure it is **not** the default — either choose a different default, or clear the default entirely:
```bash
curl "$OPUSDNS_API_BASE/v1/vanity-nameserver-sets/default" \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
After clearing, new zones fall back to the standard OpusDNS nameservers. Existing zones keep the branding they already have.
### Brand a new zone explicitly
When [creating a zone](/products/dns/manage-zones), include `vanity_nameserver_set_id` with the `set_id`. This works for _any_ active set, default or not:
```bash
curl "$OPUSDNS_API_BASE/v1/dns" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"name": "example.net",
"vanity_nameserver_set_id": "vns_01kvn2kr1qep2bd7e60tt65fxn"
}'
```
### Re-brand or unbrand an existing zone
A pre-existing zone can be re-stamped with a different set — or reset back to the OpusDNS defaults — at any time, without recreating it:
```bash
curl "$OPUSDNS_API_BASE/v1/dns/example.net/vanity-set" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"vanity_nameserver_set_id": "vns_01kvn2kr1qep2bd7e60tt65fxn"
}'
```
Set `vanity_nameserver_set_id` to `null` to unbrand the zone and restamp its apex back to the standard OpusDNS nameservers. This rewrites the zone's apex `NS` records and `SOA` at the DNS provider (and re-signs the zone if DNSSEC is enabled). Afterwards the zone appears in the set's [zones listing](#list-the-zones-using-a-set).
The target set must be `active` and belong to your organization. A suspended set returns `409`, a missing or other-organization set returns `404`. Re-branding requires both DNS-zone and vanity-NS manage permissions.
To re-brand (or unbrand) **many zones at once**, use the bulk jobs API with the `dns_zone_restamp_vanity_ns_bulk` command — see [DNS bulk commands](/automation/jobs/dns-commands).
### List the zones using a set
```bash
curl "$OPUSDNS_API_BASE/v1/vanity-nameserver-sets/$SET_ID/zones" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Returns the zones currently branded with the set (paginated). Useful before deleting a set, since a set in use cannot be deleted.
## Check the status of a set
The `/check` endpoint is a **read-only health report** for a set. It changes nothing — it tells you what is correctly set up, what is missing, and what is optional-but-recommended. It is the quickest way to see why a set has not gone active, or why a customer's vanity nameservers "aren't working."
```bash
curl "$OPUSDNS_API_BASE/v1/vanity-nameserver-sets/check" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"set_id": "vns_01kvn2kr1qep2bd7e60tt65fxn"
}'
```
The response carries an overall `summary` and a list of individual `checks`:
```json
{
"set_id": "vns_01kvn2kr1qep2bd7e60tt65fxn",
"parent_domain_name": "example.com",
"status": "provisioning",
"summary": {
"state": "action_required",
"detail": "Nameserver A/AAAA records are not yet published for ns1.example.com, ns2.example.com."
},
"checks": [
{
"id": "ns_a_records",
"label": "Nameserver A/AAAA records",
"status": "fail",
"severity": "required",
"source": "public_dns",
"confidence": "authoritative",
"detail": "Vanity NS hostnames are not yet resolving to the assigned anycast addresses.",
"observed": {
"required_records": {
"A": ["192.174.68.145", "176.97.158.145"],
"AAAA": ["2001:67c:1bc::145", "2001:67c:10b8::145"]
}
},
"remediation": "Publish A (and AAAA) records for each nameserver hostname pointing at the addresses in required_records."
}
]
}
```
### The overall summary state
| `state` | Meaning | Your action |
| ----------------- | ------------------------------------------------------------------------------------------------------------ | ---------------------------------------------- |
| `ready` | Everything checks out — nameservers resolve and glue is in place. | None. |
| `propagating` | Setup is correct but a change has not fully appeared in DNS yet. | Wait and re-check — no action needed. |
| `action_required` | Something you must do is missing — e.g. nameserver `A` records are not published, or glue is not registered. | Follow the `remediation` on the failing check. |
| `degraded` | Registered values do not match what is visible in DNS (a misconfiguration or stale delegation). | Investigate the mismatch. |
### The individual checks
| Check | What it answers | When present |
| ------------------------------------------ | ------------------------------------------------------------------------------------------------------------------------------------------------ | -------------------------------------------------- |
| `ns_a_records` _(required)_ | Do the nameserver hostnames resolve to the assigned anycast addresses? `observed.required_records` lists the exact addresses you should publish. | Always. |
| `registry_glue_registered` _(recommended)_ | Is the nameserver glue registered at the registry, and to which addresses? Read directly from the registry. | Only when the parent domain is managed by OpusDNS. |
| `registry_glue_visible` _(recommended)_ | Is the glue visible in public DNS yet (at the parent TLD's nameservers)? Reflects propagation. | Always. |
Each check reports a `status` (`pass` / `warn` / `fail` / `info`), a `severity` (`required` / `recommended` / `optional`), the `observed` values, and — when relevant — a `remediation` hint.
A common and **healthy** situation is `registry_glue_registered = pass` with `registry_glue_visible = warn` and an overall state of `propagating`: the glue is registered correctly and DNS just hasn't caught up yet. It clears on its own.
## Retry a failed set
A `failed` set means activation did not complete within its window — usually because the nameserver `A` / `AAAA` records or registry glue were not in place in time. Once you have fixed what was missing, re-run activation for the **same** set instead of recreating it:
```bash
curl "$OPUSDNS_API_BASE/v1/vanity-nameserver-sets/$SET_ID/retry" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
The call returns **`202 Accepted`**; the set returns to `provisioning` and activation runs again, asynchronously, exactly as it did on create. Retry applies only to `failed` sets — calling it on a set in any other status returns `409`.
Run [`/check`](#check-the-status-of-a-set) before retrying to confirm the prerequisites are now satisfied, so the re-run succeeds instead of failing again.
## Glue records
**Glue records** are the IP addresses attached to a nameserver at the registry/TLD level. They are needed when a nameserver lives _under the same domain it serves_ — "in-bailiwick", e.g. using `ns1.example.com` to serve `example.com` itself — because otherwise resolving the nameserver would be circular.
* When the **parent domain is registered with OpusDNS**, glue is registered automatically — you do not need to do anything.
* When the **parent domain is registered elsewhere**, register glue (sometimes called "host records", "child hosts", or "private nameservers") at _your_ registrar, pointing the nameserver hostnames at the anycast addresses from `/check`. If your domain is registered with OpusDNS but managed as a host object, see [Host objects (glue records)](/products/domains/host-objects).
* Glue is **only required for in-bailiwick use**. If you only point _other_ domains at your branded nameservers, glue is not strictly required — which is why the glue checks are advisory, not blocking.
## Lifecycle: renewal, grace, and deletion
A vanity nameserver set is a **subscription that renews annually for a fee**. As long as it renews, it keeps working with no action needed. See your pricing information for the renewal figure.
### If the subscription lapses
If a renewal does not go through, the set enters a **30-day grace period**:
* **At the start of grace**, the set is **suspended** and automatically removed as the organization default, so it stops being applied to _new_ zones. Zones that already use it **keep working normally** throughout grace.
* **Restore it during grace** to return it to normal:
```bash
curl "$OPUSDNS_API_BASE/v1/vanity-nameserver-sets/$SET_ID/restore" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
A restored set comes back `active`, but not automatically as the default — re-select it as the default if you want it to brand new zones again. Restoring incurs a fee; see your pricing information.
* **At the end of grace**, if it has not been restored, OpusDNS automatically restamps every zone still using the set back to the standard OpusDNS nameservers and tears the set down. Those zones are then served by the OpusDNS nameservers again.
### Deleting a set
Delete a set with `DELETE /v1/vanity-nameserver-sets/{set_id}`. The set must first be **out of use** — deletion is refused with `409` while:
* **any zone still references the set** — re-stamp every such zone onto a different set, or back to the OpusDNS defaults ([Re-brand or unbrand a zone](#re-brand-or-unbrand-an-existing-zone)), first; or
* **the set is the organization default and other active sets exist** — choose a different default first. (Deleting your only active set is fine.)
```bash
curl "$OPUSDNS_API_BASE/v1/vanity-nameserver-sets/$SET_ID" \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
When accepted, the call returns `202 Accepted` and the set is torn down asynchronously.
Deleting a set takes down the vanity NS configuration, but does **not** remove nameserver glue / host records registered at the registry. If you no longer want those nameservers to exist at all, remove the glue / host records separately — for an externally-registered domain, at your own registrar.
## API reference
| Method and path | Purpose |
| --------------------------------------------------- | ------------------------------------------------------------------------------------ |
| `POST /v1/vanity-nameserver-sets` | Create a set. Returns `202` plus the set. |
| `GET /v1/vanity-nameserver-sets` | List your organization's sets (paginated). |
| `GET /v1/vanity-nameserver-sets/{set_id}` | Get one set. |
| `POST /v1/vanity-nameserver-sets/check` | Run the read-only diagnostic on a set. |
| `GET /v1/vanity-nameserver-sets/{set_id}/zones` | List the DNS zones branded with the set. |
| `PATCH /v1/vanity-nameserver-sets/{set_id}/default` | Make the set your organization default. |
| `DELETE /v1/vanity-nameserver-sets/default` | Clear the organization default. |
| `POST /v1/vanity-nameserver-sets/{set_id}/restore` | Restore a suspended set during its grace period. |
| `POST /v1/vanity-nameserver-sets/{set_id}/retry` | Re-run activation for a `failed` set. Returns `202`. |
| `DELETE /v1/vanity-nameserver-sets/{set_id}` | Delete a set (must be out of use first). Returns `202`. |
| `PATCH /v1/dns/{zone_name}/vanity-set` | Re-brand an existing zone with a set, or clear it (`null`) back to OpusDNS defaults. |
An organization can have **multiple** active sets at once (for example, different brands), coexisting independently. Only one can be the default at a time.
## Troubleshooting
**"My set has been provisioning for a while, or it went to `failed`."**\
Activation only completes once the prerequisites check out, within a limited window. If your records or glue were not in place in time, the set is marked `failed`. Run `/check` to see what is missing, fix it, then [retry the set](#retry-a-failed-set) to re-run activation — no need to recreate it.
**"I created a set but my domains still show the OpusDNS nameservers."**\
Setting or changing the organization default only brands _new_ zones created after the change. To switch an existing zone, re-stamp it with `PATCH /v1/dns/{zone_name}/vanity-set`.
**"My domain is registered elsewhere — what exactly do I do?"**\
(1) Run `/check` to get the assigned anycast addresses. (2) At your DNS host, publish `A` (and `AAAA`) records for each nameserver hostname pointing at those addresses. (3) At your registrar, register the nameservers as host / glue records if you will use them for the parent domain itself. (4) Re-run `/check` to confirm.
# Domain forwarding
Domain forwarding redirects visitors from one URL to another using HTTP redirects. Common use cases include:
* **Brand consolidation** — redirect `old-brand.com` to `new-brand.com`
* **Non-www to www** — redirect `example.com` to `www.example.com`
* **HTTP to HTTPS** — force secure connections
* **Path redirects** — send `/blog` to a separate blog platform
* **Wildcard redirects** — catch all subdomains with `*.example.com`
OpusDNS automatically manages the DNS records required for forwarding. When you enable a forward, the necessary A/AAAA records are created and marked as protected so they cannot be accidentally modified.
## Prerequisites
A DNS zone for the hostname must exist on OpusDNS and the hostname must resolve through OpusDNS nameservers. See [Manage zones](/products/dns/manage-zones).
## Set up a basic redirect
This example redirects all HTTPS traffic from `example.com` to `www.example.com` with a 301 permanent redirect:
```bash
curl "$OPUSDNS_API_BASE/v1/domain-forwards" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"hostname": "example.com",
"enabled": true,
"https": {
"redirects": [
{
"request_path": "/",
"target_protocol": "https",
"target_hostname": "www.example.com",
"target_path": "/",
"redirect_code": 301
}
]
}
}'
```
Setting `enabled: true` immediately activates the forward and creates the required DNS records. If you omit it (defaults to `false`), the configuration is saved but no DNS records are created until you enable it.
### Redirect rule fields
Each redirect rule maps an incoming request to a target destination:
| Field | Type | Description |
| ----------------- | --------- | ------------------------------------------------ |
| `request_path` | `string` | The incoming path to match (e.g., `/`, `/blog`). |
| `target_protocol` | `string` | Where to redirect: `http` or `https`. |
| `target_hostname` | `string` | Destination hostname. |
| `target_path` | `string` | Destination path. |
| `redirect_code` | `integer` | HTTP status code for the redirect. |
### Choosing a redirect code
| Code | When to use |
| ----- | ------------------------------------------------------------------------------- |
| `301` | Permanent move. Search engines transfer SEO value. Browsers cache aggressively. |
| `302` | Temporary redirect. Use when the original URL will come back. |
| `307` | Temporary redirect that preserves the HTTP method (POST stays POST). |
| `308` | Permanent redirect that preserves the HTTP method. |
For most use cases, `301` is the right choice. Use `302` or `307` for temporary redirects during migrations.
## Common scenarios
### Redirect HTTP to HTTPS
Force all HTTP traffic to use HTTPS. This requires both an HTTP and HTTPS forward set:
```bash
curl "$OPUSDNS_API_BASE/v1/domain-forwards" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"hostname": "example.com",
"enabled": true,
"http": {
"redirects": [
{
"request_path": "/",
"target_protocol": "https",
"target_hostname": "example.com",
"target_path": "/",
"redirect_code": 301
}
]
}
}'
```
### Redirect an old domain to a new one
After a rebrand, redirect the old domain permanently:
```bash
curl "$OPUSDNS_API_BASE/v1/domain-forwards" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"hostname": "old-brand.com",
"enabled": true,
"https": {
"redirects": [
{
"request_path": "/",
"target_protocol": "https",
"target_hostname": "new-brand.com",
"target_path": "/",
"redirect_code": 301
}
]
}
}'
```
### Wildcard subdomain redirect
Catch all subdomains and redirect them to the main domain:
```bash
curl "$OPUSDNS_API_BASE/v1/domain-forwards" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"hostname": "*.example.com",
"enabled": true,
"https": {
"redirects": [
{
"request_path": "/",
"target_protocol": "https",
"target_hostname": "example.com",
"target_path": "/",
"redirect_code": 301
}
]
}
}'
```
## Managing forwards
### Add a path-specific redirect
After the initial setup, you can add redirects for specific paths using the patch endpoint. This adds a `/blog` redirect without affecting existing rules:
```bash
curl "$OPUSDNS_API_BASE/v1/domain-forwards" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"ops": [
{
"op": "upsert",
"redirect": {
"request_protocol": "https",
"request_hostname": "example.com",
"request_path": "/blog",
"target_protocol": "https",
"target_hostname": "blog.example.com",
"target_path": "/",
"redirect_code": 301
}
}
]
}'
```
### Temporarily disable a forward
Disabling removes the DNS records but keeps the configuration intact. This is useful during migrations or debugging:
```bash
curl "$OPUSDNS_API_BASE/v1/domain-forwards/example.com/disable" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Re-enable when ready:
```bash
curl "$OPUSDNS_API_BASE/v1/domain-forwards/example.com/enable" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Remove a forward
Delete the entire forward configuration and its DNS records:
```bash
curl "$OPUSDNS_API_BASE/v1/domain-forwards/example.com" \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Traffic analytics
OpusDNS tracks redirect traffic automatically. See [Metrics & analytics](/products/domain-forwarding/metrics) for a full guide on monitoring traffic by browser, platform, geography, referrer, and more.
## Related API Reference
* [`POST /v1/domain-forwards`](/api-reference#tag/domain_forward/POST/v1/domain-forwards)
* [`GET /v1/domain-forwards`](/api-reference#tag/domain_forward/GET/v1/domain-forwards)
* [`PATCH /v1/domain-forwards`](/api-reference#tag/domain_forward/PATCH/v1/domain-forwards)
* [`GET /v1/domain-forwards/metrics`](/api-reference#tag/domain_forward/GET/v1/domain-forwards/metrics)
# Domain forwarding metrics
OpusDNS tracks every redirect that passes through your domain forwards,
giving you visibility into traffic patterns, visitor demographics, and
redirect performance.
## Overview metrics
Get a high-level summary of all your domain forwards:
```bash
curl "$OPUSDNS_API_BASE/v1/domain-forwards/metrics" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
```json
{
"configured_forwards": 12,
"invoked_forwards": 8,
"total_visits": 45230,
"unique_visits": 31450
}
```
| Field | Description |
| --- | --- |
| `configured_forwards` | Total number of domain forwards set up in your account. |
| `invoked_forwards` | How many forwards actually received traffic. |
| `total_visits` | Total redirect count (includes repeat visitors). |
| `unique_visits` | Unique visitor count (deduplicated). |
## Filtering
All metrics endpoints accept the same filter parameters:
| Parameter | Description |
| --- | --- |
| `hostname` | Filter to a specific source hostname (e.g., `example.com`). |
| `domain` | Filter by domain. |
| `protocol` | Filter by protocol: `http` or `https`. |
| `time_range` | Time window: `1h`, `1d`, `7d`, or `30d`. |
| `exclude_bots` | Set to `true` to exclude bot and unknown traffic. |
Example — last 7 days of HTTPS traffic for a specific domain, excluding bots:
```bash
curl --get "$OPUSDNS_API_BASE/v1/domain-forwards/metrics" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "hostname=example.com" \
--data-urlencode "protocol=https" \
--data-urlencode "time_range=7d" \
--data-urlencode "exclude_bots=true"
```
## Traffic over time
See how redirect traffic changes over time, bucketed by hourly or daily
intervals depending on the time range:
```bash
curl --get "$OPUSDNS_API_BASE/v1/domain-forwards/metrics/time-series" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "time_range=7d"
```
Use this to spot traffic spikes, detect unusual patterns, or verify that a
newly configured forward is receiving traffic.
## Visitor breakdowns
### By browser
See which browsers your visitors use:
```bash
curl --get "$OPUSDNS_API_BASE/v1/domain-forwards/metrics/browser" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "time_range=30d"
```
Returns traffic counts for Chrome, Safari, Firefox, Edge, and others.
### By platform
Understand which operating systems and devices are being used:
```bash
curl --get "$OPUSDNS_API_BASE/v1/domain-forwards/metrics/platform" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "time_range=30d"
```
Returns breakdowns for Windows, macOS, iOS, Android, Linux, and others.
### By geographic location
See where your redirect traffic originates from:
```bash
curl --get "$OPUSDNS_API_BASE/v1/domain-forwards/metrics/geo" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "time_range=30d"
```
Returns visit counts grouped by country code.
### By referrer
Discover where your visitors are coming from:
```bash
curl --get "$OPUSDNS_API_BASE/v1/domain-forwards/metrics/referrer" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "time_range=30d"
```
Useful for understanding which external sites link to your redirected domains.
### By user agent
Get the raw user agent strings for detailed traffic analysis:
```bash
curl --get "$OPUSDNS_API_BASE/v1/domain-forwards/metrics/user-agent" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "time_range=7d" \
--data-urlencode "exclude_bots=true"
```
## Redirect status codes
See the distribution of HTTP redirect codes being served:
```bash
curl --get "$OPUSDNS_API_BASE/v1/domain-forwards/metrics/status-code" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "time_range=30d"
```
This shows how many redirects used 301, 302, 307, or 308 status codes. If
you see unexpected codes, check your forward set configuration.
## Visits grouped by key
Aggregate visit metrics by different dimensions:
```bash
curl --get "$OPUSDNS_API_BASE/v1/domain-forwards/metrics/visits-by-key" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "grouping=domain" \
--data-urlencode "time_range=30d"
```
| Grouping | What it shows |
| --- | --- |
| `url` | Visits per individual redirect URL. |
| `fqdn` | Visits per fully-qualified domain name. |
| `domain` | Visits aggregated by root domain. |
| `forward` | Visits per forward configuration. |
This is useful for identifying which of your domain forwards receives the
most traffic, or which specific redirect URLs are most popular.
## Related API Reference
- [`GET /v1/domain-forwards/metrics`](/api-reference#tag/domain_forward/GET/v1/domain-forwards/metrics)
- [`GET /v1/domain-forwards/metrics/time-series`](/api-reference#tag/domain_forward/GET/v1/domain-forwards/metrics/time-series)
- [`GET /v1/domain-forwards/metrics/browser`](/api-reference#tag/domain_forward/GET/v1/domain-forwards/metrics/browser)
- [`GET /v1/domain-forwards/metrics/geo`](/api-reference#tag/domain_forward/GET/v1/domain-forwards/metrics/geo)
- [`GET /v1/domain-forwards/metrics/visits-by-key`](/api-reference#tag/domain_forward/GET/v1/domain-forwards/metrics/visits-by-key)
# Email forwarding
Email forwarding lets you receive emails at your domain and automatically forward them to existing mailboxes — without running a mail server. Common use cases include:
* **Professional email** — use `info@yourdomain.com` instead of a personal Gmail
* **Team distribution** — forward `support@yourdomain.com` to multiple team members
* **Department routing** — separate aliases for sales, billing, and support
* **Domain parking** — catch emails on domains you own but don't actively host
OpusDNS automatically manages the MX and TXT DNS records needed for email forwarding. These records are marked as protected so they cannot be accidentally modified.
## Prerequisites
A DNS zone for the hostname must exist on OpusDNS and the hostname must resolve through OpusDNS nameservers. See [Manage zones](/products/dns/manage-zones).
## Set up email forwarding
This example creates email forwarding for `example.com` with two aliases: `info@example.com` forwards to a personal mailbox, and `support@example.com` forwards to two team members.
```bash
curl "$OPUSDNS_API_BASE/v1/email-forwards" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"hostname": "example.com",
"enabled": true,
"aliases": [
{
"alias": "info",
"forward_to": ["john@gmail.com"]
},
{
"alias": "support",
"forward_to": ["alice@company.com", "bob@company.com"]
}
]
}'
```
Setting `enabled: true` activates forwarding immediately and creates the required MX records. Emails sent to `info@example.com` will start arriving at `john@gmail.com` as soon as DNS propagates.
### How aliases work
Each alias maps a local address to one or more destination mailboxes:
| Field | Description |
| ------------ | -------------------------------------------------------------------- |
| `alias` | The local part before the `@` (e.g., `info` for `info@example.com`). |
| `forward_to` | One or more email addresses that receive the forwarded mail. |
An alias can forward to multiple addresses — every destination receives a copy of the email.
## Common scenarios
### Add a new alias to an existing forward
After the initial setup, add more aliases as your team grows. You need the email forward ID from the create response:
```bash
curl "$OPUSDNS_API_BASE/v1/email-forwards/email_forward_01h45ytscbebyvny4gc8cr8ma2/aliases" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"alias": "sales",
"forward_to": ["sales-team@company.com"]
}'
```
### Change where an alias forwards to
Update the destination addresses for an existing alias:
```bash
curl "$OPUSDNS_API_BASE/v1/email-forwards/email_forward_01h45ytscbebyvny4gc8cr8ma2/aliases/email_forward_alias_01h45ytscbebyvny4gc8cr8ma2" \
--request PUT \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"forward_to": ["new-hire@company.com", "manager@company.com"]
}'
```
### Remove an alias
```bash
curl "$OPUSDNS_API_BASE/v1/email-forwards/email_forward_01h45ytscbebyvny4gc8cr8ma2/aliases/email_forward_alias_01h45ytscbebyvny4gc8cr8ma2" \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Pause and resume forwarding
Disabling removes the MX records but keeps your alias configuration intact. This is useful if you temporarily need to stop forwarding without losing your setup:
```bash
curl "$OPUSDNS_API_BASE/v1/email-forwards/email_forward_01h45ytscbebyvny4gc8cr8ma2/disable" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Re-enable when ready:
```bash
curl "$OPUSDNS_API_BASE/v1/email-forwards/email_forward_01h45ytscbebyvny4gc8cr8ma2/enable" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Remove email forwarding
Delete the entire configuration and all aliases:
```bash
curl "$OPUSDNS_API_BASE/v1/email-forwards/email_forward_01h45ytscbebyvny4gc8cr8ma2" \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Monitoring delivery
OpusDNS tracks every forwarded email. See [Metrics & logs](/products/email-forwarding/metrics) for a full guide on delivery rates, per-alias breakdowns, troubleshooting bounces, and forwarding logs.
## Related API Reference
* [`POST /v1/email-forwards`](/api-reference#tag/email_forward/POST/v1/email-forwards)
* [`GET /v1/email-forwards`](/api-reference#tag/email_forward/GET/v1/email-forwards)
* [`GET /v1/email-forwards/{email_forward_id}`](/api-reference#tag/email_forward/GET/v1/email-forwards/%7Bemail_forward_id%7D)
* [`GET /v1/email-forwards/{email_forward_id}/metrics`](/api-reference#tag/email_forward/GET/v1/email-forwards/%7Bemail_forward_id%7D/metrics)
# Email forwarding metrics
OpusDNS tracks every email that passes through your forwarding configuration, giving you visibility into delivery success rates, per-alias performance, and detailed forwarding logs for troubleshooting.
## Delivery metrics
Get an overview of delivery performance for an email forward:
```bash
curl "$OPUSDNS_API_BASE/v1/email-forwards/email_forward_01h45ytscbebyvny4gc8cr8ma2/metrics" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
```json
{
"total_logs": 1542,
"alias_count": 3,
"by_status": {
"DELIVERED": 1480,
"QUEUED": 12,
"REFUSED": 8,
"SOFT-BOUNCE": 30,
"HARD-BOUNCE": 12
},
"rates": {
"delivery_rate": 95.98,
"queued_rate": 0.78,
"refused_rate": 0.52,
"bounce_rate": 2.72
},
"by_alias": [
{
"alias": "info",
"total_logs": 820,
"by_status": { "DELIVERED": 805, "SOFT-BOUNCE": 10, "HARD-BOUNCE": 5 }
},
{
"alias": "support",
"total_logs": 612,
"by_status": { "DELIVERED": 590, "QUEUED": 12, "REFUSED": 5, "SOFT-BOUNCE": 5 }
}
],
"filters": {
"domain": "example.com",
"start_time": null,
"end_time": null,
"include_aliases": true
}
}
```
### Response fields
| Field | Description |
| ------------- | ------------------------------------------------------- |
| `total_logs` | Total number of forwarded emails tracked. |
| `alias_count` | Number of aliases configured on this forward. |
| `by_status` | Email counts grouped by delivery status. |
| `rates` | Percentage rates for each delivery outcome. |
| `by_alias` | Per-alias breakdown (only when `include_aliases=true`). |
| `filters` | The filter parameters that were applied. |
### Delivery statuses
| Status | What it means | Action |
| ------------- | ---------------------------------------------- | ------------------------------------------------------- |
| `DELIVERED` | Email reached the destination mailbox. | None needed. |
| `QUEUED` | Email is queued and will be delivered shortly. | Wait — delivery is in progress. |
| `REFUSED` | Destination server rejected the email. | Check if the destination address accepts external mail. |
| `SOFT-BOUNCE` | Temporary failure — delivery will be retried. | Usually resolves on its own. Monitor for patterns. |
| `HARD-BOUNCE` | Permanent failure — the address is invalid. | Update the alias `forward_to` addresses. |
### Filtering by time
Narrow metrics to a specific time window:
```bash
curl --get "$OPUSDNS_API_BASE/v1/email-forwards/email_forward_01h45ytscbebyvny4gc8cr8ma2/metrics" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "start_time=2026-05-01T00:00:00Z" \
--data-urlencode "end_time=2026-05-04T23:59:59Z"
```
## Interpreting your metrics
### Healthy forwarding
A healthy email forwarding setup typically shows:
* **Delivery rate above 95%**
* **Low bounce rate** (under 2%)
* **No hard bounces** — these indicate invalid destination addresses
A high hard-bounce rate means one or more `forward_to` addresses are invalid. Update stale addresses immediately to maintain good email deliverability.
### Common issues
**High hard-bounce rate** — one or more `forward_to` addresses are invalid. Review your aliases and update any stale addresses:
```bash
curl "$OPUSDNS_API_BASE/v1/email-forwards/email_forward_01h45ytscbebyvny4gc8cr8ma2/aliases/email_forward_alias_01h45ytscbebyvny4gc8cr8ma2" \
--request PUT \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{ "forward_to": ["valid-address@company.com"] }'
```
**High refused rate** — the destination mail server is blocking forwarded emails. This can happen if the destination has strict SPF/DMARC policies. Contact your email provider to whitelist forwarded mail.
**Persistent soft-bounces** — the destination server has intermittent issues. If soft-bounces for a specific alias persist over days, the destination address may have become invalid.
## Forwarding logs
For detailed troubleshooting, inspect individual forwarding logs to see exactly what happened with each email:
```bash
curl "$OPUSDNS_API_BASE/v1/archive/email-forward-logs/email_forward_01h45ytscbebyvny4gc8cr8ma2?page=1&page_size=25" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Each log entry contains:
| Field | Description |
| ----------------- | -------------------------------------------------------------- |
| `sender_email` | Who sent the original email. |
| `recipient_email` | The alias address that received it (e.g., `info@example.com`). |
| `forward_email` | Where it was forwarded to. |
| `subject` | The email subject line. |
| `final_status` | Delivery outcome (`DELIVERED`, `REFUSED`, etc.). |
| `events` | Processing events with timestamps and status codes. |
| `created_on` | When the email was received. |
### Filter logs by alias
To see logs for a specific alias only:
```bash
curl "$OPUSDNS_API_BASE/v1/archive/email-forward-logs/aliases/email_forward_alias_01h45ytscbebyvny4gc8cr8ma2?page=1&page_size=25" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
This is useful when one alias has delivery issues while others work fine.
## Related API Reference
* [`GET /v1/email-forwards/{email_forward_id}/metrics`](/api-reference#tag/email_forward/GET/v1/email-forwards/%7Bemail_forward_id%7D/metrics)
* [`GET /v1/archive/email-forward-logs/{email_forward_id}`](/api-reference#tag/archive/GET/v1/archive/email-forward-logs/%7Bemail_forward_id%7D)
* [`GET /v1/archive/email-forward-logs/aliases/{email_forward_alias_id}`](/api-reference#tag/archive/GET/v1/archive/email-forward-logs/aliases/%7Bemail_forward_alias_id%7D)
# Jobs overview
The Jobs API lets you submit large numbers of operations for asynchronous execution. Instead of making thousands of individual API calls, you bundle commands into a **batch**, and OpusDNS processes them reliably in the background.
## Core concepts
### Batches and jobs
A **batch** is a container that holds one or more commands. When you submit a batch, OpusDNS creates individual **jobs** for each command (or each instance in a bulk command). Each job is processed independently and tracked through its own lifecycle.
```plaintext
Batch (up to 50,000 commands)
├── Job 1 → domain_create "example.com" → succeeded
├── Job 2 → domain_create "example.net" → succeeded
├── Job 3 → domain_create "example.org" → failed
└── ...
```
### Single vs. bulk commands
There are two categories of commands:
**Single-resource commands** create one job per command. Each command targets a specific resource:
```json
{
"type": "domain_create",
"payload": {
"name": "example.com",
"contacts": { "registrant": "contact_01h45ytscbebyvny4gc8cr8ma2" },
"renewal_mode": "renew",
"period": { "unit": "y", "value": 1 }
}
}
```
**Bulk commands** use a **template + instances** pattern. The template defines shared settings, and each instance specifies a target resource with optional overrides. Each instance becomes its own job:
```json
{
"type": "domain_create_bulk",
"payload": {
"template": {
"contacts": { "registrant": "contact_01h45ytscbebyvny4gc8cr8ma2" },
"renewal_mode": "renew",
"period": { "unit": "y", "value": 1 }
},
"instances": [
{ "name": "example.com" },
{ "name": "example.net" },
{ "name": "example.org" }
]
}
}
```
This is significantly more efficient than submitting 3 individual `domain_create` commands — shared fields are defined once in the template rather than repeated in every command.
Instance-level overrides completely replace the template's setting for that field — they are not merged. If an instance specifies `contacts`, it replaces the template's contacts entirely.
## Submitting a batch
Create a batch with `POST /v1/jobs`:
```bash
curl "$OPUSDNS_API_BASE/v1/jobs" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "Q1 2026 bulk registration",
"commands": [
{
"type": "domain_create",
"payload": {
"name": "example1.com",
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "renew",
"period": { "unit": "y", "value": 1 }
}
},
{
"type": "domain_create",
"payload": {
"name": "example2.com",
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "renew",
"period": { "unit": "y", "value": 1 }
}
}
]
}'
```
### Batch request fields
| Field | Required | Default | Description |
| ------------ | -------- | ------- | ----------------------------------------------------- |
| `commands` | Yes | — | Array of command objects. Up to **50,000** per batch. |
| `label` | No | `null` | Human-readable label to identify the batch. |
| `paused` | No | `false` | If `true`, jobs are created in a paused state. |
| `not_before` | No | `null` | UTC timestamp — jobs stay `blocked` until this time. |
### Batch response
```json
{
"batch_id": "batch_01h45ytscbebyvny4gc8cr8ma2",
"total_commands": 2,
"jobs_created": 2,
"jobs_duplicated": 0,
"jobs_failed": 0,
"duplicates": [],
"errors": [],
"status_url": "/v1/jobs/batch_01h45ytscbebyvny4gc8cr8ma2"
}
```
| Field | Description |
| ----------------- | ------------------------------------------------------------------- |
| `batch_id` | Unique identifier for the batch. |
| `total_commands` | Total number of commands submitted. |
| `jobs_created` | Number of jobs successfully created. |
| `jobs_duplicated` | Commands skipped due to duplicate idempotency keys. |
| `jobs_failed` | Commands that failed validation at submission time. |
| `duplicates` | Array of duplicate command details (index, existing job/batch IDs). |
| `errors` | Array of command errors (index, error message, error code). |
| `status_url` | URL to poll for batch progress. |
## Job lifecycle
Each job transitions through a defined set of statuses:
```plaintext
blocked → queued → running → succeeded
→ failed
→ dead_letter
↕
paused
↓
canceled
```
| Status | Description |
| ------------- | --------------------------------------------------------------------------------- |
| `blocked` | Waiting for eligibility — either scheduled via `not_before` or awaiting capacity. |
| `queued` | Eligible and waiting for a worker to pick it up. |
| `paused` | Paused by user action. Must be explicitly resumed. |
| `running` | Currently being executed. |
| `succeeded` | Completed successfully. |
| `failed` | Execution failed. Check `error_class` and `error_message` on the job. |
| `canceled` | Canceled before execution started. |
| `dead_letter` | Permanently failed after exhausting all retry attempts. |
The batch has its own status:
| Batch status | Meaning |
| ------------ | -------------------------------------------------------------------------------------- |
| `pending` | At least one job is still in a non-terminal state. |
| `complete` | All jobs have reached a terminal state (succeeded, failed, canceled, or dead\_letter). |
## Scheduling
Use `not_before` to schedule a batch for future execution:
```json
{
"label": "Scheduled renewal update",
"not_before": "2026-06-01T00:00:00Z",
"commands": [...]
}
```
Jobs remain `blocked` until the scheduled time, then move to `queued` for processing. This is useful for maintenance windows, coordinated rollouts, or time-sensitive operations.
## Idempotency
Include an `idempotency_key` on any command to prevent duplicate processing:
```json
{
"type": "domain_create",
"idempotency_key": "reg-example-com-2026-q1",
"payload": {
"name": "example.com",
...
}
}
```
Always use idempotency keys for domain registrations and transfers — accidental duplicates have financial impact.
If a job with the same idempotency key has already been processed, the command is skipped. The batch response reports these in the `duplicates` array:
```json
{
"duplicates": [
{
"index": 0,
"existing_job_id": "job_01h45ytscbebyvny4gc8cr8ma2",
"existing_batch_id": "batch_01h35xrscbebyvny4gc8cr8ma2",
"resource_key": "example.com"
}
]
}
```
This is especially important for domain registrations and transfers where accidental duplicates would have financial impact.
## Limits
| Constraint | Limit |
| -------------------------------------- | ------ |
| Commands per batch | 50,000 |
| Instances per bulk command | 1,000 |
| Operations per DNS bulk patch instance | 100 |
## Available commands
### Single-resource commands
| Command | Description |
| ----------------- | ----------------------------------------------------------------------- |
| `domain_create` | Register a domain. |
| `domain_update` | Update domain settings (contacts, nameservers, statuses, renewal mode). |
| `domain_transfer` | Initiate an inbound domain transfer. |
| `dns_zone_create` | Create a DNS zone with optional records. |
| `dns_zone_update` | Update an existing DNS zone. |
| `contact_create` | Create a contact. |
### Bulk commands
| Command | Description |
| ----------------------------- | ------------------------------------------------- |
| `domain_create_bulk` | Register multiple domains. |
| `domain_update_bulk` | Update multiple domains. |
| `domain_transfer_bulk` | Transfer multiple domains. |
| `dns_zone_create_bulk` | Create multiple DNS zones. |
| `dns_zone_update_bulk` | Replace RRsets and zone attributes across zones. |
| `dns_zone_patch_rrsets_bulk` | Upsert or remove entire RRsets across zones. |
| `dns_zone_patch_records_bulk` | Upsert or remove individual records across zones. |
| `contact_create_bulk` | Create multiple contacts. |
| `parking_create_bulk` | Create parking pages for multiple domains. |
| `parking_enable_bulk` | Enable parking on multiple domains. |
| `parking_disable_bulk` | Disable parking on multiple domains. |
| `parking_delete_bulk` | Delete parking pages for multiple domains. |
See [Domain commands](/automation/jobs/domain-commands) and [DNS & infrastructure commands](/automation/jobs/dns-commands) for full payload details and examples.
## Related API Reference
* [`POST /v1/jobs`](/api-reference#tag/jobs/POST/v1/jobs)
* [`GET /v1/jobs`](/api-reference#tag/jobs/GET/v1/jobs)
* [`GET /v1/jobs/{batch_id}`](/api-reference#tag/jobs/GET/v1/jobs/%7Bbatch_id%7D)
* [`GET /v1/jobs/{batch_id}/jobs`](/api-reference#tag/jobs/GET/v1/jobs/%7Bbatch_id%7D/jobs)
# Domain commands
This page covers the domain-related commands available in the Jobs API: registering, updating, and transferring domains — both individually and in bulk.
## domain\_create
Register a single domain:
```json
{
"type": "domain_create",
"idempotency_key": "reg-example-com-2026",
"payload": {
"name": "example.com",
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2",
"admin": "contact_01h45ytscbebyvny4gc8cr8ma2",
"tech": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"nameservers": ["ns1.opusdns.com", "ns2.opusdns.net"],
"renewal_mode": "renew",
"period": { "unit": "y", "value": 1 },
"create_zone": true
}
}
```
### Payload fields
| Field | Required | Default | Description |
| ------------------------------- | -------- | ------- | --------------------------------------------------------------------------------------------- |
| `name` | Yes | — | Domain name to register. |
| `contacts` | Yes | — | Contact handles or contact IDs for registrant, admin, tech, and billing. |
| `period` | Yes | — | Registration period. `unit` is `"y"` (years), `value` is the number of years. |
| `renewal_mode` | Yes | — | How the domain renews: `renew`, `autoexpire`, `autodelete`, or `renewonce`. |
| `nameservers` | No | `null` | Array of nameserver hostnames. |
| `create_zone` | No | `false` | If `true`, automatically create an OpusDNS DNS zone for this domain. |
| `auth_code` | No | `null` | Authorization code (6–32 characters). Used for specific TLDs that require it at registration. |
| `expected_price` | No | `null` | Expected price. If set and the actual price differs, the registration is rejected. |
| `attributes` | No | `null` | TLD-specific registry attributes (keyed by attribute name). |
| `claims_notice_acceptance_hash` | No | `null` | TMCH claims notice hash (for domains under trademark protection). |
### Contacts
The `contacts` field accepts either contact IDs or inline contact handles:
**Using contact IDs** (recommended for bulk operations):
```json
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2",
"admin": "contact_01h45ytscbebyvny4gc8cr8ma2",
"tech": "contact_01h45ytscbebyvny4gc8cr8ma2"
}
```
**Using inline contact handles** (for one-off registrations):
```json
"contacts": {
"registrant": {
"first_name": "Jane",
"last_name": "Doe",
"email": "jane@example.com",
"phone": "+49.30123456",
"street": "Friedrichstraße 123",
"city": "Berlin",
"postal_code": "10117",
"country": "DE"
}
}
```
## domain\_create\_bulk
Register multiple domains efficiently using the template + instances pattern:
```json
{
"type": "domain_create_bulk",
"payload": {
"template": {
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2",
"admin": "contact_01h45ytscbebyvny4gc8cr8ma2",
"tech": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"nameservers": ["ns1.opusdns.com", "ns2.opusdns.net"],
"renewal_mode": "renew",
"period": { "unit": "y", "value": 1 },
"create_zone": true
},
"instances": [
{ "name": "example.com" },
{ "name": "example.net" },
{ "name": "example.org" },
{ "name": "my-brand.de", "period": { "unit": "y", "value": 2 } }
]
}
}
```
The **template** defines shared defaults — contacts, nameservers, renewal mode, and period apply to every instance. Each **instance** specifies the domain name and can optionally override any template field.
Up to 1,000 instances per bulk command. Instance-level overrides completely replace the template's setting for that field.
## domain\_update
Update settings on a single domain:
```json
{
"type": "domain_update",
"payload": {
"domain_id": "domain_01h45ytscbebyvny4gc8cr8ma2",
"renewal_mode": "autoexpire",
"nameservers": ["ns1.newprovider.com", "ns2.newprovider.com"]
}
}
```
### Payload fields
| Field | Required | Description |
| ---------------- | -------- | --------------------------------------------------------- |
| `domain_id` | Yes | The domain to update (TypeID). |
| `contacts` | No | Updated contact handles or IDs. |
| `nameservers` | No | New nameserver list. |
| `renewal_mode` | No | New renewal mode. |
| `statuses` | No | Set the full list of client statuses (replaces existing). |
| `status_changes` | No | Add or remove specific statuses (relative change). |
| `auth_code` | No | Set a new authorization code. |
### Statuses vs. status\_changes
`statuses` and `status_changes` are mutually exclusive — use one or the other, never both in the same command.
**`statuses`** — replaces the entire status set:
```json
{
"type": "domain_update",
"payload": {
"domain_id": "domain_01h45ytscbebyvny4gc8cr8ma2",
"statuses": ["clientTransferProhibited", "clientDeleteProhibited"]
}
}
```
**`status_changes`** — adds or removes specific statuses without affecting others:
```json
{
"type": "domain_update",
"payload": {
"domain_id": "domain_01h45ytscbebyvny4gc8cr8ma2",
"status_changes": {
"add": ["clientTransferProhibited"],
"remove": ["clientHold"]
}
}
}
```
## domain\_update\_bulk
Update settings across many domains at once. This is particularly powerful with `status_changes` in the template:
### Example: Lock transfers across your portfolio
```json
{
"type": "domain_update_bulk",
"payload": {
"template": {
"status_changes": {
"add": ["clientTransferProhibited"]
}
},
"instances": [
{ "name": "example.com" },
{ "name": "example.net" },
{ "name": "example.org" }
]
}
}
```
### Example: Bulk update with per-domain overrides
If one domain needs different treatment, its instance can override the template:
```json
{
"type": "domain_update_bulk",
"payload": {
"template": {
"status_changes": {
"add": ["clientTransferProhibited"]
}
},
"instances": [
{ "name": "example.com" },
{ "name": "example.net" },
{
"name": "special-case.com",
"status_changes": {
"remove": ["clientHold"]
}
}
]
}
}
```
In this example, `special-case.com` uses its own `status_changes` (removing `clientHold`) instead of the template's (adding `clientTransferProhibited`). An instance-level override **completely replaces** the template's setting for that field.
### Example: Change nameservers in bulk
```json
{
"type": "domain_update_bulk",
"payload": {
"template": {
"nameservers": ["ns1.opusdns.com", "ns2.opusdns.net"]
},
"instances": [
{ "name": "example.com" },
{ "name": "example.net" },
{ "name": "example.org" }
]
}
}
```
### Instance identification
Each instance can identify the target domain by either `name` or `domain_id`, but not both:
```json
{ "name": "example.com" }
// or
{ "domain_id": "domain_01h45ytscbebyvny4gc8cr8ma2" }
```
## domain\_transfer
Initiate an inbound transfer for a single domain:
```json
{
"type": "domain_transfer",
"idempotency_key": "transfer-example-com-2026",
"payload": {
"name": "example.com",
"auth_code": "Xy9!kL2m",
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2",
"admin": "contact_01h45ytscbebyvny4gc8cr8ma2",
"tech": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "renew",
"period": { "unit": "y", "value": 1 },
"create_zone": true
}
}
```
### Payload fields
| Field | Required | Description |
| ---------------- | ----------- | -------------------------------------------------------------------------------------------------------------------------------------------------- |
| `name` | Yes | Domain name to transfer. |
| `auth_code` | Yes | Authorization code from the current registrar (6–32 characters). |
| `contacts` | Conditional | Contact handles or IDs. Required for most TLDs, but optional for TLDs where every supported contact role has a minimum of `0` (e.g. `.ca`, `.ch`). |
| `renewal_mode` | Yes | Renewal mode after transfer. |
| `period` | No | Transfer period. |
| `nameservers` | No | Nameservers to set after transfer completes. |
| `create_zone` | No | If `true`, create a DNS zone automatically. Defaults to `false`. |
| `expected_price` | No | Expected transfer price. Rejects if actual price differs. |
| `attributes` | No | TLD-specific registry attributes. |
## domain\_transfer\_bulk
Transfer multiple domains using the template + instances pattern:
```json
{
"type": "domain_transfer_bulk",
"payload": {
"template": {
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2",
"admin": "contact_01h45ytscbebyvny4gc8cr8ma2",
"tech": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "renew",
"create_zone": true
},
"instances": [
{ "name": "example.com", "auth_code": "Xy9!kL2m" },
{ "name": "example.net", "auth_code": "Ab3$nR7p" },
{ "name": "example.org", "auth_code": "Cd5&hT1q" }
]
}
}
```
Each instance must include its own `auth_code` since authorization codes are unique per domain. Shared settings like contacts, renewal mode, and zone creation go in the template. The `contacts` block can be omitted entirely for TLDs that do not require any contacts on transfer (every supported contact role has a minimum of `0`, e.g. `.ca`, `.ch`).
## Full batch example
Here's a real-world example combining multiple command types in a single batch:
```bash
curl "$OPUSDNS_API_BASE/v1/jobs" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "Portfolio setup - May 2026",
"commands": [
{
"type": "domain_create_bulk",
"idempotency_key": "may-2026-registrations",
"payload": {
"template": {
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "renew",
"period": { "unit": "y", "value": 1 },
"create_zone": true
},
"instances": [
{ "name": "newbrand.com" },
{ "name": "newbrand.net" },
{ "name": "newbrand.de", "period": { "unit": "y", "value": 2 } }
]
}
},
{
"type": "domain_transfer_bulk",
"payload": {
"template": {
"contacts": {
"registrant": "contact_01h45ytscbebyvny4gc8cr8ma2"
},
"renewal_mode": "renew"
},
"instances": [
{ "name": "existing-domain.com", "auth_code": "Xy9!kL2m" },
{ "name": "existing-domain.eu", "auth_code": "Mn4@pQ8w" }
]
}
},
{
"type": "domain_update_bulk",
"payload": {
"template": {
"status_changes": {
"add": ["clientTransferProhibited"]
}
},
"instances": [
{ "name": "protect-this.com" },
{ "name": "protect-that.net" }
]
}
}
]
}'
```
This single batch registers 3 domains, transfers 2 domains, and locks 2 domains — creating 7 jobs total.
## Related pages
* [Jobs overview](/automation/jobs/overview) — concepts, lifecycle, and limits.
* [DNS & infrastructure commands](/automation/jobs/dns-commands) — DNS zone, contact, and parking commands.
* [Managing batches](/automation/jobs/managing-batches) — monitoring, pause/resume, error handling.
# DNS & infrastructure commands
This page covers the DNS zone, contact, and parking commands available in the Jobs API.
## DNS zone commands
### dns\_zone\_create
Create a single DNS zone with optional records:
```json
{
"type": "dns_zone_create",
"payload": {
"name": "example.com",
"dnssec_status": "enabled",
"rrsets": [
{
"name": "@",
"type": "A",
"ttl": 300,
"records": [{ "rdata": "203.0.113.10" }]
},
{
"name": "www",
"type": "CNAME",
"ttl": 300,
"records": [{ "rdata": "example.com." }]
}
]
}
}
```
| Field | Required | Default | Description |
| --------------- | -------- | ---------- | ---------------------------------------------- |
| `name` | Yes | — | Zone name (typically matches the domain name). |
| `dnssec_status` | No | `disabled` | Enable or disable DNSSEC zone signing. |
| `rrsets` | No | `[]` | Initial resource record sets to create. |
### dns\_zone\_update
Update an existing DNS zone. This is a full replacement — whatever RRsets you supply become the zone's RRsets. Records not included are removed:
```json
{
"type": "dns_zone_update",
"payload": {
"name": "example.com",
"dnssec_status": "enabled",
"rrsets": [
{
"name": "@",
"type": "A",
"ttl": 300,
"records": [{ "rdata": "203.0.113.20" }]
}
]
}
}
```
System-managed record types (SOA, DNSKEY, DS) cannot be set via this command.
### dns\_zone\_create\_bulk
Create multiple DNS zones at once:
```json
{
"type": "dns_zone_create_bulk",
"payload": {
"template": {
"dnssec_status": "enabled",
"rrsets": [
{
"name": "@",
"type": "A",
"ttl": 300,
"records": [{ "rdata": "203.0.113.10" }]
}
]
},
"instances": [
{ "name": "example.com" },
{ "name": "example.net" },
{
"name": "example.org",
"rrsets": [
{
"name": "@",
"type": "A",
"ttl": 300,
"records": [{ "rdata": "203.0.113.99" }]
}
]
}
]
}
}
```
The template's RRsets apply to all instances unless overridden. In this example, `example.org` gets its own A record while the other two zones share the template's.
### dns\_zone\_update\_bulk
Replace RRsets and zone attributes across multiple zones. This is the bulk equivalent of `PUT /v1/dns/{zone_name}/rrsets`.
Both `rrsets` and `dnssec_status` are partial-update fields:
| Value | Behavior |
| ------------------------------------ | -------------------------------- |
| Omitted (both template and instance) | Leave unchanged on the zone. |
| `[]` (rrsets only) | Delete all records. |
| `[...]` or a status value | Replace with the provided value. |
An instance with neither `rrsets` nor `dnssec_status` (after template merge) is rejected as a no-op.
#### Example: Set records and enable DNSSEC
```json
{
"type": "dns_zone_update_bulk",
"payload": {
"template": {
"rrsets": [
{
"name": "@",
"type": "A",
"ttl": 300,
"records": [{ "rdata": "203.0.113.10" }]
}
],
"dnssec_status": "enabled"
},
"instances": [
{ "name": "example.com" },
{
"name": "example.net",
"rrsets": [
{
"name": "@",
"type": "A",
"ttl": 300,
"records": [{ "rdata": "203.0.113.20" }]
}
]
}
]
}
}
```
#### Example: Toggle DNSSEC without touching records
Omit `rrsets` everywhere to only change DNSSEC status:
```json
{
"type": "dns_zone_update_bulk",
"payload": {
"template": { "dnssec_status": "enabled" },
"instances": [
{ "name": "example.com" },
{ "name": "example.net" },
{ "name": "example.org" }
]
}
}
```
### dns\_zone\_patch\_rrsets\_bulk
Upsert or remove entire RRsets by `(name, type)` across multiple zones. This is the bulk equivalent of `PATCH /v1/dns/{zone_name}/rrsets`.
Each instance specifies a zone and an array of operations:
* **`upsert`** — create or replace the RRset. Any prior records for that `(name, type)` are discarded.
* **`remove`** — delete the entire RRset.
```json
{
"type": "dns_zone_patch_rrsets_bulk",
"payload": {
"instances": [
{
"zone_name": "example.com",
"ops": [
{
"op": "upsert",
"rrset": {
"name": "www",
"type": "A",
"ttl": 300,
"records": [
{ "rdata": "203.0.113.10" },
{ "rdata": "203.0.113.11" }
]
}
},
{
"op": "remove",
"rrset": {
"name": "old",
"type": "CNAME",
"ttl": 300,
"records": []
}
}
]
}
]
}
}
```
Up to 100 operations per instance for RRset-level patches.
### dns\_zone\_patch\_records\_bulk
Upsert or remove individual `rdata` values within RRsets across multiple zones. This is the bulk equivalent of `PATCH /v1/dns/{zone_name}/records`.
Unlike the RRset-level patch, this operates on **single records** without touching siblings:
* **`upsert`** — add or update one rdata value. Creates the RRset if it doesn't exist. Other records in the RRset are untouched.
* **`remove`** — remove just one rdata value. Other records in the RRset remain.
```json
{
"type": "dns_zone_patch_records_bulk",
"payload": {
"instances": [
{
"zone_name": "example.com",
"ops": [
{
"op": "upsert",
"record": {
"name": "@",
"type": "MX",
"ttl": 300,
"rdata": "5 new-mail.example.com."
}
},
{
"op": "remove",
"record": {
"name": "@",
"type": "MX",
"ttl": 300,
"rdata": "10 old-mail.example.com."
}
}
]
}
]
}
}
```
Note the key difference: RRset patches use `rrset` with a `records[]` array, while record patches use `record` with a single `rdata` string.
Up to 100 operations per instance for record-level patches.
### dns\_zone\_restamp\_vanity\_ns\_bulk
Re-brand multiple zones onto a [vanity nameserver set](/products/dns/vanity-nameservers), or reset them to the standard OpusDNS nameservers. This is the bulk equivalent of `PATCH /v1/dns/{zone_name}/vanity-set`: each zone's apex `NS` and `SOA` are rewritten to the set's nameservers (and the zone is re-signed if DNSSEC is enabled).
The template's `vanity_nameserver_set_id` applies to every zone; an instance may override it, including `null` to unbrand just that zone:
| Value | Behavior |
| ---------- | ---------------------------------------------------------------------- |
| A `set_id` | Brand the zone with that vanity nameserver set. |
| `null` | Unbrand the zone — reset its apex to the standard OpusDNS nameservers. |
```json
{
"type": "dns_zone_restamp_vanity_ns_bulk",
"payload": {
"template": { "vanity_nameserver_set_id": "vns_01kvn2kr1qep2bd7e60tt65fxn" },
"instances": [
{ "name": "example.com" },
{ "name": "example.net" },
{ "name": "example.org", "vanity_nameserver_set_id": null }
]
}
}
```
The target set must be `active` and belong to your organization. For a single zone, use the `PATCH /v1/dns/{zone_name}/vanity-set` endpoint instead.
### Choosing the right DNS command
| Command | Operates on | Use when |
| --------------------------------- | ------------------------------ | ----------------------------------------------------------------------------- |
| `dns_zone_update_bulk` | Whole zone | Resetting all RRsets or toggling DNSSEC across zones. |
| `dns_zone_patch_rrsets_bulk` | Whole RRsets by `(name, type)` | Replacing all records of a given type at a given name. |
| `dns_zone_patch_records_bulk` | Individual rdata values | Adding or removing a single record without touching siblings. |
| `dns_zone_restamp_vanity_ns_bulk` | Apex `NS` / `SOA` branding | Pointing many zones at a vanity nameserver set (or back to OpusDNS defaults). |
**Example scenario:** You're migrating mail to a new provider across 200 domains.
* Use `dns_zone_patch_records_bulk` if you need to add the new MX record while keeping the old one temporarily.
* Use `dns_zone_patch_rrsets_bulk` if you want to replace all MX records at once.
* Use `dns_zone_update_bulk` if you're rebuilding the entire zone from scratch.
## Contact commands
### contact\_create
Create a single contact:
```json
{
"type": "contact_create",
"payload": {
"first_name": "Jane",
"last_name": "Doe",
"email": "jane@example.com",
"phone": "+49.30123456",
"street": "Friedrichstraße 123",
"city": "Berlin",
"postal_code": "10117",
"country": "DE",
"disclose": true
}
}
```
### Contact payload fields
| Field | Required | Description |
| ------------- | -------- | ------------------------------------------------ |
| `first_name` | Yes | First name. |
| `last_name` | Yes | Last name. |
| `email` | Yes | Email address. |
| `phone` | Yes | Phone number (E.164 format). |
| `street` | Yes | Street address. |
| `city` | Yes | City. |
| `postal_code` | Yes | Postal/ZIP code. |
| `country` | Yes | Two-letter country code (ISO 3166-1 alpha-2). |
| `disclose` | Yes | Whether contact information is publicly visible. |
| `org` | No | Organization name. |
| `title` | No | Title (e.g., "Dr.", "Prof."). |
| `state` | No | State or province. |
| `fax` | No | Fax number (E.164 format). |
### contact\_create\_bulk
Create multiple contacts using the template + instances pattern:
```json
{
"type": "contact_create_bulk",
"payload": {
"template": {
"country": "DE",
"city": "Berlin",
"postal_code": "10117",
"street": "Friedrichstraße 123",
"disclose": true
},
"instances": [
{
"first_name": "Jane",
"last_name": "Doe",
"email": "jane@example.com",
"phone": "+49.30123456"
},
{
"first_name": "John",
"last_name": "Smith",
"email": "john@example.com",
"phone": "+49.30654321"
}
]
}
}
```
Shared address fields go in the template. Per-contact fields (name, email, phone) go in each instance.
## Parking commands
Parking commands manage placeholder pages for domains that aren't actively used. All parking commands are bulk-only.
### parking\_create\_bulk
Create parking pages for multiple domains:
```json
{
"type": "parking_create_bulk",
"payload": {
"instances": [
{ "name": "parked-domain.com" },
{ "name": "another-parked.net" }
]
}
}
```
### parking\_enable\_bulk / parking\_disable\_bulk
Enable or disable parking on multiple domains:
```json
{
"type": "parking_enable_bulk",
"payload": {
"instances": [
{ "name": "parked-domain.com" },
{ "name": "another-parked.net" }
]
}
}
```
```json
{
"type": "parking_disable_bulk",
"payload": {
"instances": [
{ "name": "parked-domain.com" }
]
}
}
```
### parking\_delete\_bulk
Delete parking pages:
```json
{
"type": "parking_delete_bulk",
"payload": {
"instances": [
{ "name": "parked-domain.com" }
]
}
}
```
## Related pages
* [Jobs overview](/automation/jobs/overview) — concepts, lifecycle, and limits.
* [Domain commands](/automation/jobs/domain-commands) — domain registration, update, and transfer commands.
* [Managing batches](/automation/jobs/managing-batches) — monitoring, pause/resume, error handling.
# Managing batches
Once you've submitted a batch, you can monitor its progress, control
execution flow, handle errors, and inspect individual job results.
## Monitoring progress
### Batch status
Poll the batch endpoint to check overall progress:
```bash
curl "$OPUSDNS_API_BASE/v1/jobs/batch_01h45ytscbebyvny4gc8cr8ma2" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
```json
{
"batch_id": "batch_01h45ytscbebyvny4gc8cr8ma2",
"label": "Q1 2026 bulk registration",
"status": "pending",
"total_jobs": 150,
"job_counts": {
"blocked": 0,
"queued": 12,
"paused": 0,
"running": 3,
"succeeded": 130,
"failed": 4,
"canceled": 0,
"dead_letter": 1
},
"progress_percentage": 90.0,
"created_on": "2026-05-04T12:00:00Z",
"started_at": "2026-05-04T12:00:01Z",
"finished_at": null
}
```
The `progress_percentage` reflects how many jobs have reached a terminal
state (succeeded, failed, canceled, or dead_letter) out of the total.
When all jobs are done, `status` changes from `pending` to `complete`.
### Individual job results
List the jobs within a batch:
```bash
curl "$OPUSDNS_API_BASE/v1/jobs/batch_01h45ytscbebyvny4gc8cr8ma2/jobs?page=1&page_size=50" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Each job response includes:
| Field | Description |
| --- | --- |
| `job_id` | Unique identifier for this job. |
| `status` | Current status (`queued`, `running`, `succeeded`, `failed`, etc.). |
| `command` | The command type that was executed. |
| `operation` | The operation being performed. |
| `domain_name` | The domain this job operates on (when applicable). |
| `resource_key` | The primary resource identifier. |
| `display` | Human-readable description of the job. |
| `attempts` | Number of execution attempts. |
| `error_class` | Error category (on failure). |
| `error_message` | Human-readable error detail (on failure). |
| `payload` | The command payload that was submitted. |
| `created_on` | When the job was created. |
| `started_at` | When execution began. |
| `finished_at` | When execution completed. |
| `paused_at` | When the job was paused (if applicable). |
### Filtering jobs by status
Use the `status` parameter (repeatable) to find specific jobs:
```bash
# Find all failed jobs
curl --get "$OPUSDNS_API_BASE/v1/jobs/batch_01h45ytscbebyvny4gc8cr8ma2/jobs" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "status=failed" \
--data-urlencode "status=dead_letter"
```
```bash
# Find jobs still running
curl --get "$OPUSDNS_API_BASE/v1/jobs/batch_01h45ytscbebyvny4gc8cr8ma2/jobs" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "status=running"
```
### Sorting jobs
Control the order of results:
```bash
curl --get "$OPUSDNS_API_BASE/v1/jobs/batch_01h45ytscbebyvny4gc8cr8ma2/jobs" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "sort_by=finished_at" \
--data-urlencode "sort_order=desc"
```
| Parameter | Values | Default |
| --- | --- | --- |
| `sort_by` | `created_on`, `started_at`, `finished_at` | `created_on` |
| `sort_order` | `asc`, `desc` | `desc` |
| `page` | 1+ | 1 |
| `page_size` | 1–1000 | 10 |
## Listing batches
View all batches for your organization:
```bash
curl "$OPUSDNS_API_BASE/v1/jobs?page=1&page_size=25" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Each batch in the list includes metadata:
```json
{
"batch_id": "batch_01h45ytscbebyvny4gc8cr8ma2",
"label": "Q1 2026 bulk registration",
"status": "complete",
"total_jobs": 150,
"job_counts": {
"succeeded": 145,
"failed": 4,
"dead_letter": 1,
"canceled": 0,
"blocked": 0,
"queued": 0,
"paused": 0,
"running": 0
},
"created_on": "2026-05-04T12:00:00Z",
"started_at": "2026-05-04T12:00:01Z",
"finished_at": "2026-05-04T12:15:30Z"
}
```
### Filtering and sorting batches
```bash
# Only pending batches, newest first
curl --get "$OPUSDNS_API_BASE/v1/jobs" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "status=pending" \
--data-urlencode "sort_by=created_on" \
--data-urlencode "sort_order=desc"
```
| Parameter | Values | Default |
| --- | --- | --- |
| `status` | `pending`, `complete` | all |
| `sort_by` | `created_on`, `started_at`, `finished_at` | `created_on` |
| `sort_order` | `asc`, `desc` | `desc` |
## Controlling execution
### Pause a batch
Temporarily stop processing. Queued jobs are held, and no new jobs start.
Jobs that are already `running` will complete:
```bash
curl "$OPUSDNS_API_BASE/v1/jobs/batch_01h45ytscbebyvny4gc8cr8ma2/pause" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Returns `204 No Content` on success.
### Resume a batch
Resume processing of paused jobs:
```bash
curl "$OPUSDNS_API_BASE/v1/jobs/batch_01h45ytscbebyvny4gc8cr8ma2/resume" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Cancel a batch
Cancel all pending jobs in a batch. Completed and currently running jobs are
not affected:
```bash
curl "$OPUSDNS_API_BASE/v1/jobs/batch_01h45ytscbebyvny4gc8cr8ma2" \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Returns `204 No Content` on success.
### Retry failed jobs
Jobs that ended in `failed` or `dead_letter` state can be retried without
rebuilding the batch. Two endpoints support this — one for individual jobs and
one for an entire batch.
#### Retry a single job
```bash
curl "$OPUSDNS_API_BASE/v1/job/job_01h45ytscbebyvny4gc8cr8ma2/retry" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Returns the updated job. Status resets to `queued`, `attempts` resets to `0`,
and `error_class` / `error_message` are cleared. Only `failed` and
`dead_letter` jobs can be retried; jobs in any other status return
`409 Conflict`.
#### Retry an entire batch
```bash
curl "$OPUSDNS_API_BASE/v1/jobs/batch_01h45ytscbebyvny4gc8cr8ma2/retry" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
```json
{
"batch_id": "batch_01h45ytscbebyvny4gc8cr8ma2",
"retried_count": 5
}
```
All `failed` and `dead_letter` jobs in the batch are re-queued in a single
operation. Jobs in any other state (succeeded, canceled, running, etc.) are
left untouched. The response reports how many jobs were retried.
#### Filtering retries by error type
A batch may contain a mix of failures — some recoverable (such as
`BillingInsufficientFundsError` after an account top-up) and some not (such
as `DomainRegistryPolicyError` from a name the registry rejected). Pass one
or more `error_class` query parameters to retry only matching jobs:
```bash
# Retry only insufficient-funds failures
curl --get "$OPUSDNS_API_BASE/v1/jobs/batch_01h45ytscbebyvny4gc8cr8ma2/retry" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "error_class=BillingInsufficientFundsError"
```
```bash
# Retry insufficient-funds and transient registry errors together
curl --get "$OPUSDNS_API_BASE/v1/jobs/batch_01h45ytscbebyvny4gc8cr8ma2/retry" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "error_class=BillingInsufficientFundsError" \
--data-urlencode "error_class=DomainRegistryTemporaryError"
```
Multiple `error_class` values are OR'd — a job is retried if its `error_class`
matches **any** of the supplied values. Omitting the filter retries all
`failed` and `dead_letter` jobs in the batch.
The `error_class` for each failed job is visible on the individual job
response, so a typical flow is:
1. List the failed jobs in the batch and group by `error_class`.
2. Determine which failures are recoverable.
3. Call retry with the relevant `error_class` filter.
### Starting paused
For large or critical batches, create them paused so you can review all jobs before committing to execution.
Create a batch in a paused state for review before execution:
```bash
curl "$OPUSDNS_API_BASE/v1/jobs" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "Review before running",
"paused": true,
"commands": [...]
}'
```
Inspect the batch and its jobs, then resume when ready:
```bash
# Review the jobs
curl "$OPUSDNS_API_BASE/v1/jobs/batch_01h45ytscbebyvny4gc8cr8ma2/jobs?page_size=100" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
# Everything looks good — resume
curl "$OPUSDNS_API_BASE/v1/jobs/batch_01h45ytscbebyvny4gc8cr8ma2/resume" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Error handling
### Submission errors
Errors caught at submission time appear in the batch response:
```json
{
"batch_id": "batch_01h45ytscbebyvny4gc8cr8ma2",
"total_commands": 3,
"jobs_created": 2,
"jobs_failed": 1,
"errors": [
{
"index": 2,
"error": "Invalid domain name format",
"code": "INVALID_DOMAIN_NAME",
"type": "validation-error",
"resource_key": "not-a-valid-domain",
"instance_index": null
}
]
}
```
| Error field | Description |
| --- | --- |
| `index` | Position of the command in the `commands` array (0-based). |
| `instance_index` | For bulk commands, the position within `instances` (0-based). `null` for single commands. |
| `error` | Human-readable error message. |
| `code` | Stable error code for programmatic handling. |
| `type` | RFC 9457 problem type identifier. |
| `resource_key` | The resource that caused the error (e.g., domain name). |
### Batch-level errors
| Error | HTTP status | Description |
| --- | --- | --- |
| `ERROR_BATCH_EMPTY` | 400 | The `commands` array is empty. |
| `ERROR_BATCH_JOB_CREATION_FAILED` | 503 | Internal error creating jobs. Retry the request. |
| `ERROR_BATCH_NOT_FOUND` | 404 | The batch ID does not exist. |
| `ERROR_BATCH_STATUS_FETCH_FAILED` | 503 | Temporary error fetching batch status. Retry. |
### Runtime job failures
Jobs that fail during execution have `error_class` and `error_message`
fields:
```json
{
"job_id": "job_01h45ytscbebyvny4gc8cr8ma2",
"status": "failed",
"command": "domain_create",
"domain_name": "taken-domain.com",
"error_class": "DomainUnavailable",
"error_message": "Domain taken-domain.com is not available for registration",
"attempts": 1,
"finished_at": "2026-05-04T12:01:15Z"
}
```
### Dead letter jobs
A job moves to `dead_letter` when it has exhausted all retry attempts. This
typically indicates a persistent issue:
```bash
# Find dead letter jobs
curl --get "$OPUSDNS_API_BASE/v1/jobs/batch_01h45ytscbebyvny4gc8cr8ma2/jobs" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "status=dead_letter"
```
Dead letter jobs require manual investigation. Check the `error_class` and
`error_message` to understand what went wrong.
For recoverable failures (such as insufficient funds at the time of the
original attempts), use the [retry endpoints](#retry-failed-jobs) to re-queue
the affected jobs once the underlying issue is resolved. For failures that
won't resolve with another attempt (invalid names, registry policy
rejections, and similar), submit a new batch with corrected resources.
Dead letter jobs are not retried automatically. They must be retried explicitly via the retry endpoints once the underlying issue is resolved, or replaced in a new batch.
### Handling duplicates
When commands have `idempotency_key` values that match previously processed
jobs, they appear in the `duplicates` array:
```json
{
"duplicates": [
{
"index": 0,
"existing_job_id": "job_01h45ytscbebyvny4gc8cr8ma2",
"existing_batch_id": "batch_01h35xrscbebyvny4gc8cr8ma2",
"resource_key": "example.com",
"instance_index": null
}
],
"jobs_duplicated": 1
}
```
Duplicates are not errors — they're an intentional safeguard. Use the
`existing_job_id` and `existing_batch_id` to look up the original job's
result.
## Best practices
### Use labels consistently
Labels make it easy to identify batches when reviewing history:
```json
{
"label": "Customer migration - ACME Corp - May 2026",
"commands": [...]
}
```
### Use idempotency keys for critical operations
Always include idempotency keys for domain registrations and transfers where
accidental duplicates would have financial impact:
```json
{
"type": "domain_create",
"idempotency_key": "reg-example-com-2026-q1",
"payload": { ... }
}
```
### Use bulk commands for efficiency
A single `domain_create_bulk` with 500 instances is more efficient than 500
individual `domain_create` commands. Shared fields are validated once rather
than 500 times.
### Start large batches paused
For batches with hundreds or thousands of commands, create them paused so you
can review before committing:
```json
{
"paused": true,
"label": "Large migration - review first",
"commands": [...]
}
```
### Schedule for off-peak hours
Use `not_before` for large batches that don't need to run immediately:
```json
{
"not_before": "2026-06-01T02:00:00Z",
"label": "Scheduled maintenance - off-peak",
"commands": [...]
}
```
### Monitor and react to failures
Build a workflow that polls for completion and handles failures:
1. Submit the batch and store the `batch_id`.
2. Poll `GET /v1/jobs/{batch_id}` until `status` is `complete`.
3. Check `job_counts.failed` and `job_counts.dead_letter`.
4. If either is non-zero, list failed jobs and group by `error_class`.
5. For recoverable failures (e.g. `BillingInsufficientFundsError`), call
`POST /v1/jobs/{batch_id}/retry` — optionally with an `error_class` filter —
to re-queue just the affected jobs. For failures that won't resolve with
another attempt, build a new batch with corrected items.
## Related API Reference
- [`POST /v1/jobs`](/api-reference#tag/jobs/POST/v1/jobs)
- [`GET /v1/jobs`](/api-reference#tag/jobs/GET/v1/jobs)
- [`GET /v1/jobs/{batch_id}`](/api-reference#tag/jobs/GET/v1/jobs/{batch_id})
- [`DELETE /v1/jobs/{batch_id}`](/api-reference#tag/jobs/DELETE/v1/jobs/{batch_id})
- [`GET /v1/jobs/{batch_id}/jobs`](/api-reference#tag/jobs/GET/v1/jobs/{batch_id}/jobs)
- [`POST /v1/jobs/{batch_id}/pause`](/api-reference#tag/jobs/POST/v1/jobs/{batch_id}/pause)
- [`POST /v1/jobs/{batch_id}/resume`](/api-reference#tag/jobs/POST/v1/jobs/{batch_id}/resume)
- [`POST /v1/jobs/{batch_id}/retry`](/api-reference#tag/jobs/POST/v1/jobs/{batch_id}/retry)
- [`POST /v1/job/{job_id}/retry`](/api-reference#tag/jobs/POST/v1/job/{job_id}/retry)
# Events overview
The OpusDNS API uses a polling-based event system to notify you about changes
to your domains, contacts, and other resources. Events are created automatically
when operations complete, fail, or require your attention.
## How events work
1. Operations like domain registrations, transfers, or renewals generate events.
2. You poll `GET /v1/events` to retrieve pending events.
3. After processing an event, you acknowledge it with `PATCH /v1/events/{event_id}`.
4. Acknowledged events are no longer returned in pending queries.
## List events
Retrieve events for your organization:
```bash
curl "$OPUSDNS_API_BASE/v1/events?page=1&page_size=25" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Filter options
| Parameter | Description |
| --- | --- |
| `object_type` | Filter by resource type: `DOMAIN`, `CONTACT`, `HOST` |
| `object_id` | Filter by specific resource ID |
| `type` | Filter by event type (see [the event object](/products/events/event-object)) |
| `subtype` | Filter by subtype: `NOTIFICATION`, `SUCCESS`, `FAILURE`, `CANCELED` |
| `acknowledged` | Filter by acknowledgment status: `true` or `false` |
| `sort_by` | Sort field |
| `sort_order` | Sort direction: `asc` or `desc` |
Example — list only failed domain events:
```bash
curl --get "$OPUSDNS_API_BASE/v1/events" \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--data-urlencode "object_type=DOMAIN" \
--data-urlencode "subtype=FAILURE" \
--data-urlencode "acknowledged=false"
```
## Get a single event
Retrieve the full details of an event:
```bash
curl "$OPUSDNS_API_BASE/v1/events/event_01h45ytscbebyvny4gc8cr8ma2" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Acknowledge an event
Mark an event as processed:
```bash
curl "$OPUSDNS_API_BASE/v1/events/event_01h45ytscbebyvny4gc8cr8ma2" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Once acknowledged, the event's `acknowledged_on` timestamp is set and it is
excluded from default pending queries.
## Polling strategy
Events use a polling model — there are no webhooks. Poll regularly and acknowledge events promptly to keep your pending queue clean.
Since the event system is poll-based, consider these best practices:
1. **Poll regularly** — check for new events on a schedule (e.g., every 30
seconds to 5 minutes, depending on your needs).
2. **Filter by acknowledgment** — use `acknowledged=false` to only retrieve
events you have not yet processed.
3. **Acknowledge promptly** — mark events as acknowledged after processing to
keep your pending queue clean.
4. **Use pagination** — for high-volume accounts, page through results to
avoid missing events.
## Related API Reference
- [`GET /v1/events`](/api-reference#tag/event/GET/v1/events)
- [`GET /v1/events/{event_id}`](/api-reference#tag/event/GET/v1/events/{event_id})
- [`PATCH /v1/events/{event_id}`](/api-reference#tag/event/PATCH/v1/events/{event_id})
# The event object
The event object represents a notification about an operation that occurred on
a resource in your OpusDNS account. Events are returned by `GET /v1/events` and
`GET /v1/events/{event_id}`.
## Example response
```json
{
"event_id": "event_01h45ytscbebyvny4gc8cr8ma2",
"object_id": "dom_01h45ytscbebyvny4gc8cr8ma2",
"object_type": "DOMAIN",
"type": "REGISTRATION",
"subtype": "SUCCESS",
"event_data": {
"version": "1.0",
"message": "Domain example.com registered successfully"
},
"created_on": "2026-01-15T10:30:00Z",
"acknowledged_on": null
}
```
## Fields
| Field | Type | Description |
| --- | --- | --- |
| `event_id` | `string` | Unique identifier for the event (TypeID format, prefixed with `event_`). |
| `object_id` | `string \| null` | The ID of the resource this event relates to (e.g., a domain ID or contact ID). |
| `object_type` | `string` | The type of resource. See [Object types](#object-types). |
| `type` | `string \| null` | The category of operation. See [Event types](#event-types). |
| `subtype` | `string \| null` | The outcome of the operation. See [Subtypes](#subtypes). |
| `event_data` | `object` | Structured payload with event details. See [Event data](#event-data). |
| `created_on` | `datetime` | When the event was created. |
| `acknowledged_on` | `datetime \| null` | When the event was acknowledged. `null` if not yet acknowledged. |
## Object types
The `object_type` field indicates which kind of resource the event relates to.
| Object type | Description |
| --- | --- |
| `DOMAIN` | A domain in your account. |
| `CONTACT` | A contact record. |
| `HOST` | A subordinate host (glue record). |
| `RAW` | A raw registry event not mapped to a specific resource type. |
| `UNKNOWN` | The object type could not be determined. |
## Event types
The `type` field indicates which operation triggered the event.
| Type | Description |
| --- | --- |
| `REGISTRATION` | A domain was registered. |
| `RENEWAL` | A domain was renewed. |
| `MODIFICATION` | A domain or contact was modified. |
| `DELETION` | A domain was deleted. |
| `INBOUND_TRANSFER` | A domain was transferred into OpusDNS. |
| `OUTBOUND_TRANSFER` | A domain was transferred away from OpusDNS. |
| `TRANSIT` | A domain entered transit state (TLD-specific, e.g., `.de`). |
| `WITHDRAW` | A domain was withdrawn from the registry (TLD-specific, e.g., `.at`). |
| `VERIFICATION` | A contact or domain verification event. |
## Subtypes
The `subtype` field indicates the outcome or stage of the operation.
| Subtype | Description |
| --- | --- |
| `NOTIFICATION` | Informational — an operation started or needs your attention. |
| `SUCCESS` | The operation completed successfully. |
| `FAILURE` | The operation failed. |
| `CANCELED` | The operation was canceled. |
## Event data
The `event_data` object uses a standardized V1 structure. Every event includes
a `version` and a `message`. Failure events also include an `error` object, and
some events carry additional typed data in a `details` object.
| Field | Required | Description |
|-----------|----------|--------------------------------------------------------------------------|
| `version` | Yes | Payload format version. Always `"1.0"`. |
| `message` | Yes | Human-readable summary of the event. |
| `error` | No | Structured failure information. Present only for failure events. |
| `details` | No | Typed event-specific data, such as renewal or verification details. |
### Successful event
```json
{
"event_id": "event_01h45ytscbebyvny4gc8cr8ma2",
"object_id": "example.com",
"object_type": "DOMAIN",
"type": "INBOUND_TRANSFER",
"subtype": "SUCCESS",
"event_data": {
"version": "1.0",
"message": "Domain transferred in successfully"
},
"created_on": "2026-05-05T10:30:00Z",
"acknowledged_on": null
}
```
### Failure event
Failure events include `event_data.error.code` and
`event_data.error.detail`. Registry error codes are preserved when available.
```json
{
"event_id": "event_01h45ytscbebyvny4gc8cr8ma2",
"object_id": "example.com",
"object_type": "DOMAIN",
"type": "OUTBOUND_TRANSFER",
"subtype": "FAILURE",
"event_data": {
"version": "1.0",
"message": "Outbound domain transfer failed",
"error": {
"code": "ERROR_DOMAIN_TRANSFER",
"detail": "Outbound transfer failed for example.com"
}
},
"created_on": "2026-05-05T10:30:00Z",
"acknowledged_on": null
}
```
| Error field | Type | Description |
|-------------|----------|--------------------------------------------|
| `code` | `string` | Machine-readable error code. |
| `detail` | `string` | Human-readable explanation of the failure. |
### Renewal details
When a domain renewal succeeds, the event includes the new registration
expiration date under `event_data.details`.
```json
{
"event_data": {
"version": "1.0",
"message": "Domain renewed successfully",
"details": {
"detail_type": "domain_renewal",
"expires_on": "2027-01-01T00:00:00Z"
}
}
}
```
| Details field | Type | Description |
|---------------|------------|---------------------------------------------------------|
| `detail_type` | `string` | Always `domain_renewal` for renewal details. |
| `expires_on` | `datetime` | The new registration expiration date after the renewal. |
### Verification details
When a domain needs verification, the event may include deadlines, required
verification claims, and registrant contact information.
```json
{
"event_data": {
"version": "1.0",
"message": "Domain verification notification received",
"details": {
"detail_type": "domain_verification",
"domain_id": "domain_01h455e1yewzjmrqt7xk5g8w4d",
"verification_deadlines": [
{
"type": "dedelegation",
"date": "2026-05-20T13:01:05+02:00"
},
{
"type": "deletion",
"date": "2026-08-18T13:01:05+02:00"
}
],
"verification_claims": [
"address",
"name"
],
"registrants": [
{
"contact_id": "contact_01h455e1yewzjmrqt7xk5g8w6f",
"name": "Jane Doe",
"email": "jane.doe@example.com"
}
]
}
}
}
```
| Details field | Type | Description |
|--------------------------|----------|--------------------------------------------------------------------------------------------|
| `detail_type` | `string` | Always `domain_verification` for verification details. |
| `domain_id` | `string` | TypeID of the domain that requires verification. |
| `verification_deadlines` | `array` | Deadlines that apply to the verification process. |
| `verification_claims` | `array` | Claims that need verification. Values can include `name`, `address`, `email`, and `phone`. |
| `registrants` | `array` | Registrant contacts associated with the domain. |
### Integration notes
Integrations that read `event_data` should:
1. Check `event_data.version`.
2. Use `event_data.message` as the primary event summary.
3. For failures, use `event_data.error.code` and `event_data.error.detail`.
4. For renewal events, read `event_data.details.expires_on` when
`event_data.details.detail_type` is `domain_renewal`.
5. For verification events, read `verification_deadlines`,
`verification_claims`, and `registrants` when
`event_data.details.detail_type` is `domain_verification`.
Older events that were created before the V1 migration may still contain the previous event_data shape. Integrations that process historical events should keep a fallback path for legacy event_data and use the top-level type and subtype fields to route those events.
## Related API Reference
- [`GET /v1/events`](/api-reference#tag/event/GET/v1/events)
- [`GET /v1/events/{event_id}`](/api-reference#tag/event/GET/v1/events/{event_id})
- [`PATCH /v1/events/{event_id}`](/api-reference#tag/event/PATCH/v1/events/{event_id})
# User tags
User tags are custom labels you create to organize and filter your domains, contacts, and zones. Use them to categorize resources by project, team, environment, client, or anything else that fits your workflow.
## Tag properties
| Field | Type | Description |
| -------------- | --------- | --------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `tag_id` | `string` | Unique identifier for the tag (TypeID format, e.g. `tag_01h45ytscbebyvny4gc8cr8ma2`). |
| `label` | `string` | The display name of the tag. Must be unique per type within your organization. |
| `type` | `string` | The resource type this tag applies to: `DOMAIN`, `CONTACT`, or `ZONE`. |
| `color` | `string` | Display color, from `color-1` through `color-10`. Colors are intentionally generic so that API consumers can map them to values that match their own branding and UI. |
| `description` | `string` | An optional description of what this tag represents. |
| `object_count` | `integer` | Number of objects currently assigned this tag. |
## Create a tag
```bash
curl "$OPUSDNS_API_BASE/v1/tags" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "Production",
"type": "DOMAIN",
"color": "color-3",
"description": "Domains used in production environments"
}'
```
Response:
```json
{
"tag_id": "tag_01h45ytscbebyvny4gc8cr8ma2",
"label": "Production",
"type": "DOMAIN",
"color": "color-3",
"description": "Domains used in production environments",
"object_count": 0,
"created_on": "2026-05-12T10:00:00Z",
"updated_on": "2026-05-12T10:00:00Z"
}
```
## List tags
Retrieve all tags for your organization, optionally filtered by type:
```bash
curl "$OPUSDNS_API_BASE/v1/tags?tag_types=DOMAIN" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
The response is paginated and supports sorting by `label`, `created_on`, or `updated_on`.
## Update a tag
Change the label, color, or description of an existing tag:
```bash
curl "$OPUSDNS_API_BASE/v1/tags/tag_01h45ytscbebyvny4gc8cr8ma2" \
--request PATCH \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "Staging",
"color": "color-5"
}'
```
## Delete a tag
Deleting a tag removes it from all assigned objects.
```bash
curl "$OPUSDNS_API_BASE/v1/tags/tag_01h45ytscbebyvny4gc8cr8ma2" \
--request DELETE \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Assign tags to objects
You can tag domains, contacts, and zones. There are two approaches depending on whether you want to operate from the tag side or the object side.
### Bulk assign by object
Use `POST /v1/tags/objects` to add, remove, or replace tags across multiple objects at once:
```bash
curl "$OPUSDNS_API_BASE/v1/tags/objects" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"type": "DOMAIN",
"objects": [
"domain_01h45ytscbebyvny4gc8cr8ma2",
"domain_01j7abc123def456ghi789jkl"
],
"add": [
"tag_01h45ytscbebyvny4gc8cr8ma2"
]
}'
```
You can use `add` and `remove` together to change tags in a single request. Alternatively, pass `replace` to set the exact tag list for the given objects, removing any tags not in the list.
The `replace` field is mutually exclusive with `add` and `remove`. An empty `replace` list removes all tags from the objects.
### Assign objects to a tag
Use `POST /v1/tags/{tag_id}/objects` to add or remove objects from a specific tag:
```bash
curl "$OPUSDNS_API_BASE/v1/tags/tag_01h45ytscbebyvny4gc8cr8ma2/objects" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"add": [
{ "object_type": "DOMAIN", "object_id": "domain_01h45ytscbebyvny4gc8cr8ma2" }
]
}'
```
## Include tags in domain responses
By default, domain responses do not include tag data. To include tags, add `include=tags` as a query parameter:
```bash
curl "$OPUSDNS_API_BASE/v1/domains?include=tags" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
Each domain in the response will contain an additional `tags` array:
```json
{
"domain_id": "domain_01h45ytscbebyvny4gc8cr8ma2",
"name": "example.com",
"tags": [
{ "tag_id": "tag_01h45ytscbebyvny4gc8cr8ma2", "label": "Production", "color": "color-3" }
]
}
```
| Field | Type | Description |
| -------- | -------- | ------------------------ |
| `tag_id` | `string` | The tag identifier. |
| `label` | `string` | The tag's display name. |
| `color` | `string` | The tag's display color. |
## Filter domains by user tags
Pass `tag_ids` to filter domains that have specific tags assigned:
```bash
curl "$OPUSDNS_API_BASE/v1/domains?tag_ids=tag_01h45ytscbebyvny4gc8cr8ma2&include=tags" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
When filtering by multiple tags, control the matching behavior with `tag_mode`:
| Mode | Behavior |
| ------------ | ----------------------------------------------------------------------------------------------------------- |
| `match_any` | Domain matches if it has **at least one** of the specified tags. This is the default. |
| `match_all` | Domain matches only if it has **all** of the specified tags. |
| `match_none` | Domain matches only if it has **none** of the specified tags. Domains carrying no tags at all are included. |
```bash
curl "$OPUSDNS_API_BASE/v1/domains?tag_ids=tag_01a,tag_02b&tag_mode=match_all&include=tags" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Related API Reference
* [`GET /v1/tags`](/api-reference#tag/tag/GET/v1/tags)
* [`POST /v1/tags`](/api-reference#tag/tag/POST/v1/tags)
* [`GET /v1/tags/{tag_id}`](/api-reference#tag/tag/GET/v1/tags/%7Btag_id%7D)
* [`PATCH /v1/tags/{tag_id}`](/api-reference#tag/tag/PATCH/v1/tags/%7Btag_id%7D)
* [`DELETE /v1/tags/{tag_id}`](/api-reference#tag/tag/DELETE/v1/tags/%7Btag_id%7D)
* [`POST /v1/tags/objects`](/api-reference#tag/tag/POST/v1/tags/objects)
* [`POST /v1/tags/{tag_id}/objects`](/api-reference#tag/tag/POST/v1/tags/%7Btag_id%7D/objects)
* [`GET /v1/domains`](/api-reference#tag/domain/GET/v1/domains)
# Status tags
Status tags are system-managed labels that OpusDNS assigns automatically based on the state of a domain. Unlike [user tags](/automation/tags/user-tags), you cannot create, modify, or remove status tags through the API — they are controlled entirely by the system and reflect conditions that may require your attention.
## How status tags work
When a domain enters a state that requires action or awareness, OpusDNS assigns the corresponding status tag automatically via a background process. Once the condition is resolved, the tag is removed. No API calls are needed on your part to manage these tags.
## Available status tags
| Tag type | Label | Description |
| --------------------------- | ------------------------- | ------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------ |
| `VERIFICATION_REQUIRED` | VERIFICATION REQUIRED | The domain requires identity verification from the registrant. Assigned when a registry mandates holder verification and removed once verification is completed. |
| `CREATE_REQUESTED` | CREATE REQUESTED | The registration was accepted but the domain does not exist at the registry yet, because it is waiting on an out-of-band step — the signed applicant declaration for a `.no` registration, for example. The domain cannot be updated while this tag is set. Removed once the registry create succeeds. |
| `INBOUND_TRANSFER_PENDING` | INBOUND TRANSFER PENDING | A transfer of the domain into your account is in progress at the registry. |
| `OUTBOUND_TRANSFER_PENDING` | OUTBOUND TRANSFER PENDING | A transfer of the domain away from your account is pending. Removed when the transfer completes or is rejected. |
| `EXTERNAL` | EXTERNAL | The domain is mirrored from a connected external registrar rather than sponsored by OpusDNS. See [Read-only domains](/products/domains/manage#read-only-domains). |
| `IMPORT_REQUESTED` | IMPORT REQUESTED | The domain was bulk-imported and is awaiting its initial registry synchronization. |
| `IMPORT_PENDING` | IMPORT PENDING | The initial registry synchronization for an imported domain has been queued and is awaiting execution. |
| `DNSSEC_PENDING` | DNSSEC PENDING | The zone is signed, but the registry has not yet accepted the DS record and the submission is being retried. See [Domain DNSSEC](/products/domains/dnssec). |
Additional status tag types may be introduced over time. Your integration should handle unknown `tag_type` values gracefully.
## Status tag response format
When you request `include=tags` on a domain endpoint, each domain includes a `status_tags` array alongside the user `tags` array:
```json
{
"domain_id": "domain_01h45ytscbebyvny4gc8cr8ma2",
"name": "example.com",
"tags": [],
"status_tags": [
{
"tag_type": "VERIFICATION_REQUIRED",
"label": "VERIFICATION REQUIRED",
"color": "color-1"
}
]
}
```
| Field | Type | Description |
| ------------- | -------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------- |
| `tag_type` | `string` | The status tag type identifier (e.g. `VERIFICATION_REQUIRED`). Use this for programmatic checks. |
| `label` | `string` | Human-readable display label. |
| `description` | `string` | Optional description of the status condition. |
| `color` | `string` | Display color for UI rendering. Colors are intentionally generic (e.g. `color-1`) so that API consumers can map them to values that fit their own branding. |
## Include status tags in responses
Status tags are returned together with user tags when you add `include=tags` to a domain request:
```bash
curl "$OPUSDNS_API_BASE/v1/domains?include=tags" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
This works on both the domain list and single-domain endpoints:
```bash
curl "$OPUSDNS_API_BASE/v1/domains/example.com?include=tags" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Filter domains by status tags
Use the `status_tags` parameter to find domains with specific status conditions:
```bash
curl "$OPUSDNS_API_BASE/v1/domains?status_tags=VERIFICATION_REQUIRED&include=tags" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
### Filter mode
When filtering by multiple status tags, control the matching behavior with `status_tag_mode`:
| Mode | Behavior |
| ------------ | ------------------------------------------------------------------------------------------------------------------------- |
| `match_any` | Domain matches if it has **at least one** of the specified status tags. This is the default. |
| `match_all` | Domain matches only if it has **all** of the specified status tags. |
| `match_none` | Domain matches only if it has **none** of the specified status tags. Domains carrying no status tags at all are included. |
```bash
curl "$OPUSDNS_API_BASE/v1/domains?status_tags=VERIFICATION_REQUIRED&status_tag_mode=match_all&include=tags" \
--header "X-Api-Key: $OPUSDNS_API_KEY"
```
## Status tags vs. registry statuses
Status tags and registry statuses serve different purposes:
| | Status tags | Registry statuses |
| -------------- | ------------------------------------------------ | --------------------------------------------------------- |
| **Source** | Assigned by OpusDNS based on internal processes | Set by the domain registry (e.g. Verisign, EURid) |
| **Purpose** | Indicate conditions that may need your attention | Control what operations are allowed on the domain |
| **Management** | Automatic — no API calls needed | Can be managed via `PATCH /v1/domains/{domain_reference}` |
| **Examples** | `VERIFICATION_REQUIRED` | `clientTransferProhibited`, `ok`, `pendingTransfer` |
Both are visible in the domain response but in separate fields: `status_tags` for OpusDNS status tags and `registry_statuses` for EPP status codes.
## Related guides
* [User tags](/automation/tags/user-tags) — create and manage your own tags
* [The domain object](/products/domains/domain-object) — full domain response reference
* [Manage a domain](/products/domains/manage) — update domain configuration
## Related API Reference
* [`GET /v1/domains`](/api-reference#tag/domain/GET/v1/domains)
* [`GET /v1/domains/{domain_reference}`](/api-reference#tag/domain/GET/v1/domains/%7Bdomain_reference%7D)
# Changelog
Track notable updates to the OpusDNS API and developer documentation here.
## 2026
### 2 September 2026
- Changed **independent billing for suborganizations to require approval**:
`billing_mode: "independent"` on
[`POST /v1/organizations`](/api-reference#tag/organization/POST/v1/organizations)
is now accepted only for top-level organizations that have been enabled for
the feature. Other requests are rejected with `422
ERROR_INDEPENDENT_BILLING_NOT_APPROVED`; consolidated billing and existing
independent suborganizations are unaffected. Contact
[support@opusdns.com](mailto:support@opusdns.com) for more information about
this feature. See [Billing modes](/account/organizations/manage#billing-modes).
- Changed **the production environment to serve timezone-aware (RFC 3339)
datetimes by default**, completing the staged cutover: every datetime in a
public `/v1` response now carries a trailing `Z`. The `X-Datetime-Format:
rfc3339` header remains accepted and is now a no-op. See
[Timezone-aware datetimes (RFC 3339)](/upcoming-changes/rfc3339-datetimes).
- Added **the registrar credential to domains held at a connected registrar**:
request `include=registrar_credential` on
[`GET /v1/domains`](/api-reference#tag/domain/GET/v1/domains) or
[`GET /v1/domains/{domain_reference}`](/api-reference#tag/domain/GET/v1/domains/{domain_reference})
and each domain synced from a connected registrar carries a
`registrar_credential` object with its `registrar_credential_id`, `name` and
`registrar`; natively registered domains return `null`. The domain list also
gained two repeatable filters, `registrar_credential_id` and `registrar`, so
you can list the domains behind one credential or one registrar. Values
within a parameter are OR-ed and the two parameters are AND-ed, as with `tld`
and `tag_ids`.
- Changed **domain `attributes` values to be validated**: `auto_renew_period`
accepts only `monthly` or `yearly`, and any other value is rejected with a
`422` naming the accepted values, on domain create, transfer-in and update and
at bulk job submission. Keys the platform writes itself
(`verification_required`, `nor_id_declaration`, `nor_id_declaration_token`,
`punktum_dk_tracking_no`) are now rejected if supplied, as the promotion keys
already were. The `attributes` field in the API Reference now lists every
key with its accepted values, the TLDs it applies to and whether it is read
from the request or written by the platform. Changing `auto_renew_period`
takes effect at the next renewal; the current expiry date does not move.
### 1 September 2026
- Onboarded **[`.bayern`](/tld-knowledge-base/gtlds/bayern)** (Bayern Connect
GmbH) and **[`.nrw`](/tld-knowledge-base/gtlds/nrw)** (Minds + Machines GmbH),
both served over the Tango registry backend. Published their TLD Knowledge Base
pages. Both lock a domain for 60 days after a registration or a transfer.
`.nrw` additionally requires the domain owner to hold a physical address in
Germany.
- Onboarded **[`.berlin`](/tld-knowledge-base/gtlds/berlin)** and
**[`.hamburg`](/tld-knowledge-base/gtlds/hamburg)** (both operated by TLD-BOX
Registrydienstleistungen GmbH). Published their TLD Knowledge Base pages. Both
require a domain owner, administrative and technical contact, each carrying a
physical address, and both lock a domain for 60 days after a registration or a
transfer.
- Onboarded **[`.dk`](/tld-knowledge-base/cctlds/dk)** (Denmark, operated by
Punktum dk). Published its TLD Knowledge Base page. A `.dk` registration is an
application rather than an allocation: the registry queues it, and the domain is
activated only once the registrant's data and ID control has completed. That
control is run by Punktum dk, using MitID for registrants residing in Denmark
and a risk assessment for everyone else.
### 28 August 2026
- Onboarded **[`.mx`](/tld-knowledge-base/cctlds/mx)** (Mexico, operated by
Registry .MX) together with its second-level extensions `.com.mx` and
`.org.mx`. Published its TLD Knowledge Base page.
### 27 August 2026
- Added **an `in_use` filter to the contact list**: `GET /v1/contacts?in_use=true`
returns only contacts attached to at least one domain, and `in_use=false` only
contacts attached to none. A contact counts as in use through any role -
registrant, admin, tech, or billing. Omitting the parameter keeps the
unfiltered listing. See
[`GET /v1/contacts`](/api-reference#tag/contact/GET/v1/contacts).
### 25 August 2026
- Onboarded **[`.se`](/tld-knowledge-base/cctlds/se)** (Sweden) and
**[`.nu`](/tld-knowledge-base/cctlds/nu)** (Niue), both operated by
Internetstiftelsen (The Swedish Internet Foundation). Published their TLD
Knowledge Base pages. For both TLDs the registry owns the auth code — request a
fresh one with
[`POST /v1/domains/tld-specific/se/{domain_reference}/auth_code/request`](/api-reference#tag/domain_tld_specific/POST/v1/domains/tld-specific/se/{domain_reference}/auth_code/request)
(or the `.nu` equivalent), which invalidates the previous code — and transfers
complete immediately, with no pending window.
- Released **the OpusDNS MCP server**, documented under the new **MCP** tab. It is
a hosted [Model Context Protocol](https://modelcontextprotocol.io) endpoint at
`https://api.opusdns.com/mcp` (sandbox: `https://sandbox.opusdns.com/mcp`) that
lets an AI client work with your account through nine tools: catalog search and
single operations, portfolio reads that project only the fields you ask for, and
multi-domain changes submitted as [Jobs](/automation/jobs/overview) batches
rather than a loop. Sign-in is browser OAuth and API keys are not accepted;
everything that is not a read is blocked server-side until you explicitly
approve it, and the approval is bound to the exact action, including the
resolved list of domains for a bulk change. The new pages cover connecting each
client, worked workflows, approvals, bulk operations, what the agent can see,
and troubleshooting. See [OpusDNS MCP server](/mcp-server).
- Added **an exclusionary tag filter mode**: `match_none` returns only the objects
carrying **none** of the listed tags, including objects that carry no tags at
all. It is accepted wherever `match_any` and `match_all` already were —
`tag_mode` on `GET /v1/domains`, `GET /v1/contacts` and `GET /v1/dns`, and
`status_tag_mode` on `GET /v1/domains` and `GET /v1/contacts`. See
[User tags](/automation/tags/user-tags#filter-mode) and
[Status tags](/automation/tags/status-tags#filter-mode).
- Added **status tag counts to the domain summary**: `GET /v1/domains/summary`
now returns a `by_status_tag` breakdown alongside `by_status`, `by_tld`, and
`by_organization`. Only status tags with at least one domain are included, so
the map is empty rather than zero-filled when nothing is tagged.
- Fixed **`match_all` tag filtering when the same tag is repeated** in the query
string. `?status_tags=X&status_tags=X` compared a distinct-tag count against
the number of values supplied and therefore matched nothing; repeated values
are now collapsed.
- Added **`create_zone` to whitelabel Plus onboarding**. A Plus create or upgrade
can now ask OpusDNS to create the customer's DNS zone as part of onboarding
instead of requiring a separate zone create first. The flag is remembered and
re-applied on every recheck, and a caller who created without it can opt in on
a later recheck. A zone that cannot be created fails onboarding with the new
`zone_create_failed` code. Domain verification is unchanged — the customer
still has to delegate the domain to the OpusDNS nameservers.
- Documented **the AFNIC contact attributes** on the TLD Knowledge Base pages for
[`.fr`](/tld-knowledge-base/cctlds/fr#contact-attributes),
[`.re`](/tld-knowledge-base/cctlds/re#contact-attributes),
[`.pm`](/tld-knowledge-base/cctlds/pm#contact-attributes),
[`.wf`](/tld-knowledge-base/cctlds/wf#contact-attributes),
[`.yt`](/tld-knowledge-base/cctlds/yt#contact-attributes) and
[`.tf`](/tld-knowledge-base/cctlds/tf#contact-attributes) — the `PP`/`PM`
split, the identifiers each legal status accepts, the association rules, and
the fact that AFNIC requires the attributes on every contact role rather than
on the registrant alone.
### 24 August 2026
- Added **spec-selection overrides to the TLD specification endpoint**.
`GET /v1/tlds/{tld}` accepts optional `backend`, `customer_spec_ref`, and
`version` query parameters to read a specific registry backend's specification
instead of the one resolved for your organization. Omitting them keeps the
existing behaviour.
- Changed **`.dk` contact pre-verification to be optional**. Punktum dk runs its
own data and identity control and reports the outcome over poll;
`PUNKTUM_DK_CONTACT_VERIFIED` previously had to be asserted on every `.dk`
contact. It is now an optional attribute — omit it to let the registry perform
the control, or assert it to declare the contact already verified.
### 22 August 2026
- Added **the `DNSSEC_PENDING` status tag**. A domain carries it while a deferred
DNSSEC registry submission is being retried, so a zone that reads as signed
while the parent still holds no DS is visible rather than silently
misreported. The tag is removed on every terminal outcome. See
[Status tags](/automation/tags/status-tags).
### 21 August 2026
- Changed **enabling DNSSEC to complete asynchronously when the registry defers
the DS submission**. Some registries — DENIC among them — check the domain's
public nameservers before accepting a DS and reject a submission made before
the new key material has propagated. Rather than failing, the zone stays
signed and the submission is retried in the background for roughly 16 minutes;
if that budget runs out, DNSSEC is switched back off and the registry's own
diagnostic reaches you as a domain modification failure event.
`POST /v1/domains/{domain_reference}/dnssec/enable` and
`POST /v1/dns/{zone_name}/dnssec/enable` now answer **`202 Accepted`** when the
submission was deferred, instead of always answering `200`. A concurrent
disable that supersedes the enable returns **`409 Conflict`** with
`ERROR_DOMAIN_DNSSEC_ENABLE_SUPERSEDED`. On the zone route, `DnsChangesResponse`
carries the outcome in `dnssec_registry_publish` — `published`, `deferred`,
`skipped`, `withdrawn`, or `failed`, and `null` when the response makes no
statement about a registry submission. A signed zone with no DS at the parent
resolves as unsigned, so the intermediate state is safe. See
[Domain DNSSEC](/products/domains/dnssec).
- Fixed **IDN registrations on Verisign TLDs**. Registering an internationalized
domain under `.com`, `.net`, `.cc`, or `.name` failed at the registry with
`Language tag required for IDN label domain names`, because the required
language tag was not sent. It is now included on registration. Note that the
API does not convert a Unicode name to its A-label for you — send the
punycode form (`xn--…`).
### 20 August 2026
- Added **typed credential errors to registrar sync**. When a connected
registrar rejects the stored credentials, the sync status now reports a stable
`error_code` — `ERROR_CREDENTIAL_AUTH` when the credentials were rejected, or
`ERROR_CREDENTIAL_ACCESS` when the account denied access (for example, a
calling IP that is not allowlisted) — alongside an actionable `error_message`
and the registrar's own diagnostic in `error_detail`. These failures are no
longer retried, so they surface immediately instead of after several minutes
of backoff.
- Added **the `IMPORT_REQUESTED` and `IMPORT_PENDING` status tags**, carried by
domains during a bulk import while their initial registry synchronization is
queued and then running. See
[Status tags](/automation/tags/status-tags).
### 19 August 2026
- Added **the `EXTERNAL` status tag**, assigned to every domain mirrored into
your portfolio from a connected external registrar. It distinguishes mirrored
domains from the ones OpusDNS sponsors, and can be filtered on like any other
status tag. See [Status tags](/automation/tags/status-tags).
- Added **the billing period to the whitelabel subscription block**. The nested
`subscription` object now carries `period` in the same shape the create body
accepts (`{"value": 1, "unit": "m"}`), so a client can tell whether a
whitelabel renews monthly or yearly without a second lookup.
- Changed **`.dk` contact validation to run before the request reaches the
registry**. `PUNKTUM_DK_CVR` is required for a Danish legal entity and refused
on a Danish individual, and `PUNKTUM_DK_SOLE_PROPRIETORSHIP` is refused on any
Danish contact — all three previously failed only once Punktum dk saw them.
EU/EEA legal entities outside Denmark may still supply a CVR and are not
required to.
### 18 August 2026
- Changed **the sandbox environment to serve timezone-aware (RFC 3339) datetimes
by default**, on schedule per the announced staged cutover. Every datetime in
public `/v1` responses from sandbox now carries the explicit UTC designator
(trailing `Z`); the `X-Datetime-Format: rfc3339` header remains accepted there
and is now a no-op. Production follows on Tuesday, 2026-09-01. See
[Timezone-aware datetimes (RFC 3339)](/upcoming-changes/rfc3339-datetimes) for
migration guidance.
- Added **a `read_only` flag to the domain object**: a domain marked read-only
is listed in your portfolio but cannot be managed — updates, renewals, and
deletions are rejected. OpusDNS sets and removes the flag; it cannot be
changed through the API. It is used for domains imported ahead of a
migration, domains locked for legal reasons, and domains managed at an
external registrar. The flag is included in every domain response and
`GET /v1/domains` accepts a `read_only` query parameter to filter by it. See
[The domain object](/products/domains/domain-object) and
[Read-only domains](/products/domains/manage#read-only-domains).
### 14 August 2026
- Added **postal code validation on contacts**: `postal_code` is validated
against the country's published format for an initial set of 16 countries
(`AT`, `BE`, `CA`, `CH`, `CZ`, `DE`, `DK`, `ES`, `FR`, `GB`, `IT`, `LU`,
`NL`, `NO`, `SE`, `US`). Contacts in every other country are unaffected. An
invalid postal code returns a `422` request-validation error whose error
`type` is `invalid_postal_code`, locating the `postal_code` field. A postal
code containing non-ASCII characters is rejected for every country, because
it cannot be transmitted to a registry. See
[Postal codes](/products/contacts/postal-codes).
- Changed **postal codes to be stored in a canonical form**: Dutch postal codes
are stored in the official national notation (`1234 AB` — both `1234AB` and
`1234 ab` are accepted), cross-border country prefixes are stripped
(`D-26133` → `26133` for a `DE` contact), and US ZIP+4 is normalized to the
hyphenated form (`12345 6789` → `12345-6789`). Existing Dutch contact data
was migrated to the canonical form. See
[What gets stored](/products/contacts/postal-codes#what-gets-stored).
- Added **the registry's own field-level validation messages** to registry
errors. Where a registry reports which field it refused, an
`ERROR_REGISTRY_POLICY` on a domain or contact operation now carries that text
in `detail` after the generic result code, instead of the result code text
alone. For a `.nl` postcode rejected by SIDN, `detail` now ends with
`Contact address group: A postcode has to be four numbers and two letters.`
### 11 August 2026
- Onboarded the Welsh geographic TLDs
**[`.wales`](/tld-knowledge-base/gtlds/wales)** and
**[`.cymru`](/tld-knowledge-base/gtlds/cymru)** (operated by Nominet).
Published their TLD Knowledge Base pages.
### 10 August 2026
- Onboarded **[`.pl`](/tld-knowledge-base/cctlds/pl)** (Poland) together with
its second-level extensions `.com.pl`, `.net.pl`, and `.org.pl`;
**[`.gg`](/tld-knowledge-base/cctlds/gg)** (Guernsey) together with `.co.gg`,
`.net.gg`, and `.org.gg`; and **[`.je`](/tld-knowledge-base/cctlds/je)**
(Jersey) together with `.co.je`, `.net.je`, and `.org.je`. Published their TLD
Knowledge Base pages.
- Onboarded the Belgian geographic TLDs
**[`.brussels`](/tld-knowledge-base/gtlds/brussels)** and
**[`.vlaanderen`](/tld-knowledge-base/gtlds/vlaanderen)**. Published their TLD
Knowledge Base pages.
### 04 August 2026
- Added **sub-zone delegation**: NS records below the zone apex are now
fully supported on every zone endpoint — include them when creating a zone,
or manage them with the RRset and record PATCH endpoints like any other
record type. OpusDNS nameservers serve the delegation as a standard DNS
referral. Delegations from DNSSEC-signed zones are insecure delegations
(child DS records are not supported). See
[Delegate a subdomain](/products/dns/subzone-delegation).
- Changed **writes targeting system-managed records to return errors instead
of silently doing nothing**. Previously, a `PUT`/`PATCH` that tried to
modify or remove the zone apex NS, SOA, DNSKEY, or DS records could return
`204 No Content` while the request had no effect. These now return
`409 Conflict` with a `protected_reason`. Zone responses also report
`protected: true` consistently for every system-managed RRset. If your
integration echoes a full zone read back into a write, filter out RRsets
with `protected: true` first — see
[Protected records](/products/dns/zone-object#protected-records).
### 03 August 2026
- Onboarded **[`.lt`](/tld-knowledge-base/cctlds/lt)** (Lithuania) and
**[`.ws`](/tld-knowledge-base/cctlds/ws)** (Samoa). Published their TLD
Knowledge Base pages.
### 31 July 2026
- Onboarded **[`.vegas`](/tld-knowledge-base/gtlds/vegas)**. Published its TLD
Knowledge Base page.
### 30 July 2026
- Onboarded **[`.no`](/tld-knowledge-base/cctlds/no)** (Norway). Published its
TLD Knowledge Base page.
- Added **outbound transfer resolution** — approve or reject a pending
transfer of a domain away from OpusDNS directly via the API:
`POST /v1/domains/{domain_reference}/transfer/outbound` with an `action` of
`approve` or `reject`. Approving acknowledges the transfer at the registry;
the domain remains in your account until the registry confirms the transfer
has completed. Requires the domain to have a pending transfer, and is
available for TLDs whose registry lets the losing registrar act on
transfers. See
[Outbound transfers](/products/domains/transfer#outbound-transfers).
### 22 July 2026
- Onboarded **[`.si`](/tld-knowledge-base/cctlds/si)** (Slovenia). Published its
TLD Knowledge Base page.
### 17 July 2026
- Onboarded **[`.lv`](/tld-knowledge-base/cctlds/lv)** (Latvia) together with
its second-level extensions `.asn.lv`, `.com.lv`, `.conf.lv`, `.edu.lv`,
`.id.lv`, `.net.lv`, and `.org.lv`. Published its TLD Knowledge Base page.
- Added **independent billing for suborganizations**: create a suborganization
with `billing_mode: "independent"` and it gets its own wallet, invoices, and
payment methods instead of rolling up to your account. Consolidated billing
remains the default and is unchanged. Also added the monthly
**suborganization billing transactions report** covering spend across your
whole organization tree. See
[Billing modes](/account/organizations/manage#billing-modes).
- Added **opt-in RFC 3339 datetimes**: send the `X-Datetime-Format: rfc3339`
request header on any public `/v1` endpoint and every datetime in the response
is returned as timezone-aware UTC with a trailing `Z`. This fixes clients (such
as JavaScript's `new Date()`) that misparse today's marker-less timestamps as
local time. The tz-aware format becomes the default per environment on a staged
schedule, after which the header is a no-op. See
[Timezone-aware datetimes (RFC 3339)](/upcoming-changes/rfc3339-datetimes) for
the cutover dates and migration guidance.
### 10 July 2026
- Added **automatic DNSSEC reconciliation** on inbound transfers and nameserver
changes. Stale DS records imported from a previous DNS provider — which could
previously break resolution (`SERVFAIL`) once a domain moved to OpusDNS
nameservers — are now removed or replaced automatically. Domains on external
nameservers are never touched. See
[Automatic DNSSEC reconciliation](/products/domains/dnssec#automatic-dnssec-reconciliation).
### 08 July 2026
- Onboarded **3 IDN gTLDs** operated by Public Interest Registry:
[`.xn--c1avg`](/tld-knowledge-base/gtlds/xn--c1avg) (.орг),
[`.xn--i1b6b1a6a2e`](/tld-knowledge-base/gtlds/xn--i1b6b1a6a2e) (.संगठन), and
[`.xn--nqv7f`](/tld-knowledge-base/gtlds/xn--nqv7f) (.机构). Their TLD Knowledge
Base pages are published.
- Onboarded **[`.juegos`](/tld-knowledge-base/gtlds/juegos)**. Its TLD Knowledge
Base page is published.
### 07 July 2026
- Onboarded **[`.lu`](/tld-knowledge-base/cctlds/lu)** (Luxembourg). Published
its TLD Knowledge Base page.
### 06 July 2026
- Onboarded **`.co.at`** and **`.or.at`**, the Austrian second-level
extensions. See the [`.at` TLD Knowledge Base](/tld-knowledge-base/cctlds/at)
page.
### 02 July 2026
- Onboarded **8 new gTLDs**: [`.to`](/tld-knowledge-base/cctlds/to) (Tonga),
[`.country`](/tld-knowledge-base/gtlds/country),
[`.diy`](/tld-knowledge-base/gtlds/diy),
[`.food`](/tld-knowledge-base/gtlds/food),
[`.hiv`](/tld-knowledge-base/gtlds/hiv),
[`.lifestyle`](/tld-knowledge-base/gtlds/lifestyle),
[`.living`](/tld-knowledge-base/gtlds/living), and
[`.sexy`](/tld-knowledge-base/gtlds/sexy). Published their TLD Knowledge Base
pages.
### 30 June 2026
- Made the **`contacts` section optional on domain transfers**. For TLDs that do
not require any contacts on an inbound transfer - where every supported contact
role has a minimum of `0` in the TLD specification (for example `.ca` and
`.ch`) - you can
now omit `contacts` entirely instead of sending an empty object. This applies to
`POST /v1/domains/transfer` as well as the `domain_transfer` and
`domain_transfer_bulk` job commands. TLDs that require one or more contact roles
still reject transfers submitted without them.
### 26 June 2026
- Onboarded **13 new gTLDs**: [`.best`](/tld-knowledge-base/gtlds/best),
[`.cam`](/tld-knowledge-base/gtlds/cam),
[`.case`](/tld-knowledge-base/gtlds/case),
[`.dealer`](/tld-knowledge-base/gtlds/dealer),
[`.fans`](/tld-knowledge-base/gtlds/fans),
[`.frl`](/tld-knowledge-base/gtlds/frl),
[`.help`](/tld-knowledge-base/gtlds/help),
[`.inc`](/tld-knowledge-base/gtlds/inc),
[`.kred`](/tld-knowledge-base/gtlds/kred),
[`.luxury`](/tld-knowledge-base/gtlds/luxury),
[`.ooo`](/tld-knowledge-base/gtlds/ooo),
[`.reit`](/tld-knowledge-base/gtlds/reit), and
[`.saarland`](/tld-knowledge-base/gtlds/saarland). Published their TLD
Knowledge Base pages.
### 25 June 2026
- Onboarded **[`.name`](/tld-knowledge-base/gtlds/name)** and
**[`.cc`](/tld-knowledge-base/cctlds/cc)**. Published their TLD Knowledge Base
pages.
### 24 June 2026
- Onboarded **[`.blog`](/tld-knowledge-base/gtlds/blog)**. Published its TLD
Knowledge Base page.
### 21 June 2026
- Added **vanity nameservers** — serve your DNS zones under your own branded
nameserver names (for example `ns1.example.com`) while OpusDNS continues to
answer the DNS. Create and manage vanity nameserver sets with
`POST`/`GET`/`DELETE /v1/vanity-nameserver-sets`, choose an organization
default with `PATCH /v1/vanity-nameserver-sets/{set_id}/default`, and brand
individual zones via `vanity_nameserver_set_id` (on zone creation, or with
`PATCH /v1/dns/{zone_name}/vanity-set`).
- Added the **`/check` diagnostic** — `POST /v1/vanity-nameserver-sets/check`
reports whether a set's nameservers resolve to the anycast pool, whether glue
is in place, and what (if anything) still needs publishing.
- Published the [Vanity nameservers](/products/dns/vanity-nameservers) guide.
### 19 June 2026
- Onboarded **21 new TLDs**, including the Bahrain ccTLD bundle and its
Arabic-script variant:
- [`.bh`](/tld-knowledge-base/cctlds/bh),
[`.biz.bh`](/tld-knowledge-base/cctlds/biz.bh),
[`.cc.bh`](/tld-knowledge-base/cctlds/cc.bh),
[`.com.bh`](/tld-knowledge-base/cctlds/com.bh),
[`.edu.bh`](/tld-knowledge-base/cctlds/edu.bh),
[`.info.bh`](/tld-knowledge-base/cctlds/info.bh),
[`.me.bh`](/tld-knowledge-base/cctlds/me.bh),
[`.name.bh`](/tld-knowledge-base/cctlds/name.bh),
[`.net.bh`](/tld-knowledge-base/cctlds/net.bh),
[`.org.bh`](/tld-knowledge-base/cctlds/org.bh), and
[`.xn--mgbcpq6gpa1a`](/tld-knowledge-base/gtlds/xn--mgbcpq6gpa1a) (Bahrain)
- [`.co.nl`](/tld-knowledge-base/cctlds/co.nl),
[`.co.no`](/tld-knowledge-base/cctlds/co.no),
[`.co.com`](/tld-knowledge-base/gtlds/co.com)
- [`.fm`](/tld-knowledge-base/cctlds/fm) (Micronesia),
[`.fo`](/tld-knowledge-base/cctlds/fo) (Faroe Islands),
[`.gd`](/tld-knowledge-base/cctlds/gd) (Grenada),
[`.gl`](/tld-knowledge-base/cctlds/gl) (Greenland),
[`.radio.am`](/tld-knowledge-base/cctlds/radio.am),
[`.radio.fm`](/tld-knowledge-base/cctlds/radio.fm),
[`.vg`](/tld-knowledge-base/cctlds/vg) (British Virgin Islands)
- Published their TLD Knowledge Base pages.
### 18 June 2026
- Onboarded **[`.it`](/tld-knowledge-base/cctlds/it)** (Italy),
**[`.sk`](/tld-knowledge-base/cctlds/sk)** and **`.org.sk`** (Slovakia), and
**[`.latino`](/tld-knowledge-base/gtlds/latino)**. Published their TLD
Knowledge Base pages.
### 17 June 2026
- Onboarded **[`.cloud`](/tld-knowledge-base/gtlds/cloud)**. Published its TLD
Knowledge Base page.
### 16 June 2026
- Released the **role-based permissions** system. Access is now governed by
roles built from `resource:scope` permissions (scopes: `read`, `manage`,
`delete`).
- Added **built-in roles** — `admin`, `viewer`, `domain_manager`, `dns_manager`,
and `billing_manager` — available in every organization.
- Added **custom roles** — define organization-owned roles with exactly the
permissions you need via `POST /v1/organizations/roles`, and manage them with
`GET`/`PATCH`/`DELETE /v1/organizations/roles/{label}`. Retrieve the grantable
permission catalog from `GET /v1/organizations/role-permissions`.
- Added **per-user role assignment** — `GET` and `PUT /v1/users/{user_id}/role`
set a user's built-in or custom role. API keys are granted a role at issuance.
- Published the [Roles & permissions](/account/organizations/roles) guide and a
roles section in [User management](/account/users).
### 15 June 2026
- Onboarded **[`.cz`](/tld-knowledge-base/cctlds/cz)** (Czechia). Published its
TLD Knowledge Base page.
### 12 June 2026
- Added **host object management** — create, retrieve, update, and delete
nameserver host objects (glue records) for hostnames subordinate to domains
in your account: `POST /v1/hosts` and
`GET`/`PUT`/`DELETE /v1/hosts/{host_reference}`. Hosts can be referenced by
ID or hostname.
- Published the [Host objects (glue records)](/products/domains/host-objects)
guide and linked it from the nameservers, registration, and transfer guides.
- Added **batch retry** — re-attempt jobs in a batch that ended in `failed` or
`dead_letter` state without rebuilding the batch.
`POST /v1/jobs/{batch_id}/retry` re-queues all eligible jobs in one call;
jobs in any other state are left untouched.
- Added an optional repeatable `error_class` query parameter on batch retry to
re-attempt only specific failure types (for example,
`?error_class=BillingInsufficientFundsError` after an account top-up).
Multiple values are OR'd.
- Added **single-job retry** — `POST /v1/job/{job_id}/retry` re-queues an
individual `failed` or `dead_letter` job. Retrying a job in any other state
returns `409 Conflict`.
- Updated the [Managing batches](/automation/jobs/managing-batches) guide with
retry usage, including how `error_class` filtering helps recover from
mixed-failure batches.
### 12 May 2026
- Added **status tags** — system-managed labels that are automatically assigned
to domains based on their state. The first status tag type is
`VERIFICATION_REQUIRED`, applied when a registry mandates holder verification.
- Domain list endpoints now support `status_tags` and `status_tag_mode` filters
to find domains by their current status conditions.
- When requesting `include=tags`, domain responses now return both user `tags`
and `status_tags` in separate arrays.
- Published the [User tags](/automation/tags/user-tags) and
[Status tags](/automation/tags/status-tags) documentation guides.
### 08 May 2026
- Released the V1 event payload format. All events now use a standardized
`event_data` structure with `version`, `message`, optional `error`, and
optional `details` fields. See [the event object](/automation/events/event-object)
for the full schema.
- Changed the event ID prefix from `epp_event_` to `event_`.
- Added typed `details` for renewal events (`expires_on`) and verification
events (`verification_deadlines`, `verification_claims`, `registrants`).
- Migrated all existing production events to the V1 payload format.
- Removed the `source` field from the event response.
### 05 May 2026
- Launched the new OpusDNS API Docs experience, including guides for
authentication, domains, DNS, forwarding, jobs, events, account management,
and TLD-specific operations.
- Published authentication documentation covering token retrieval, header usage,
and credential management.
- Published the Reports API and Tags API in the public OpenAPI schema.
- Documented bulk DNS-zone command behavior in the Jobs guide.
### 23 April 2026
- Added the Tags API and expanded tagging across domains, contacts, and DNS
zones.
- Added bulk tagging endpoints for applying tags to many resources at once.
- Added `tag_ids` filters for domain lists and search, plus tag support in
inventory and DNS-zone CSV exports.
- Added an `is_premium` filter for domain listings.
- Added additional DNS record type support: `HTTPS`, `SVCB`, `NAPTR`, `SSHFP`,
and `CERT`.
- Added `dnssec_status` support to bulk DNS-zone updates.
- Added `domain_forwards`, `expiring_domains`, and `email_forwards` report
types.
- Added new default nameservers for staging and sandbox environments.
- Improved DNS record handling for duplicate records and fully qualified domain
name comparisons.
### 16 April 2026
- Added premium-domain handling.
- Added EPP fee and charge support for domain pricing workflows.
- Added trademark-claims support for domain availability and registration
workflows.
- Added support for retrieving trademark notices and accepting claims during
domain registration.
- Added required attestation handling for `.music` and `.travel` registrations.
- Expanded TLD and registry coverage:
- `.co`
- `.mobile`
- `.music`
- `.link`
- `.name`
- `.cc`
- `.us`
- `.ua`
- `.nl`
- Google Registry TLDs
### 31 March 2026
- Published job batches and reports in the public API schema.
- Added the Reports API, including asynchronous report generation, downloads,
filtering, pagination, and DNS zone report types.
- Added downloadable report archives.
- Added generic filterable report endpoints and standardized report field names.
- Improved Jobs API list responses with typed payloads, labels, sorting, and
server-side status filtering.
- Added multi-value status filtering for batch jobs.
- Added filtering and sorting across jobs and batches, including status,
correlation ID, and topic filters.
- Added batch domain-exists checks and streaming domain availability requests.
### 12 February 2026
- Expanded the Jobs API with bulk domain operations, DNS zone updates, DNS patch
operations, contact creation, parking operations, and pause/resume controls.
- Added bulk multi-domain commands, bulk DNS-zone update commands, and DNS-zone
patch batches.
- Added bulk contact creation and single contact creation as Jobs API commands.
- Added bulk parking operations.
- Added job ownership checks and the `MANAGE_JOBS` permission.
- Added support for domain names or `domain_id` values in bulk domain update
payloads.
- Added Parking API support, including signup, restrictions, agreement
validation, and metrics.
### 15 January 2026
- Added domain forwarding metrics filters, including protocol and status-code
breakdowns for redirect traffic.
- Added forward-rule grouping in metrics aggregations.
- Added platform and browser aggregation fields for forwarding metrics.
## 2025
### 18 December 2025
- Added the Batch Jobs API and OpenAPI documentation for job workflows.
- Added job lookup and delete endpoints, batch deletion, TypeID job identifiers,
and standard pagination for batch jobs.
- Added recurring-job updates and deletion.
- Added bulk job cancellation.
- Added timezone-aware datetime serialization across the Jobs API.
- Added alpha-2 country-code validation on contact creation.
### 04 December 2025
- Added domain forwarding metrics endpoints.
- Revised email forwarding endpoints around `email_forward_id`-based routing.
- Revised the Domain Forwarding API surface with clearer create, update, delete,
and read operations.
- Added an endpoint to list all domain forwards in an organization.
- Added hostname validation and improved wildcard handling for domain forwards.
- Added cleanup behavior for DNS records when removing enabled forwarding rules.
- Added the Archive API with request-history and object-log endpoints.
- Improved email-forwarding search.
### 15 November 2025
- Introduced the Jobs service foundation for asynchronous API operations and
bulk workflow orchestration.
- Added the foundation for job context propagation across asynchronous API
workflows.
- Aligned DNS and Domains list endpoints with the public pagination format.
- Added DNSSEC operations to the Domains API.
### 14 October 2025
- Added domain forwarding to the API documentation and expanded the Domain
Forwarding API.
- Added domain-forward rule models, domain-forward enabled zones, sub-zone
handling, wildcard forwarding, and per-rule enable tracking.
- Added a TLD-specification list endpoint with `key` and `tld` filters.
- Increased TXT record support up to 65,535 bytes.
- Added `namestore` extension support for host commands on supported registries.
### 01 October 2025
- OpusDNS launches! 🚀
- Added the Domain API for core domain lifecycle operations.
- Added the DNS API for hosted zones, DNS records, and DNSSEC.
- Added the Contacts API for domain contact management.
- Added the Organizations and Users APIs for account management.
- Added API authentication with API keys and bearer tokens.
# 🇦🇬 .ag — Antigua and Barbuda
> The **.ag** is a country-code top-level domain (ccTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [nic.ag](https://nic.ag) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact, Administrator |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.nic.ag/dispute_policy.htm](https://www.nic.ag/dispute_policy.htm) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇦🇮 .ai — Anguilla
> The **.ai** is a country-code top-level domain (ccTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.nic.ai](https://www.nic.ai) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 2–10 years |
| Renewal Period | 2–10 years |
| Transfer Renewal Period | 2 years |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 15 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact, Administrator |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+2 years) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇦🇹 .at — Austria
> The **.at** is a country-code top-level domain (ccTLD) operated by nic.at GmbH. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | nic.at GmbH |
| Registry Country | Austria |
| Registry Website | [www.nic.at](https://www.nic.at/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1 year |
| Renewal Period | 1 year |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 0 days |
| Redemption Period | 60 days |
| Pending Restore | 7 days |
| Pending Delete | 59 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (6–16 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 2–8 |
| Host Objects Allowed | ❌ No |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ❌ No |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ❌ No |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.at` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | Domain Dispute |
| Reference | [www.nic.at/en/how-at-works/faqs/domain-disputes-and-wait-status](https://www.nic.at/en/how-at-works/faqs/domain-disputes-and-wait-status) |
| UDRP Support | ❌ No |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇧🇪 .be — Belgium
> The **.be** is a country-code top-level domain (ccTLD) operated by DNS Belgium. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | DNS Belgium |
| Registry Country | Belgium |
| Registry Website | [www.dnsbelgium.be](https://www.dnsbelgium.be) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1 year |
| Renewal Period | 1 year |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 0 days |
| Redemption Period | 40 days |
| Pending Restore | 0 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 2–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–9 |
| Host Objects Allowed | ❌ No |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DNSKEY |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.dns.be` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | ADR |
| Reference | [www.dnsbelgium.be/en/domain-name/dispute/ADR](https://www.dnsbelgium.be/en/domain-name/dispute/ADR) |
| UDRP Support | ❌ No |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇧🇭 .bh — Bahrain
> The **.bh** is a country-code top-level domain (ccTLD) operated by Telecommunications Regulatory Authority (TRA). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Telecommunications Regulatory Authority (TRA) |
| Registry Country | Bahrain |
| Registry Website | [domains.bh](https://domains.bh/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–5 years |
| Renewal Period | 1–5 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.bhregistry.bh` |
| RDAP Server | [rdap.bhregistry.bh/rdap](https://rdap.bhregistry.bh/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇧🇭 .biz.bh — Bahrain
> The **.biz.bh** is a country-code top-level domain (ccTLD) operated by Telecommunications Regulatory Authority (TRA). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Telecommunications Regulatory Authority (TRA) |
| Registry Country | Bahrain |
| Registry Website | [domains.bh](https://domains.bh/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–5 years |
| Renewal Period | 1–5 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.bhregistry.bh` |
| RDAP Server | [rdap.bhregistry.bh/rdap](https://rdap.bhregistry.bh/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇧🇿 .bz — Belize
> The **.bz** is a country-code top-level domain (ccTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [belizenic.bz](https://belizenic.bz) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact, Administrator |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [belizenic.bz/support/content.php?action=mypages&page=policy-udndrp.html](https://belizenic.bz/support/content.php?action=mypages&page=policy-udndrp.html) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇨🇦 .ca — Canada
> The **.ca** is a country-code top-level domain (ccTLD) operated by Canadian Internet Registration Authority (CIRA). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Canadian Internet Registration Authority (CIRA) |
| Registry Country | Canada |
| Registry Website | [www.cira.ca](https://www.cira.ca) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 2–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ✅ Yes |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (6–16 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.cira.ca` |
| RDAP Server | [rdap.ca.fury.ca](https://rdap.ca.fury.ca/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | CDRP |
| Reference | [www.cira.ca/en/resources/documents/domains/cira-domain-name-dispute-resolution-rules-16](https://www.cira.ca/en/resources/documents/domains/cira-domain-name-dispute-resolution-rules-16/) |
| UDRP Support | ❌ No |
| URS Support | ❌ No |
## Local Presence
| Property | Value |
| --- | --- |
| Local Presence Required | ✅ Yes |
| Applies To Roles | Domain Owner |
| Requirements | Physical Address, Business Entity |
| Eligible Countries | CA |
## Contact Attributes
`.ca` registrations carry a registry-specific contact attribute beyond the standard EPP fields:
| Attribute | Type | Required | Applies to | Allowed values |
| --- | --- | --- | --- | --- |
| `CIRA_CPR` | Enum | ✅ Required | Domain Owner | Any code in the table below |
| `CIRA_CPR` | Enum | ➖ Optional | Administrator | `CCT`, `RES`, `LGR`, `ABO` |
CIRA requires the administrator contact to be an **individual**, so its optional `CIRA_CPR` value is limited to the four individual categories (`CCT`, `RES`, `LGR`, `ABO`). The domain owner may use any category.
> ⚠️ **Reusing one contact for every role?** Do not copy the domain owner's `CIRA_CPR` onto the administrator contact. A non-individual value such as `EDU` or `GOV` is valid for the domain owner but rejected for the administrator:
>
> ```json
> {
> "type": "policy-validation-error",
> "title": "Policy Validation Error",
> "status": 422,
> "code": "ERROR_POLICY_VALIDATION",
> "errors": [
> {
> "detail": "Invalid value 'EDU' for attribute 'CIRA_CPR'. Allowed values: CCT, RES, LGR, ABO",
> "pointer": "contacts.admin[0].attributes.CIRA_CPR"
> }
> ],
> "detail": "Policy validation failed"
> }
> ```
>
> Since the administrator's `CIRA_CPR` is optional, the simplest approach is to omit it for non-registrant roles.
These per-role constraints are machine-readable: each `possible_attributes` entry returned by [`GET /v1/tlds/ca`](/api-reference#tag/tld/GET/v1/tlds/{tld}) carries its own `values`, `required`, and `contact_roles` fields. Integrations that build forms from the TLD specification should filter the allowed values by contact role rather than offering the domain owner's list for every contact.
## Canadian Presence Requirement (CIRA_CPR)
Every `.ca` domain must satisfy CIRA's [Canadian Presence Requirements](https://www.cira.ca/en/resources/documents/domains/canadian-presence-requirements-registrants/). The registrant declares which legal type establishes their Canadian presence through the `CIRA_CPR` attribute.
| Code | Legal type | Individual |
| --- | --- | --- |
| `ABO` | Aboriginal Peoples (individuals or groups) indigenous to Canada | ✅ |
| `ASS` | Canadian unincorporated association | ❌ |
| `CCO` | Canadian corporation, or Canadian province or territory | ❌ |
| `CCT` | Canadian citizen | ✅ |
| `EDU` | Canadian educational institution | ❌ |
| `GOV` | Government or government entity in Canada | ❌ |
| `HOP` | Canadian hospital | ❌ |
| `INB` | Indian Band recognized by the Indian Act of Canada | ❌ |
| `LAM` | Canadian library, archive, or museum | ❌ |
| `LGR` | Legal Representative of a Canadian Citizen or Permanent Resident | ✅ |
| `MAJ` | Her/His Majesty the Queen/King | ❌ |
| `OMK` | Official mark registered in Canada | ❌ |
| `PLT` | Canadian political party | ❌ |
| `PRT` | Partnership registered in Canada | ❌ |
| `RES` | Permanent resident of Canada | ✅ |
| `TDM` | Trade-mark registered in Canada (by a non-Canadian owner) | ❌ |
| `TRD` | Canadian trade union | ❌ |
| `TRS` | Trust established in Canada | ❌ |
Registrants whose legal type is `TDM` or `OMK` are exempt from the Canadian local-presence requirement: a Canadian-registered trade-mark or official mark satisfies the Canadian Presence Requirement on its own, so the registrant need not be located in Canada.
### Organization requirement for non-individual categories
A contact using a non-individual category must have its `org` field set. If it is missing, the request is rejected:
```json
{
"detail": "Organization is required for non-individual CIRA CPR category 'GOV'",
"pointer": "contact.org"
}
```
# 🇨🇨 .cc — Cocos (Keeling) Islands
> The **.cc** is a country-code top-level domain (ccTLD) operated by eNIC Cocos (Keeling) Islands Pty.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | eNIC Cocos (Keeling) Islands Pty. |
| Registry Country | Australia |
| Registry Website | [nic.cc](https://nic.cc/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `ccwhois.verisign-grs.com` |
| RDAP Server | [tld-rdap.verisign.com/cc/v1](https://tld-rdap.verisign.com/cc/v1/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇧🇭 .cc.bh — Bahrain
> The **.cc.bh** is a country-code top-level domain (ccTLD) operated by Telecommunications Regulatory Authority (TRA). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Telecommunications Regulatory Authority (TRA) |
| Registry Country | Bahrain |
| Registry Website | [domains.bh](https://domains.bh/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–5 years |
| Renewal Period | 1–5 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.bhregistry.bh` |
| RDAP Server | [rdap.bhregistry.bh/rdap](https://rdap.bhregistry.bh/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇨🇭 .ch — Switzerland
> The **.ch** is a country-code top-level domain (ccTLD) operated by Switch. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Switch |
| Registry Country | Switzerland |
| Registry Website | [www.switch.ch/de](https://www.switch.ch/de) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 0 days |
| Redemption Period | 40 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (6–60 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ❌ No |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.ch` |
| RDAP Server | [rdap.nic.ch](https://rdap.nic.ch) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | Dispute Resolution Proceedings |
| Reference | [www.nic.ch/terms/disputes/proceedings](https://www.nic.ch/terms/disputes/proceedings/) |
| UDRP Support | ❌ No |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇨🇴 .co — Colombia
> The **.co** is a country-code top-level domain (ccTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [registry.co](https://registry.co) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–5 years |
| Renewal Period | 1–5 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ❌ No |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.co` |
| RDAP Server | [rdap.registry.co](https://rdap.registry.co/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇳🇱 .co.nl — Netherlands
> The **.co.nl** is a country-code top-level domain (ccTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇳🇴 .co.no — Norway
> The **.co.no** is a country-code top-level domain (ccTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇧🇭 .com.bh — Bahrain
> The **.com.bh** is a country-code top-level domain (ccTLD) operated by Telecommunications Regulatory Authority (TRA). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Telecommunications Regulatory Authority (TRA) |
| Registry Country | Bahrain |
| Registry Website | [domains.bh](https://domains.bh/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–5 years |
| Renewal Period | 1–5 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.bhregistry.bh` |
| RDAP Server | [rdap.bhregistry.bh/rdap](https://rdap.bhregistry.bh/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇩🇪 .com.de — Germany
> The **.com.de** is a country-code top-level domain (ccTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇸🇪 .com.se — Sweden
> The **.com.se** is a country-code top-level domain (ccTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇨🇿 .cz — Czechia
> The **.cz** is a country-code top-level domain (ccTLD) operated by CZ.NIC, z. s. p. o.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | CZ.NIC, z. s. p. o. |
| Registry Country | Czechia |
| Registry Website | [www.nic.cz](https://www.nic.cz) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ❌ No |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 30 days |
| Redemption Period | 31 days |
| Pending Restore | 0 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 2–10 |
| Host Objects Allowed | ❌ No |
| Registry Nameserver Check | ✅ Yes |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DNSKEY |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ❌ No |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ❌ No |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.cz` |
| RDAP Server | [rdap.nic.cz](https://rdap.nic.cz/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇩🇪 .de — Germany
> The **.de** is a country-code top-level domain (ccTLD) operated by DENIC eG. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | DENIC eG |
| Registry Country | Germany |
| Registry Website | [www.denic.de](https://www.denic.de/) |
| Provisioning Protocol | RRI |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1 year |
| Renewal Period | 1 year |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 0 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–16 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ❌ No |
| Registry Nameserver Check | ✅ Yes |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DNSKEY |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ❌ No |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.denic.de` |
| RDAP Server | [rdap.denic.de](https://rdap.denic.de) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | Domain Dispute |
| Reference | [www.denic.de/en/service/dispute](https://www.denic.de/en/service/dispute) |
| UDRP Support | ❌ No |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇩🇰 .dk — Denmark
> The **.dk** is a country-code top-level domain (ccTLD) operated by Punktum dk A/S. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Punktum dk A/S |
| Registry Country | Denmark |
| Registry Website | [punktum.dk](https://punktum.dk) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1 year |
| Renewal Period | 1 year |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 0 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 2–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–64 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 2–7 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ✅ Yes |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ❌ No |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.punktum.dk` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Registration model
A `.dk` registration is an **application**, not an immediate allocation. [`POST /v1/domains`](/api-reference#tag/domain/POST/v1/domains) is accepted and the request enters a registry queue that clears in anything from a few seconds to a few days. The domain does not exist at the registry until it does, and a lookup before then reports the name as unavailable with the reason `Enqueued`.
Once the queue clears, a second gate applies: the domain is **activated only after the registrant's data and ID control has completed**. Both gates are reported through registry notifications, described below.
Registrations and renewals are **one year**, and no other period is accepted.
## Contact handles
`.dk` is a thick registry that recognises a **registrant only**. Administrative, technical and billing contacts are not supported and are rejected if supplied.
Handles are minted by the registry; one supplied on a create is ignored. Contacts can be neither deleted nor transferred at the registry, and a contact that is no longer referenced is removed automatically once it has been unused for 14 days.
The registry does not implement `contact:disclose`, and there is no privacy or proxy service.
## Contact Attributes
| Attribute | Type | Required | Applies to |
| --- | --- | --- | --- |
| `PUNKTUM_DK_USER_TYPE` | Enum | ✅ Yes | Registrant |
| `PUNKTUM_DK_CVR` | String | Conditional | Legal entities |
| `PUNKTUM_DK_PNUMBER` | String | ➖ Optional | Legal entities |
| `PUNKTUM_DK_EAN` | String | ➖ Optional | Danish legal entities |
| `PUNKTUM_DK_SECONDARY_EMAIL` | String | ➖ Optional | Any |
| `PUNKTUM_DK_MOBILEPHONE` | String | ➖ Optional | Any |
| `PUNKTUM_DK_SOLE_PROPRIETORSHIP` | Boolean | ➖ Optional | Foreign contacts |
`PUNKTUM_DK_USER_TYPE` is one of `company`, `public_organization`, `association` or `individual`, and it determines how the remaining attributes are interpreted.
`PUNKTUM_DK_CVR` carries the Danish CVR number or a European VAT number. It is **mandatory for a Danish company, public organization or association**, optional elsewhere in the EU and EEA, and **not supported for an `individual`** — supplying it on an individual contact is rejected.
`PUNKTUM_DK_EAN`, when supplied, must correspond to the CVR number on the same contact.
`PUNKTUM_DK_SOLE_PROPRIETORSHIP` applies only to contacts outside Denmark. Danish contacts are classified from the CVR register and the attribute is rejected on them.
## Registry-maintained contact data
Once a contact is matched to an authoritative register, the registry takes ownership of its name and address and keeps them in step with that register:
- Danish individuals are bound to the Central Person Register (CPR).
- Danish companies, public organizations and associations are bound to the Central Business Register (CVR).
- Companies elsewhere in the EU are bound through their VAT number and the VIES service.
For those contacts, name and address are maintained by the registry and changes submitted through the API do not take effect. Contacts outside those categories are maintained normally.
## Data and ID control
Danish law requires the registry to hold verified contact information for every `.dk` registrant. The control is run by **Punktum dk**, not by the registrar, and it is free of charge.
### How it runs
1. The domain is registered and remains **inactive**.
2. Punktum dk emails the registrant with a request for data and ID control.
3. The registrant completes the control on Punktum dk's self-service portal.
4. The domain is activated.
**Registrants residing in Denmark** identify themselves with **MitID**, the Danish national electronic identity, and confirm their CPR or CVR number on Punktum dk's portal. The number is matched against the register and then discarded. There is no way to complete this step on the registrant's behalf: the CPR number is never transmitted over the registry's interface and never reaches the registrar.
**Registrants residing outside Denmark** are assessed on a risk basis. Many are activated without any ID control at all. Those the registry does flag are asked to supply documentation proving their identity and address.
In both cases the registrant may additionally be asked to confirm their email address by replying to a verification message.
### Deadlines
**Every request states its own deadline**, and that date is the one to work from. The registry's terms set the response window at **25 days**, shortened to 10 in exceptional circumstances, but the deadline attached to a given request is what governs it.
A control request that expires or is rejected suspends the registrant's domains, and the registrant is recorded as unknown. The suspension applies to **every domain held by that registrant**, not only the one that triggered the control. If the control is still incomplete **30 days** later, those domains are deleted.
Email confirmation requests are far shorter lived than identity checks, often expiring within a day or two of being issued.
### Changing a verified email address
An email address that has been verified must be verified again after it is changed, and the change only takes effect once that happens. This applies to both the primary and the secondary address.
## Registrant change
A change of registrant is submitted through [`PATCH /v1/domains/{domain_reference}`](/api-reference#tag/domain/PATCH/v1/domains/{domain_reference}), alongside any other change, exactly as on any other TLD. The registry itself refuses to combine a registrant change with anything else, but that is handled for you: the update is split into the necessary registry commands, with the registrant applied last.
Because nothing at the registry spans those commands, a failure partway through can leave the earlier changes applied. The response states which part landed, and the domain is resynchronised from the registry.
A registrant change requires the incoming registrant to have accepted Punktum dk's terms, declared through the `punktum_dk_terms_acceptance` confirmation. It is checked before any registry traffic, so a missing acceptance fails the request up front.
The change also triggers a new data and ID control for the incoming registrant. Until that control completes, the domain sits in a pending state and further updates are refused.
## Transfers
A `.dk` transfer is **immediate**. The registry settles it on receipt rather than opening a transfer window, so there is no pending phase, no acknowledgement or rejection by the losing registrar, and no transfer notification to wait for.
- The transfer request carries **no period** and the domain is **not renewed** by the transfer. The expiry date is unchanged.
- The auth code is **time limited** and can only be issued by the registrar currently sponsoring the domain.
- The registrant contact is **cloned by the registry** as part of the transfer, so the domain ends up with a new registrant handle.
- A domain carrying the registry's VID service cannot be transferred to registrar management at all.
For a Danish registrant, and for a flagged foreign registrant, the data and ID control has to be complete **before** the transfer settles.
## Renewal
Renewals are explicit and always **one year**. Three registry rules apply:
- A renewal is only accepted within **two months of the expiry date**.
- The total registration term may not exceed **14 months** after the renewal.
- The renewal is charged to the billing contact registered with Punktum dk, so the registrar account must hold that privilege.
## Deletion and restore
A deleted `.dk` domain enters a **30 day redemption period** during which it can be restored with [`POST /v1/domains/{domain_reference}/restore`](/api-reference#tag/domain/POST/v1/domains/{domain_reference}/restore).
The registry does not implement the two-step RGP restore. There is no restore request phase and no report to file afterwards: a single restore call completes the operation.
> ⚠️ A redemption period **caused by a failed data or ID control cannot be restored**. When the domain entered redemption because the registrant's ID control expired or was rejected, rather than because the domain was deleted or allowed to expire, the restore is refused. Completing the outstanding control is the only way back, and it has to happen before the redemption period ends.
The notification that opens the redemption period carries the **exact date** on which the domain will be deleted.
## Name servers
- A domain carries **at least two and at most seven** name servers.
- A name server must already exist at the registry before it can be attached to a domain.
- The registry **queries the name servers** as part of the change and rejects the request if the zone does not answer for the domain.
> ⚠️ Changing the name servers on a signed domain **removes all of its DS records**. Re-publish the DNSSEC data after the change.
## Domain statuses
`.dk` supports **no client-managed statuses**. Transfer locks, update locks and holds are applied by the registry alone and cannot be set or cleared through the API. Clearing a registry-applied status is arranged with Punktum dk directly.
## Registry notifications
Punktum dk reports what it does to a domain and to its contacts through notifications, and the changes are reconciled onto the domain automatically. The notifications cover:
| Notification | What it means |
| --- | --- |
| Registered and activated | The application succeeded and the domain resolves |
| Registered, but not activated | The domain exists and is waiting on the registrant's data or ID control |
| Application cancelled or rejected | The application did not result in a registration |
| Data or ID control required | The registrant has been asked to complete a control |
| Data or ID control completed, expired or cancelled | The outcome of a control that was requested earlier |
| Email confirmation required or confirmed | A primary or secondary address needs verification, or has been verified |
| Registrant changed, or not completed in time | The outcome of a change of registrant |
| Name servers or DS records changed | The delegation was altered |
| Added to or removed from the portfolio | The domain was transferred in or out |
| Deleted, or deletion stopped | The domain was deleted, or a pending deletion was cancelled |
# 🇧🇭 .edu.bh — Bahrain
> The **.edu.bh** is a country-code top-level domain (ccTLD) operated by Telecommunications Regulatory Authority (TRA). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Telecommunications Regulatory Authority (TRA) |
| Registry Country | Bahrain |
| Registry Website | [domains.bh](https://domains.bh/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–5 years |
| Renewal Period | 1–5 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.bhregistry.bh` |
| RDAP Server | [rdap.bhregistry.bh/rdap](https://rdap.bhregistry.bh/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇪🇺 .eu — European Union
> The **.eu** is a country-code top-level domain (ccTLD) operated by EURid vzw/asbl. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | EURid vzw/asbl |
| Registry Country | Belgium |
| Registry Website | [eurid.eu](http://eurid.eu/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1 year |
| Renewal Period | 1 year |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 0 days |
| Redemption Period | 40 days |
| Pending Restore | 0 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 2–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–9 |
| Host Objects Allowed | ❌ No |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DNSKEY |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ❌ No |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.eurid.eu` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | ADR |
| Reference | [eu.adr.eu](http://eu.adr.eu/) |
| UDRP Support | ❌ No |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇫🇲 .fm — Federated States of Micronesia
> The **.fm** is a country-code top-level domain (ccTLD) operated by FSM Telecommunications Corporation. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | FSM Telecommunications Corporation |
| Registry Country | Federated States of Micronesia |
| Registry Website | [www.dot.fm](https://www.dot.fm/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.fm` |
| RDAP Server | [rdap.centralnic.com/fm](https://rdap.centralnic.com/fm/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇫🇴 .fo — Faroe Islands
> The **.fo** is a country-code top-level domain (ccTLD) operated by FO Council. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | FO Council |
| Registry Country | Faroe Islands |
| Registry Website | [www.nic.fo](https://www.nic.fo/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.fo` |
| RDAP Server | [rdap.centralnic.com/fo](https://rdap.centralnic.com/fo/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇫🇷 .fr — France
> The **.fr** is a country-code top-level domain (ccTLD) operated by AFNIC (Association Française pour le Nommage Internet en Coopération). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | AFNIC (Association Française pour le Nommage Internet en Coopération) |
| Registry Country | France |
| Registry Website | [www.afnic.fr](https://www.afnic.fr) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 0 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–8 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 8 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.fr` |
| RDAP Server | [rdap.nic.fr](https://rdap.nic.fr) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Contact Attributes
AFNIC models every contact as either a **natural person** (`PP` — *personne physique*) or a
**legal entity** (`PM` — *personne morale*), and that choice decides which of the remaining
attributes apply.
Two things set the AFNIC TLDs apart from most ccTLDs:
- the attributes are required on **every** contact role — registrant, administrative, and
technical — not on the registrant alone;
- the roles do not have to agree. A `PP` registrant with a `PM` technical contact is a normal
`.fr` registration.
| Attribute | Type | Required | Applies to | Allowed values |
| --- | --- | --- | --- | --- |
| `AFNIC_CONTACT_TYPE` | Enum | ✅ Required | Every role | `PP` (natural person) or `PM` (legal entity) |
### Natural person (`PP`)
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PP_FIRST_NAME` | String | ✅ Required | The contact's first name. It is sent to AFNIC in addition to the standard `name` field, which carries the full name |
| `AFNIC_ID_STATUS` | Enum | ➖ Optional | `ok`, `no`, `pending`, `problem`, `ko`, `deprecated`, `control`, `delayed` |
| `AFNIC_REACHABLE_MEDIA` | Enum | ➖ Optional | `email` or `voice` — the channel through which the registrant was reached |
| `AFNIC_REACHABLE_STATUS` | Boolean | ➖ Optional | Whether that channel was confirmed |
`AFNIC_REACHABLE_STATUS` is only sent to the registry when `AFNIC_REACHABLE_MEDIA` is set
alongside it — a status on its own is dropped, because AFNIC carries the confirmation as an
attribute of the channel.
### Legal entity (`PM`)
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PM_LEGAL_STATUS` | Enum | ✅ Required | `company`, `association`, or `other` |
| `AFNIC_PM_SIREN` | String | ➖ Optional | SIREN or SIRET number from the French business register |
| `AFNIC_PM_VAT` | String | ➖ Optional | European VAT number |
| `AFNIC_PM_TRADEMARK` | String | ➖ Optional | Trademark registration number |
| `AFNIC_PM_DUNS` | Integer | ➖ Optional | D-U-N-S number |
| `AFNIC_PM_LOCAL` | String | ➖ Optional | Identifier from another official register, for an entity that has none of the above |
| `AFNIC_ID_STATUS` | Enum | ➖ Optional | Same values as for a natural person |
The five identifiers apply to the `company` and `other` legal statuses. An entity may supply
several; AFNIC accepts them together.
#### Associations
An `association` identifies itself through its WALDEC number, or through its publication in the
*Journal Officiel* — one of the two is mandatory, and a create that carries neither is rejected
before it reaches the registry.
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PM_ASSOC_WALDEC` | String | ➖ Conditional | WALDEC number of the association |
| `AFNIC_PM_ASSOC_PUBL_DATE` | Datetime | ➖ Conditional | Date of publication in the *Journal Officiel* |
| `AFNIC_PM_ASSOC_PUBL_PAGE` | Integer | ➖ Conditional | Page of that publication |
| `AFNIC_PM_ASSOC_PUBL_ANNOUNCE` | Integer | ➖ Optional | Announcement number within the publication |
| `AFNIC_PM_ASSOC_DECL` | Datetime | ➖ Optional | Date the association was declared |
Supply **either** `AFNIC_PM_ASSOC_WALDEC`, **or** `AFNIC_PM_ASSOC_PUBL_DATE` together with
`AFNIC_PM_ASSOC_PUBL_PAGE`. When a WALDEC number is present it is what gets sent, and the
publication attributes are ignored. `AFNIC_PM_ASSOC_DECL` and `AFNIC_PM_ASSOC_PUBL_ANNOUNCE`
only add detail to the publication route; neither satisfies the requirement on its own.
```json
{
"type": "policy-validation-error",
"title": "Policy Validation Error",
"status": 422,
"code": "ERROR_POLICY_VALIDATION",
"detail": "PM association requires AFNIC_PM_ASSOC_WALDEC or (AFNIC_PM_ASSOC_PUBL_DATE + AFNIC_PM_ASSOC_PUBL_PAGE)"
}
```
### Registry-managed attributes
| Attribute | Type | Allowed values |
| --- | --- | --- |
| `AFNIC_RESTRICTED_PUBLICATION` | Boolean | Whether AFNIC restricts publication of the contact's details |
`AFNIC_RESTRICTED_PUBLICATION` is read back from AFNIC when a contact is imported or read; it is
not sent on a contact create, so setting it on an attribute set has no effect.
### Example attribute sets
A natural person:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "FR registrant - individual",
"tld": "fr",
"attributes": {
"AFNIC_CONTACT_TYPE": "PP",
"AFNIC_PP_FIRST_NAME": "Pierre"
}
}'
```
An association identified by its *Journal Officiel* publication:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "FR registrant - association",
"tld": "fr",
"attributes": {
"AFNIC_CONTACT_TYPE": "PM",
"AFNIC_PM_LEGAL_STATUS": "association",
"AFNIC_PM_ASSOC_PUBL_DATE": "2015-03-14T00:00:00Z",
"AFNIC_PM_ASSOC_PUBL_PAGE": 118
}
}'
```
> ⚠️ **Reusing one contact for every role?** `AFNIC_CONTACT_TYPE` is required on the
> administrative and technical contacts too, not only the registrant. A create that carries it
> on the registrant alone is rejected before it reaches the registry:
>
> ```json
> {
> "type": "policy-validation-error",
> "title": "Policy Validation Error",
> "status": 422,
> "code": "ERROR_POLICY_VALIDATION",
> "errors": [
> {
> "detail": "Attribute 'AFNIC_CONTACT_TYPE' is required for admin contacts",
> "pointer": "contacts.admin[0].attributes.AFNIC_CONTACT_TYPE"
> }
> ],
> "detail": "Policy validation failed"
> }
> ```
These constraints are machine-readable: each `possible_attributes` entry returned by
[`GET /v1/tlds/fr`](/api-reference#tag/tld/GET/v1/tlds/{tld}) carries its own `type`,
`values`, `required`, `contact_roles`, and `conditions` fields. Build forms from the
specification rather than hard-coding the `PP`/`PM` split.
## Contact handles
AFNIC assigns contact handles itself — a handle cannot be chosen when creating a contact, and an
existing AFNIC handle cannot be adopted through the API.
## Transfers and registrant changes
The registrant is **not** part of a `.fr` transfer request: an inbound transfer keeps the
registrant the domain already has at the registry. The administrative and technical contacts are
supplied with the transfer as usual.
To move a domain to a different holder, transfer it first and then change the registrant with a
domain update — `.fr` supports a registrant change through
[`PATCH /v1/domains/{domain_reference}`](/api-reference#tag/domain/PATCH/v1/domains/{domain_reference}).
# 🇬🇩 .gd — Grenada
> The **.gd** is a country-code top-level domain (ccTLD) operated by The National Telecommunications Regulatory Commission (NTRC). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | The National Telecommunications Regulatory Commission (NTRC) |
| Registry Country | Grenada |
| Registry Website | [nic.gd](https://nic.gd/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.gd` |
| RDAP Server | [rdap.centralnic.com/gd](https://rdap.centralnic.com/gd/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇬🇬 .gg — Guernsey
> The **.gg** is a country-code top-level domain (ccTLD) operated by Island Networks Ltd.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Island Networks Ltd. |
| Registry Country | Guernsey |
| Registry Website | [www.channelisles.net](https://www.channelisles.net) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 31 days |
| Redemption Period | 12 days |
| Pending Restore | 0 days |
| Pending Delete | 12 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ✅ Yes |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (6–16 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 1–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.gg` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | CI-DRS |
| Reference | [www.channelisles.net/legal/dispute-resolution](https://www.channelisles.net/legal/dispute-resolution) |
| UDRP Support | ❌ No |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇬🇱 .gl — Greenland
> The **.gl** is a country-code top-level domain (ccTLD) operated by TELE Greenland A/S. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | TELE Greenland A/S |
| Registry Country | Greenland |
| Registry Website | [www.nic.gl](https://www.nic.gl/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.gl` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇧🇭 .info.bh — Bahrain
> The **.info.bh** is a country-code top-level domain (ccTLD) operated by Telecommunications Regulatory Authority (TRA). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Telecommunications Regulatory Authority (TRA) |
| Registry Country | Bahrain |
| Registry Website | [domains.bh](https://domains.bh/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–5 years |
| Renewal Period | 1–5 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.bhregistry.bh` |
| RDAP Server | [rdap.bhregistry.bh/rdap](https://rdap.bhregistry.bh/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇮🇴 .io — British Indian Ocean Territory
> The **.io** is a country-code top-level domain (ccTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [nic.io](https://nic.io) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact, Administrator |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [nic.io/dispute_policy.htm](https://nic.io/dispute_policy.htm) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇮🇹 .it — Italy
> The **.it** is a country-code top-level domain (ccTLD) operated by Istituto di Informatica e Telematica (IIT-CNR). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Istituto di Informatica e Telematica (IIT-CNR) |
| Registry Country | Italy |
| Registry Website | [www.nic.it](https://www.nic.it) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1 year |
| Renewal Period | 1 year |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 15 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (6–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 2–6 |
| Host Objects Allowed | ❌ No |
| Registry Nameserver Check | ✅ Yes |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ❌ No |
| Transfer Duration | 1 day |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.it` |
| RDAP Server | [rdap.pubtest.nic.it](https://rdap.pubtest.nic.it/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Contact Attributes
`.it` carries two registry-specific attributes on the **registrant** contact, beyond the standard EPP fields. Both are required on registrations and inbound transfers:
| Attribute | Type | Required | Applies to | Allowed values |
| --- | --- | --- | --- | --- |
| `NIC_IT_ENTITY_TYPE` | Enum | ✅ Required | Registrant | See the entity-type table below |
| `NIC_IT_REG_CODE` | String | ✅ Required | Registrant | Tax or registration code, 1-36 chars (format depends on the entity type) |
### Entity types (`NIC_IT_ENTITY_TYPE`)
The registrant declares its legal nature through `NIC_IT_ENTITY_TYPE`. That value drives the nationality, organization, and registration-code rules below. The registry code is the number NIC.it echoes back in policy errors (e.g. "entity type = 1").
| Value | Legal nature | Registry code | Natural person |
| --- | --- | --- | --- |
| `natural_person` | Natural person | 1 | ✅ |
| `company` | Company / one-person company | 2 | ❌ |
| `individual_firm` | Freelancer / sole proprietor | 3 | ❌ |
| `non_profit` | Non-profit organization | 4 | ❌ |
| `public_org` | Public organization | 5 | ❌ |
| `other` | Other entity | 6 | ❌ |
| `foreign_legal_entity` | Foreign (non-Italian) legal entity | 7 | ❌ |
### Registration code (`NIC_IT_REG_CODE`)
The expected format depends on the entity type and nationality:
| Entity type | Expected code |
| --- | --- |
| `natural_person` (Italian) | 16-character Codice Fiscale |
| `natural_person` (non-Italian) | Home-country identifier (no format check) |
| `company`, `public_org`, `other` | 11-digit Partita IVA |
| `individual_firm` | Codice Fiscale or Partita IVA |
| `non_profit` | Partita IVA, or the literal `N.A.` when none exists |
| `foreign_legal_entity` | Home-country identifier (no format check) |
### Nationality, province, and organization
The registrant's standard fields are constrained by the entity type:
- **Country** (`contact.country`):
- Italian legal types (`company`, `individual_firm`, `non_profit`, `public_org`, `other`) must be `IT`
- `foreign_legal_entity` must be a non-`IT` country in the EEA plus Vatican, San Marino, Switzerland, and the UK
- `natural_person` may be any country in that same EEA-plus set, including `IT`
- **Province** (`contact.state`): required and must be a valid 2-letter Italian province code (e.g. `RM`, `MI`, `NA`) whenever the country is `IT`
- **Organization** (`contact.org`):
- required for every legal-entity type
- for `natural_person` it must be omitted or equal the contact's full name
### Per-role rules
`.it` is a thick registry with a registrant, admin, and tech contact. A few cross-role rules are enforced before the request reaches the registry:
- the **tech** contact is required, on both create and update
- for a `natural_person` registrant, the **admin** contact must reference the same contact as the registrant
- the registrant is immutable through a normal update: omit it and the existing registrant is kept; it cannot be replaced via `update`
> ⚠️ **Reusing one contact for every role?** For a `natural_person` registrant the admin has to be that same contact, and any contacts update must still carry a tech. The two failures integrators hit most:
>
> ```json
> {
> "type": "policy-validation-error",
> "title": "Policy Validation Error",
> "status": 422,
> "code": "ERROR_POLICY_VALIDATION",
> "errors": [
> {
> "detail": "For 'natural_person' registrant, the admin contact must reference the same contact as the registrant",
> "pointer": "contacts.admin[0].contact_id"
> }
> ],
> "detail": "Policy validation failed"
> }
> ```
>
> ```json
> {
> "type": "policy-validation-error",
> "title": "Policy Validation Error",
> "status": 422,
> "code": "ERROR_POLICY_VALIDATION",
> "errors": [
> {
> "detail": "Tech contact is required",
> "pointer": "contacts.tech"
> }
> ],
> "detail": "Policy validation failed"
> }
> ```
The attribute constraints are machine-readable: each `possible_attributes` entry returned by [`GET /v1/tlds/it`](/api-reference#tag/tld/GET/v1/tlds/{tld}) carries its own `values`, `required`, and `contact_roles` fields.
## Registrant Policy Acknowledgement
`.it` registrations and inbound transfers require the registrar to confirm — on the registrant's behalf — compliance with the Registro .it (IIT-CNR) policies, and to pass those policies on to the domain owner. Surface the acknowledgement below to the end user **before** submitting a `.it` create or transfer; the confirmation is mandatory for both operations.
| Policy | Reference |
| --- | --- |
| Terms of Service | [Terms of Service (PDF)](https://cdn.prod.website-files.com/66f35e9c0faa52510e6c6d4c/68ac34bfb6a7a14ab952248d_TermsOfService_en.pdf) |
| Dispute Resolution Policy (.it) | [nic.it — Legal / Dispute Resolution](https://www.nic.it/en/manage-your-it/legal) |
| Privacy Policy | [nic.it — Privacy Policy](https://www.nic.it/en/privacy-policy) |
### Confirmation text
Present a single **required** checkbox. The registrant must accept it for the create or transfer to proceed. Suggested copy in English and German:
**English**
> Please confirm that you comply with the following policies and that you will pass them on to the domain owner accordingly.
>
> - [Terms of Service](https://cdn.prod.website-files.com/66f35e9c0faa52510e6c6d4c/68ac34bfb6a7a14ab952248d_TermsOfService_en.pdf)
> - [Dispute Resolution Policy .it](https://www.nic.it/en/manage-your-it/legal)
> - [Privacy Policy](https://www.nic.it/en/privacy-policy)
>
> ☐ I hereby confirm my compliance with the policies listed above.
**Deutsch**
> Bitte bestätigen Sie die Einhaltung der folgenden Policies bzw. dass Sie diese entsprechend an den Inhaber der Domain weitergeben.
>
> - [Servicebedingungen](https://cdn.prod.website-files.com/66f35e9c0faa52510e6c6d4c/68ac34bfb6a7a14ab952248d_TermsOfService_en.pdf)
> - [Dispute Resolution .it](https://www.nic.it/en/manage-your-it/legal)
> - [Datenschutzerklärung](https://www.nic.it/en/privacy-policy)
>
> ☐ Hiermit bestätige ich die Einhaltung der genannten Policies.
> ℹ️ The acknowledgement is required for **both** `.it` registrations and inbound transfers. Capture the confirmation at the point of sale for each operation — a prior registration does not carry the acknowledgement over to a later transfer.
# 🇯🇪 .je — Jersey
> The **.je** is a country-code top-level domain (ccTLD) operated by Island Networks (Jersey) Ltd.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Island Networks (Jersey) Ltd. |
| Registry Country | Jersey |
| Registry Website | [www.channelisles.net](https://www.channelisles.net) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 31 days |
| Redemption Period | 12 days |
| Pending Restore | 0 days |
| Pending Delete | 12 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ✅ Yes |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (6–16 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 1–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.je` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | CI-DRS |
| Reference | [www.channelisles.net/legal/dispute-resolution](https://www.channelisles.net/legal/dispute-resolution) |
| UDRP Support | ❌ No |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇱🇨 .lc — Saint Lucia
> The **.lc** is a country-code top-level domain (ccTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [nic.lc](https://nic.lc) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact, Administrator |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.nic.lc/legal-issues.htm](https://www.nic.lc/legal-issues.htm) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇱🇮 .li — Liechtenstein
> The **.li** is a country-code top-level domain (ccTLD) operated by Switch. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Switch |
| Registry Country | Switzerland |
| Registry Website | [www.switch.ch/de](https://www.switch.ch/de) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 0 days |
| Redemption Period | 40 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (6–60 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ❌ No |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.li` |
| RDAP Server | [rdap.nic.li](https://rdap.nic.li) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | Dispute Resolution Proceedings |
| Reference | [www.nic.ch/terms/disputes/proceedings](https://www.nic.ch/terms/disputes/proceedings/) |
| UDRP Support | ❌ No |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇱🇹 .lt — Lithuania
> The **.lt** is a country-code top-level domain (ccTLD) operated by DOMREG (Kaunas University of Technology). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | DOMREG (Kaunas University of Technology) |
| Registry Country | Lithuania |
| Registry Website | [www.domreg.lt](https://www.domreg.lt) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–5 years |
| Renewal Period | 1–5 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 0 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 2–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (1–255 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 2–13 |
| Host Objects Allowed | ❌ No |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.domreg.lt` |
| RDAP Server | [rdap.domreg.lt](https://rdap.domreg.lt) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Contact Attributes
`.lt` contacts support one registry-specific attribute beyond the standard EPP fields:
| Attribute | Type | Required | Applies to | Allowed values |
| --- | --- | --- | --- | --- |
| `DOMREG_LT_ORG_CODE` | String | ➖ Optional | Legal-entity contacts | Company code from the relevant business register |
## Auth Codes
`.lt` transfer auth codes are generated by the registry and cannot be chosen or changed through a domain update.
Request one with [`POST /v1/domains/tld-specific/lt/{domain_reference}/auth_code/request`](/api-reference#tag/domain/POST/v1/domains/tld-specific/lt/{domain_reference}/auth_code/request); it stays valid for **7 days** and is consumed by the transfer that uses it.
Generating the code is what opens the transfer window on the registry side.
A transfer attempted after the code expired (or without one ever being generated) is rejected by the registry as "not allowed or expired".
## Transfers
`.lt` transfers complete **immediately**: there is no pending phase and nothing for the losing registrar to approve. One of their rules deserve attention:
### The holder never changes on a TRANSFER
The registrant contact supplied with the transfer MUST represent the *current* holder:
the registry matches it by organization name (legal entities) or personal name (natural persons) and rejects the transfer when they differ.
Only the name is matched; the company code is not part of the comparison. To move a domain to a *different* holder, the current holder must initiate a **TRADE** in DOMREG's registrant portal - this is not yet available through the API.
## Deletion
Deleted `.lt` domains are placed in **quarantine** rather than released immediately, and can only be restored for the same registrant while quarantined.
# 🇱🇺 .lu — Luxembourg
> The **.lu** is a country-code top-level domain (ccTLD) operated by Fondation RESTENA (DNS-LU). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Fondation RESTENA (DNS-LU) |
| Registry Country | Luxembourg |
| Registry Website | [www.dns.lu](https://www.dns.lu) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1 year |
| Renewal Period | 1 year |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 0 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ❌ No |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 2–10 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ✅ Yes |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 0 days after transfer) |
| Transfer Duration | 12 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ❌ No |
| Confirmation Required | ✅ Yes (Registrant) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.dns.lu` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇱🇻 .lv — Latvia
> The **.lv** is a country-code top-level domain (ccTLD) operated by Network Information Centre (NIC), Institute of Mathematics and Computer Science, University of Latvia. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Network Information Centre (NIC), Institute of Mathematics and Computer Science, University of Latvia |
| Registry Country | Latvia |
| Registry Website | [www.nic.lv](https://www.nic.lv) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1 year |
| Renewal Period | 1 year |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ❌ No |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 30 days |
| Redemption Period | 0 days |
| Pending Restore | 0 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 2–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator |
| Supported Roles | Domain Owner, Administrator |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 2–5 |
| Host Objects Allowed | ❌ No |
| Registry Nameserver Check | ✅ Yes |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.lv` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Contact Attributes
`.lv` registrations carry two registry-specific contact attributes beyond the standard EPP fields. They identify the **registrant** (holder) of the domain:
| Attribute | Type | Required | Applies to | Allowed values |
| --- | --- | --- | --- | --- |
| `NIC_LV_REG_NR` | String | ➖ Conditional | Registrant | Registration number, 3-20 characters (letters, digits and `#:./-`) |
| `NIC_LV_VAT_NR` | String | ➖ Conditional | Registrant | VAT number, 3-20 characters (letters, digits and `#:./-`) |
- `NIC_LV_REG_NR` holds a **registration number**: a personal code for a natural person, or a company registration number for a legal entity.
- `NIC_LV_VAT_NR` holds a **VAT number**.
Which attribute is required depends on the registrant:
| Registrant | Required attribute |
| --- | --- |
| Latvian (natural person or legal entity) | `NIC_LV_REG_NR` |
| Foreign EU legal entity | `NIC_LV_VAT_NR` |
| Foreign non-EU | none |
These constraints are machine-readable: each `possible_attributes` entry returned by [`GET /v1/tlds/lv`](/api-reference#tag/tld/GET/v1/tlds/{tld}) carries its own `type`, `required`, and `contact_roles` fields.
## Contact roles
A `.lv` domain is managed with a registrant and an administrative contact. Two role rules apply:
- the **administrative contact must be a natural person** (no `org`);
- when the **registrant is a natural person**, the administrative contact must reference the **same contact** as the registrant.
> ⚠️ **Reusing one contact for every role?** When the registrant is a natural person, the admin has to be that same contact:
>
> ```json
> {
> "type": "policy-validation-error",
> "title": "Policy Validation Error",
> "status": 422,
> "code": "ERROR_POLICY_VALIDATION",
> "errors": [
> {
> "detail": "When the .lv holder is a natural person, the administrative contact must be the same contact as the registrant",
> "pointer": "contacts.admin"
> }
> ],
> "detail": "Policy validation failed"
> }
> ```
## Transfers
On an inbound transfer the registrant and administrative contact are preserved as they already are on the domain — they cannot be set in the transfer request:
- the **registrant** cannot be changed through a transfer or a domain update;
- the **administrative contact** is kept during the transfer. When the registrant is an organization, the admin is a separate individual and can be changed with a domain update afterwards. When the registrant is a natural person, the admin is the same contact as the registrant, so it changes only when the registrant changes.
The billing and technical contacts are managed automatically and are set when the transfer completes; they are not part of the transfer request.
# 🇲🇪 .me — Montenegro
> The **.me** is a country-code top-level domain (ccTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [domain.me](https://domain.me) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact, Administrator |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [domain.me/policies/#dispute-policy](https://domain.me/policies/#dispute-policy) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇧🇭 .me.bh — Bahrain
> The **.me.bh** is a country-code top-level domain (ccTLD) operated by Telecommunications Regulatory Authority (TRA). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Telecommunications Regulatory Authority (TRA) |
| Registry Country | Bahrain |
| Registry Website | [domains.bh](https://domains.bh/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–5 years |
| Renewal Period | 1–5 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.bhregistry.bh` |
| RDAP Server | [rdap.bhregistry.bh/rdap](https://rdap.bhregistry.bh/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇲🇳 .mn — Mongolia
> The **.mn** is a country-code top-level domain (ccTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [domain.mn](https://domain.mn) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact, Administrator |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [domain.mn/mnpolicy.php](https://domain.mn/mnpolicy.php) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇲🇽 .mx — Mexico
> The **.mx** is a country-code top-level domain (ccTLD) operated by Registry .MX. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Registry .MX |
| Registry Country | Mexico |
| Registry Website | [www.registry.mx](https://www.registry.mx) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–5 years |
| Renewal Period | 1–5 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ❌ No |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 0 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ❌ No |
| Reserved Domains | ✅ Yes |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (6–20 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–10 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ✅ Yes |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.mx` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇧🇭 .name.bh — Bahrain
> The **.name.bh** is a country-code top-level domain (ccTLD) operated by Telecommunications Regulatory Authority (TRA). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Telecommunications Regulatory Authority (TRA) |
| Registry Country | Bahrain |
| Registry Website | [domains.bh](https://domains.bh/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–5 years |
| Renewal Period | 1–5 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.bhregistry.bh` |
| RDAP Server | [rdap.bhregistry.bh/rdap](https://rdap.bhregistry.bh/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇧🇭 .net.bh — Bahrain
> The **.net.bh** is a country-code top-level domain (ccTLD) operated by Telecommunications Regulatory Authority (TRA). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Telecommunications Regulatory Authority (TRA) |
| Registry Country | Bahrain |
| Registry Website | [domains.bh](https://domains.bh/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–5 years |
| Renewal Period | 1–5 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.bhregistry.bh` |
| RDAP Server | [rdap.bhregistry.bh/rdap](https://rdap.bhregistry.bh/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇳🇱 .nl — Netherlands
> The **.nl** is a country-code top-level domain (ccTLD) operated by SIDN. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | SIDN |
| Registry Country | Netherlands |
| Registry Website | [www.sidn.nl](https://www.sidn.nl) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1 year |
| Renewal Period | 1 year |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 0 days |
| Redemption Period | 40 days |
| Pending Restore | 0 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 2–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DNSKEY |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ❌ No |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.sidn.nl` |
| RDAP Server | [rdap.sidn.nl](https://rdap.sidn.nl/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | SIDN Dispute Resolution |
| Reference | [www.sidn.nl/en/registrars/dispute-resolution-nl](https://www.sidn.nl/en/registrars/dispute-resolution-nl) |
| UDRP Support | ❌ No |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇳🇴 .no — Norway
> The **.no** is a country-code top-level domain (ccTLD) operated by Norid AS. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Norid AS |
| Registry Country | Norway |
| Registry Website | [www.norid.no](https://www.norid.no) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1 year |
| Renewal Period | 1 year |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ❌ No |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 0 days |
| Redemption Period | 0 days |
| Pending Restore | 0 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 2–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (8–64 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 2–10 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ✅ Yes |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.norid.no` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Local Presence
| Property | Value |
| --- | --- |
| Local Presence Required | ✅ Yes |
| Applies To Roles | Domain Owner |
| Requirements | Physical Address, Business Entity |
| Eligible Countries | NO |
## Registration model
`.no` registrations are **two-step**: `POST /v1/domains` accepts the registration request, but the domain is only registered at Norid once the **applicant declaration** is signed. The registrant receives an email with a signing link, with reminders on days **7, 14, 21 and 27**.
If the declaration is not signed within **30 days**, the request is cancelled and refunded.
## Contact Attributes
`.no` registrations identify the **registrant** (called *subscriber* by Norid) through a registry-verified identity:
| Attribute | Type | Required | Applies to | Allowed values |
| --- | --- | --- | --- | --- |
| `NOR_ID_IDENTITY_TYPE` | Enum | ✅ Yes | Registrant | `ORGANIZATION_NUMBER`, `ANONYMOUS_PERSON_IDENTIFIER`, `LOCAL_IDENTITY` |
| `NOR_ID_IDENTITY_VALUE` | String | ✅ Yes | Registrant | See below |
| `NOR_ID_CONTACT_TYPE` | Enum | ➖ Optional | Any | `PERSON`, `ORGANIZATION`, `ROLE` (derived automatically when omitted) |
- `ORGANIZATION_NUMBER`:
- a 9-digit organization number registered in the [Brønnøysund register](https://www.brreg.no/) (MOD11 check digit).
- Requires an **organization** contact (`org` field set).
- `ANONYMOUS_PERSON_IDENTIFIER`:
- a Norid person ID in the `N.PRI.xxxxxxxx` format, created by the registrant with [Norid's personal ID tool](https://pid.norid.no/).
- Requires a **person** contact (no `org`).
- The contact type is derived from the contact:
- `org` set → `ORGANIZATION`, otherwise `PERSON`.
- Technical contacts are always created as `ROLE` contacts (Norid requirement) and carry no identity.
## Identity verification by the registry
Norid cross-checks the contact data against the official Norwegian registers at contact creation:
- **Organizations**: the organization number must match the organization name in the Brønnøysund register (`EC004033 Name and identity mismatch`).
- **Persons**: the contact name must match the person registered for the personal ID in the National Population Register (Folkeregisteret), also `EC004033`. The match is case-insensitive but **strict about Norwegian letters**: a name registered as `Aktiv Ærfugl` is rejected when submitted as `AKTIV AERFUGL` (transliterated `AE`/`OE`/`AA` forms are not accepted). Use the exact spelling with `Æ`, `Ø`, `Å`.
## Registrant address
The registrant must have a **Norwegian postal address**: country `NO` and a 4-digit Norwegian postcode matching the Norwegian postal service's address lists. Both are validated upfront:
- a non-`NO` registrant country is rejected (local presence policy);
- a postcode that is not a 4-digit Norwegian postcode is rejected with a `422` pointing at `contacts.registrant[0].postal_code`.
Technical contacts may have foreign addresses.
## Applicant declaration
- The declaration is signed on a hosted page linked from the registrant email - resellers can also submit an already-signed declaration through [`POST /v1/domains/tld-specific/no/{domain}/applicant-declaration`](/api-reference#tag/domain_tld_specific/POST/v1/domains/tld-specific/no/{domain_reference}/applicant-declaration).
- For **person** registrants the declaration must be signed by the registrant themselves:
- the signed name must match the registrant contact name;
- it gets compared case-insensitively, accepting transliterated Norwegian letters;
- A mismatch returns `400`, `ERROR_NORID_DECLARATION_NAME_MISMATCH`.
- For **organization** registrants the signer is any person authorized by the organization, so the signed name is free text.
- The signature (name, date, IP, user agent) is stored for auditing and sent to Norid. The registrant receives a copy of the data by email.
# 🇳🇺 .nu — Niue
> The **.nu** is a country-code top-level domain (ccTLD) operated by Internetstiftelsen (The Swedish Internet Foundation). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Internetstiftelsen (The Swedish Internet Foundation) |
| Registry Country | Sweden |
| Registry Website | [internetstiftelsen.se](https://internetstiftelsen.se) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ❌ No |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 10 days |
| Redemption Period | 60 days |
| Pending Restore | 0 days |
| Pending Delete | 7 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (9–64 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–10 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ✅ Yes |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ❌ No |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ❌ No |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.iis.se` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
`.nu` is the ccTLD for Niue, operated from Sweden by Internetstiftelsen on the same EPP platform as [`.se`](/tld-knowledge-base/cctlds/se) and under the same technical rules. There is no local presence requirement.
## Contact Attributes
`.nu` provisions the holder (the registrant) only, and that holder must carry a personal or organization number:
| Attribute | Type | Required | Applies to | Format |
| --- | --- | --- | --- | --- |
| `REGISTRY_SE_ORG_NO` | String | ✅ Required | Domain Owner | A bracketed ISO 3166-1 alpha-2 country code followed by 1 to 123 characters, 127 characters overall |
| `REGISTRY_SE_VAT_NO` | String | ➖ Optional | Domain Owner | A two-letter country code followed by a country-specific string of letters and digits, 32 characters overall |
The country code identifies the jurisdiction in which the person or company is **registered**, which is not necessarily the country in the contact's postal address. A German company operating from Stockholm is `[DE]`, not `[SE]`.
`REGISTRY_SE_ORG_NO` is immutable once the handle exists at the registry. `REGISTRY_SE_VAT_NO` can be changed.
### `[SE]` numbers are verified by the registry
For every country code other than `[SE]`, the registry accepts a free-form identifier — the common case for `.nu`, which has no local presence requirement. `[SE]` is the exception: it requires a valid Swedish personal or organization number — six digits, a hyphen, then four digits (`[SE]NNNNNN-NNNN`) — and the registry verifies the number itself, not only its format.
> ⚠️ A correctly formatted but non-existent number is rejected. `[SE]111111-1111` matches the documented format and still fails:
>
> ```json
> {
> "type": "registry-request",
> "title": "Registry Request Error",
> "status": 400,
> "code": "ERROR_REGISTRY_REQUEST",
> "detail": "2004: Parameter value range error: Value error personal/organization identification number"
> }
> ```
>
> Supply the holder's own personal or organization number, or use a non-Swedish country code when the holder is registered elsewhere.
Internetstiftelsen's EPP specification uses `[SE]802405-0190` as its worked example (§7.1.5). That is Internetstiftelsen's own organisationsnummer — a live number, not a test value — so treat it as illustrative and submit the holder's own number instead.
When the holder has no organization name and the country code is `[SE]`, the registry expects a personal number rather than an organization number.
## Auth Codes
`.nu` auth codes are owned by the registry. A registrar cannot choose the value: the registry generates it, returns it in the registration response, and does not expose it in a later domain info request.
Request a fresh code with [`POST /v1/domains/tld-specific/nu/{domain_reference}/auth_code/request`](/api-reference#tag/domain_tld_specific/POST/v1/domains/tld-specific/nu/{domain_reference}/auth_code/request), which returns the code directly and **invalidates the previous one**. This is how a code consumed by a transfer is replaced.
## Transfers
`.nu` transfers complete **immediately**: there is no pending window, no approval and no rejection. A transfer request either succeeds outright or fails.
Two consequences are worth planning for:
- the gaining registrar learns the outcome from the transfer response itself, with no notification to wait for;
- the losing registrar is notified after the fact and cannot prevent the transfer.
Transfers do not extend the registration period, and the auth code is consumed in the process.
## Contacts on an Inbound Transfer
Transferring a `.nu` domain in does not move its contact with it. The registry **clones** the holder under your account as a new handle, and that clone is incomplete: it retains the name, email address, phone number and `iis:orgno`, but the postal address is returned as empty strings.
A cloned holder is returned in this form:
```json
{
"id": "76uFie8Nap2SVSfN",
"roid": "CONTACT_0000129392-TEST",
"email": "person@example.com",
"voice": "+46.812345678",
"postal_infos": [
{
"type": "loc",
"name": "Full Name",
"org": null,
"street": [""],
"city": "",
"sp": null,
"pc": null,
"cc": ""
}
],
"status": ["ok", "linked"]
}
```
The street, city, state, postal code and country the holder had at the losing registrar are **not carried over**, and cannot be recovered from the registry.
Because a contact cannot be stored without an address, the import populates each empty field with OpusDNS's own company address rather than leaving it blank. An imported `.nu` holder therefore arrives with `Franz-Mayer-Str. 1`, `Regensburg`, `93053`, `DE`, even though the holder has no connection to that address. The name, email address, phone number and `REGISTRY_SE_ORG_NO` are the holder's own.
> ⚠️ **Update the holder after an inbound transfer.** The placeholder address is a technical stand-in, not the holder's data. Correct it with `PATCH /v1/contacts/{contact_id}` once the transfer completes, and the change is propagated to the registry.
## Holder Verification
Internetstiftelsen may hold a new registration while it verifies the holder's data. The domain is created, but the registry applies `serverHold`, `serverTransferProhibited` and `serverRenewProhibited`, so it does not resolve and cannot be transferred or renewed while the check is open.
The check clears when the registry accepts the holder data, or when the holder is replaced with one that passes. Either outcome is reported by the registry and reconciled onto the domain automatically, so these statuses are removed without intervention. No action is required beyond correcting the holder data when the registry asks for it.
## Registry Lock
Registry lock blocks updates, transfers and deletions, and can be requested when registering or updating a domain. **The registry does not support unlocking over EPP**, so removal must be arranged directly with Internetstiftelsen.
# 🇧🇭 .org.bh — Bahrain
> The **.org.bh** is a country-code top-level domain (ccTLD) operated by Telecommunications Regulatory Authority (TRA). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Telecommunications Regulatory Authority (TRA) |
| Registry Country | Bahrain |
| Registry Website | [domains.bh](https://domains.bh/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–5 years |
| Renewal Period | 1–5 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.bhregistry.bh` |
| RDAP Server | [rdap.bhregistry.bh/rdap](https://rdap.bhregistry.bh/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇵🇱 .pl — Poland
> The **.pl** is a country-code top-level domain (ccTLD) operated by NASK - Naukowa i Akademicka Siec Komputerowa. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | NASK - Naukowa i Akademicka Siec Komputerowa |
| Registry Country | Poland |
| Registry Website | [www.dns.pl](https://www.dns.pl) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ❌ No |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 0 days |
| Redemption Period | 5 days |
| Pending Restore | 0 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (4–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ❌ No |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ❌ No |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.dns.pl` |
| RDAP Server | [rdap.dns.pl](https://rdap.dns.pl/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | .pl domain name dispute resolution (Polish arbitration courts) |
| Reference | [www.dns.pl/en/regulations](https://www.dns.pl/en/regulations) |
| UDRP Support | ❌ No |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇵🇲 .pm — Saint Pierre and Miquelon
> The **.pm** is a country-code top-level domain (ccTLD) operated by AFNIC (Association Française pour le Nommage Internet en Coopération). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | AFNIC (Association Française pour le Nommage Internet en Coopération) |
| Registry Country | France |
| Registry Website | [www.afnic.fr](https://www.afnic.fr) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 0 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–8 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 8 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.pm` |
| RDAP Server | [rdap.nic.pm](https://rdap.nic.pm) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Contact Attributes
AFNIC models every contact as either a **natural person** (`PP` — *personne physique*) or a
**legal entity** (`PM` — *personne morale*), and that choice decides which of the remaining
attributes apply.
Two things set the AFNIC TLDs apart from most ccTLDs:
- the attributes are required on **every** contact role — registrant, administrative, and
technical — not on the registrant alone;
- the roles do not have to agree. A `PP` registrant with a `PM` technical contact is a normal
`.pm` registration.
| Attribute | Type | Required | Applies to | Allowed values |
| --- | --- | --- | --- | --- |
| `AFNIC_CONTACT_TYPE` | Enum | ✅ Required | Every role | `PP` (natural person) or `PM` (legal entity) |
### Natural person (`PP`)
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PP_FIRST_NAME` | String | ✅ Required | The contact's first name. It is sent to AFNIC in addition to the standard `name` field, which carries the full name |
| `AFNIC_ID_STATUS` | Enum | ➖ Optional | `ok`, `no`, `pending`, `problem`, `ko`, `deprecated`, `control`, `delayed` |
| `AFNIC_REACHABLE_MEDIA` | Enum | ➖ Optional | `email` or `voice` — the channel through which the registrant was reached |
| `AFNIC_REACHABLE_STATUS` | Boolean | ➖ Optional | Whether that channel was confirmed |
`AFNIC_REACHABLE_STATUS` is only sent to the registry when `AFNIC_REACHABLE_MEDIA` is set
alongside it — a status on its own is dropped, because AFNIC carries the confirmation as an
attribute of the channel.
### Legal entity (`PM`)
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PM_LEGAL_STATUS` | Enum | ✅ Required | `company`, `association`, or `other` |
| `AFNIC_PM_SIREN` | String | ➖ Optional | SIREN or SIRET number from the French business register |
| `AFNIC_PM_VAT` | String | ➖ Optional | European VAT number |
| `AFNIC_PM_TRADEMARK` | String | ➖ Optional | Trademark registration number |
| `AFNIC_PM_DUNS` | Integer | ➖ Optional | D-U-N-S number |
| `AFNIC_PM_LOCAL` | String | ➖ Optional | Identifier from another official register, for an entity that has none of the above |
| `AFNIC_ID_STATUS` | Enum | ➖ Optional | Same values as for a natural person |
The five identifiers apply to the `company` and `other` legal statuses. An entity may supply
several; AFNIC accepts them together.
#### Associations
An `association` identifies itself through its WALDEC number, or through its publication in the
*Journal Officiel* — one of the two is mandatory, and a create that carries neither is rejected
before it reaches the registry.
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PM_ASSOC_WALDEC` | String | ➖ Conditional | WALDEC number of the association |
| `AFNIC_PM_ASSOC_PUBL_DATE` | Datetime | ➖ Conditional | Date of publication in the *Journal Officiel* |
| `AFNIC_PM_ASSOC_PUBL_PAGE` | Integer | ➖ Conditional | Page of that publication |
| `AFNIC_PM_ASSOC_PUBL_ANNOUNCE` | Integer | ➖ Optional | Announcement number within the publication |
| `AFNIC_PM_ASSOC_DECL` | Datetime | ➖ Optional | Date the association was declared |
Supply **either** `AFNIC_PM_ASSOC_WALDEC`, **or** `AFNIC_PM_ASSOC_PUBL_DATE` together with
`AFNIC_PM_ASSOC_PUBL_PAGE`. When a WALDEC number is present it is what gets sent, and the
publication attributes are ignored. `AFNIC_PM_ASSOC_DECL` and `AFNIC_PM_ASSOC_PUBL_ANNOUNCE`
only add detail to the publication route; neither satisfies the requirement on its own.
```json
{
"type": "policy-validation-error",
"title": "Policy Validation Error",
"status": 422,
"code": "ERROR_POLICY_VALIDATION",
"detail": "PM association requires AFNIC_PM_ASSOC_WALDEC or (AFNIC_PM_ASSOC_PUBL_DATE + AFNIC_PM_ASSOC_PUBL_PAGE)"
}
```
### Registry-managed attributes
| Attribute | Type | Allowed values |
| --- | --- | --- |
| `AFNIC_RESTRICTED_PUBLICATION` | Boolean | Whether AFNIC restricts publication of the contact's details |
`AFNIC_RESTRICTED_PUBLICATION` is read back from AFNIC when a contact is imported or read; it is
not sent on a contact create, so setting it on an attribute set has no effect.
### Example attribute sets
A natural person:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "PM registrant - individual",
"tld": "pm",
"attributes": {
"AFNIC_CONTACT_TYPE": "PP",
"AFNIC_PP_FIRST_NAME": "Pierre"
}
}'
```
An association identified by its *Journal Officiel* publication:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "PM registrant - association",
"tld": "pm",
"attributes": {
"AFNIC_CONTACT_TYPE": "PM",
"AFNIC_PM_LEGAL_STATUS": "association",
"AFNIC_PM_ASSOC_PUBL_DATE": "2015-03-14T00:00:00Z",
"AFNIC_PM_ASSOC_PUBL_PAGE": 118
}
}'
```
> ⚠️ **Reusing one contact for every role?** `AFNIC_CONTACT_TYPE` is required on the
> administrative and technical contacts too, not only the registrant. A create that carries it
> on the registrant alone is rejected before it reaches the registry:
>
> ```json
> {
> "type": "policy-validation-error",
> "title": "Policy Validation Error",
> "status": 422,
> "code": "ERROR_POLICY_VALIDATION",
> "errors": [
> {
> "detail": "Attribute 'AFNIC_CONTACT_TYPE' is required for admin contacts",
> "pointer": "contacts.admin[0].attributes.AFNIC_CONTACT_TYPE"
> }
> ],
> "detail": "Policy validation failed"
> }
> ```
These constraints are machine-readable: each `possible_attributes` entry returned by
[`GET /v1/tlds/pm`](/api-reference#tag/tld/GET/v1/tlds/{tld}) carries its own `type`,
`values`, `required`, `contact_roles`, and `conditions` fields. Build forms from the
specification rather than hard-coding the `PP`/`PM` split.
## Contact handles
AFNIC assigns contact handles itself — a handle cannot be chosen when creating a contact, and an
existing AFNIC handle cannot be adopted through the API.
## Transfers and registrant changes
The registrant is **not** part of a `.pm` transfer request: an inbound transfer keeps the
registrant the domain already has at the registry. The administrative and technical contacts are
supplied with the transfer as usual.
To move a domain to a different holder, transfer it first and then change the registrant with a
domain update — `.pm` supports a registrant change through
[`PATCH /v1/domains/{domain_reference}`](/api-reference#tag/domain/PATCH/v1/domains/{domain_reference}).
# 🇵🇷 .pr — Puerto Rico
> The **.pr** is a country-code top-level domain (ccTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact, Administrator |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇦🇲 .radio.am — Armenia
> The **.radio.am** is a country-code top-level domain (ccTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇫🇲 .radio.fm — Federated States of Micronesia
> The **.radio.fm** is a country-code top-level domain (ccTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇷🇪 .re — Réunion
> The **.re** is a country-code top-level domain (ccTLD) operated by AFNIC (Association Française pour le Nommage Internet en Coopération). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | AFNIC (Association Française pour le Nommage Internet en Coopération) |
| Registry Country | France |
| Registry Website | [www.afnic.fr](https://www.afnic.fr) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 0 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–8 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 8 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.re` |
| RDAP Server | [rdap.nic.re](https://rdap.nic.re) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Contact Attributes
AFNIC models every contact as either a **natural person** (`PP` — *personne physique*) or a
**legal entity** (`PM` — *personne morale*), and that choice decides which of the remaining
attributes apply.
Two things set the AFNIC TLDs apart from most ccTLDs:
- the attributes are required on **every** contact role — registrant, administrative, and
technical — not on the registrant alone;
- the roles do not have to agree. A `PP` registrant with a `PM` technical contact is a normal
`.re` registration.
| Attribute | Type | Required | Applies to | Allowed values |
| --- | --- | --- | --- | --- |
| `AFNIC_CONTACT_TYPE` | Enum | ✅ Required | Every role | `PP` (natural person) or `PM` (legal entity) |
### Natural person (`PP`)
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PP_FIRST_NAME` | String | ✅ Required | The contact's first name. It is sent to AFNIC in addition to the standard `name` field, which carries the full name |
| `AFNIC_ID_STATUS` | Enum | ➖ Optional | `ok`, `no`, `pending`, `problem`, `ko`, `deprecated`, `control`, `delayed` |
| `AFNIC_REACHABLE_MEDIA` | Enum | ➖ Optional | `email` or `voice` — the channel through which the registrant was reached |
| `AFNIC_REACHABLE_STATUS` | Boolean | ➖ Optional | Whether that channel was confirmed |
`AFNIC_REACHABLE_STATUS` is only sent to the registry when `AFNIC_REACHABLE_MEDIA` is set
alongside it — a status on its own is dropped, because AFNIC carries the confirmation as an
attribute of the channel.
### Legal entity (`PM`)
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PM_LEGAL_STATUS` | Enum | ✅ Required | `company`, `association`, or `other` |
| `AFNIC_PM_SIREN` | String | ➖ Optional | SIREN or SIRET number from the French business register |
| `AFNIC_PM_VAT` | String | ➖ Optional | European VAT number |
| `AFNIC_PM_TRADEMARK` | String | ➖ Optional | Trademark registration number |
| `AFNIC_PM_DUNS` | Integer | ➖ Optional | D-U-N-S number |
| `AFNIC_PM_LOCAL` | String | ➖ Optional | Identifier from another official register, for an entity that has none of the above |
| `AFNIC_ID_STATUS` | Enum | ➖ Optional | Same values as for a natural person |
The five identifiers apply to the `company` and `other` legal statuses. An entity may supply
several; AFNIC accepts them together.
#### Associations
An `association` identifies itself through its WALDEC number, or through its publication in the
*Journal Officiel* — one of the two is mandatory, and a create that carries neither is rejected
before it reaches the registry.
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PM_ASSOC_WALDEC` | String | ➖ Conditional | WALDEC number of the association |
| `AFNIC_PM_ASSOC_PUBL_DATE` | Datetime | ➖ Conditional | Date of publication in the *Journal Officiel* |
| `AFNIC_PM_ASSOC_PUBL_PAGE` | Integer | ➖ Conditional | Page of that publication |
| `AFNIC_PM_ASSOC_PUBL_ANNOUNCE` | Integer | ➖ Optional | Announcement number within the publication |
| `AFNIC_PM_ASSOC_DECL` | Datetime | ➖ Optional | Date the association was declared |
Supply **either** `AFNIC_PM_ASSOC_WALDEC`, **or** `AFNIC_PM_ASSOC_PUBL_DATE` together with
`AFNIC_PM_ASSOC_PUBL_PAGE`. When a WALDEC number is present it is what gets sent, and the
publication attributes are ignored. `AFNIC_PM_ASSOC_DECL` and `AFNIC_PM_ASSOC_PUBL_ANNOUNCE`
only add detail to the publication route; neither satisfies the requirement on its own.
```json
{
"type": "policy-validation-error",
"title": "Policy Validation Error",
"status": 422,
"code": "ERROR_POLICY_VALIDATION",
"detail": "PM association requires AFNIC_PM_ASSOC_WALDEC or (AFNIC_PM_ASSOC_PUBL_DATE + AFNIC_PM_ASSOC_PUBL_PAGE)"
}
```
### Registry-managed attributes
| Attribute | Type | Allowed values |
| --- | --- | --- |
| `AFNIC_RESTRICTED_PUBLICATION` | Boolean | Whether AFNIC restricts publication of the contact's details |
`AFNIC_RESTRICTED_PUBLICATION` is read back from AFNIC when a contact is imported or read; it is
not sent on a contact create, so setting it on an attribute set has no effect.
### Example attribute sets
A natural person:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "RE registrant - individual",
"tld": "re",
"attributes": {
"AFNIC_CONTACT_TYPE": "PP",
"AFNIC_PP_FIRST_NAME": "Pierre"
}
}'
```
An association identified by its *Journal Officiel* publication:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "RE registrant - association",
"tld": "re",
"attributes": {
"AFNIC_CONTACT_TYPE": "PM",
"AFNIC_PM_LEGAL_STATUS": "association",
"AFNIC_PM_ASSOC_PUBL_DATE": "2015-03-14T00:00:00Z",
"AFNIC_PM_ASSOC_PUBL_PAGE": 118
}
}'
```
> ⚠️ **Reusing one contact for every role?** `AFNIC_CONTACT_TYPE` is required on the
> administrative and technical contacts too, not only the registrant. A create that carries it
> on the registrant alone is rejected before it reaches the registry:
>
> ```json
> {
> "type": "policy-validation-error",
> "title": "Policy Validation Error",
> "status": 422,
> "code": "ERROR_POLICY_VALIDATION",
> "errors": [
> {
> "detail": "Attribute 'AFNIC_CONTACT_TYPE' is required for admin contacts",
> "pointer": "contacts.admin[0].attributes.AFNIC_CONTACT_TYPE"
> }
> ],
> "detail": "Policy validation failed"
> }
> ```
These constraints are machine-readable: each `possible_attributes` entry returned by
[`GET /v1/tlds/re`](/api-reference#tag/tld/GET/v1/tlds/{tld}) carries its own `type`,
`values`, `required`, `contact_roles`, and `conditions` fields. Build forms from the
specification rather than hard-coding the `PP`/`PM` split.
## Contact handles
AFNIC assigns contact handles itself — a handle cannot be chosen when creating a contact, and an
existing AFNIC handle cannot be adopted through the API.
## Transfers and registrant changes
The registrant is **not** part of a `.re` transfer request: an inbound transfer keeps the
registrant the domain already has at the registry. The administrative and technical contacts are
supplied with the transfer as usual.
To move a domain to a different holder, transfer it first and then change the registrant with a
domain update — `.re` supports a registrant change through
[`PATCH /v1/domains/{domain_reference}`](/api-reference#tag/domain/PATCH/v1/domains/{domain_reference}).
# 🇷🇴 .ro — Romania
> The **.ro** is a country-code top-level domain (ccTLD) operated by National Institute for R&D in Informatics (ROTLD). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | National Institute for R&D in Informatics (ROTLD) |
| Registry Country | Romania |
| Registry Website | [www.rotld.ro](https://www.rotld.ro/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | At expiration |
| Auto-Renew Enabled | ❌ No |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 0 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (6–40 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–6 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ❌ No |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ❌ No |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.rotld.ro` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇸🇨 .sc — Seychelles
> The **.sc** is a country-code top-level domain (ccTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [nic.sc](https://nic.sc) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact, Administrator |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [nic.sc/en/forms/Uniform-Domain-Name-Dispute-Resolution-Policy.pdf](https://nic.sc/en/forms/Uniform-Domain-Name-Dispute-Resolution-Policy.pdf) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇸🇪 .se — Sweden
> The **.se** is a country-code top-level domain (ccTLD) operated by Internetstiftelsen (The Swedish Internet Foundation). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Internetstiftelsen (The Swedish Internet Foundation) |
| Registry Country | Sweden |
| Registry Website | [internetstiftelsen.se](https://internetstiftelsen.se) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ❌ No |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 10 days |
| Redemption Period | 60 days |
| Pending Restore | 0 days |
| Pending Delete | 7 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (9–64 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–10 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ✅ Yes |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ❌ No |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ❌ No |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.iis.se` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Contact Attributes
`.se` provisions the holder (the registrant) only, and that holder must carry a personal or organization number:
| Attribute | Type | Required | Applies to | Format |
| --- | --- | --- | --- | --- |
| `REGISTRY_SE_ORG_NO` | String | ✅ Required | Domain Owner | A bracketed ISO 3166-1 alpha-2 country code followed by 1 to 123 characters, 127 characters overall |
| `REGISTRY_SE_VAT_NO` | String | ➖ Optional | Domain Owner | A two-letter country code followed by a country-specific string of letters and digits, 32 characters overall |
The country code identifies the jurisdiction in which the person or company is **registered**, which is not necessarily the country in the contact's postal address. A German company operating from Stockholm is `[DE]`, not `[SE]`.
`REGISTRY_SE_ORG_NO` is immutable once the handle exists at the registry. `REGISTRY_SE_VAT_NO` can be changed.
### `[SE]` numbers are verified by the registry
For every country code other than `[SE]`, the registry accepts a free-form identifier. `[SE]` is the exception: it requires a valid Swedish personal or organization number — six digits, a hyphen, then four digits (`[SE]NNNNNN-NNNN`) — and the registry verifies the number itself, not only its format.
> ⚠️ A correctly formatted but non-existent number is rejected. `[SE]111111-1111` matches the documented format and still fails:
>
> ```json
> {
> "type": "registry-request",
> "title": "Registry Request Error",
> "status": 400,
> "code": "ERROR_REGISTRY_REQUEST",
> "detail": "2004: Parameter value range error: Value error personal/organization identification number"
> }
> ```
>
> Supply the holder's own personal or organization number, or use a non-Swedish country code when the holder is registered elsewhere.
Internetstiftelsen's EPP specification uses `[SE]802405-0190` as its worked example (§7.1.5). That is Internetstiftelsen's own organisationsnummer — a live number, not a test value — so treat it as illustrative and submit the holder's own number instead.
When the holder has no organization name and the country code is `[SE]`, the registry expects a personal number rather than an organization number.
## Auth Codes
`.se` auth codes are owned by the registry. A registrar cannot choose the value: the registry generates it, returns it in the registration response, and does not expose it in a later domain info request.
Request a fresh code with [`POST /v1/domains/tld-specific/se/{domain_reference}/auth_code/request`](/api-reference#tag/domain_tld_specific/POST/v1/domains/tld-specific/se/{domain_reference}/auth_code/request), which returns the code directly and **invalidates the previous one**. This is how a code consumed by a transfer is replaced.
## Transfers
`.se` transfers complete **immediately**: there is no pending window, no approval and no rejection. A transfer request either succeeds outright or fails.
Two consequences are worth planning for:
- the gaining registrar learns the outcome from the transfer response itself, with no notification to wait for;
- the losing registrar is notified after the fact and cannot prevent the transfer.
Transfers do not extend the registration period, and the auth code is consumed in the process.
## Contacts on an Inbound Transfer
Transferring a `.se` domain in does not move its contact with it. The registry **clones** the holder under your account as a new handle, and that clone is incomplete: it retains the name, email address, phone number and `iis:orgno`, but the postal address is returned as empty strings.
A cloned holder is returned in this form:
```json
{
"id": "76uFie8Nap2SVSfN",
"roid": "CONTACT_0000129392-TEST",
"email": "person@example.com",
"voice": "+46.812345678",
"postal_infos": [
{
"type": "loc",
"name": "Full Name",
"org": null,
"street": [""],
"city": "",
"sp": null,
"pc": null,
"cc": ""
}
],
"status": ["ok", "linked"]
}
```
The street, city, state, postal code and country the holder had at the losing registrar are **not carried over**, and cannot be recovered from the registry.
Because a contact cannot be stored without an address, the import populates each empty field with OpusDNS's own company address rather than leaving it blank. An imported `.se` holder therefore arrives with `Franz-Mayer-Str. 1`, `Regensburg`, `93053`, `DE`, even though the holder has no connection to that address. The name, email address, phone number and `REGISTRY_SE_ORG_NO` are the holder's own.
> ⚠️ **Update the holder after an inbound transfer.** The placeholder address is a technical stand-in, not the holder's data. Correct it with `PATCH /v1/contacts/{contact_id}` once the transfer completes, and the change is propagated to the registry.
## Holder Verification
Internetstiftelsen may hold a new registration while it verifies the holder's data. The domain is created, but the registry applies `serverHold`, `serverTransferProhibited` and `serverRenewProhibited`, so it does not resolve and cannot be transferred or renewed while the check is open.
The check clears when the registry accepts the holder data, or when the holder is replaced with one that passes. Either outcome is reported by the registry and reconciled onto the domain automatically, so these statuses are removed without intervention. No action is required beyond correcting the holder data when the registry asks for it.
## Registry Lock
Registry lock blocks updates, transfers and deletions, and can be requested when registering or updating a domain. **The registry does not support unlocking over EPP**, so removal must be arranged directly with Internetstiftelsen.
# 🇸🇮 .si — Slovenia
> The **.si** is a country-code top-level domain (ccTLD) operated by Academic and Research Network of Slovenia (Arnes). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Academic and Research Network of Slovenia (Arnes) |
| Registry Country | Slovenia |
| Registry Website | [www.register.si](https://www.register.si) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–5 years |
| Renewal Period | 1–5 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ❌ No |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 30 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 2–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (1–255 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 2–10 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ✅ Yes |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ❌ No |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.register.si` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇸🇰 .sk — Slovakia
> The **.sk** is a country-code top-level domain (ccTLD) operated by SK-NIC, a.s.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | SK-NIC, a.s. |
| Registry Country | Slovakia |
| Registry Website | [www.sk-nic.sk](https://www.sk-nic.sk) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ❌ No |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 0 days |
| Standard Grace Period | 0 days |
| Redemption Period | 40 days |
| Pending Restore | 0 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (16–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ❌ No |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.sk-nic.sk` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Local Presence
| Property | Value |
| --- | --- |
| Local Presence Required | ✅ Yes |
| Applies To Roles | Domain Owner |
| Requirements | Physical Address |
| Eligible Countries | AT, BE, BG, HR, CY, CZ, DK, EE, FI, FR, DE, GR, HU, IE, IT, LV, LT, LU, MT, NL, PL, PT, RO, SK, SI, ES, SE, IS, LI, NO, CH, GB |
## Contact Attributes
`.sk` registrations carry registry-specific contact attributes beyond the standard EPP fields:
| Attribute | Type | Required | Applies to | Allowed values |
| --- | --- | --- | --- |--------------------------------------------------------------------|
| `SK_NIC_LEGAL_FORM` | Enum | ➖ Optional | All roles | `CORP` \| `PERS` |
| `SK_NIC_IDENT_VALUE` | String | ➖ Optional | All roles | Company identifier (`CORP`) or date of birth `YYYY-MM-DD` (`PERS`) |
The extension exists to discern the **legal form** of the contact, mainly for personal-data-protection reasons.
When `SK_NIC_LEGAL_FORM` is omitted, the legal form is derived from the contact: a contact with an `org` is treated as `CORP`, otherwise `PERS`.
Supplying `SK_NIC_LEGAL_FORM` explicitly overrides that derivation (needed for a self-employed entrepreneur, who is a natural person but registers as `CORP`).
These per-attribute constraints are machine-readable: each `possible_attributes` entry returned by [`GET /v1/tlds/sk`](/api-reference#tag/tld/GET/v1/tlds/{tld}) carries its own `type`, `required`, and `values` fields.
## Legal Form & Identification
Each `.sk` contact declares its legal form through `SK_NIC_LEGAL_FORM`, and may optionally provide an identifier through `SK_NIC_IDENT_VALUE`. The identifier type depends on the legal form.
| Legal form | Constant | Identifier (`SK_NIC_IDENT_VALUE`) | Format |
| --- | --- | --- | --- |
| Natural person | `PERS` | Date of birth | `YYYY-MM-DD` (e.g. `1987-01-01`) |
| Legal person or self-employed entrepreneur | `CORP` | Company identifier (IČO for Slovak legal persons; the equivalent business number from the relevant official register for foreign legal persons) | String, up to 32 characters |
The identifier is **not mandatory**, but the registry strongly recommends providing it to better identify the user and to support their claim to the domain.
# 🇹🇫 .tf — French Southern Territories
> The **.tf** is a country-code top-level domain (ccTLD) operated by AFNIC (Association Française pour le Nommage Internet en Coopération). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | AFNIC (Association Française pour le Nommage Internet en Coopération) |
| Registry Country | France |
| Registry Website | [www.afnic.fr](https://www.afnic.fr) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 0 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–8 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 8 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.tf` |
| RDAP Server | [rdap.nic.tf](https://rdap.nic.tf) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Contact Attributes
AFNIC models every contact as either a **natural person** (`PP` — *personne physique*) or a
**legal entity** (`PM` — *personne morale*), and that choice decides which of the remaining
attributes apply.
Two things set the AFNIC TLDs apart from most ccTLDs:
- the attributes are required on **every** contact role — registrant, administrative, and
technical — not on the registrant alone;
- the roles do not have to agree. A `PP` registrant with a `PM` technical contact is a normal
`.tf` registration.
| Attribute | Type | Required | Applies to | Allowed values |
| --- | --- | --- | --- | --- |
| `AFNIC_CONTACT_TYPE` | Enum | ✅ Required | Every role | `PP` (natural person) or `PM` (legal entity) |
### Natural person (`PP`)
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PP_FIRST_NAME` | String | ✅ Required | The contact's first name. It is sent to AFNIC in addition to the standard `name` field, which carries the full name |
| `AFNIC_ID_STATUS` | Enum | ➖ Optional | `ok`, `no`, `pending`, `problem`, `ko`, `deprecated`, `control`, `delayed` |
| `AFNIC_REACHABLE_MEDIA` | Enum | ➖ Optional | `email` or `voice` — the channel through which the registrant was reached |
| `AFNIC_REACHABLE_STATUS` | Boolean | ➖ Optional | Whether that channel was confirmed |
`AFNIC_REACHABLE_STATUS` is only sent to the registry when `AFNIC_REACHABLE_MEDIA` is set
alongside it — a status on its own is dropped, because AFNIC carries the confirmation as an
attribute of the channel.
### Legal entity (`PM`)
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PM_LEGAL_STATUS` | Enum | ✅ Required | `company`, `association`, or `other` |
| `AFNIC_PM_SIREN` | String | ➖ Optional | SIREN or SIRET number from the French business register |
| `AFNIC_PM_VAT` | String | ➖ Optional | European VAT number |
| `AFNIC_PM_TRADEMARK` | String | ➖ Optional | Trademark registration number |
| `AFNIC_PM_DUNS` | Integer | ➖ Optional | D-U-N-S number |
| `AFNIC_PM_LOCAL` | String | ➖ Optional | Identifier from another official register, for an entity that has none of the above |
| `AFNIC_ID_STATUS` | Enum | ➖ Optional | Same values as for a natural person |
The five identifiers apply to the `company` and `other` legal statuses. An entity may supply
several; AFNIC accepts them together.
#### Associations
An `association` identifies itself through its WALDEC number, or through its publication in the
*Journal Officiel* — one of the two is mandatory, and a create that carries neither is rejected
before it reaches the registry.
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PM_ASSOC_WALDEC` | String | ➖ Conditional | WALDEC number of the association |
| `AFNIC_PM_ASSOC_PUBL_DATE` | Datetime | ➖ Conditional | Date of publication in the *Journal Officiel* |
| `AFNIC_PM_ASSOC_PUBL_PAGE` | Integer | ➖ Conditional | Page of that publication |
| `AFNIC_PM_ASSOC_PUBL_ANNOUNCE` | Integer | ➖ Optional | Announcement number within the publication |
| `AFNIC_PM_ASSOC_DECL` | Datetime | ➖ Optional | Date the association was declared |
Supply **either** `AFNIC_PM_ASSOC_WALDEC`, **or** `AFNIC_PM_ASSOC_PUBL_DATE` together with
`AFNIC_PM_ASSOC_PUBL_PAGE`. When a WALDEC number is present it is what gets sent, and the
publication attributes are ignored. `AFNIC_PM_ASSOC_DECL` and `AFNIC_PM_ASSOC_PUBL_ANNOUNCE`
only add detail to the publication route; neither satisfies the requirement on its own.
```json
{
"type": "policy-validation-error",
"title": "Policy Validation Error",
"status": 422,
"code": "ERROR_POLICY_VALIDATION",
"detail": "PM association requires AFNIC_PM_ASSOC_WALDEC or (AFNIC_PM_ASSOC_PUBL_DATE + AFNIC_PM_ASSOC_PUBL_PAGE)"
}
```
### Registry-managed attributes
| Attribute | Type | Allowed values |
| --- | --- | --- |
| `AFNIC_RESTRICTED_PUBLICATION` | Boolean | Whether AFNIC restricts publication of the contact's details |
`AFNIC_RESTRICTED_PUBLICATION` is read back from AFNIC when a contact is imported or read; it is
not sent on a contact create, so setting it on an attribute set has no effect.
### Example attribute sets
A natural person:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "TF registrant - individual",
"tld": "tf",
"attributes": {
"AFNIC_CONTACT_TYPE": "PP",
"AFNIC_PP_FIRST_NAME": "Pierre"
}
}'
```
An association identified by its *Journal Officiel* publication:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "TF registrant - association",
"tld": "tf",
"attributes": {
"AFNIC_CONTACT_TYPE": "PM",
"AFNIC_PM_LEGAL_STATUS": "association",
"AFNIC_PM_ASSOC_PUBL_DATE": "2015-03-14T00:00:00Z",
"AFNIC_PM_ASSOC_PUBL_PAGE": 118
}
}'
```
> ⚠️ **Reusing one contact for every role?** `AFNIC_CONTACT_TYPE` is required on the
> administrative and technical contacts too, not only the registrant. A create that carries it
> on the registrant alone is rejected before it reaches the registry:
>
> ```json
> {
> "type": "policy-validation-error",
> "title": "Policy Validation Error",
> "status": 422,
> "code": "ERROR_POLICY_VALIDATION",
> "errors": [
> {
> "detail": "Attribute 'AFNIC_CONTACT_TYPE' is required for admin contacts",
> "pointer": "contacts.admin[0].attributes.AFNIC_CONTACT_TYPE"
> }
> ],
> "detail": "Policy validation failed"
> }
> ```
These constraints are machine-readable: each `possible_attributes` entry returned by
[`GET /v1/tlds/tf`](/api-reference#tag/tld/GET/v1/tlds/{tld}) carries its own `type`,
`values`, `required`, `contact_roles`, and `conditions` fields. Build forms from the
specification rather than hard-coding the `PP`/`PM` split.
## Contact handles
AFNIC assigns contact handles itself — a handle cannot be chosen when creating a contact, and an
existing AFNIC handle cannot be adopted through the API.
## Transfers and registrant changes
The registrant is **not** part of a `.tf` transfer request: an inbound transfer keeps the
registrant the domain already has at the registry. The administrative and technical contacts are
supplied with the transfer as usual.
To move a domain to a different holder, transfer it first and then change the registrant with a
domain update — `.tf` supports a registrant change through
[`PATCH /v1/domains/{domain_reference}`](/api-reference#tag/domain/PATCH/v1/domains/{domain_reference}).
# 🇹🇴 .to — Tonga
> The **.to** is a country-code top-level domain (ccTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇹🇻 .tv — Tuvalu
> The **.tv** is a country-code top-level domain (ccTLD) operated by Ministry of Transport, Energy, Communications and Innovations. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Ministry of Transport, Energy, Communications and Innovations |
| Registry Country | Tuvalu |
| Registry Website | [turnon.tv](https://turnon.tv) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.tv` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇬🇧 .uk — United Kingdom
> The **.uk** is a country-code top-level domain (ccTLD) operated by Nominet UK. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Nominet UK |
| Registry Country | United Kingdom |
| Registry Website | [www.nominet.uk](https://www.nominet.uk) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ❌ No |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, renewal |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 30 days |
| Redemption Period | 60 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ❌ No |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–10 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ❌ No |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.uk` |
| RDAP Server | [rdap.nominet.uk/uk](https://rdap.nominet.uk/uk/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | DRS |
| Reference | [www.nominet.uk/disputes](https://www.nominet.uk/disputes/) |
| UDRP Support | ❌ No |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇺🇸 .us — United States
> The **.us** is a country-code top-level domain (ccTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.us` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | usDRP |
| Reference | [www.about.us/policies/ustld-dispute-resolution-policy](https://www.about.us/policies/ustld-dispute-resolution-policy/) |
| UDRP Support | ❌ No |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇻🇨 .vc — Saint Vincent and the Grenadines
> The **.vc** is a country-code top-level domain (ccTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact, Administrator |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇻🇬 .vg — British Virgin Islands
> The **.vg** is a country-code top-level domain (ccTLD) operated by Telecommunications Regulatory Commission of the Virgin Islands. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Telecommunications Regulatory Commission of the Virgin Islands |
| Registry Country | British Virgin Islands |
| Registry Website | [nic.vg](https://nic.vg/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.vg` |
| RDAP Server | [rdap.centralnic.com/vg](https://rdap.centralnic.com/vg/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇻🇺 .vu — Vanuatu
> The **.vu** is a country-code top-level domain (ccTLD) operated by Telecommunications Radiocommunications and Broadcasting Regulator (TRBR). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Telecommunications Radiocommunications and Broadcasting Regulator (TRBR) |
| Registry Country | Vanuatu |
| Registry Website | [vunic.vu](https://vunic.vu) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ❌ No |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.dnrs.vu` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇼🇫 .wf — Wallis and Futuna
> The **.wf** is a country-code top-level domain (ccTLD) operated by AFNIC (Association Française pour le Nommage Internet en Coopération). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | AFNIC (Association Française pour le Nommage Internet en Coopération) |
| Registry Country | France |
| Registry Website | [www.afnic.fr](https://www.afnic.fr) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 0 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–8 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 8 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.wf` |
| RDAP Server | [rdap.nic.wf](https://rdap.nic.wf) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Contact Attributes
AFNIC models every contact as either a **natural person** (`PP` — *personne physique*) or a
**legal entity** (`PM` — *personne morale*), and that choice decides which of the remaining
attributes apply.
Two things set the AFNIC TLDs apart from most ccTLDs:
- the attributes are required on **every** contact role — registrant, administrative, and
technical — not on the registrant alone;
- the roles do not have to agree. A `PP` registrant with a `PM` technical contact is a normal
`.wf` registration.
| Attribute | Type | Required | Applies to | Allowed values |
| --- | --- | --- | --- | --- |
| `AFNIC_CONTACT_TYPE` | Enum | ✅ Required | Every role | `PP` (natural person) or `PM` (legal entity) |
### Natural person (`PP`)
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PP_FIRST_NAME` | String | ✅ Required | The contact's first name. It is sent to AFNIC in addition to the standard `name` field, which carries the full name |
| `AFNIC_ID_STATUS` | Enum | ➖ Optional | `ok`, `no`, `pending`, `problem`, `ko`, `deprecated`, `control`, `delayed` |
| `AFNIC_REACHABLE_MEDIA` | Enum | ➖ Optional | `email` or `voice` — the channel through which the registrant was reached |
| `AFNIC_REACHABLE_STATUS` | Boolean | ➖ Optional | Whether that channel was confirmed |
`AFNIC_REACHABLE_STATUS` is only sent to the registry when `AFNIC_REACHABLE_MEDIA` is set
alongside it — a status on its own is dropped, because AFNIC carries the confirmation as an
attribute of the channel.
### Legal entity (`PM`)
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PM_LEGAL_STATUS` | Enum | ✅ Required | `company`, `association`, or `other` |
| `AFNIC_PM_SIREN` | String | ➖ Optional | SIREN or SIRET number from the French business register |
| `AFNIC_PM_VAT` | String | ➖ Optional | European VAT number |
| `AFNIC_PM_TRADEMARK` | String | ➖ Optional | Trademark registration number |
| `AFNIC_PM_DUNS` | Integer | ➖ Optional | D-U-N-S number |
| `AFNIC_PM_LOCAL` | String | ➖ Optional | Identifier from another official register, for an entity that has none of the above |
| `AFNIC_ID_STATUS` | Enum | ➖ Optional | Same values as for a natural person |
The five identifiers apply to the `company` and `other` legal statuses. An entity may supply
several; AFNIC accepts them together.
#### Associations
An `association` identifies itself through its WALDEC number, or through its publication in the
*Journal Officiel* — one of the two is mandatory, and a create that carries neither is rejected
before it reaches the registry.
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PM_ASSOC_WALDEC` | String | ➖ Conditional | WALDEC number of the association |
| `AFNIC_PM_ASSOC_PUBL_DATE` | Datetime | ➖ Conditional | Date of publication in the *Journal Officiel* |
| `AFNIC_PM_ASSOC_PUBL_PAGE` | Integer | ➖ Conditional | Page of that publication |
| `AFNIC_PM_ASSOC_PUBL_ANNOUNCE` | Integer | ➖ Optional | Announcement number within the publication |
| `AFNIC_PM_ASSOC_DECL` | Datetime | ➖ Optional | Date the association was declared |
Supply **either** `AFNIC_PM_ASSOC_WALDEC`, **or** `AFNIC_PM_ASSOC_PUBL_DATE` together with
`AFNIC_PM_ASSOC_PUBL_PAGE`. When a WALDEC number is present it is what gets sent, and the
publication attributes are ignored. `AFNIC_PM_ASSOC_DECL` and `AFNIC_PM_ASSOC_PUBL_ANNOUNCE`
only add detail to the publication route; neither satisfies the requirement on its own.
```json
{
"type": "policy-validation-error",
"title": "Policy Validation Error",
"status": 422,
"code": "ERROR_POLICY_VALIDATION",
"detail": "PM association requires AFNIC_PM_ASSOC_WALDEC or (AFNIC_PM_ASSOC_PUBL_DATE + AFNIC_PM_ASSOC_PUBL_PAGE)"
}
```
### Registry-managed attributes
| Attribute | Type | Allowed values |
| --- | --- | --- |
| `AFNIC_RESTRICTED_PUBLICATION` | Boolean | Whether AFNIC restricts publication of the contact's details |
`AFNIC_RESTRICTED_PUBLICATION` is read back from AFNIC when a contact is imported or read; it is
not sent on a contact create, so setting it on an attribute set has no effect.
### Example attribute sets
A natural person:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "WF registrant - individual",
"tld": "wf",
"attributes": {
"AFNIC_CONTACT_TYPE": "PP",
"AFNIC_PP_FIRST_NAME": "Pierre"
}
}'
```
An association identified by its *Journal Officiel* publication:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "WF registrant - association",
"tld": "wf",
"attributes": {
"AFNIC_CONTACT_TYPE": "PM",
"AFNIC_PM_LEGAL_STATUS": "association",
"AFNIC_PM_ASSOC_PUBL_DATE": "2015-03-14T00:00:00Z",
"AFNIC_PM_ASSOC_PUBL_PAGE": 118
}
}'
```
> ⚠️ **Reusing one contact for every role?** `AFNIC_CONTACT_TYPE` is required on the
> administrative and technical contacts too, not only the registrant. A create that carries it
> on the registrant alone is rejected before it reaches the registry:
>
> ```json
> {
> "type": "policy-validation-error",
> "title": "Policy Validation Error",
> "status": 422,
> "code": "ERROR_POLICY_VALIDATION",
> "errors": [
> {
> "detail": "Attribute 'AFNIC_CONTACT_TYPE' is required for admin contacts",
> "pointer": "contacts.admin[0].attributes.AFNIC_CONTACT_TYPE"
> }
> ],
> "detail": "Policy validation failed"
> }
> ```
These constraints are machine-readable: each `possible_attributes` entry returned by
[`GET /v1/tlds/wf`](/api-reference#tag/tld/GET/v1/tlds/{tld}) carries its own `type`,
`values`, `required`, `contact_roles`, and `conditions` fields. Build forms from the
specification rather than hard-coding the `PP`/`PM` split.
## Contact handles
AFNIC assigns contact handles itself — a handle cannot be chosen when creating a contact, and an
existing AFNIC handle cannot be adopted through the API.
## Transfers and registrant changes
The registrant is **not** part of a `.wf` transfer request: an inbound transfer keeps the
registrant the domain already has at the registry. The administrative and technical contacts are
supplied with the transfer as usual.
To move a domain to a different holder, transfer it first and then change the registrant with a
domain update — `.wf` supports a registrant change through
[`PATCH /v1/domains/{domain_reference}`](/api-reference#tag/domain/PATCH/v1/domains/{domain_reference}).
# 🇼🇸 .ws — Samoa
> The **.ws** is a country-code top-level domain (ccTLD) operated by Global Domains International, Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | Global Domains International, Inc. |
| Registry Country | United States |
| Registry Website | [www.website.ws](https://www.website.ws) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 4–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.website.ws` |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🇾🇹 .yt — Mayotte
> The **.yt** is a country-code top-level domain (ccTLD) operated by AFNIC (Association Française pour le Nommage Internet en Coopération). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | ccTLD |
| Registry | AFNIC (Association Française pour le Nommage Internet en Coopération) |
| Registry Country | France |
| Registry Website | [www.afnic.fr](https://www.afnic.fr) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 0 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–8 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 8 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.yt` |
| RDAP Server | [rdap.nic.yt](https://rdap.nic.yt) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Contact Attributes
AFNIC models every contact as either a **natural person** (`PP` — *personne physique*) or a
**legal entity** (`PM` — *personne morale*), and that choice decides which of the remaining
attributes apply.
Two things set the AFNIC TLDs apart from most ccTLDs:
- the attributes are required on **every** contact role — registrant, administrative, and
technical — not on the registrant alone;
- the roles do not have to agree. A `PP` registrant with a `PM` technical contact is a normal
`.yt` registration.
| Attribute | Type | Required | Applies to | Allowed values |
| --- | --- | --- | --- | --- |
| `AFNIC_CONTACT_TYPE` | Enum | ✅ Required | Every role | `PP` (natural person) or `PM` (legal entity) |
### Natural person (`PP`)
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PP_FIRST_NAME` | String | ✅ Required | The contact's first name. It is sent to AFNIC in addition to the standard `name` field, which carries the full name |
| `AFNIC_ID_STATUS` | Enum | ➖ Optional | `ok`, `no`, `pending`, `problem`, `ko`, `deprecated`, `control`, `delayed` |
| `AFNIC_REACHABLE_MEDIA` | Enum | ➖ Optional | `email` or `voice` — the channel through which the registrant was reached |
| `AFNIC_REACHABLE_STATUS` | Boolean | ➖ Optional | Whether that channel was confirmed |
`AFNIC_REACHABLE_STATUS` is only sent to the registry when `AFNIC_REACHABLE_MEDIA` is set
alongside it — a status on its own is dropped, because AFNIC carries the confirmation as an
attribute of the channel.
### Legal entity (`PM`)
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PM_LEGAL_STATUS` | Enum | ✅ Required | `company`, `association`, or `other` |
| `AFNIC_PM_SIREN` | String | ➖ Optional | SIREN or SIRET number from the French business register |
| `AFNIC_PM_VAT` | String | ➖ Optional | European VAT number |
| `AFNIC_PM_TRADEMARK` | String | ➖ Optional | Trademark registration number |
| `AFNIC_PM_DUNS` | Integer | ➖ Optional | D-U-N-S number |
| `AFNIC_PM_LOCAL` | String | ➖ Optional | Identifier from another official register, for an entity that has none of the above |
| `AFNIC_ID_STATUS` | Enum | ➖ Optional | Same values as for a natural person |
The five identifiers apply to the `company` and `other` legal statuses. An entity may supply
several; AFNIC accepts them together.
#### Associations
An `association` identifies itself through its WALDEC number, or through its publication in the
*Journal Officiel* — one of the two is mandatory, and a create that carries neither is rejected
before it reaches the registry.
| Attribute | Type | Required | Allowed values |
| --- | --- | --- | --- |
| `AFNIC_PM_ASSOC_WALDEC` | String | ➖ Conditional | WALDEC number of the association |
| `AFNIC_PM_ASSOC_PUBL_DATE` | Datetime | ➖ Conditional | Date of publication in the *Journal Officiel* |
| `AFNIC_PM_ASSOC_PUBL_PAGE` | Integer | ➖ Conditional | Page of that publication |
| `AFNIC_PM_ASSOC_PUBL_ANNOUNCE` | Integer | ➖ Optional | Announcement number within the publication |
| `AFNIC_PM_ASSOC_DECL` | Datetime | ➖ Optional | Date the association was declared |
Supply **either** `AFNIC_PM_ASSOC_WALDEC`, **or** `AFNIC_PM_ASSOC_PUBL_DATE` together with
`AFNIC_PM_ASSOC_PUBL_PAGE`. When a WALDEC number is present it is what gets sent, and the
publication attributes are ignored. `AFNIC_PM_ASSOC_DECL` and `AFNIC_PM_ASSOC_PUBL_ANNOUNCE`
only add detail to the publication route; neither satisfies the requirement on its own.
```json
{
"type": "policy-validation-error",
"title": "Policy Validation Error",
"status": 422,
"code": "ERROR_POLICY_VALIDATION",
"detail": "PM association requires AFNIC_PM_ASSOC_WALDEC or (AFNIC_PM_ASSOC_PUBL_DATE + AFNIC_PM_ASSOC_PUBL_PAGE)"
}
```
### Registry-managed attributes
| Attribute | Type | Allowed values |
| --- | --- | --- |
| `AFNIC_RESTRICTED_PUBLICATION` | Boolean | Whether AFNIC restricts publication of the contact's details |
`AFNIC_RESTRICTED_PUBLICATION` is read back from AFNIC when a contact is imported or read; it is
not sent on a contact create, so setting it on an attribute set has no effect.
### Example attribute sets
A natural person:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "YT registrant - individual",
"tld": "yt",
"attributes": {
"AFNIC_CONTACT_TYPE": "PP",
"AFNIC_PP_FIRST_NAME": "Pierre"
}
}'
```
An association identified by its *Journal Officiel* publication:
```bash
curl "$OPUSDNS_API_BASE/v1/contacts/attribute-sets" \
--request POST \
--header "X-Api-Key: $OPUSDNS_API_KEY" \
--header "Content-Type: application/json" \
--data '{
"label": "YT registrant - association",
"tld": "yt",
"attributes": {
"AFNIC_CONTACT_TYPE": "PM",
"AFNIC_PM_LEGAL_STATUS": "association",
"AFNIC_PM_ASSOC_PUBL_DATE": "2015-03-14T00:00:00Z",
"AFNIC_PM_ASSOC_PUBL_PAGE": 118
}
}'
```
> ⚠️ **Reusing one contact for every role?** `AFNIC_CONTACT_TYPE` is required on the
> administrative and technical contacts too, not only the registrant. A create that carries it
> on the registrant alone is rejected before it reaches the registry:
>
> ```json
> {
> "type": "policy-validation-error",
> "title": "Policy Validation Error",
> "status": 422,
> "code": "ERROR_POLICY_VALIDATION",
> "errors": [
> {
> "detail": "Attribute 'AFNIC_CONTACT_TYPE' is required for admin contacts",
> "pointer": "contacts.admin[0].attributes.AFNIC_CONTACT_TYPE"
> }
> ],
> "detail": "Policy validation failed"
> }
> ```
These constraints are machine-readable: each `possible_attributes` entry returned by
[`GET /v1/tlds/yt`](/api-reference#tag/tld/GET/v1/tlds/{tld}) carries its own `type`,
`values`, `required`, `contact_roles`, and `conditions` fields. Build forms from the
specification rather than hard-coding the `PP`/`PM` split.
## Contact handles
AFNIC assigns contact handles itself — a handle cannot be chosen when creating a contact, and an
existing AFNIC handle cannot be adopted through the API.
## Transfers and registrant changes
The registrant is **not** part of a `.yt` transfer request: an inbound transfer keeps the
registrant the domain already has at the registry. The administrative and technical contacts are
supplied with the transfer as usual.
To move a domain to a different holder, transfer it first and then change the registrant with a
domain update — `.yt` supports a registrant change through
[`PATCH /v1/domains/{domain_reference}`](/api-reference#tag/domain/PATCH/v1/domains/{domain_reference}).
# 🌐 .academy — Identity Digital Inc.
> The **.academy** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .accountants — Identity Digital Inc.
> The **.accountants** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .actor — Identity Digital Inc.
> The **.actor** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .ae.org — CentralNic Group PLC
> The **.ae.org** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .agency — Identity Digital Inc.
> The **.agency** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .airforce — Identity Digital Inc.
> The **.airforce** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .apartments — Identity Digital Inc.
> The **.apartments** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .app — Charleston Road Registry Inc.
> The **.app** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2018-03-29 – 2018-05-01) |
| Eap | ✅ Supported (2018-05-01 – 2018-05-08) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .archi — Identity Digital Inc.
> The **.archi** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .army — Identity Digital Inc.
> The **.army** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .art — CentralNic Group PLC
> The **.art** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .associates — Identity Digital Inc.
> The **.associates** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .attorney — Identity Digital Inc.
> The **.attorney** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .auction — Identity Digital Inc.
> The **.auction** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .audio — CentralNic Group PLC
> The **.audio** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .auto — CentralNic Group PLC
> The **.auto** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .autos — CentralNic Group PLC
> The **.autos** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .baby — CentralNic Group PLC
> The **.baby** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .band — Identity Digital Inc.
> The **.band** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .bargains — Identity Digital Inc.
> The **.bargains** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .bayern — Bayern Connect GmbH
> The **.bayern** is a generic top-level domain (gTLD) operated by Bayern Connect GmbH. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Bayern Connect GmbH |
| Registry Country | Germany |
| Registry Website | [domains.bayern](https://domains.bayern) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (4–89 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–12 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DNSKEY |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.bayern` |
| RDAP Server | [rdap.nic.bayern](https://rdap.nic.bayern/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .beer — GoDaddy Inc.
> The **.beer** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (4 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.beer` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .berlin — TLD-BOX Registrydienstleistungen GmbH
> The **.berlin** is a generic top-level domain (gTLD) operated by TLD-BOX Registrydienstleistungen GmbH. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | TLD-BOX Registrydienstleistungen GmbH |
| Registry Country | Austria |
| Registry Website | [www.nic.at/en/tldbox](https://www.nic.at/en/tldbox) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ❌ No |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (2 tables) |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.berlin` |
| RDAP Server | [rdap.nic.berlin/v1](https://rdap.nic.berlin/v1/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Local Presence
| Property | Value |
| --- | --- |
| Local Presence Required | ✅ Yes |
| Applies To Roles | Domain Owner, Administrator, Technical Contact |
| Requirements | Physical Address |
| Eligible Countries | Any |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .best — CentralNic Group PLC
> The **.best** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .bet — Identity Digital Inc.
> The **.bet** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .bike — Identity Digital Inc.
> The **.bike** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .bingo — Identity Digital Inc.
> The **.bingo** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .bio — Identity Digital Inc.
> The **.bio** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .biz — GoDaddy Inc.
> The **.biz** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (15 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .black — Identity Digital Inc.
> The **.black** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .blackfriday — GoDaddy Inc.
> The **.blackfriday** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (8 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .blog — Knock Knock WhoIS There, LLC (KKWT)
> The **.blog** is a generic top-level domain (gTLD) operated by Knock Knock WhoIS There, LLC (KKWT). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Knock Knock WhoIS There, LLC (KKWT) |
| Registry Country | United States |
| Registry Website | [my.blog](https://my.blog) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (6–16 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.blog` |
| RDAP Server | [rdap.blog.fury.ca/rdap](https://rdap.blog.fury.ca/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .blue — Identity Digital Inc.
> The **.blue** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .boats — CentralNic Group PLC
> The **.boats** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .bond — CentralNic Group PLC
> The **.bond** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .boo — Charleston Road Registry Inc.
> The **.boo** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2022-10-04 – 2022-11-07) |
| Eap | ✅ Supported (2022-11-08 – 2022-11-15) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .boston — GoDaddy Inc.
> The **.boston** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .boutique — Identity Digital Inc.
> The **.boutique** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .br.com — CentralNic Group PLC
> The **.br.com** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .broker — Identity Digital Inc.
> The **.broker** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .brussels — DNS Belgium
> The **.brussels** is a generic top-level domain (gTLD) operated by DNS Belgium. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | DNS Belgium |
| Registry Country | Belgium |
| Registry Website | [www.dnsbelgium.be](https://www.dnsbelgium.be) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 2–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ❌ No |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| RDAP Server | [rdap.nic.brussels](https://rdap.nic.brussels/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .build — CentralNic Group PLC
> The **.build** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .builders — Identity Digital Inc.
> The **.builders** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .business — Identity Digital Inc.
> The **.business** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cab — Identity Digital Inc.
> The **.cab** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cafe — Identity Digital Inc.
> The **.cafe** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cam — CentralNic Group PLC
> The **.cam** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .camera — Identity Digital Inc.
> The **.camera** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .camp — Identity Digital Inc.
> The **.camp** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .capital — Identity Digital Inc.
> The **.capital** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .car — CentralNic Group PLC
> The **.car** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cards — Identity Digital Inc.
> The **.cards** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .care — Identity Digital Inc.
> The **.care** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .careers — Identity Digital Inc.
> The **.careers** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cars — CentralNic Group PLC
> The **.cars** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .casa — GoDaddy Inc.
> The **.casa** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (3 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .case — CentralNic Group PLC
> The **.case** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cash — Identity Digital Inc.
> The **.cash** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .casino — Identity Digital Inc.
> The **.casino** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .catering — Identity Digital Inc.
> The **.catering** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .center — Identity Digital Inc.
> The **.center** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .ceo — CentralNic Group PLC
> The **.ceo** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cfd — CentralNic Group PLC
> The **.cfd** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .channel — Charleston Road Registry Inc.
> The **.channel** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2022-05-03 – 2022-06-07) |
| Eap | ✅ Supported (2025-02-04 – 2025-02-11) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .charity — Public Interest Registry
> The **.charity** is a generic top-level domain (gTLD) operated by Public Interest Registry. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Public Interest Registry |
| Registry Country | United States |
| Registry Website | [pir.org](https://pir.org/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.charity` |
| RDAP Server | [rdap.publicinterestregistry.org/rdap](https://rdap.publicinterestregistry.org/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | URS |
| Reference | [www.icann.org/urs-en](https://www.icann.org/urs-en) |
| UDRP Support | ❌ No |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .chat — Identity Digital Inc.
> The **.chat** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cheap — Identity Digital Inc.
> The **.cheap** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .christmas — CentralNic Group PLC
> The **.christmas** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .church — Identity Digital Inc.
> The **.church** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .city — Identity Digital Inc.
> The **.city** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .claims — Identity Digital Inc.
> The **.claims** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cleaning — Identity Digital Inc.
> The **.cleaning** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .clinic — Identity Digital Inc.
> The **.clinic** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .clothing — Identity Digital Inc.
> The **.clothing** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cloud — Tucows Registry Inc.
> The **.cloud** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.cloud` |
| RDAP Server | [rdap.registry.cloud/rdap](https://rdap.registry.cloud/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .club — GoDaddy Inc.
> The **.club** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (19 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cn.com — CentralNic Group PLC
> The **.cn.com** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .co.com — CentralNic Group PLC
> The **.co.com** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .coach — Identity Digital Inc.
> The **.coach** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .codes — Identity Digital Inc.
> The **.codes** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .coffee — Identity Digital Inc.
> The **.coffee** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .college — CentralNic Group PLC
> The **.college** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .com — VeriSign, Inc.
> The **.com** is a generic top-level domain (gTLD) operated by VeriSign, Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | VeriSign, Inc. |
| Registry Country | United States |
| Registry Website | [www.verisign.com](https://www.verisign.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (97 tables) |
| Premium Domains | ❌ No |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.verisign-grs.com` |
| RDAP Server | [rdap.verisign.com/com/v1](https://rdap.verisign.com/com/v1/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .community — Identity Digital Inc.
> The **.community** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .company — Identity Digital Inc.
> The **.company** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .compare — GoDaddy Inc.
> The **.compare** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .computer — Identity Digital Inc.
> The **.computer** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .condos — Identity Digital Inc.
> The **.condos** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .construction — Identity Digital Inc.
> The **.construction** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .consulting — Identity Digital Inc.
> The **.consulting** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .contact — Identity Digital Inc.
> The **.contact** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (12 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .contractors — Identity Digital Inc.
> The **.contractors** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cooking — GoDaddy Inc.
> The **.cooking** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (3 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cool — Identity Digital Inc.
> The **.cool** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .country — Tucows Registry Inc.
> The **.country** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .coupons — Identity Digital Inc.
> The **.coupons** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .courses — GoDaddy Inc.
> The **.courses** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .credit — Identity Digital Inc.
> The **.credit** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .creditcard — Identity Digital Inc.
> The **.creditcard** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cruises — Identity Digital Inc.
> The **.cruises** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cymru — Nominet UK
> The **.cymru** is a generic top-level domain (gTLD) operated by Nominet UK. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Nominet UK |
| Registry Country | United Kingdom |
| Registry Website | [www.nominet.uk](https://www.nominet.uk) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ❌ No |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–10 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ❌ No |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.cymru` |
| RDAP Server | [rdap.nominet.uk/cymru](https://rdap.nominet.uk/cymru/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .cyou — CentralNic Group PLC
> The **.cyou** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .dad — Charleston Road Registry Inc.
> The **.dad** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2023-04-02 – 2023-05-03) |
| Eap | ✅ Supported (2023-05-03 – 2023-05-10) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .dance — Identity Digital Inc.
> The **.dance** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .dating — Identity Digital Inc.
> The **.dating** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .day — Charleston Road Registry Inc.
> The **.day** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2022-10-04 – 2022-11-07) |
| Eap | ✅ Supported (2022-11-08 – 2022-11-15) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .de.com — CentralNic Group PLC
> The **.de.com** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .dealer — CentralNic Group PLC
> The **.dealer** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .deals — Identity Digital Inc.
> The **.deals** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .degree — Identity Digital Inc.
> The **.degree** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .delivery — Identity Digital Inc.
> The **.delivery** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .democrat — Identity Digital Inc.
> The **.democrat** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .dental — Identity Digital Inc.
> The **.dental** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .dentist — Identity Digital Inc.
> The **.dentist** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .design — GoDaddy Inc.
> The **.design** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (10 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .dev — Charleston Road Registry Inc.
> The **.dev** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2019-01-16 – 2019-02-19) |
| Eap | ✅ Supported (2019-02-19 – 2019-02-28) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .diamonds — Identity Digital Inc.
> The **.diamonds** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .diet — CentralNic Group PLC
> The **.diet** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .digital — Identity Digital Inc.
> The **.digital** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .direct — Identity Digital Inc.
> The **.direct** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .directory — Identity Digital Inc.
> The **.directory** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .discount — Identity Digital Inc.
> The **.discount** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .diy — Tucows Registry Inc.
> The **.diy** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .doctor — Identity Digital Inc.
> The **.doctor** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .dog — Identity Digital Inc.
> The **.dog** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .domains — Identity Digital Inc.
> The **.domains** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .education — Identity Digital Inc.
> The **.education** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .email — Identity Digital Inc.
> The **.email** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .energy — Identity Digital Inc.
> The **.energy** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .engineer — Identity Digital Inc.
> The **.engineer** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .engineering — Identity Digital Inc.
> The **.engineering** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .enterprises — Identity Digital Inc.
> The **.enterprises** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .equipment — Identity Digital Inc.
> The **.equipment** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .esq — Charleston Road Registry Inc.
> The **.esq** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2023-04-02 – 2023-05-03) |
| Eap | ✅ Supported (2023-05-03 – 2023-05-10) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .estate — Identity Digital Inc.
> The **.estate** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .eu.com — CentralNic Group PLC
> The **.eu.com** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .events — Identity Digital Inc.
> The **.events** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .exchange — Identity Digital Inc.
> The **.exchange** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .expert — Identity Digital Inc.
> The **.expert** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .exposed — Identity Digital Inc.
> The **.exposed** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .express — Identity Digital Inc.
> The **.express** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .fail — Identity Digital Inc.
> The **.fail** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .family — Identity Digital Inc.
> The **.family** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .fan — Identity Digital Inc.
> The **.fan** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .fans — CentralNic Group PLC
> The **.fans** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .farm — Identity Digital Inc.
> The **.farm** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .fashion — GoDaddy Inc.
> The **.fashion** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (4 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .finance — Identity Digital Inc.
> The **.finance** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .financial — Identity Digital Inc.
> The **.financial** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .fish — Identity Digital Inc.
> The **.fish** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .fishing — GoDaddy Inc.
> The **.fishing** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (3 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .fit — GoDaddy Inc.
> The **.fit** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (4 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .fitness — Identity Digital Inc.
> The **.fitness** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .flights — Identity Digital Inc.
> The **.flights** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .florist — Identity Digital Inc.
> The **.florist** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .flowers — CentralNic Group PLC
> The **.flowers** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .foo — Charleston Road Registry Inc.
> The **.foo** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2023-04-02 – 2023-05-03) |
| Eap | ✅ Supported (2023-05-03 – 2023-05-10) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .food — Tucows Registry Inc.
> The **.food** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .football — Identity Digital Inc.
> The **.football** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .forex — Identity Digital Inc.
> The **.forex** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .forsale — Identity Digital Inc.
> The **.forsale** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .foundation — Public Interest Registry
> The **.foundation** is a generic top-level domain (gTLD) operated by Public Interest Registry. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Public Interest Registry |
| Registry Country | United States |
| Registry Website | [pir.org](https://pir.org/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.foundation` |
| RDAP Server | [rdap.publicinterestregistry.org/rdap](https://rdap.publicinterestregistry.org/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | URS |
| Reference | [www.icann.org/urs-en](https://www.icann.org/urs-en) |
| UDRP Support | ❌ No |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .frl — CentralNic Group PLC
> The **.frl** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .fun — Tucows Registry Inc.
> The **.fun** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.radix.host` |
| RDAP Server | [rdap.radix.host/rdap](https://rdap.radix.host/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .fund — Identity Digital Inc.
> The **.fund** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .furniture — Identity Digital Inc.
> The **.furniture** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .futbol — Identity Digital Inc.
> The **.futbol** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .fyi — Identity Digital Inc.
> The **.fyi** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .gallery — Identity Digital Inc.
> The **.gallery** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .game — CentralNic Group PLC
> The **.game** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .games — Identity Digital Inc.
> The **.games** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .garden — GoDaddy Inc.
> The **.garden** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (3 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .gay — GoDaddy Inc.
> The **.gay** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (10 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .gb.net — CentralNic Group PLC
> The **.gb.net** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .gifts — Identity Digital Inc.
> The **.gifts** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .gives — Public Interest Registry
> The **.gives** is a generic top-level domain (gTLD) operated by Public Interest Registry. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Public Interest Registry |
| Registry Country | United States |
| Registry Website | [pir.org](https://pir.org/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.gives` |
| RDAP Server | [rdap.publicinterestregistry.org/rdap](https://rdap.publicinterestregistry.org/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | URS |
| Reference | [www.icann.org/urs-en](https://www.icann.org/urs-en) |
| UDRP Support | ❌ No |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .giving — Public Interest Registry
> The **.giving** is a generic top-level domain (gTLD) operated by Public Interest Registry. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Public Interest Registry |
| Registry Country | United States |
| Registry Website | [pir.org](https://pir.org/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.giving` |
| RDAP Server | [rdap.publicinterestregistry.org/rdap](https://rdap.publicinterestregistry.org/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | URS |
| Reference | [www.icann.org/urs-en](https://www.icann.org/urs-en) |
| UDRP Support | ❌ No |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .glass — Identity Digital Inc.
> The **.glass** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .global — Identity Digital Inc.
> The **.global** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (28 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .gmbh — Identity Digital Inc.
> The **.gmbh** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .gold — Identity Digital Inc.
> The **.gold** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .golf — Identity Digital Inc.
> The **.golf** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .gr.com — CentralNic Group PLC
> The **.gr.com** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .graphics — Identity Digital Inc.
> The **.graphics** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .gratis — Identity Digital Inc.
> The **.gratis** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .green — Identity Digital Inc.
> The **.green** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .gripe — Identity Digital Inc.
> The **.gripe** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .group — Identity Digital Inc.
> The **.group** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .guide — Identity Digital Inc.
> The **.guide** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .guitars — CentralNic Group PLC
> The **.guitars** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .guru — Identity Digital Inc.
> The **.guru** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .hair — CentralNic Group PLC
> The **.hair** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .hamburg — TLD-BOX Registrydienstleistungen GmbH
> The **.hamburg** is a generic top-level domain (gTLD) operated by TLD-BOX Registrydienstleistungen GmbH. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | TLD-BOX Registrydienstleistungen GmbH |
| Registry Country | Austria |
| Registry Website | [www.nic.at/en/tldbox](https://www.nic.at/en/tldbox) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ❌ No |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (2 tables) |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.hamburg` |
| RDAP Server | [rdap.nic.hamburg/v1](https://rdap.nic.hamburg/v1/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Local Presence
| Property | Value |
| --- | --- |
| Local Presence Required | ✅ Yes |
| Applies To Roles | Domain Owner, Administrator, Technical Contact |
| Requirements | Physical Address |
| Eligible Countries | Any |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .haus — Identity Digital Inc.
> The **.haus** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .health — GoDaddy Inc.
> The **.health** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .healthcare — Identity Digital Inc.
> The **.healthcare** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .help — CentralNic Group PLC
> The **.help** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .hiv — Tucows Registry Inc.
> The **.hiv** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .hockey — Identity Digital Inc.
> The **.hockey** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .holdings — Identity Digital Inc.
> The **.holdings** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .holiday — Identity Digital Inc.
> The **.holiday** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .homes — CentralNic Group PLC
> The **.homes** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .horse — GoDaddy Inc.
> The **.horse** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (3 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .hospital — Identity Digital Inc.
> The **.hospital** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .host — Tucows Registry Inc.
> The **.host** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.radix.host` |
| RDAP Server | [rdap.radix.host/rdap](https://rdap.radix.host/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .hosting — CentralNic Group PLC
> The **.hosting** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .house — Identity Digital Inc.
> The **.house** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .how — Charleston Road Registry Inc.
> The **.how** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2014-11-10 – 2015-01-09) |
| Landrush | ✅ Supported (2015-01-12 – 2015-01-26) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .hu.net — CentralNic Group PLC
> The **.hu.net** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .icu — CentralNic Group PLC
> The **.icu** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .immo — Identity Digital Inc.
> The **.immo** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .immobilien — Identity Digital Inc.
> The **.immobilien** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .inc — CentralNic Group PLC
> The **.inc** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .industries — Identity Digital Inc.
> The **.industries** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .info — Identity Digital Inc.
> The **.info** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .ing — Charleston Road Registry Inc.
> The **.ing** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2023-09-20 – 2023-10-24) |
| Eap | ✅ Supported (2023-10-31 – 2023-12-05) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .ink — GoDaddy Inc.
> The **.ink** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (10 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .institute — Identity Digital Inc.
> The **.institute** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .insure — Identity Digital Inc.
> The **.insure** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .international — Identity Digital Inc.
> The **.international** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .investments — Identity Digital Inc.
> The **.investments** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .irish — Identity Digital Inc.
> The **.irish** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .jetzt — Identity Digital Inc.
> The **.jetzt** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .jewelry — Identity Digital Inc.
> The **.jewelry** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .jp.net — CentralNic Group PLC
> The **.jp.net** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .jpn.com — CentralNic Group PLC
> The **.jpn.com** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .juegos — Identity Digital Inc.
> The **.juegos** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (8 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .kaufen — Identity Digital Inc.
> The **.kaufen** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .kim — Identity Digital Inc.
> The **.kim** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .kitchen — Identity Digital Inc.
> The **.kitchen** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .kred — CentralNic Group PLC
> The **.kred** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .land — Identity Digital Inc.
> The **.land** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .lat — CentralNic Group PLC
> The **.lat** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .latino — Tucows Registry Inc.
> The **.latino** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.latino` |
| RDAP Server | [rdap.mobile-registry.com/rdap](https://rdap.mobile-registry.com/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .law — GoDaddy Inc.
> The **.law** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (4 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .lawyer — Identity Digital Inc.
> The **.lawyer** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .lease — Identity Digital Inc.
> The **.lease** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .legal — Identity Digital Inc.
> The **.legal** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .lgbt — Identity Digital Inc.
> The **.lgbt** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .life — Identity Digital Inc.
> The **.life** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .lifestyle — Tucows Registry Inc.
> The **.lifestyle** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .lighting — Identity Digital Inc.
> The **.lighting** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .limited — Identity Digital Inc.
> The **.limited** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .limo — Identity Digital Inc.
> The **.limo** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .link — Tucows Registry Inc.
> The **.link** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .live — Identity Digital Inc.
> The **.live** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .living — Tucows Registry Inc.
> The **.living** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .llc — Identity Digital Inc.
> The **.llc** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .loans — Identity Digital Inc.
> The **.loans** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .lol — CentralNic Group PLC
> The **.lol** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .london — CentralNic Group PLC
> The **.london** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .lotto — Identity Digital Inc.
> The **.lotto** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .ltd — Identity Digital Inc.
> The **.ltd** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .luxe — GoDaddy Inc.
> The **.luxe** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (12 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .luxury — CentralNic Group PLC
> The **.luxury** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .maison — Identity Digital Inc.
> The **.maison** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .makeup — CentralNic Group PLC
> The **.makeup** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .management — Identity Digital Inc.
> The **.management** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .market — Identity Digital Inc.
> The **.market** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .marketing — Identity Digital Inc.
> The **.marketing** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .markets — Identity Digital Inc.
> The **.markets** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .mba — Identity Digital Inc.
> The **.mba** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .media — Identity Digital Inc.
> The **.media** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .meme — Charleston Road Registry Inc.
> The **.meme** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2023-09-20 – 2023-10-24) |
| Eap | ✅ Supported (2023-11-28 – 2023-12-05) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .memorial — Identity Digital Inc.
> The **.memorial** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .mex.com — CentralNic Group PLC
> The **.mex.com** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .miami — GoDaddy Inc.
> The **.miami** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (2 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .mobi — Identity Digital Inc.
> The **.mobi** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .mobile — Tucows Registry Inc.
> The **.mobile** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.mobile` |
| RDAP Server | [rdap.mobile-registry.com/rdap](https://rdap.mobile-registry.com/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .moda — Identity Digital Inc.
> The **.moda** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .mom — CentralNic Group PLC
> The **.mom** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .money — Identity Digital Inc.
> The **.money** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .monster — CentralNic Group PLC
> The **.monster** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .mortgage — Identity Digital Inc.
> The **.mortgage** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .motorcycles — CentralNic Group PLC
> The **.motorcycles** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .mov — Charleston Road Registry Inc.
> The **.mov** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2023-04-02 – 2023-05-03) |
| Eap | ✅ Supported (2023-05-03 – 2023-05-10) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .movie — Identity Digital Inc.
> The **.movie** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .music — Tucows Registry Inc.
> The **.music** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.music` |
| RDAP Server | [rdap.registryservices.music/rdap](https://rdap.registryservices.music/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .name — VeriSign, Inc.
> The **.name** is a generic top-level domain (gTLD) operated by VeriSign, Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | VeriSign, Inc. |
| Registry Country | United States |
| Registry Website | [www.verisign.com](https://www.verisign.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ✅ Yes (103 tables) |
| Premium Domains | ❌ No |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.name` |
| RDAP Server | [tld-rdap.verisign.com/name/v1](https://tld-rdap.verisign.com/name/v1/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .navy — Identity Digital Inc.
> The **.navy** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .net — VeriSign, Inc.
> The **.net** is a generic top-level domain (gTLD) operated by VeriSign, Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | VeriSign, Inc. |
| Registry Country | United States |
| Registry Website | [www.verisign.com](https://www.verisign.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (97 tables) |
| Premium Domains | ❌ No |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.verisign-grs.com` |
| RDAP Server | [rdap.verisign.com/net/v1](https://rdap.verisign.com/net/v1/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .network — Identity Digital Inc.
> The **.network** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .new — Charleston Road Registry Inc.
> The **.new** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2019-10-15 – 2020-01-14) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ❌ No |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .news — Identity Digital Inc.
> The **.news** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .nexus — Charleston Road Registry Inc.
> The **.nexus** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2023-04-02 – 2023-05-03) |
| Eap | ✅ Supported (2023-05-03 – 2023-05-10) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .ngo — Public Interest Registry
> The **.ngo** is a generic top-level domain (gTLD) operated by Public Interest Registry. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Public Interest Registry |
| Registry Country | United States |
| Registry Website | [pir.org](https://pir.org/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ✅ Yes (20 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.ngo` |
| RDAP Server | [rdap.publicinterestregistry.org/rdap](https://rdap.publicinterestregistry.org/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | URS |
| Reference | [www.icann.org/urs-en](https://www.icann.org/urs-en) |
| UDRP Support | ❌ No |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .ninja — Identity Digital Inc.
> The **.ninja** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .nrw — Minds + Machines GmbH
> The **.nrw** is a generic top-level domain (gTLD) operated by Minds + Machines GmbH. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Minds + Machines GmbH |
| Registry Country | Germany |
| Registry Website | [domains.nrw](https://domains.nrw) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | On expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (4–89 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–12 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DNSKEY |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.nrw` |
| RDAP Server | [rdap.nic.nrw](https://rdap.nic.nrw/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Local Presence
| Property | Value |
| --- | --- |
| Local Presence Required | ✅ Yes |
| Applies To Roles | Domain Owner |
| Requirements | Physical Address |
| Eligible Countries | DE |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .ong — Public Interest Registry
> The **.ong** is a generic top-level domain (gTLD) operated by Public Interest Registry. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Public Interest Registry |
| Registry Country | United States |
| Registry Website | [pir.org](https://pir.org/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ✅ Yes (20 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.ong` |
| RDAP Server | [rdap.publicinterestregistry.org/rdap](https://rdap.publicinterestregistry.org/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | URS |
| Reference | [www.icann.org/urs-en](https://www.icann.org/urs-en) |
| UDRP Support | ❌ No |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .online — Tucows Registry Inc.
> The **.online** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.radix.host` |
| RDAP Server | [rdap.radix.host/rdap](https://rdap.radix.host/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .ooo — CentralNic Group PLC
> The **.ooo** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .org — Public Interest Registry
> The **.org** is a generic top-level domain (gTLD) operated by Public Interest Registry. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Public Interest Registry |
| Registry Country | United States |
| Registry Website | [pir.org](https://pir.org/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 2–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ❌ No |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.publicinterestregistry.org` |
| RDAP Server | [rdap.publicinterestregistry.org/rdap](https://rdap.publicinterestregistry.org/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .organic — Identity Digital Inc.
> The **.organic** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .page — Charleston Road Registry Inc.
> The **.page** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2018-03-29 – 2018-05-01) |
| Eap | ✅ Supported (2018-05-01 – 2018-05-08) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .partners — Identity Digital Inc.
> The **.partners** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .parts — Identity Digital Inc.
> The **.parts** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .pet — Identity Digital Inc.
> The **.pet** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .phd — Charleston Road Registry Inc.
> The **.phd** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2023-04-02 – 2023-05-03) |
| Eap | ✅ Supported (2023-05-03 – 2023-05-10) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .photo — GoDaddy Inc.
> The **.photo** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (8 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .photography — Identity Digital Inc.
> The **.photography** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .photos — Identity Digital Inc.
> The **.photos** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .pics — CentralNic Group PLC
> The **.pics** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .pictures — Identity Digital Inc.
> The **.pictures** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .pink — Identity Digital Inc.
> The **.pink** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .pizza — Identity Digital Inc.
> The **.pizza** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .place — Identity Digital Inc.
> The **.place** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .plumbing — Identity Digital Inc.
> The **.plumbing** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .plus — Identity Digital Inc.
> The **.plus** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .poker — Identity Digital Inc.
> The **.poker** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .press — Tucows Registry Inc.
> The **.press** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.radix.host` |
| RDAP Server | [rdap.radix.host/rdap](https://rdap.radix.host/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .pro — Identity Digital Inc.
> The **.pro** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .productions — Identity Digital Inc.
> The **.productions** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .prof — Charleston Road Registry Inc.
> The **.prof** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2023-04-02 – 2023-05-03) |
| Eap | ✅ Supported (2023-05-03 – 2023-05-10) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .promo — Identity Digital Inc.
> The **.promo** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .properties — Identity Digital Inc.
> The **.properties** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .protection — CentralNic Group PLC
> The **.protection** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .pub — Identity Digital Inc.
> The **.pub** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .qpon — CentralNic Group PLC
> The **.qpon** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .quest — CentralNic Group PLC
> The **.quest** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .recipes — Identity Digital Inc.
> The **.recipes** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .red — Identity Digital Inc.
> The **.red** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .rehab — Identity Digital Inc.
> The **.rehab** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .reise — Identity Digital Inc.
> The **.reise** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .reisen — Identity Digital Inc.
> The **.reisen** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .reit — CentralNic Group PLC
> The **.reit** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .rent — CentralNic Group PLC
> The **.rent** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .rentals — Identity Digital Inc.
> The **.rentals** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .repair — Identity Digital Inc.
> The **.repair** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .report — Identity Digital Inc.
> The **.report** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .republican — Identity Digital Inc.
> The **.republican** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .restaurant — Identity Digital Inc.
> The **.restaurant** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .reviews — Identity Digital Inc.
> The **.reviews** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .rip — Identity Digital Inc.
> The **.rip** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .rocks — Identity Digital Inc.
> The **.rocks** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .rodeo — GoDaddy Inc.
> The **.rodeo** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (3 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .rsvp — Charleston Road Registry Inc.
> The **.rsvp** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2022-10-04 – 2022-11-07) |
| Eap | ✅ Supported (2022-11-08 – 2022-11-15) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .ru.com — CentralNic Group PLC
> The **.ru.com** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .run — Identity Digital Inc.
> The **.run** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .sa.com — CentralNic Group PLC
> The **.sa.com** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .saarland — CentralNic Group PLC
> The **.saarland** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .sale — Identity Digital Inc.
> The **.sale** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .salon — Identity Digital Inc.
> The **.salon** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .sarl — Identity Digital Inc.
> The **.sarl** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .sbs — CentralNic Group PLC
> The **.sbs** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .school — Identity Digital Inc.
> The **.school** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .schule — Identity Digital Inc.
> The **.schule** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .se.net — CentralNic Group PLC
> The **.se.net** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .security — CentralNic Group PLC
> The **.security** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .select — GoDaddy Inc.
> The **.select** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .services — Identity Digital Inc.
> The **.services** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .sexy — Tucows Registry Inc.
> The **.sexy** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .shiksha — Identity Digital Inc.
> The **.shiksha** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .shoes — Identity Digital Inc.
> The **.shoes** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .shop — GMO Registry, Inc.
> The **.shop** is a generic top-level domain (gTLD) operated by GMO Registry, Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GMO Registry, Inc. |
| Registry Country | Japan |
| Registry Website | [www.gmoregistry.com/en](https://www.gmoregistry.com/en/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 2–63 characters |
| IDN Support | ✅ Yes (13 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.shop` |
| RDAP Server | [rdap.gmoregistry.net/rdap](https://rdap.gmoregistry.net/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .shopping — Identity Digital Inc.
> The **.shopping** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .show — Identity Digital Inc.
> The **.show** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .singles — Identity Digital Inc.
> The **.singles** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .site — Tucows Registry Inc.
> The **.site** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.radix.host` |
| RDAP Server | [rdap.radix.host/rdap](https://rdap.radix.host/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .ski — Identity Digital Inc.
> The **.ski** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .skin — CentralNic Group PLC
> The **.skin** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .soccer — Identity Digital Inc.
> The **.soccer** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .social — Identity Digital Inc.
> The **.social** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .software — Identity Digital Inc.
> The **.software** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .solar — Identity Digital Inc.
> The **.solar** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .solutions — Identity Digital Inc.
> The **.solutions** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .soy — Charleston Road Registry Inc.
> The **.soy** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2014-07-24 – 2014-09-24) |
| Landrush | ✅ Supported (2014-09-24 – 2014-10-08) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .space — Tucows Registry Inc.
> The **.space** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.radix.host` |
| RDAP Server | [rdap.radix.host/rdap](https://rdap.radix.host/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .storage — CentralNic Group PLC
> The **.storage** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .store — Tucows Registry Inc.
> The **.store** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.radix.host` |
| RDAP Server | [rdap.radix.host/rdap](https://rdap.radix.host/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .studio — Identity Digital Inc.
> The **.studio** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .study — GoDaddy Inc.
> The **.study** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .style — Identity Digital Inc.
> The **.style** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .supplies — Identity Digital Inc.
> The **.supplies** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .supply — Identity Digital Inc.
> The **.supply** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .support — Identity Digital Inc.
> The **.support** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .surf — GoDaddy Inc.
> The **.surf** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (3 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .surgery — Identity Digital Inc.
> The **.surgery** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .systems — Identity Digital Inc.
> The **.systems** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .tattoo — GoDaddy Inc.
> The **.tattoo** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .tax — Identity Digital Inc.
> The **.tax** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .taxi — Identity Digital Inc.
> The **.taxi** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .team — Identity Digital Inc.
> The **.team** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .tech — Tucows Registry Inc.
> The **.tech** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.radix.host` |
| RDAP Server | [rdap.radix.host/rdap](https://rdap.radix.host/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .technology — Identity Digital Inc.
> The **.technology** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .tennis — Identity Digital Inc.
> The **.tennis** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .theater — Identity Digital Inc.
> The **.theater** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .theatre — CentralNic Group PLC
> The **.theatre** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .tickets — CentralNic Group PLC
> The **.tickets** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .tienda — Identity Digital Inc.
> The **.tienda** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .tips — Identity Digital Inc.
> The **.tips** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .tires — Identity Digital Inc.
> The **.tires** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .today — Identity Digital Inc.
> The **.today** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .tools — Identity Digital Inc.
> The **.tools** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .tours — Identity Digital Inc.
> The **.tours** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .town — Identity Digital Inc.
> The **.town** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .toys — Identity Digital Inc.
> The **.toys** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .trading — Identity Digital Inc.
> The **.trading** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .training — Identity Digital Inc.
> The **.training** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .travel — Identity Digital Inc.
> The **.travel** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .uk.com — CentralNic Group PLC
> The **.uk.com** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .uk.net — CentralNic Group PLC
> The **.uk.net** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .university — Identity Digital Inc.
> The **.university** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .uno — Tucows Registry Inc.
> The **.uno** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.radix.host` |
| RDAP Server | [rdap.radix.host/rdap](https://rdap.radix.host/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .us.com — CentralNic Group PLC
> The **.us.com** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .us.org — CentralNic Group PLC
> The **.us.org** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .vacations — Identity Digital Inc.
> The **.vacations** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .vegas — Identity Digital Inc.
> The **.vegas** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .ventures — Identity Digital Inc.
> The **.ventures** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .vet — Identity Digital Inc.
> The **.vet** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .viajes — Identity Digital Inc.
> The **.viajes** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .video — Identity Digital Inc.
> The **.video** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .villas — Identity Digital Inc.
> The **.villas** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .vin — Identity Digital Inc.
> The **.vin** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .vip — GoDaddy Inc.
> The **.vip** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (12 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .vision — Identity Digital Inc.
> The **.vision** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .vlaanderen — DNS Belgium
> The **.vlaanderen** is a generic top-level domain (gTLD) operated by DNS Belgium. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | DNS Belgium |
| Registry Country | Belgium |
| Registry Website | [www.dnsbelgium.be](https://www.dnsbelgium.be) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 2–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ❌ No |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| RDAP Server | [rdap.nic.vlaanderen](https://rdap.nic.vlaanderen/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .vodka — GoDaddy Inc.
> The **.vodka** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (3 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .vote — Identity Digital Inc.
> The **.vote** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .voto — Identity Digital Inc.
> The **.voto** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (26 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .voyage — Identity Digital Inc.
> The **.voyage** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .wales — Nominet UK
> The **.wales** is a generic top-level domain (gTLD) operated by Nominet UK. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Nominet UK |
| Registry Country | United Kingdom |
| Registry Website | [www.nominet.uk](https://www.nominet.uk) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ❌ No |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ❌ No |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–10 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 0 days |
| Transfer Extends Domain | ❌ No |
| Transfer via AuthInfo | ❌ No |
| Confirmation Required | ✅ Yes (registrar) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.wales` |
| RDAP Server | [rdap.nominet.uk/wales](https://rdap.nominet.uk/wales/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .watch — Identity Digital Inc.
> The **.watch** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .watches — Identity Digital Inc.
> The **.watches** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (16 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .website — Tucows Registry Inc.
> The **.website** is a generic top-level domain (gTLD) operated by Tucows Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Tucows Registry Inc. |
| Registry Country | Canada |
| Registry Website | [www.tucowsregistry.com](https://www.tucowsregistry.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 1 day before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.radix.host` |
| RDAP Server | [rdap.radix.host/rdap](https://rdap.radix.host/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .wedding — GoDaddy Inc.
> The **.wedding** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (4 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .wiki — GoDaddy Inc.
> The **.wiki** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (10 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .wine — Identity Digital Inc.
> The **.wine** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .work — GoDaddy Inc.
> The **.work** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (4 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .works — Identity Digital Inc.
> The **.works** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .world — Identity Digital Inc.
> The **.world** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .wtf — Identity Digital Inc.
> The **.wtf** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .xn--c1avg — Public Interest Registry
> The **.xn--c1avg** is a generic top-level domain (gTLD) operated by Public Interest Registry. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Public Interest Registry |
| Registry Country | United States |
| Registry Website | [pir.org](https://pir.org/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ✅ Yes (8 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.xn--c1avg` |
| RDAP Server | [rdap.publicinterestregistry.org/rdap](https://rdap.publicinterestregistry.org/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | URS |
| Reference | [www.icann.org/urs-en](https://www.icann.org/urs-en) |
| UDRP Support | ❌ No |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .xn--i1b6b1a6a2e — Public Interest Registry
> The **.xn--i1b6b1a6a2e** is a generic top-level domain (gTLD) operated by Public Interest Registry. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Public Interest Registry |
| Registry Country | United States |
| Registry Website | [pir.org](https://pir.org/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ✅ Yes (1 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.xn--i1b6b1a6a2e` |
| RDAP Server | [rdap.publicinterestregistry.org/rdap](https://rdap.publicinterestregistry.org/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | URS |
| Reference | [www.icann.org/urs-en](https://www.icann.org/urs-en) |
| UDRP Support | ❌ No |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .xn--mgbcpq6gpa1a — Telecommunications Regulatory Authority (TRA)
> The **.xn--mgbcpq6gpa1a** is a generic top-level domain (gTLD) operated by Telecommunications Regulatory Authority (TRA). This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Telecommunications Regulatory Authority (TRA) |
| Registry Country | Bahrain |
| Registry Website | [domains.bh](https://domains.bh/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–5 years |
| Renewal Period | 1–5 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.bhregistry.bh` |
| RDAP Server | [rdap.bhregistry.bh/rdap](https://rdap.bhregistry.bh/rdap) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .xn--nqv7f — Public Interest Registry
> The **.xn--nqv7f** is a generic top-level domain (gTLD) operated by Public Interest Registry. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Public Interest Registry |
| Registry Country | United States |
| Registry Website | [pir.org](https://pir.org/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–63 characters |
| IDN Support | ✅ Yes (2 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.nic.xn--nqv7f` |
| RDAP Server | [rdap.publicinterestregistry.org/rdap](https://rdap.publicinterestregistry.org/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | URS |
| Reference | [www.icann.org/urs-en](https://www.icann.org/urs-en) |
| UDRP Support | ❌ No |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .xn--q9jyb4c — Charleston Road Registry Inc.
> The **.xn--q9jyb4c** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2013-12-09 – 2014-02-26) |
| Landrush | ✅ Supported (2014-01-15 – 2014-02-26) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 3–15 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .xyz — CentralNic Group PLC
> The **.xyz** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .yachts — CentralNic Group PLC
> The **.yachts** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ❌ No |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .yoga — GoDaddy Inc.
> The **.yoga** is a generic top-level domain (gTLD) operated by GoDaddy Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | GoDaddy Inc. |
| Registry Country | United States |
| Registry Website | [registry.godaddy](https://registry.godaddy/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (4 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner |
| Supported Roles | Domain Owner, Technical Contact, Administrator, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ❌ No |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.godaddy.com` |
| RDAP Server | [rdap.godaddy.com](https://rdap.godaddy.com) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ❌ No |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .za.com — CentralNic Group PLC
> The **.za.com** is a generic top-level domain (gTLD) operated by CentralNic Group PLC. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | CentralNic Group PLC |
| Registry Country | United Kingdom |
| Registry Website | [www.centralnic.com](https://www.centralnic.com) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 5 days |
| Redemption Period | 30 days |
| Pending Restore | 7 days |
| Pending Delete | 0 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ❌ No |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact, Billing Contact |
| Thick WHOIS | ✅ Yes |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ✅ Yes |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.centralnic.com` |
| RDAP Server | [rdap.centralnic.com](https://rdap.centralnic.com/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .zip — Charleston Road Registry Inc.
> The **.zip** is a generic top-level domain (gTLD) operated by Charleston Road Registry Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Charleston Road Registry Inc. |
| Registry Country | United States |
| Registry Website | [registry.google](https://registry.google/) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ✅ Yes |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 0 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| Sunrise | ✅ Supported (2023-04-02 – 2023-05-03) |
| Eap | ✅ Supported (2023-05-03 – 2023-05-10) |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ✅ Yes |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes |
| Premium Domains | ✅ Yes |
| Reserved Domains | ✅ Yes |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ❌ No |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (12–63 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (0 days after registration; 0 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.registry.google` |
| RDAP Server | [rdap.registry.google](https://rdap.registry.google/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# 🌐 .zone — Identity Digital Inc.
> The **.zone** is a generic top-level domain (gTLD) operated by Identity Digital Inc.. This article documents the technical, operational, and contractual requirements for the TLD, along with special considerations for registry, registrar, and domain management.
## General Information
| Property | Value |
| --- | --- |
| TLD Type | gTLD |
| Registry | Identity Digital Inc. |
| Registry Country | United States |
| Registry Website | [www.identity.digital](https://www.identity.digital) |
| Provisioning Protocol | EPP |
| Second-Level Registration | ❌ No |
| Accreditation Required | ✅ Yes |
## Domain Lifecycle
| Property | Value |
| --- | --- |
| Registration Period | 1–10 years |
| Renewal Period | 1–10 years |
| Transfer Renewal Period | 1 year |
| Deletion Policy | Immediate, At expiration |
| Auto-Renew Enabled | ✅ Yes |
| Auto-Renewal Before Expiry | 7 days before expiration |
| Sync After Operations | registration, renewal, transfer |
**Grace periods**
| Period | Duration |
| --- | --- |
| Add Grace Period | 5 days |
| Standard Grace Period | 45 days |
| Redemption Period | 30 days |
| Pending Restore | 5 days |
| Pending Delete | 5 days |
## Launch Phases & Availability
| Property | Value |
| --- | --- |
| General Availability | ✅ TLD is live |
| TMCH / Trademark Claims | ❌ No |
## Domain Characteristics
| Property | Value |
| --- | --- |
| Domain Length | 1–63 characters |
| IDN Support | ✅ Yes (14 tables) |
| Premium Domains | ✅ Yes |
| Reserved Domains | ❌ No |
| Registry Lock | ✅ Yes |
## Contacts & Roles
| Property | Value |
| --- | --- |
| Required Contacts | Domain Owner, Administrator, Technical Contact |
| Supported Roles | Domain Owner, Administrator, Technical Contact |
| Thick WHOIS | ❌ No |
| Privacy Proxy Allowed | ✅ Yes |
| Contacts Transferable | ❌ No |
| Allowed Postal Types | Local, International |
| AuthInfo Required | ✅ Yes (8–32 characters) |
## Nameservers & DNS
| Property | Value |
| --- | --- |
| Nameserver Count | 0–13 |
| Host Objects Allowed | ✅ Yes |
| Registry Nameserver Check | ❌ No |
| DNSSEC Allowed | ✅ Yes |
| DNSSEC Required | ❌ No |
| DNSSEC Mode | DS |
| CZDS (Zone Download) | ✅ Yes |
## Transfer Policy
| Property | Value |
| --- | --- |
| Transfer Lock Enabled | ✅ Yes (60 days after registration; 60 days after transfer) |
| Transfer Duration | 5 days |
| Transfer Extends Domain | ✅ Yes (+1 year) |
| Transfer via AuthInfo | ✅ Yes |
| Confirmation Required | ✅ Yes (Both parties) |
## WHOIS & RDAP
| Property | Value |
| --- | --- |
| WHOIS Server | `whois.identitydigital.services` |
| RDAP Server | [rdap.identitydigital.services/rdap](https://rdap.identitydigital.services/rdap/) |
## Dispute Resolution
| Property | Value |
| --- | --- |
| Dispute Resolution Available | ✅ Yes |
| Procedure | UDRP |
| Reference | [www.icann.org/resources/pages/help/dndr/udrp-en](https://www.icann.org/resources/pages/help/dndr/udrp-en) |
| UDRP Support | ✅ Yes |
| URS Support | ✅ Yes |
## Implementation Notes
- Ensure complete TLS/SSL configuration for every registry environment.
- Enable DNSSEC wherever the registry supports it.
- Make sure AuthInfo/transfer secrets meet the registry's length and format requirements.
- Review the registry's supported domain statuses and dispute-resolution policies before launch.
# OpusDNS MCP server
The OpusDNS MCP server is a remote [Model Context Protocol](https://modelcontextprotocol.io) server that exposes the OpusDNS Domain API to AI clients. It is hosted by OpusDNS — there is nothing to install and no server to run. Point any MCP client that speaks remote Streamable HTTP at the endpoint, sign in with your OpusDNS account, and the client gets nine tools that cover the whole API.
New here? The [Quickstart](/mcp-server/quickstart) gets you from nothing to an approved change in about ten minutes. Building unattended automation instead? Read [MCP or the REST API?](/mcp-server/mcp-or-api) first.
## Try asking
Once your client is connected, you talk to it in your own words — the model picks the tools. A few that exercise each family:
* _"How many domains do I have, and what is expiring in the next 90 days?"_
* _"Which of my .com domains expire in the next 30 days? Just the names and dates."_
* _"Lock transfers on everything tagged migration."_
* _"Renew acme-labs.com for a year."_
* _"Turn off auto-renew on every .io that expires this quarter."_
* _"Batch batch\_01k3n0m5xrf9pab6t2wqzhkvr3 has failures — retry only the ones that ran out of funds."_
The first two answer straight away. The rest write, so each one stops and asks you to approve it before anything reaches the OpusDNS API — and the bulk ones show you how many domains matched before you decide.
## Endpoints
| Environment | MCP endpoint |
| ----------- | --------------------------------- |
| Production | `https://api.opusdns.com/mcp` |
| Sandbox | `https://sandbox.opusdns.com/mcp` |
The MCP endpoint lives on the API host: `https://api.opusdns.com/mcp`. There is no `mcp.opusdns.com` — that hostname does not resolve.
The sandbox is a separate account and a separate identity realm, free and fully isolated from production. Use it to try the tools out.
## What you get: nine tools
**Discovery** — every operation in the OpusDNS API is reachable through three tools, so the client's context holds three tool definitions instead of hundreds.
| Tool | Purpose |
| -------------------- | ----------------------------------------------------- |
| `search_operations` | Relevance-ranked search of the API catalog |
| `describe_operation` | Parameters, request body and safety for one operation |
| `call_operation` | Call one operation |
**Bulk** — multi-domain mutations run through [OpusDNS Jobs](/automation/jobs/overview), never a loop.
| Tool | Purpose |
| ------------------- | -------------------------------------------------------------- |
| `bulk_preview` | Resolve a selector and show the planned batch. Submits nothing |
| `bulk_submit` | Submit the batch, after you approve it |
| `job_batch_status` | Progress and per-state job counts |
| `job_batch_control` | Pause, resume, retry or cancel a batch |
**Portfolio** — compact reads that stay small on large accounts.
| Tool | Purpose |
| ------------------- | ---------------------------------------------------- |
| `portfolio_summary` | Totals and breakdowns by status, TLD and expiry |
| `portfolio_query` | List domains, projecting only the fields you ask for |
Full parameter reference: [Tools reference](/mcp-server/tools). Worked examples: [Tool workflows](/mcp-server/tool-workflows).
## Approvals
Anything that is not a read — every write, every cost-bearing operation, every deletion or transfer — is blocked before any request reaches the OpusDNS API and requires your explicit approval.
Approval is enforced by the server, not by instructions to the model. A model cannot talk its way past the gate, and the approval is bound to the exact action — including the exact resolved list of domains for a bulk operation. See [Approvals and confirmations](/mcp-server/approvals).
## Limits
| Limit | Value |
| ------------------------------------------------- | -------------------------------------------------------------- |
| Approval lifetime | About 5 minutes, single use |
| Domains one bulk selector may resolve to | 1,000 |
| `portfolio_query` page size | 200 maximum |
| Concurrent in-flight requests per server instance | 32; above that, `503` with `Retry-After: 1` |
| API response size per tool call | 512 KiB; larger responses come back marked `"truncated": true` |
| Upstream API timeout | 10 seconds |
| Tool-list freshness hint | 15 minutes |
Defaults, where you do not say otherwise:
| Default | Value |
| ---------------------------------- | ------------------- |
| `search_operations` results | 25 |
| `portfolio_query` page / page size | page 1, 50 rows |
| `bulk_preview` sample size | 10 resolved domains |
The 1,000-domain limit is the Jobs API's cap on instances in a single bulk command, and a batch built from a selector is one command. To change more than 1,000 domains, narrow the selector and submit more than one batch — for example one TLD at a time.
## Protocol
* MCP protocol revision `2026-07-28`, negotiating down to earlier revisions for clients that do not speak it.
* Transport: Streamable HTTP. Not SSE-only, not stdio.
* Server identity: `opusdns-mcp`.
* Capabilities: tools only. No prompts, no resources, no sampling.
* **Stateless.** No session is established, so `Mcp-Session-Id` is not required and should not be relied on.
## Next
* [Quickstart](/mcp-server/quickstart) — connected, asking and approving in ten minutes
* [Connect your client](/mcp-server/connect) — Claude, Cursor, VS Code, ChatGPT
* [Recipes](/mcp-server/recipes) — worked examples for the jobs people actually do
* [Tool workflows](/mcp-server/tool-workflows) — one worked example per tool family
* [Sub-organizations](/mcp-server/sub-organizations) — acting on an organization below your own
* [Bulk operations with Jobs](/mcp-server/bulk-operations)
* [Results and errors](/mcp-server/results) — every shape a tool can return
* [Data handling](/mcp-server/data-handling) — what the agent sees and where it goes
* [API Quickstart](/introduction/quickstart) — the same operations over plain HTTP with an API key
* [API Reference](/api-reference) — every endpoint the tools can reach
# Quickstart
Connect a client, ask a question, make a change. About ten minutes, most of it read-only.
This walkthrough uses **production** (`https://api.opusdns.com/mcp`) — the endpoint you will keep using. Steps 1–3 only read and preview; nothing changes until you approve step 4. If you would rather rehearse against throwaway domains first, there is a free sandbox — see step 5.
## Before you start
* An OpusDNS account.
* An MCP client that speaks remote Streamable HTTP. This page uses Claude Code because it is a single command; every other client is on [Connect your client](/mcp-server/connect).
You do **not** need an API key. The MCP endpoint authenticates with OAuth in your browser and rejects API keys.
## 1. Add the server
```bash
claude mcp add --transport http opusdns https://api.opusdns.com/mcp
```
Then run `/mcp` inside Claude Code, pick **opusdns**, and complete the sign-in that opens in your browser. There is nothing to paste back.
Check it worked:
```bash
claude mcp list
```
The server should be listed as connected. If it is not, the symptom is almost certainly in [Troubleshooting](/mcp-server/troubleshooting#connecting).
## 2. Ask a read question
Read questions answer straight away — nothing to approve, because nothing changes.
> _"How many domains do I have, and what is expiring in the next 90 days?"_
The model calls `portfolio_summary`, which takes no arguments and returns one small object:
```json
{
"status": "ok",
"operationId": "get_domain_summary_v1_domains_summary_get",
"httpStatus": 200,
"data": {
"domains": {
"total_count": 28,
"by_tld": { "com": 7, "de": 8, "net": 4, "org": 5, "io": 4 },
"expiring_soon": { "next_30_days": 6, "next_60_days": 9, "next_90_days": 11 }
}
},
"truncated": false
}
```
That single call is why the tools stay usable on a large portfolio: the answer is a summary, not a list of every domain.
## 3. Preview a change
Now a change. Ask for something narrow:
> _"Show me what would happen if I turned off auto-renew on every .io domain."_
The model calls `bulk_preview`. It resolves the selector against your portfolio server-side and shows you the plan — it submits nothing and asks for no approval:
```json
{
"templateType": "domain_update_bulk",
"template": { "renewal_mode": "expire" },
"selector": { "tld": ["io"] },
"sampleSize": 3
}
```
The reply's `matchedDomains` is the number that matters. **Read it before you approve anything** — it is the difference between changing four domains and changing four thousand.
## 4. Approve the change
This step changes live domains. Check `matchedDomains` from step 3 first, and keep the selector narrow. To rehearse the write itself against throwaway domains, run the same steps against the sandbox — step 5.
> _"Yes, do it."_
The model calls `bulk_submit` with the same arguments. This one writes, so it stops and asks you first. Depending on your client you either get an approval prompt in the client itself, or a `confirmation_required` payload the model relays to you; both are described in [Approvals and confirmations](/mcp-server/approvals).
The prompt names the command, the count and the filters:
```plaintext
Approve: domain_update_bulk on 4 domain(s) matching tld=["io"] (POST /v1/jobs)? Risk: writes data.
```
Approve it, and the answer carries a `batch_id`:
```json
{
"status": "ok",
"operationId": "create_batch_v1_jobs_post",
"httpStatus": 201,
"data": { "batch_id": "batch_01k3n0m5xrf9pab6t2wqzhkvr3", "jobs_created": 4 },
"truncated": false
}
```
Ask _"is that batch done?"_ and the model calls `job_batch_status` with that id.
## 5. Optional: the sandbox
If you want to try writes without touching live domains, the sandbox runs the same nine tools against a free, fully isolated account. Same client, one different URL:
```bash
claude mcp add --transport http opusdns-sandbox https://sandbox.opusdns.com/mcp
```
It is a separate account and a separate sign-in, so its domains and your production domains never see each other. You can keep both connected at once — give them distinct names, as above. See [Adding the sandbox alongside production](/mcp-server/connect#adding-the-sandbox-alongside-production).
## What just happened
* You never typed a domain name. The **selector** described the set, and the server resolved it against your portfolio.
* The change went out as **one Jobs batch**, not as a loop of single calls.
* Nothing ran before you approved it, and the approval was bound to the exact set of domains the preview matched. If that set changes, you are asked again.
* The batch outlives the conversation. Closing the client neither pauses nor cancels it.
## Next
* [Recipes](/mcp-server/recipes) — worked examples for the jobs people actually do
* [Approvals and confirmations](/mcp-server/approvals) — what is gated and why
* [Bulk operations with Jobs](/mcp-server/bulk-operations) — selectors, templates and limits in full
* [Results and errors](/mcp-server/results) — what every tool hands back
# MCP or the REST API?
Both reach the same registrar. They differ in who is driving.
| Use the MCP server when | Use the REST API when |
| --- | --- |
| A person is in the loop and reads the answers | Nothing is watching, and nothing may stop to ask |
| The work is exploratory — "what is expiring", "which of these are locked" | The work is defined in advance and repeats |
| The shape of the task changes as you learn | The shape is fixed and encoded in your code |
| You want one-off portfolio changes with an explicit approval | You are building a pipeline, a cron job, or an event handler |
| You are asking in words | You are calling in code |
The approval gate on the MCP server cannot be turned off. That is a feature for
interactive work and a blocker for unattended automation — a nightly job that
hits an approval prompt simply stops. Automate against the API.
## What is the same
- **The same operations.** Every OpusDNS API endpoint is reachable through
`call_operation`; the bulk tools submit the same
[Jobs](/automation/jobs/overview) batches you would `POST /v1/jobs` yourself.
- **The same permissions.** Authorization is decided by your account's roles.
Connecting over MCP grants nothing your account did not already have.
- **The same limits.** Jobs caps a command at 1,000 instances either way.
- **The same request IDs.** `x-server-request-id` identifies a request for
support regardless of how it arrived.
## What is different
| | MCP server | REST API |
| --- | --- | --- |
| Credential | OAuth in a browser, no key to store | An API key you create and store |
| Approval | Server-enforced on every write | None — your code is responsible |
| Discovery | `search_operations` over the catalog | [API Reference](/api-reference) |
| Result size | Capped and projected to fit a model's context | Whatever the endpoint returns |
| Who sees the data | Your AI client and its model provider | Only your systems |
That last row is the one worth thinking about before connecting a production
account. [Data handling](/mcp-server/data-handling) spells out what does and
does not leave OpusDNS.
## Using both
The common shape is an agent that explores and a script that executes: ask over
MCP to work out *which* domains and *what* change, then encode the result as a
Jobs batch in your own code once the answer stops changing. The selector you
converged on in conversation is the same filter set `GET /v1/domains` takes.
## Next
- [Quickstart](/mcp-server/quickstart) — the MCP path, end to end
- [API Quickstart](/introduction/quickstart) — the same operations over HTTP
- [Bulk operations with Jobs](/mcp-server/bulk-operations)
# Connect Claude and Claude Code
Everything you need for either client:
* **URL** — `https://api.opusdns.com/mcp` (sandbox: `https://sandbox.opusdns.com/mcp`)
* **Transport** — remote Streamable HTTP
* **Authentication** — OAuth 2.1 in the browser. No API key, no token to paste.
You do not create a credential for the MCP server. The client registers itself with the OpusDNS identity provider automatically and then opens a browser for you to sign in. The API keys described in [Authentication](/introduction/authentication) are for direct API calls and are **not** accepted by the MCP endpoint.
## Claude Code
Add the server:
```bash
claude mcp add --transport http opusdns https://api.opusdns.com/mcp
```
Then, inside Claude Code, run `/mcp`, select **opusdns**, and complete the browser sign-in. From a shell instead:
```bash
claude mcp login opusdns
```
By default the server is registered for the current project only. To make it available everywhere, or to check it in for your team:
```bash
claude mcp add --transport http --scope user opusdns https://api.opusdns.com/mcp
claude mcp add --transport http --scope project opusdns https://api.opusdns.com/mcp
```
The project scope writes a shared `.mcp.json`:
```json
{
"mcpServers": {
"opusdns": {
"type": "http",
"url": "https://api.opusdns.com/mcp"
}
}
}
```
The `"type"` field is required. An entry with a `url` and no `type` is read as a local command, and the server is skipped.
Inspect and remove:
```bash
claude mcp list
claude mcp get opusdns
claude mcp remove opusdns
```
### Adding the sandbox alongside production
```bash
claude mcp add --transport http opusdns-sandbox https://sandbox.opusdns.com/mcp
```
Production and sandbox are separate identity realms, so each connector needs its own sign-in and neither can see the other's domains. Give them distinct names — an agent offered two connectors with the same name will pick one arbitrarily.
### Check it worked
```bash
claude mcp list
```
The server should show as connected. Then ask for something read-only — _"how many domains do I have?"_ — and expect a count back. If it does not connect, the symptom is almost certainly in [Troubleshooting](/mcp-server/troubleshooting#connecting).
## Claude desktop and Claude on the web
Open **Settings → Connectors → Add custom connector**, name it `OpusDNS`, paste `https://api.opusdns.com/mcp`, add it, then choose **Connect** and complete the browser sign-in.
Custom connectors are a paid-plan feature, and on team and enterprise plans an administrator may need to allow custom connectors for the organization first.
## Clients that only speak stdio
Older clients cannot open a remote HTTP connection themselves and need a local bridge:
```json
{
"mcpServers": {
"opusdns": {
"command": "npx",
"args": ["-y", "mcp-remote", "https://api.opusdns.com/mcp"]
}
}
}
```
For Claude desktop that file is `claude_desktop_config.json`, under `~/Library/Application Support/Claude/` on macOS and `%APPDATA%\Claude\` on Windows. The bridge runs the OAuth flow on first use and caches the tokens on disk; delete its cache directory to force a fresh sign-in.
`mcp-remote` is a third-party npm package, not maintained or supported by OpusDNS. Prefer a client with native remote HTTP support. If you use the bridge, you are running third-party code that holds your OpusDNS access token on disk.
## Next
* [Tool workflows](/mcp-server/tool-workflows) — what to ask for first
* [Approvals and confirmations](/mcp-server/approvals) — what a confirmation prompt looks like
* [OAuth details](/mcp-server/connect/oauth) — the flow in full, for writing your own client
* [Disconnecting](/mcp-server/connect/disconnect) — removing the connector, signing out, and cutting access off
# Connect Cursor, VS Code, and ChatGPT
All of these clients talk to the same endpoint with the same credentials: `https://api.opusdns.com/mcp`, remote Streamable HTTP, browser OAuth. What differs is the config file and the key it nests the server under.
| Client | Remote HTTP | Browser sign-in | Bridge needed | Approval prompt |
| ------------------------------- | ----------- | --------------------------------------- | ------------- | ----------------------------- |
| Claude Code | Yes | Yes | No | In the client (Path A) |
| Claude desktop and web | Yes | Yes | No | In the client (Path A) |
| Cursor | Yes | Yes | No | Relayed by the agent (Path B) |
| VS Code | Yes | Yes | No | Relayed by the agent (Path B) |
| ChatGPT custom connectors | Yes | Yes | No | Relayed by the agent (Path B) |
| OpenAI Responses API `mcp` tool | Yes | **No** — needs a token you already hold | No | Relayed by the agent (Path B) |
| stdio-only clients | No | Through a bridge | Yes | Relayed by the agent (Path B) |
The last column is about _who draws the prompt_, not about how strongly the action is gated — the gate is server-side either way. A client gets Path A only if it negotiates protocol revision `2026-07-28` **and** declares elicitation; everything else falls back to Path B, which works everywhere. See [Approvals and confirmations](/mcp-server/approvals).
ChatGPT adds a second gate the other clients do not have: signing in is one thing, _seeing_ the tools is another, and the latter needs developer mode, which is not offered on the free plan. See [ChatGPT](#chatgpt).
## Cursor
Write `~/.cursor/mcp.json` for every project, or `.cursor/mcp.json` in a project root for one:
```json
{
"mcpServers": {
"opusdns": {
"url": "https://api.opusdns.com/mcp"
}
}
}
```
Then open Cursor's MCP settings; the server appears with a sign-in action. Complete the browser flow.
Some Cursor versions also expect an explicit `"type": "http"` alongside `"url"`. Adding it is harmless on versions that do not require it.
## VS Code
Write `.vscode/mcp.json` in the workspace, or use the **MCP: Add Server** command for a user-level install.
```json
{
"servers": {
"opusdns": {
"type": "http",
"url": "https://api.opusdns.com/mcp"
}
}
}
```
VS Code nests servers under `servers`, not `mcpServers`. Copying a config from another client's documentation without changing that key is the most common reason the server never appears.
## ChatGPT
Create a connector, paste `https://api.opusdns.com/mcp`, and set authentication to OAuth. The only OpusDNS-specific values are that URL and choosing OAuth.
Sign-in itself works on any plan: Dynamic Client Registration completes, the browser flow completes, and the server answers `tools/list` with its full tool list. Whether ChatGPT then _shows_ those tools is a separate, plan-dependent question.
Outside developer mode, ChatGPT surfaces only tools named `search` and `fetch`. This server exposes neither, so on a plan without developer mode a connector that authenticated perfectly still reports no tools. Developer mode is [available to Pro, Plus, Business, Enterprise, and Education accounts on the web](https://developers.openai.com/api/docs/guides/developer-mode) — it does not exist on the free plan. This is an OpenAI product limitation; nothing on the OpusDNS side can lift it.
On a plan that offers it, the toggle is under **Settings → Security and login**. It has moved before — it lived under Connectors → Advanced until Connectors was renamed to Plugins — so treat OpenAI's documentation, not any particular path, as authoritative. With developer mode on, every tool this server exposes is available, writes included, subject to your confirmation settings.
Two limits survive developer mode: agent mode does not use custom connectors at all, and deep research uses them for reads only, which puts `bulk_submit` out of reach there.
### OpenAI Responses API
For a programmatic agent rather than the ChatGPT app:
```json
{
"model": "gpt-5",
"tools": [
{
"type": "mcp",
"server_label": "opusdns",
"server_url": "https://api.opusdns.com/mcp",
"authorization": "",
"require_approval": "always"
}
]
}
```
This path takes a bearer token you have already obtained — it does not run an interactive OAuth flow, and the MCP endpoint does not accept API keys. You have to mint an access token yourself against `https://auth.opusdns.com/realms/opusdns`. The device-code grant is the practical option for a headless agent; request `offline_access` so you can refresh, because access tokens are short-lived. See [OAuth details](/mcp-server/connect/oauth).
Keep `require_approval` on. The server gates writes on its own side regardless, but a model that cannot see an approval prompt will simply stop at the confirmation payload — see [Approvals and confirmations](/mcp-server/approvals).
## Any other MCP client
Everything a client needs:
* **URL** — `https://api.opusdns.com/mcp`
* **Transport** — Streamable HTTP. POST JSON-RPC with `Accept: application/json, text/event-stream`
* **Authentication** — OAuth 2.1 authorization code with PKCE (`S256`). Dynamic Client Registration is supported, so no credential has to be provisioned by hand
* **Scopes to request** — `openid profile email opusdns:mcp offline_access`
* **Session** — none. The server is stateless
* **CORS** — open, and `WWW-Authenticate` is exposed, so a browser-based client can read the challenge
For a client that only speaks stdio, bridge it: `npx -y mcp-remote https://api.opusdns.com/mcp`.
Full discovery chain and token requirements: [OAuth details](/mcp-server/connect/oauth).
# OAuth details
Most clients handle all of this for you — this page is for writing your own client, or debugging one that will not connect.
The server is an OAuth 2.1 protected resource. It authenticates the caller and forwards the identity to the OpusDNS API; the API decides what that identity is allowed to do.
## The discovery chain
### 1. An unauthenticated call is challenged
```bash
curl -i -X POST 'https://api.opusdns.com/mcp' \
--header 'Content-Type: application/json' \
--header 'Accept: application/json, text/event-stream' \
--data '{"jsonrpc":"2.0","id":1,"method":"tools/list","params":{}}'
```
```http
HTTP/2 401
www-authenticate: Bearer resource_metadata="https://api.opusdns.com/.well-known/oauth-protected-resource"
{"error":"authentication_required"}
```
The `WWW-Authenticate` header is the entry point: it names the metadata document rather than the authorization server, so the resource can move realms without clients being reconfigured.
### 2. Fetch the protected-resource metadata
```bash
curl https://api.opusdns.com/.well-known/oauth-protected-resource
```
```json
{
"resource": "https://api.opusdns.com/mcp",
"authorization_servers": ["https://auth.opusdns.com/realms/opusdns"],
"bearer_methods_supported": ["header"],
"scopes_supported": ["profile", "email", "opusdns:mcp", "offline_access"],
"resource_documentation": "https://developers.opusdns.com/mcp-server"
}
```
Sandbox differs in two fields: the authorization server is `https://auth.opusdns.com/realms/opusdns-sandbox` and the resource is `https://sandbox.opusdns.com/mcp`.
The document is also served at `/.well-known/oauth-protected-resource/mcp`, for clients that append the resource path.
### 3. Fetch the authorization-server metadata
```bash
curl https://auth.opusdns.com/realms/opusdns/.well-known/openid-configuration
```
Supported grants include authorization code with PKCE (`S256`), refresh token, and device code. The device-code grant is the one to use for an agent with no browser.
### 4. Register
Dynamic Client Registration is enabled, so a client can register itself:
```bash
curl -X POST \
https://auth.opusdns.com/realms/opusdns/clients-registrations/openid-connect \
--header 'Content-Type: application/json' \
--data '{"client_name":"my-agent","redirect_uris":["http://127.0.0.1:8976/callback"]}'
```
There is no client to request from OpusDNS and no ticket to file.
### 5. Authorize, exchange, call
Run the authorization-code flow with PKCE, then send the access token on every call:
```bash
curl -X POST 'https://api.opusdns.com/mcp' \
--header 'Authorization: Bearer ' \
--header 'Content-Type: application/json' \
--header 'Accept: application/json, text/event-stream' \
--data '{"jsonrpc":"2.0","id":1,"method":"tools/list","params":{}}'
```
## Scopes
| Scope | Why |
| ------------------ | -------------------------------------------------------------------------------------- |
| `openid` | Sent on the authorization request, but deliberately **absent** from `scopes_supported` |
| `profile`, `email` | Identify the signed-in user |
| `opusdns:mcp` | The resource scope for this server |
| `offline_access` | Refresh tokens, so you are not re-prompted every hour |
The two oddities in that table are deliberate, and both change what a client has to do.
### Why `openid` is not advertised
`openid` is the OpenID Connect authentication marker, not a resource scope, and the identity provider's client-registration policy rejects it during Dynamic Client Registration because it is not a registerable client scope.
So: keep sending `openid` on the authorization request, where it is handled specially. Just do not build your registration scope set by copying `scopes_supported` and expecting `openid` to be in it.
### Why offline access is advertised
RFC 9728 says a resource server SHOULD NOT advertise the `offline_access` scope. This one does, on purpose.
Clients commonly build their Dynamic Client Registration scope set from `scopes_supported`, and the identity provider grants a registered client only the scopes it registered with. The client then appends `offline_access` at the authorization step, because the _authorization server_ advertises it. If the resource metadata omitted it, the authorization request would ask for a scope the client was never granted, and the provider would answer `invalid_scope`. Advertising it reconciles the two scope sets so refresh tokens work.
If you are writing your own client: treat `scopes_supported` here as the set to register with, not as an RFC-pure list of resource scopes.
## What the server checks
| Check | Requirement |
| --------- | -------------------------------------------------------------------- |
| Signature | Verified against the realm's published signing keys |
| `iss` | Must match the environment's realm issuer exactly |
| `exp` | Must be present and in the future. A token with no `exp` is rejected |
| `aud` | Must include the audience the deployment requires |
Request the `opusdns:mcp` scope and the resulting token carries the audience the server requires. A token minted for the sandbox realm will not authenticate against production, and vice versa.
## Metadata aliases and redirects
Some clients probe for authorization-server metadata at the resource URL rather than following the protected-resource document. Those probes are redirected to the realm:
| Path | Behaviour |
| ------------------------------------------- | --------------------------------------- |
| `/.well-known/oauth-protected-resource` | The metadata document |
| `/.well-known/oauth-protected-resource/mcp` | The same document |
| `…/.well-known/openid-configuration` | `302` to the realm's discovery document |
| `…/.well-known/oauth-authorization-server` | `302` to the realm's discovery document |
## What is not supported
The hosted MCP endpoint does not accept API keys. An `X-Api-Key` header is ignored, the request counts as anonymous, and you get `401 {"error":"authentication_required"}`. Use the OAuth flow. API keys remain the right credential for direct API calls — see [Authentication](/introduction/authentication).
## Permissions come from your account, not from scopes
Authentication proves who you are. Authorization is decided by the OpusDNS API from your organization roles, and it answers `403` when you lack the right. Holding `opusdns:mcp` does not grant write access to anything.
An MCP session inherits your own permissions. If your account can delete domains, so can an agent acting for you — which is what the approval gate is for. See [Approvals and confirmations](/mcp-server/approvals) and [Roles & permissions](/account/organizations/roles).
# Disconnecting
Three different things end an agent's access, and they are not
interchangeable: the credentials your client has stored, the sign-in session
behind them, and the OpusDNS account the agent was acting for. Removing the
connector stops the agent; on its own it does not invalidate a token that has
already been issued.
## Remove the server from your client
Your credentials live in the client, never on the MCP server, so this is the
step that actually deletes them.
| Client | How |
| --- | --- |
| Claude Code | `claude mcp logout opusdns` clears the stored credentials; `claude mcp remove opusdns` also drops the entry |
| Claude desktop and web | **Settings → Connectors**, then remove the connector |
| Cursor | Delete the entry from `~/.cursor/mcp.json`, or from the project's `.cursor/mcp.json` |
| VS Code | Delete the entry from `.vscode/mcp.json`, or remove the server from the MCP view |
| `mcp-remote` bridge | Delete its cache directory, `~/.mcp-auth` |
The bridge is the one people forget. It caches your access token on disk under
your home directory, so deleting the server from a client's config file leaves
the credential behind. Remove the cache directory too.
## Sign out
Signing out at the OpusDNS identity provider ends the session your client
renews against:
- Production — `https://auth.opusdns.com/realms/opusdns/account`
- Sandbox — `https://auth.opusdns.com/realms/opusdns-sandbox/account`
An access token that has already been issued keeps working until it expires.
Signing out stops the client obtaining a new one; it does not reach back and
cancel the one it already has.
## Cut access off immediately
Deleting the user the agent signed in as removes their OpusDNS sign-in
altogether, and every tool call checks the account it is acting for — so the
next call fails, whatever the client still holds. See
[User management](/account/users).
You cannot delete your own account or the last admin in an organization, so
this is a step for a second administrator. If you are locking yourself out of
your own agent, remove the connector and sign out instead.
## What disconnecting does not do
- **It does not touch your API keys.** They are a separate credential, are never
accepted by the MCP endpoint, and are managed from
[Authentication](/introduction/authentication).
- **It does not stop work already submitted.** A bulk batch runs in
[Jobs](/automation/jobs/overview), not in the conversation, so disconnecting
neither pauses nor cancels it — steer it from
[Managing batches](/automation/jobs/managing-batches).
- **It leaves nothing to revoke on the approval side.** Each approval is single
use and expires within minutes of being issued. See
[Approvals and confirmations](/mcp-server/approvals).
## Related
- [Connect Claude and Claude Code](/mcp-server/connect)
- [OAuth details](/mcp-server/connect/oauth)
- [Roles & permissions](/account/organizations/roles)
# Tool workflows
Three worked examples, one per tool family. A successful tool call returns its payload twice over — as a text block and as `structuredContent`, with the same content — so your client may render either. (A tool-level failure returns text only, flagged as an error.) The examples below show the payload.
## Discovery: call one operation
### 1. Find the operation
`search_operations` with:
```json
{ "query": "renew domain", "limit": 10 }
```
comes back as:
```json
{
"count": 2,
"total": 2,
"results": [
{
"operationId": "renew_domain_v1_domains__domain_reference__renew_post",
"method": "POST",
"path": "/v1/domains/{domain_reference}/renew",
"tags": ["domain"],
"summary": "Renew a domain",
"safety": { "read": false, "write": true, "cost": true, "destructive": false }
},
{
"operationId": "epp_check_domain_v1_domains_check_get",
"method": "GET",
"path": "/v1/domains/check",
"tags": ["domain"],
"summary": "Check domain availability and registration metadata",
"safety": { "read": true, "write": false, "cost": false, "destructive": false }
}
]
}
```
Two fields are worth understanding.
`total` counts the operations in the **top relevance tier** — those matching the most of your query terms — including any beyond `limit`. So `total` larger than `count` means the results were capped and the query should be narrowed. It is not a count of the whole catalog.
`detail` is absent here, and that is the normal case. It is inlined only when `total` is exactly 1 _and_ the operation's request-body schema is small enough, so that a search with one unambiguous answer saves a round trip. Two operations matched, so pick one and run `describe_operation` on its id:
```json
{ "operationId": "renew_domain_v1_domains__domain_reference__renew_post" }
```
which returns the operation's parameters, request-body schema and safety flags, plus `requiresConfirmation`.
An `operationId` the catalog does not know is answered as a **result**, not an error — so search again rather than retrying:
```json
{
"status": "not_found",
"message": "unknown operationId: renew_domain_v2"
}
```
### 2. Call it
`call_operation` with:
```json
{
"operationId": "renew_domain_v1_domains__domain_reference__renew_post",
"pathParams": { "domain_reference": "acme-labs.com" },
"body": {
"period": { "unit": "y", "value": 1 },
"current_expiry_date": "2026-11-04T00:00:00Z"
}
}
```
`domain_reference` accepts either a domain name or a domain ID. `period` and `current_expiry_date` are both required — passing the expiry you believe is current is what stops a renewal being applied twice.
### 3. Approve it
Renewal writes data and costs money, so this first call does not execute. It returns a confirmation challenge instead, and your client asks you to approve it. See [Approvals and confirmations](/mcp-server/approvals).
### 4. Read the result
After approval, the same call returns:
```json
{
"status": "ok",
"operationId": "renew_domain_v1_domains__domain_reference__renew_post",
"httpStatus": 200,
"headers": {
"content-type": "application/json",
"x-server-request-id": "8f3c2e10-1b4a-4c6b-9e77-2a91f5d0c4aa"
},
"data": { "…the updated domain…" },
"truncated": false
}
```
`status` is `"ok"` for a 2xx or 3xx response and `"api_error"` for 4xx and 5xx. An HTTP error from OpusDNS is a normal tool result carrying `httpStatus` and the API's problem detail in `data` — not a protocol failure. Quote `headers["x-server-request-id"]` when you contact support.
## Portfolio: read a lot of domains cheaply
`portfolio_summary` takes no arguments and answers "how big is this account, and what is expiring":
```json
{
"status": "ok",
"operationId": "get_domain_summary_v1_domains_summary_get",
"httpStatus": 200,
"data": {
"organization_id": "organization_01h45ytscbebyvny4gc8cr8ma2",
"domains": {
"total_count": 4127,
"by_status": { "ok": 4001, "pendingTransfer": 12, "clientTransferProhibited": 114 },
"by_tld": { "com": 2610, "de": 802, "io": 415 },
"expiring_soon": { "next_30_days": 412, "next_60_days": 733, "next_90_days": 1104 }
}
}
}
```
`portfolio_query` lists domains but returns only the fields you name, which is what keeps a four-thousand-domain account out of the model's context:
```json
{
"selector": { "tld": ["com"], "expires_in_30_days": true },
"fields": ["name", "domain_id", "expires_on", "renewal_mode"],
"pageSize": 50
}
```
```json
{
"status": "ok",
"fields": ["name", "domain_id", "expires_on", "renewal_mode"],
"results": [
{
"name": "acme-labs.com",
"domain_id": "domain_01h45ytscbebyvny4gc8cr8ma2",
"expires_on": "2026-09-14T00:00:00Z",
"renewal_mode": "expire"
}
],
"pagination": {
"current_page": 1,
"page_size": 50,
"total_items": 412,
"total_pages": 9,
"has_next_page": true,
"has_previous_page": false
}
}
```
Omit `fields` and you get `name`, `domain_id`, `expires_on`, `renewal_mode` and `status_tags`. `pageSize` is capped server-side at 200.
### The selector
`selector` is the filter set of [`GET /v1/domains`](/api-reference), and the same object drives the bulk tools. The filters worth knowing:
| Filter | Type | Notes |
| ---------------------------------------------------------------- | ---------------------------------------- | ------------------------------------------------------------------------- |
| `tag_ids` | list of tag IDs | IDs such as `tag_01h45ytscbebyvny4gc8cr8ma2`, **not** labels |
| `tag_mode` | `match_any`, `match_all` or `match_none` | Defaults to `match_any` |
| `status_tags` | list | For example `VERIFICATION_REQUIRED`, `INBOUND_TRANSFER_PENDING` |
| `tld` | list | For example `["com", "org"]` |
| `search`, `name`, `sld` | string | Match by full name, second-level label, or free text |
| `expires_in_30_days`, `expires_in_60_days`, `expires_in_90_days` | boolean | |
| `expires_before`, `expires_after` | RFC 3339 | Also `created_*`, `updated_*`, `registered_*`, `transferred_*` |
| `transfer_lock`, `is_premium` | boolean | |
| `registry_statuses` | list | |
| `include` | list | `["tags"]` populates `tags` and `status_tags`, which are otherwise `null` |
`tag_ids` takes tag **IDs**, not labels. Ask for the tag by name and the agent will look its ID up first. See [User tags](/automation/tags/user-tags).
An empty selector matches **every domain in the account**. That is harmless for a read, and consequential for [a bulk submission](/mcp-server/bulk-operations).
## Bulk: from a query to a change
Two calls — `bulk_preview`, then `bulk_submit` with the same arguments. The selector resolves server-side, so the model never transcribes a domain name, and the approval you give is bound to the exact set that was resolved.
The useful property is that **the same selector means the same thing to both families**. Find the set with `portfolio_query` and read its `pagination.total_items`; hand the identical selector to `bulk_preview` and read `matchedDomains`. The two numbers agreeing is the check to make before you approve — if they disagree, the selector is not describing what you think it is.
Full walkthrough: [Bulk operations with Jobs](/mcp-server/bulk-operations). Task-shaped examples: [Recipes](/mcp-server/recipes).
## Related
* [Recipes](/mcp-server/recipes) — the same tools, arranged by task
* [Results and errors](/mcp-server/results) — every shape a tool can return
* [Tools reference](/mcp-server/tools) — every parameter of every tool
* [Sub-organizations](/mcp-server/sub-organizations) — the `organizationId` parameter every one of these tools takes
* [Renew a domain](/products/domains/renew), [Manage a domain](/products/domains/manage)
* [API Reference](/api-reference)
# Recipes
Worked answers to the jobs people actually bring to a registrar. Each recipe is the sentence you type, the calls it turns into, and the one thing that catches people out.
Every request payload below is checked against the tool's real input schema before it is published, so what you see is what the server accepts.
Every recipe that changes something is a two-step: `bulk_preview` first — it submits nothing and asks for no approval — then `bulk_submit` with the **same** arguments. The preview's `matchedDomains` is the number to read before you approve.
## Reading
### What is expiring, and how bad is it
> _"How many domains do I have, and what is expiring in the next 90 days?"_
`portfolio_summary` takes no arguments and answers both halves in one small object. Only when you need the names does the model go on to `portfolio_query`:
```json
{
"selector": { "expires_in_30_days": true },
"fields": ["name", "expires_on", "renewal_mode"],
"pageSize": 50
}
```
**Watch out for** asking for the domain list first. `portfolio_summary` is a fraction of the size and usually answers the question on its own.
### List domains by tag
> _"Which domains are tagged migration?"_
`tag_ids` takes tag **IDs**, not labels. The model resolves the label first — `search_operations` for the tags list operation, then `call_operation` — and only then filters:
```json
{
"selector": { "tag_ids": ["tag_01h45ytscbebyvny4gc8cr8ma2"] },
"fields": ["name", "expires_on", "status_tags", "tags"],
"pageSize": 100
}
```
**Watch out for** `status_tags` and `tags` coming back `null`. The domain list only populates them when the request asks for them, so add `"include": ["tags"]` to the selector when you project either field.
### Answer a question without pulling registrant data into the model
> _"Which .de domains renew automatically?"_
Use `portfolio_query` with an explicit `fields` list rather than `call_operation` on the domains endpoint. The projection happens server-side, so contact and registrant data never enters the conversation at all. See [Data handling](/mcp-server/data-handling).
## Changing many domains
### Turn auto-renew off for a TLD
> _"Turn off auto-renew on every .io that expires this quarter."_
```json
{
"templateType": "domain_update_bulk",
"template": { "renewal_mode": "expire" },
"selector": { "tld": ["io"], "expires_in_90_days": true }
}
```
`renewal_mode` is `renew` or `expire`. Submit with `bulk_submit` and the identical arguments.
**Watch out for** the direction. `expire` means _let it lapse_ — this is the one recipe where getting it backwards costs you the domain.
### Lock transfers across a tag
> _"Lock transfers on everything tagged migration."_
```json
{
"templateType": "domain_update_bulk",
"template": { "status_changes": { "add": ["clientTransferProhibited"] } },
"selector": { "tag_ids": ["tag_01h45ytscbebyvny4gc8cr8ma2"] }
}
```
`status_changes` is relative — `add` and `remove` against the current state, which is what you want across a mixed portfolio. The sibling field `statuses` _replaces_ the whole set.
**Watch out for** passing the tag label instead of its id. The selector matches nothing and the submit is refused with `selector matched no domains`.
### Move a set of domains to new nameservers
> _"Point everything on the old nameservers at ns1/ns2.opusdns.com."_
```json
{
"templateType": "domain_update_bulk",
"template": {
"nameservers": [
{ "hostname": "ns1.opusdns.com" },
{ "hostname": "ns2.opusdns.net" }
]
},
"selector": { "tld": ["com", "net"] }
}
```
**Watch out for** the shape: `nameservers` is a list of **objects** with a `hostname`, not a list of strings. A glue record adds `ip_addresses` alongside.
### Give a set of domains a standard DNS zone
> _"Create zones for the new .io domains with a www record."_
```json
{
"templateType": "dns_zone_create_bulk",
"template": {
"dnssec_status": "disabled",
"rrsets": [
{
"name": "www",
"type": "A",
"ttl": 3600,
"records": [{ "rdata": "203.0.113.10" }]
}
]
},
"selector": { "tld": ["io"] }
}
```
Zone templates are addressed by domain name rather than domain id, which the server handles — you still only supply the selector.
### Replace a record across many zones
> _"Point www at 203.0.113.10 on all the .io zones."_
```json
{
"templateType": "dns_zone_patch_rrsets_bulk",
"template": {
"ops": [
{
"op": "upsert",
"rrset": {
"name": "www",
"type": "A",
"ttl": 300,
"records": [{ "rdata": "203.0.113.10" }]
}
}
]
},
"selector": { "tld": ["io"] }
}
```
`upsert` replaces the whole RRset for that `(name, type)` — any prior records are discarded — and `remove` deletes it outright. The server writes the `ops` into each resolved zone, so `sampleInstances` shows a `zone_name` alongside them.
**Watch out for** `upsert` being a replace, not an append. Adding one A record to a name that already has two means listing all three.
### Redirect a set of domains to one landing page
> _"Redirect all the defensive registrations to the main site."_
```json
{
"templateType": "domain_forward_create_bulk",
"template": {
"enabled": true,
"auto_create_zone": true,
"https": {
"redirects": [
{
"request_path": "/",
"target_protocol": "https",
"target_hostname": "www.acme-labs.com",
"target_path": "/",
"redirect_code": 301
}
]
}
},
"selector": { "tag_ids": ["tag_01h45ytscbebyvny4gc8cr8ma2"] },
"hostnamePrefix": ""
}
```
`hostnamePrefix` decides _what_ gets forwarded: `""` (the default) is the apex, `"*."` is the wildcard subdomain. Run it twice to cover both.
**Watch out for** forgetting `auto_create_zone`. A forward needs a zone; without it, domains that have none fail individually inside the batch.
### Switch off the wildcard forwards again
> _"Turn off the wildcard redirects on those."_
```json
{
"templateType": "domain_forward_disable_bulk",
"template": {},
"selector": { "tag_ids": ["tag_01h45ytscbebyvny4gc8cr8ma2"] },
"hostnamePrefix": "*."
}
```
**Watch out for** `template`. The enable, disable and delete commands carry no template of their own, but the tool still requires the argument — pass `{}`.
### Catch-all email forwarding across a portfolio
> _"Forward all mail on the .com domains to ."_
```json
{
"templateType": "email_forward_create_bulk",
"template": {
"enabled": true,
"auto_create_zone": true,
"aliases": [{ "alias": "*", "forward_to": ["ops@acme-labs.com"] }]
},
"selector": { "tld": ["com"] }
}
```
### Change more than 1,000 domains
A batch is a single Jobs command, and one command carries at most 1,000 instances. A selector that resolves to more is refused before anything is submitted:
```plaintext
selector matched more than the limit of 1000 domains; narrow the selector and
submit more than one batch, for example one TLD at a time
```
Split the work along a filter that partitions cleanly — one TLD at a time is usually the least surprising:
> _"Do the .com domains first, then .de, then the rest."_
Each narrowed selector is its own preview, its own approval and its own `batch_id`. Keep the ids: they are how you check and steer each half afterwards.
## Steering a batch
### Rescue a half-failed batch
> _"Batch batch\_01k3n0m5xrf9pab6t2wqzhkvr3 has failures — retry only the ones that ran out of funds."_
First the state:
```json
{ "batchId": "batch_01k3n0m5xrf9pab6t2wqzhkvr3" }
```
Then a targeted retry. `errorClass` is a list, and omitting it retries every failed job in the batch:
```json
{
"batchId": "batch_01k3n0m5xrf9pab6t2wqzhkvr3",
"action": "retry",
"errorClass": ["BillingInsufficientFundsError"]
}
```
`pause`, `resume` and `cancel` take the same shape without `errorClass`. All four are gated, so each one asks for approval.
**Watch out for** retrying before you have fixed the cause. A retry of an insufficient-funds failure with the wallet still empty just fails again.
## One domain at a time
### Renew a single domain
> _"Renew acme-labs.com for a year."_
`search_operations` finds the operation, and because exactly one matches, its `detail` comes back inline — no `describe_operation` hop:
```json
{
"operationId": "renew_domain_v1_domains__domain_reference__renew_post",
"pathParams": { "domain_reference": "acme-labs.com" },
"body": {
"period": { "unit": "y", "value": 1 },
"current_expiry_date": "2026-11-04T00:00:00Z"
}
}
```
`domain_reference` accepts a name or a domain id. `current_expiry_date` is required and is what stops a renewal being applied twice.
**Watch out for** looping this tool over a list of domains. That is what the bulk tools exist for, and a loop costs one approval per domain.
## Acting for a customer
### Run any of the above inside a sub-organization
Add `organizationId` to **every** call in the sequence — the preview and the submit both:
```json
{
"templateType": "domain_update_bulk",
"template": { "renewal_mode": "expire" },
"selector": { "tld": ["io"] },
"organizationId": "organization_01h45ytscbebyvny4gc8cr8ma2"
}
```
**Watch out for** setting it on one leg only. A preview and a submit that disagree about the organization are two different actions, so the approval will not carry over. See [Sub-organizations](/mcp-server/sub-organizations).
## Related
* [Bulk operations with Jobs](/mcp-server/bulk-operations) — selectors, templates and limits in full
* [Bulk templates](/mcp-server/tools/templates) — every `templateType`, and the Jobs commands deliberately not reachable this way
* [Approvals and confirmations](/mcp-server/approvals)
* [Results and errors](/mcp-server/results)
# Sub-organizations
An MCP session signs you in as yourself, so by default every tool acts on your own organization. If your account is a parent of other organizations — the usual reseller shape — pass `organizationId` to act on one of them instead:
```json
{
"selector": { "expires_in_30_days": true },
"fields": ["name", "expires_on"],
"organizationId": "organization_01h45ytscbebyvny4gc8cr8ma2"
}
```
Every tool that reaches the API takes it: `call_operation`, `portfolio_summary`, `portfolio_query`, `bulk_preview`, `bulk_submit`, `job_batch_status` and `job_batch_control`. `search_operations` and `describe_operation` do not — they read the API catalog and never touch your data.
## Finding the id
It is the organization's TypeID, `organization_` followed by 26 characters. The agent can look it up for you — ask it to list your organizations, and it will call the organizations list operation through `call_operation`.
It is the **id**, not the organization's name. A name is not accepted and is rejected before anything is sent.
## What you can reach
Only organizations below your own. The target must be a descendant of the account you signed in as; OpusDNS enforces that and answers `403` otherwise, so the parameter grants nothing your account did not already have. Permissions are unchanged too: your role in that organization still decides what you may do there.
## It applies per call, not per session
There is no "switch organization and stay there". Each tool call carries its own `organizationId`, and a call without one acts on your own organization.
This matters most for bulk. `bulk_preview` and `bulk_submit` resolve the selector separately, so a preview against a sub-organization followed by a submit without the parameter would preview one set of domains and submit against another. Keep the parameter identical across both calls.
## Approvals name the organization
An approval prompt for a scoped action says which organization it is for:
```plaintext
Approve: domain_update_bulk on 412 domain(s) matching tld=["com"] (POST /v1/jobs)? Risk: writes data. Acting on sub-organization organization_01h45ytscbebyvny4gc8cr8ma2.
```
The approval is bound to it, exactly as it is bound to the path, the query and the body. Approve an action for one organization and the same action aimed at a sibling — or at your own account — does not match, and you are asked again. See [Approvals and confirmations](/mcp-server/approvals).
## Related
* [Tool workflows](/mcp-server/tool-workflows)
* [Bulk operations with Jobs](/mcp-server/bulk-operations)
* [Organizations](/account/organizations/overview), [Roles & permissions](/account/organizations/roles)
# Approvals and confirmations
Anything that is not a read is blocked before it reaches the OpusDNS API and requires your explicit approval. How you are asked depends on your client; the check on the server is the same either way.
## What is gated
Every `POST`, `PUT`, `PATCH` and `DELETE`, with one exception: a `POST` that only checks availability counts as a read, because asking whether a name is free has no side effect. In today's API that exception covers exactly one operation, `POST /v1/availability/stream`.
Reads — every `GET`, plus that one availability call — run without asking.
### The risk wording
Each approval names the risk of the operation:
| Operation | Risk shown |
| -------------------------------------------------------- | --------------------------------------------- |
| Register a domain (`POST /v1/domains`) | can create costs, writes data |
| Renew a domain | can create costs, writes data |
| Update a domain (`PATCH /v1/domains/{domain_reference}`) | writes data, can delete or transfer resources |
| Submit a batch (`POST /v1/jobs`) | writes data |
| Cancel a batch (`DELETE /v1/jobs/{batch_id}`) | writes data, can delete or transfer resources |
| Pause a batch | writes data |
| Patch zone RRsets | writes data |
The risk wording is derived from the operation's own description, so it occasionally reads more alarming than the operation is. **Update a domain** is labelled "can delete or transfer resources" because setting a transfer lock is one of the things it does. The wording changes what the prompt says, never whether approval is required.
## Which path your client takes
| Client | Path | What you see |
| ------------------------------ | ---- | ------------------------------------------------------------- |
| Claude Code | A | An approval prompt in the terminal |
| Claude desktop and web | A | An approval prompt in the conversation |
| Cursor | B | The agent relays the `confirmation_required` payload and asks |
| VS Code | B | The agent relays the payload and asks |
| ChatGPT / OpenAI Responses API | B | The agent relays the payload and asks |
Path A needs two things at once: protocol revision `2026-07-28` **and** a declared elicitation capability. A client missing either gets Path B, which works everywhere. Both enforce the same gate server-side; they differ only in who draws the prompt.
## Path A — your client asks you directly
Clients on protocol revision `2026-07-28` that support elicitation get a multi-round-trip request: the tool call terminates with an input request, and the client renders its own approval prompt.
```json
{
"resultType": "input_required",
"inputRequests": {
"approval": {
"method": "elicitation/create",
"params": {
"mode": "form",
"message": "Approve: Renew a domain (POST /v1/domains/{domain_reference}/renew)? Risk: can create costs, writes data.",
"requestedSchema": {
"type": "object",
"properties": {
"note": {
"type": "string",
"description": "Optional note recorded with the approval."
}
}
}
}
}
},
"requestState": "eyJ2IjoxLCJvcGVyYXRpb25JZCI6…"
}
```
The client asks you, then retries the same call with `requestState` echoed back verbatim and your answer under `inputResponses`:
```json
{
"name": "call_operation",
"arguments": {
"operationId": "renew_domain_v1_domains__domain_reference__renew_post",
"pathParams": { "domain_reference": "acme-labs.com" },
"body": {
"period": { "unit": "y", "value": 1 },
"current_expiry_date": "2026-11-04T00:00:00Z"
}
},
"requestState": "eyJ2IjoxLCJvcGVyYXRpb25JZCI6…",
"inputResponses": {
"approval": { "action": "accept", "content": { "note": "approved by kr" } }
}
}
```
Only `"action": "accept"` executes.
On this path the prompt is rendered by your client and the model never holds an unapproved token. It is the stronger of the two paths — prefer a client that supports it.
## Path B — the confirmation payload
Every other client gets a payload the model has to relay to you:
```json
{
"status": "confirmation_required",
"message": "Confirmation required before executing POST /v1/domains/{domain_reference}/renew (Renew a domain). Risk: can create costs, writes data. Ask the user for explicit approval, then retry the exact same action with this confirmation token.",
"confirmationToken": "eyJ2IjoxLCJvcGVyYXRpb25JZCI6…",
"expiresAt": "2026-08-25T14:35:12Z",
"operationId": "renew_domain_v1_domains__domain_reference__renew_post",
"safety": { "read": false, "write": true, "cost": true, "destructive": false }
}
```
### Retrying with a confirmation token
Repeat the **identical** call with the token added as an argument:
```json
{
"operationId": "renew_domain_v1_domains__domain_reference__renew_post",
"pathParams": { "domain_reference": "acme-labs.com" },
"body": {
"period": { "unit": "y", "value": 1 },
"current_expiry_date": "2026-11-04T00:00:00Z"
},
"confirmationToken": "eyJ2IjoxLCJvcGVyYXRpb25JZCI6…"
}
```
On this path your client has to actually show you the action and get your approval before retrying. The server can verify that the token belongs to this exact action, but it cannot verify that a human saw it. Choosing a client you trust with that is part of the security model — which is why Path A is preferable where it is available.
## What the approval is bound to
There is one token type. On Path A it travels as `requestState`; on Path B as `confirmationToken`. It is signed, and it binds:
| Bound to | Consequence |
| ---------------------------------------------------------------------------------------------------------------- | ----------------------------------------------------------------------- |
| The operation | A token for one operation cannot approve another |
| A hash of the normalised action — path parameters, query, body, and the resolved list of domains for a bulk call | Change one byte of the request and the token stops matching |
| The signed-in user | Someone else's token is useless |
| The client and the granted scopes | A different client, or a re-login with different scopes, invalidates it |
| An expiry, about 5 minutes | It cannot be banked for later |
It is also **single use**, and it is consumed only after every other check has passed — so a retry that does not match never burns a token that is still valid.
Approval is enforced by the server, before any request reaches the OpusDNS API. The gate sits in the one code path every tool call flows through, so it cannot be bypassed by prompt engineering, by reaching for a different tool, or by a model that decides the instructions do not apply to it.
## Declining, dismissing, and being asked again
**You decline or dismiss the prompt.** The call returns:
```json
{
"status": "declined",
"operationId": "renew_domain_v1_domains__domain_reference__renew_post",
"message": "The user declined this action. Nothing was executed. Do not retry unless the user asks for it again."
}
```
Nothing was sent upstream, and the token was **not** consumed — it simply expires. You can still approve the same action before it does.
**The client retried but lost your answer.** The confirmation check fails and you are asked again, which is what the protocol prescribes for a missing response. Nothing is consumed.
**The token expired, was already used, or does not match.** You get a fresh challenge. See [Troubleshooting](/mcp-server/troubleshooting#approval-keeps-being-requested).
## Approving a bulk action safely
Three things to read in the prompt before you say yes:
1. **The count.** Does `matchedDomains` from the preview match what you expected? 412 and 4,127 look alike in a hurry.
2. **The selector echo.** The prompt spells out the filters — `tld=["com"], expires_in_30_days=true`. If it says _"the entire portfolio (no filters)"_, the selector was empty.
3. **The organization.** If you are acting for a customer, the prompt names the sub-organization. If it does not, you are about to change your own portfolio.
## Bulk approvals bind the resolved set
For a bulk call, the resolved list of domains is part of what the token binds. The list is sorted before it is hashed, so re-resolving the same selector reproduces the same approval — but if a domain was added, removed or renamed between the challenge and the retry, the hash no longer matches and you are asked again.
This is a feature. It means you approve "these 412 domains", not "a bulk update, roughly".
## Related
* [Bulk operations with Jobs](/mcp-server/bulk-operations)
* [Results and errors](/mcp-server/results) — the shapes an approval can return
* [Roles & permissions](/account/organizations/roles) — approval is not authorization; the API still decides what your account may do
* [Troubleshooting](/mcp-server/troubleshooting)
# Bulk operations with Jobs
A change across many domains never becomes many tool calls. You supply a selector and one shared template; the server resolves the matching domains and submits a single [Jobs](/automation/jobs/overview) batch, where the loop, the retries and the error handling all run server-side.
Three consequences worth knowing:
* The model never transcribes a domain name, so it cannot mistype one.
* One approval covers the whole batch, bound to the exact resolved set.
* Progress and retries live in the Jobs service, so a dropped conversation does not orphan a half-finished change.
## Template types
| Family | `templateType` | Instances addressed by |
| --------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------- | ---------------------- |
| Domains | `domain_update_bulk` | `domain_id` |
| DNS zones | `dns_zone_create_bulk`, `dns_zone_update_bulk` | `name` |
| DNS RRsets | `dns_zone_patch_rrsets_bulk` | `zone_name` |
| Domain (URL) forwards | `domain_forward_create_bulk`, `domain_forward_update_bulk`, `domain_forward_enable_bulk`, `domain_forward_disable_bulk`, `domain_forward_delete_bulk` | `hostname` |
| Email forwards | `email_forward_create_bulk`, `email_forward_update_bulk`, `email_forward_enable_bulk`, `email_forward_disable_bulk`, `email_forward_delete_bulk` | `hostname` |
The always-current list, including the Jobs commands that are deliberately not reachable this way and why, is on [Bulk templates](/mcp-server/tools/templates). A worked `template` body for each family is on [Recipes](/mcp-server/recipes).
## Choosing a template body
The `template` is the shared mutation, in the shape the Jobs command expects — `renewal_mode`, `nameservers`, `status_changes` or `contacts` for a domain update; `rrsets` and `dnssec_status` for a zone; `http`/`https` redirects for a URL forward; `aliases` for an email forward.
The **enable, disable and delete** commands carry no template of their own — there is nothing to configure, only a set to act on. The tool still requires the argument, so pass an empty object: `"template": {}`.
`dns_zone_patch_rrsets_bulk` is the other shape: its command has no shared template either, because the RRset operations belong to each zone. You still pass one `template` — put the `ops` in it — and the server writes them into every resolved instance alongside its `zone_name`. `bulk_preview` shows the result under `sampleInstances`.
## The selector
The selector is the [`GET /v1/domains`](/api-reference) filter set — the same object [`portfolio_query` uses](/mcp-server/tool-workflows#the-selector). Resolution pages the domain list server-side and sorts the result, so the same selector always produces the same batch and therefore the same approval.
An empty selector targets **every domain in your account**. The approval prompt says so in as many words — "matching the entire portfolio (no filters)". Read the prompt, not the intent.
## `hostnamePrefix`, for forward templates
Forward instances are addressed by hostname, built as `hostnamePrefix` plus the resolved domain. Pass `"*."` to target wildcard subdomain forwards (`*.acme-labs.com`), or leave it out for the apex (`acme-labs.com`).
The two are separate forwards, so covering both means running the operation twice. For a selector resolving to `acme-labs.com` and `acme-shop.com`:
| `hostnamePrefix` | Resolved instances |
| ---------------- | -------------------------------------------------------------------- |
| `""` (default) | `{"hostname": "acme-labs.com"}`, `{"hostname": "acme-shop.com"}` |
| `"*."` | `{"hostname": "*.acme-labs.com"}`, `{"hostname": "*.acme-shop.com"}` |
`bulk_preview` shows exactly this under `sampleInstances`, which is the cheapest way to be sure you are about to change the one you meant.
Supplying it for a template that is not hostname-addressed is rejected:
```plaintext
hostnamePrefix is only valid for hostname-addressed templates (*_forward_*_bulk); the "domain_update_bulk" template keys on "domain_id"
```
## Step 1 — preview
`bulk_preview` with:
```json
{
"templateType": "domain_update_bulk",
"template": { "status_changes": { "add": ["clientTransferProhibited"] } },
"selector": { "tld": ["com"], "expires_in_30_days": true },
"sampleSize": 3
}
```
returns:
```json
{
"status": "dry_run",
"templateType": "domain_update_bulk",
"command": "domain_update_bulk",
"matchedDomains": 412,
"template": { "status_changes": { "add": ["clientTransferProhibited"] } },
"sampleDomains": [
{ "name": "acme-labs.com", "domain_id": "domain_01h45ytscbebyvny4gc8cr8ma2" },
{ "name": "acme-labs.net", "domain_id": "domain_01h45yv2m8fbcwnz9pq3kr7txe" },
{ "name": "acme-shop.com", "domain_id": "domain_01h45yw7q2gdexpa4bt6mn8zvc" }
],
"sampleInstances": [
{ "domain_id": "domain_01h45ytscbebyvny4gc8cr8ma2" },
{ "domain_id": "domain_01h45yv2m8fbcwnz9pq3kr7txe" },
{ "domain_id": "domain_01h45yw7q2gdexpa4bt6mn8zvc" }
],
"note": "Nothing was submitted. Call bulk_submit with the same templateType, template and selector to execute. You will be asked to approve the action first."
}
```
`matchedDomains` is the full count; `sampleDomains` and `sampleInstances` are only the first few, `sampleSize` of them (10 by default).
`bulk_preview` submits nothing and needs no approval. Always preview first — the preview is what tells you the selector matched 412 domains rather than 4,127.
## Step 2 — submit
`bulk_submit` takes the same arguments, plus an optional `label`. The first call returns an approval challenge whose prompt names the command and the resolved set:
```plaintext
Approve: domain_update_bulk on 412 domain(s) matching expires_in_30_days=true, tld=["com"] (POST /v1/jobs)? Risk: writes data.
```
After you approve:
```json
{
"status": "ok",
"operationId": "create_batch_v1_jobs_post",
"httpStatus": 201,
"data": {
"batch_id": "batch_01k3n0m5xrf9pab6t2wqzhkvr3",
"total_commands": 1,
"jobs_created": 412,
"jobs_duplicated": 0,
"jobs_failed": 0,
"status_url": "/v1/jobs/batch_01k3n0m5xrf9pab6t2wqzhkvr3"
},
"truncated": false
}
```
`total_commands` is `1`: a batch built from a selector is **one** bulk command carrying every instance. `jobs_created` is the per-domain count.
### What the server posts
```json
{
"label": "Lock .com renewals expiring in 30 days",
"commands": [
{
"command": "domain_update_bulk",
"payload": {
"template": { "status_changes": { "add": ["clientTransferProhibited"] } },
"instances": [
{ "domain_id": "domain_01h45ytscbebyvny4gc8cr8ma2" },
{ "domain_id": "domain_01h45yv2m8fbcwnz9pq3kr7txe" }
]
}
}
]
}
```
## Limits
A batch is one command, and the Jobs API allows 1,000 instances per command, so **a selector may resolve to at most 1,000 domains**. To change more, narrow the selector and submit more than one batch — one TLD at a time, for example.
The errors you will meet:
| Message | Meaning |
| ---------------------------------------------------------------------------- | ------------------------------------------------------------------- |
| `selector matched no domains; nothing to submit…` | Filters too narrow, or `tag_ids` was given a label instead of an ID |
| `selector matched 1204 domains, exceeding the limit of 1000…` | Narrow the selector and submit in parts |
| `selector matched more than the limit of 1000 domains; narrow the selector…` | Same, detected while paging |
### Changing more than 1,000 domains
Split along a filter that partitions cleanly. One TLD at a time is the least surprising, because each half is easy to describe out loud and easy to check in the preview:
1. `bulk_preview` with `{"tld": ["com"], …}` → 812 matched → submit, approve, keep the `batch_id`.
2. `bulk_preview` with `{"tld": ["de"], …}` → 392 matched → submit, approve, keep the second `batch_id`.
Each half is its own approval and its own batch. Keep both ids: that is how you check and steer them afterwards.
## Step 3 — watch it
`job_batch_status` with `{ "batchId": "batch_01k3n0m5xrf9pab6t2wqzhkvr3" }` returns the batch's progress percentage and its job counts by state — `queued`, `running`, `succeeded`, `failed`, `dead_letter` and the rest. The lifecycle those states belong to is documented in [Jobs overview](/automation/jobs/overview) and [Managing batches](/automation/jobs/managing-batches).
## Step 4 — steer it
`job_batch_control` takes an `action`:
| `action` | Effect | Approval |
| -------- | --------------------------------------------------- | -------- |
| `pause` | Pause the eligible jobs | Yes |
| `resume` | Resume a paused batch | Yes |
| `retry` | Retry failed jobs, optionally only one `errorClass` | Yes |
| `cancel` | Cancel the jobs still queued | Yes |
`errorClass` is what makes `retry` useful: retry only the jobs that failed for one reason — say insufficient funds, after topping up — and leave failures with a different cause alone. It is a **list**, and omitting it retries every failed job in the batch:
```json
{
"batchId": "batch_01k3n0m5xrf9pab6t2wqzhkvr3",
"action": "retry",
"errorClass": ["BillingInsufficientFundsError"]
}
```
```json
{
"status": "ok",
"operationId": "retry_batch_v1_jobs__batch_id__retry_post",
"httpStatus": 200,
"data": {
"batch_id": "batch_01k3n0m5xrf9pab6t2wqzhkvr3",
"retried_count": 5,
"queued_count": 5,
"blocked_count": 0
},
"truncated": false
}
```
See [Managing batches](/automation/jobs/managing-batches).
The approval prompt for a pause reads:
```plaintext
Approve: pause job batch batch_01k3n0m5xrf9pab6t2wqzhkvr3 (POST /v1/jobs/{batch_id}/pause)? Risk: writes data.
```
Pause, resume and cancel answer `204 No Content`, so the tool result carries `"httpStatus": 204` and an empty `data`. That is success, not a truncated response. Retry is the exception: it answers `200` with `batch_id`, `retried_count`, `queued_count` and `blocked_count`, so you can see how many jobs it actually picked up.
A batch outlives the conversation. It runs inside OpusDNS Jobs, so closing your client neither pauses nor cancels it — reconnect later and ask for its status by `batch_id`.
## Related
* [Recipes](/mcp-server/recipes) — a worked template body per family
* [Bulk templates](/mcp-server/tools/templates)
* [Jobs overview](/automation/jobs/overview), [Domain commands](/automation/jobs/domain-commands), [Managing batches](/automation/jobs/managing-batches)
* [User tags](/automation/tags/user-tags) — resolving a tag label to its ID
* [Approvals and confirmations](/mcp-server/approvals)
# Data handling
Connecting an MCP client changes who sees your data. This page is what to hand whoever approves the connector.
## Where your data goes
```plaintext
your MCP client → api.opusdns.com/mcp → the OpusDNS API
← results, into the model's context
```
A tool result travels back into the context of the AI client you chose. From that point your **AI vendor's terms** govern what happens to it — how long it is retained, whether it is used for training, who at that vendor can see it. OpusDNS does not run the model, is not party to that relationship, and cannot control retention on the other side of it.
This is the choice that matters most, and it is yours rather than ours: which client you connect. Everything below is about the OpusDNS side of the line.
## What the agent can reach
Everything your own account can reach — and, on a call that carries [`organizationId`](/mcp-server/sub-organizations), everything the named sub-organization can. `call_operation` covers the whole API, so that includes the contact endpoints — **registrant names, postal addresses, phone numbers and email addresses can appear in a tool result**, and therefore in the model's context, whenever the agent reads a contact.
Two tools exist partly to keep that surface small:
* `portfolio_summary` answers "how big, what is expiring" with counts only.
* `portfolio_query` returns just the fields you name, so listing domains does not drag every attribute along with them.
Ask for the narrowest thing that answers the question, and expect an agent left to its own devices to read more than you would have.
If you are subject to the GDPR, treat the AI vendor as a processor of any registrant data your agent reads, and check that your own agreements cover it before connecting production. The [sandbox](/mcp-server) is a separate account with its own data, which is the place to try things out.
## What OpusDNS keeps
The MCP server is a thin layer in front of the API, and it is deliberately uninteresting as a store:
| | |
| --------------------- | ----------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- |
| Logged per request | The request line only — method, path, status code, duration, source address and a request ID |
| Not logged | Domain names, request bodies, response bodies, and the arguments you pass a tool — with one exception: the optional label you give a bulk submission is recorded, so a batch can be traced back |
| Kept between calls | Nothing about your domains. The one exception is an approval marker, so an approval cannot be used twice; it expires within minutes and carries no domain names and no request contents |
| Sent to third parties | Nothing. The server talks to the OpusDNS API, the OpusDNS identity provider, and its own store for the approval marker above — all OpusDNS infrastructure |
Calls the server makes on your behalf arrive at the OpusDNS API as ordinary API requests, and appear in your account's request history like any other client's.
## Sign-in
The client authenticates you with OAuth against the OpusDNS identity provider and holds the resulting credentials itself, on your machine. The MCP server never stores them, and it accepts no API keys. Ending that access is [Disconnecting](/mcp-server/connect/disconnect).
## Policies
Processing of personal data by OpusDNS is covered by the [OpusDNS privacy policy](https://www.opusdns.com/privacy-policy). Connecting the MCP server introduces no separate processor: the tools reach the same OpusDNS API your account already uses, with your own permissions.
## Related
* [Results and errors](/mcp-server/results) — what a tool hands back, and how much of it
* [Approvals and confirmations](/mcp-server/approvals) — what an agent may _do_, as against what it may see
* [Roles & permissions](/account/organizations/roles) — an MCP session inherits your own permissions, no more
* [Disconnecting](/mcp-server/connect/disconnect)
# MCP tools reference
This page and the three that follow are generated from the server's own tool
list, so the parameters below are exactly the ones the running server accepts.
If you are looking for worked examples rather than a parameter reference, start
with [Tool workflows](/mcp-server/tool-workflows).
## The nine tools
| Tool | What it does | Approval |
| --- | --- | --- |
| [`search_operations`](/mcp-server/tools/discovery#searchoperations) | Search OpusDNS API operations | No |
| [`describe_operation`](/mcp-server/tools/discovery#describeoperation) | Describe an OpusDNS API operation | No |
| [`call_operation`](/mcp-server/tools/discovery#calloperation) | Call an OpusDNS API operation | Depends on the operation |
| [`bulk_preview`](/mcp-server/tools/bulk#bulkpreview) | Preview a bulk domain operation | No |
| [`bulk_submit`](/mcp-server/tools/bulk#bulksubmit) | Submit a bulk domain operation | Yes |
| [`job_batch_status`](/mcp-server/tools/bulk#jobbatchstatus) | Get job batch status | No |
| [`job_batch_control`](/mcp-server/tools/bulk#jobbatchcontrol) | Control a job batch | Yes |
| [`portfolio_summary`](/mcp-server/tools/portfolio#portfoliosummary) | Summarize the domain portfolio | No |
| [`portfolio_query`](/mcp-server/tools/portfolio#portfolioquery) | Query the domain portfolio | No |
Every tool rejects arguments it does not declare.
## What the model is told
The server sends this text as its `instructions` when a client connects, so
it is what the model on the other end reads before it picks a tool. It is
reproduced verbatim.
```text
OpusDNS Domain API. No code execution.
Single operation: search_operations -> describe_operation -> call_operation.
A single exact search match inlines "detail", so describe_operation can be skipped.
Multi-domain mutations: always bulk_preview -> bulk_submit, never call_operation in a
loop. You pass a selector (the GET /v1/domains filter set) and one shared template;
domains are resolved server-side, so never transcribe domain names yourself. Track
submitted batches with job_batch_status and steer them with job_batch_control.
Portfolio reads: portfolio_summary for totals, portfolio_query for field-projected rows.
Sub-organizations: every tool acts on the signed-in account unless you pass
organizationId, which must name a sub-organization of it. Ask the user which one before
guessing, and keep it on every call of a sequence -- preview and submit that disagree
about it are two different actions.
Operations that write, cost money, or destroy resources require explicit user approval
before they run. This is enforced server-side, not by these instructions. If a call comes
back with status "confirmation_required", ask the user, then retry the SAME call with
confirmationToken added and nothing else changed -- a different selector, body or
organizationId is a different action and will be refused. "declined" means stop.
Reading a result: status "ok" is a 2xx, status "api_error" is a 4xx or 5xx from the
OpusDNS API and is a normal result carrying httpStatus and the API's problem detail in
data -- report it, do not retry blindly. status "error" means the call did not reach the
API; its "code" says why: invalid_request or unknown_operation mean fix the arguments,
authentication_required means sign in, upstream_timeout and upstream_unavailable are
transient and may be retried once after a pause. truncated true means the response was
cut off: narrow the request instead of repeating it.
```
The tool list carries a freshness hint of **15 minutes** (`ttlMs: 900000`), so a client
may cache it that long. The list is identical for every caller.
# Discovery tools
These three tools reach every operation in the OpusDNS API without putting a
tool per endpoint in the model's context. Search the catalog, read the call
details for the operation you picked, then call it.
A search that matches exactly one operation usually returns that operation's full
call details inline, so `describe_operation` can be skipped. Operations with a
very large request body are the exception — for those, and for any search with
more than one match, call `describe_operation` on the id you picked.
## search_operations
**Search OpusDNS API operations** — approval required: **no**
Search the OpusDNS API catalog. Returns compact entries (operationId, method, path, summary, safety), plus `total` (matches at the top relevance tier: total>count means results were capped, so refine the query). Read-only, no side effects. When exactly one operation matches, the response also carries `detail` with full call details, so you can call_operation directly without describe_operation; otherwise describe_operation the id you pick.
**When to use it.** Start here whenever you know what you want to do but not which endpoint does it.
Search by intent ("renew a domain", "add a DNS record"), not by path.
| Parameter | Type | Required | Description |
| --- | --- | --- | --- |
| `query` | string | **yes** | free-text query matched against operationId, path, summary, tags and description |
| `limit` | integer | no | maximum number of results (default 25) |
Unknown parameters are rejected.
- Read-only: never changes anything in your account.
- Repeating the same call has the same effect.
- Answered from the server's built-in API catalog; makes no network call.
**Example call.**
```json
{
"query": "renew domain",
"limit": 5
}
```
**Example result.**
```json
{
"count": 2,
"total": 2,
"results": [
{
"operationId": "renew_domain_v1_domains__domain_reference__renew_post",
"method": "POST",
"path": "/v1/domains/{domain_reference}/renew",
"tags": [
"domain"
],
"summary": "Renew a domain",
"safety": {
"read": false,
"write": true,
"cost": true,
"destructive": false
}
},
{
"operationId": "epp_check_domain_v1_domains_check_get",
"method": "GET",
"path": "/v1/domains/check",
"tags": [
"domain"
],
"summary": "Check domain availability and registration metadata",
"safety": {
"read": true,
"write": false,
"cost": false,
"destructive": false
}
}
]
}
```
## describe_operation
**Describe an OpusDNS API operation** — approval required: **no**
Return full call details for one operation: method, path, parameters, request-body schema, safety flags, and whether confirmation is required before calling. An unknown operationId is answered with status "not_found" as a normal result, not an error — search_operations for the right id rather than retrying this one.
**When to use it.** Use it when a search returned several candidates and you need the parameters and
request body of the one you picked. A single-match search already includes this,
so you can skip it there.
| Parameter | Type | Required | Description |
| --- | --- | --- | --- |
| `operationId` | string | **yes** | the operationId returned by search\_operations |
Unknown parameters are rejected.
- Read-only: never changes anything in your account.
- Repeating the same call has the same effect.
- Answered from the server's built-in API catalog; makes no network call.
**Example call.**
```json
{
"operationId": "renew_domain_v1_domains__domain_reference__renew_post"
}
```
**Example result.**
```json
{
"operation": {
"operationId": "renew_domain_v1_domains__domain_reference__renew_post",
"method": "POST",
"path": "/v1/domains/{domain_reference}/renew",
"tags": [
"domain"
],
"summary": "Renew a domain",
"description": "Extends the registration period of an existing domain.",
"safety": {
"read": false,
"write": true,
"cost": true,
"destructive": false
},
"parameters": [
{
"name": "domain_reference",
"in": "path",
"required": true,
"schema": {
"title": "Domain Reference",
"…": "a domain id or a domain name"
}
}
],
"requestBody": {
"required": true,
"contentTypes": [
"application/json"
],
"schema": {
"…": "the full request-body schema"
}
},
"responseContentTypes": [
"application/json"
]
},
"requiresConfirmation": true
}
```
## call_operation
**Call an OpusDNS API operation** — approval required: **depends on the operation**
Call one OpusDNS operation. Path parameters go in pathParams, query parameters in query, and the JSON body in body — never interpolate a value into the operationId. Write/cost/destructive operations require explicit user approval before they run; clients that support elicitation are asked directly, others receive a confirmation_required payload to approve and retry with the confirmationToken, changing nothing else. For multi-domain mutations use the bulk_* tools instead of looping this tool.
**When to use it.** For one operation on one resource. For the same change across many domains, use
`bulk_preview` and `bulk_submit` instead — looping this tool is slower, costs
more context, and asks for a separate approval every time.
| Parameter | Type | Required | Description |
| --- | --- | --- | --- |
| `operationId` | string | **yes** | the operationId to call |
| `body` | any (JSON) | no | JSON request body for write operations |
| `confirmationToken` | string | no | token from a prior confirmation\_required response, echoed back to execute the approved action. Omit on the first call |
| `organizationId` | string | no | act on this sub-organization instead of your own, e.g. organization\_01h45ytscbebyvny4gc8cr8ma2. It must be a sub-organization of the signed-in account; find its id with the organizations list operation |
| `pathParams` | object (any keys) | no | path parameter values keyed by name |
| `query` | object (any keys) | no | query parameter values keyed by name |
Unknown parameters are rejected.
- **Can modify or delete data, depending on what you call.** Anything that is not a read requires your explicit approval first.
- Repeating the call repeats the effect.
- Calls the OpusDNS API.
**Example call.**
```json
{
"operationId": "renew_domain_v1_domains__domain_reference__renew_post",
"pathParams": {
"domain_reference": "acme-labs.com"
},
"body": {
"period": {
"unit": "y",
"value": 1
},
"current_expiry_date": "2026-11-04T00:00:00Z"
}
}
```
**Example result.**
```json
{
"status": "ok",
"operationId": "renew_domain_v1_domains__domain_reference__renew_post",
"httpStatus": 200,
"headers": {
"content-type": "application/json",
"x-server-request-id": "8f3c2e10-1b4a-4c6b-9e77-2a91f5d0c4aa"
},
"data": {
"…": "the updated domain"
},
"truncated": false
}
```
# Bulk tools
Multi-domain changes go through [OpusDNS Jobs](/automation/jobs/overview), never
a loop of single calls. You supply a selector and one shared template; the
server resolves the matching domains and submits a single batch.
Always `bulk_preview` before `bulk_submit`: the preview is what tells you the
selector matched 412 domains rather than 4,127. See
[Bulk operations with Jobs](/mcp-server/bulk-operations) for the full flow.
## bulk_preview
**Preview a bulk domain operation** — approval required: **no**
Dry-run a bulk operation. Resolves the selector by reading the domain list from the OpusDNS API, then renders the planned Jobs template + instances and validates them against the Jobs schema, so a template bulk_submit would reject fails here instead of after the user approved it. It reads but never writes, so it needs the same credentials as any other call and no approval. Review matchedDomains, then call bulk_submit with the same arguments.
**When to use it.** Always run this first. It resolves the selector and shows you the matched count,
the shared template, and a sample of the instances that would be created —
without submitting anything or asking for approval.
| Parameter | Type | Required | Description |
| --- | --- | --- | --- |
| `templateType` | string | **yes** | bulk template type: domain\_update\_bulk; dns\_zone\_create\_bulk, dns\_zone\_update\_bulk, dns\_zone\_patch\_rrsets\_bulk; domain\_forward\_{create, update, enable, disable, delete}\_bulk; email\_forward\_{create, update, enable, disable, delete}\_bulk |
| `template` | object (any keys) | **yes** | shared mutation applied to every selected resource (the Jobs template body). Its fields depend on templateType: domain\_update\_bulk {renewal\_mode, nameservers, contacts, statuses, status\_changes}; dns\_zone\_create\_bulk and dns\_zone\_update\_bulk {dnssec\_status, rrsets}; dns\_zone\_patch\_rrsets\_bulk {ops} where each op is {op: upsert\|remove, rrset: {name, type, ttl, records}}, copied into every instance; domain\_forward\_create\_bulk {enabled, http, https, auto\_create\_zone}; domain\_forward\_update\_bulk {enabled (required), http, https}; email\_forward\_create\_bulk {aliases, enabled, auto\_create\_zone}; email\_forward\_update\_bulk {enabled (required), aliases}; the enable, disable and delete forward templates take no fields, pass {}. bulk\_preview validates this against the Jobs schema, so preview before you submit |
| `selector` | object (any keys) | **yes** | GET /v1/domains filters (e.g. tag\_ids, tld, search, expires\_in\_30\_days) used to resolve the target domains server-side. tag\_ids, tld and status\_tags take lists, e.g. tld: \["com", "org"\] |
| `hostnamePrefix` | string | no | forward templates only: prefix prepended to each resolved domain to form the instance hostname. Use '\*.' for a wildcard subdomain forward (\*.example.com), or '' (default) for the apex (example.com) |
| `organizationId` | string | no | act on this sub-organization instead of your own, e.g. organization\_01h45ytscbebyvny4gc8cr8ma2. It must be a sub-organization of the signed-in account; find its id with the organizations list operation |
| `sampleSize` | integer | no | how many resolved domains to include in the preview (default 10) |
Unknown parameters are rejected.
- Read-only: never changes anything in your account.
- Repeating the same call has the same effect.
- Calls the OpusDNS API.
**Example call.**
```json
{
"templateType": "domain_update_bulk",
"template": {
"status_changes": {
"add": [
"clientTransferProhibited"
]
}
},
"selector": {
"tld": [
"com"
],
"expires_in_30_days": true
},
"sampleSize": 3
}
```
**Example result.**
```json
{
"status": "dry_run",
"templateType": "domain_update_bulk",
"command": "domain_update_bulk",
"matchedDomains": 412,
"template": {
"status_changes": {
"add": [
"clientTransferProhibited"
]
}
},
"sampleDomains": [
{
"name": "acme-labs.com",
"domain_id": "domain_01h45ytscbebyvny4gc8cr8ma2"
},
{
"name": "acme-labs.net",
"domain_id": "domain_01h45yv2m8fbcwnz9pq3kr7txe"
},
{
"name": "acme-shop.com",
"domain_id": "domain_01h45yw7q2gdexpa4bt6mn8zvc"
}
],
"sampleInstances": [
{
"domain_id": "domain_01h45ytscbebyvny4gc8cr8ma2"
},
{
"domain_id": "domain_01h45yv2m8fbcwnz9pq3kr7txe"
},
{
"domain_id": "domain_01h45yw7q2gdexpa4bt6mn8zvc"
}
],
"note": "Nothing was submitted. Call bulk_submit with the same templateType, template and selector to execute. You will be asked to approve the action first."
}
```
## bulk_submit
**Submit a bulk domain operation** — approval required: **yes**
Submit a bulk operation as an OpusDNS Job. Resolves the selector to domains server-side, builds a Jobs template batch, and requires explicit user approval before it runs. The approval is bound to the exact resolved set: if the selector resolves differently on retry, you must confirm again.
**When to use it.** Run it with the same arguments you previewed. The approval you give is bound to
the exact set of domains that were resolved, so if that set changes before you
retry, you are asked again.
| Parameter | Type | Required | Description |
| --- | --- | --- | --- |
| `templateType` | string | **yes** | bulk template type; must match the bulk\_preview you reviewed: domain\_update\_bulk; dns\_zone\_create\_bulk, dns\_zone\_update\_bulk, dns\_zone\_patch\_rrsets\_bulk; domain\_forward\_{create, update, enable, disable, delete}\_bulk; email\_forward\_{create, update, enable, disable, delete}\_bulk |
| `template` | object (any keys) | **yes** | shared mutation applied to every selected resource (the Jobs template body). Its fields depend on templateType: domain\_update\_bulk {renewal\_mode, nameservers, contacts, statuses, status\_changes}; dns\_zone\_create\_bulk and dns\_zone\_update\_bulk {dnssec\_status, rrsets}; dns\_zone\_patch\_rrsets\_bulk {ops}, copied into every instance; domain\_forward\_create\_bulk {enabled, http, https, auto\_create\_zone}; domain\_forward\_update\_bulk {enabled (required), http, https}; email\_forward\_create\_bulk {aliases, enabled, auto\_create\_zone}; email\_forward\_update\_bulk {enabled (required), aliases}; the enable, disable and delete forward templates take no fields, pass {}. bulk\_preview validates this against the Jobs schema, so preview before you submit |
| `selector` | object (any keys) | **yes** | GET /v1/domains filters (e.g. tag\_ids, tld, search, expires\_in\_30\_days) used to resolve the target domains server-side. tag\_ids, tld and status\_tags take lists, e.g. tld: \["com", "org"\]. An empty selector targets every domain in the account |
| `confirmationToken` | string | no | token from a prior confirmation\_required response, echoed back to execute the approved action. Omit on the first call |
| `hostnamePrefix` | string | no | forward templates only: prefix prepended to each resolved domain to form the instance hostname. Use '\*.' for a wildcard subdomain forward, or '' (default) for the apex |
| `label` | string | no | human-readable batch label |
| `organizationId` | string | no | act on this sub-organization instead of your own, e.g. organization\_01h45ytscbebyvny4gc8cr8ma2. It must be a sub-organization of the signed-in account; find its id with the organizations list operation |
Unknown parameters are rejected.
- **Can modify or delete data.** Requires your explicit approval before it runs.
- Repeating the call repeats the effect.
- Calls the OpusDNS API.
**Example call.**
```json
{
"templateType": "domain_update_bulk",
"template": {
"status_changes": {
"add": [
"clientTransferProhibited"
]
}
},
"selector": {
"tld": [
"com"
],
"expires_in_30_days": true
},
"label": "lock-expiring-com"
}
```
**Example result.**
```json
{
"status": "ok",
"operationId": "create_batch_v1_jobs_post",
"httpStatus": 201,
"headers": {
"content-type": "application/json"
},
"data": {
"batch_id": "batch_01k3n0m5xrf9pab6t2wqzhkvr3",
"jobs_created": 412,
"jobs_failed": 0,
"jobs_duplicated": 0,
"duplicates": [],
"errors": [],
"total_commands": 1,
"status_url": "/v1/jobs/batch_01k3n0m5xrf9pab6t2wqzhkvr3"
},
"truncated": false
}
```
## job_batch_status
**Get job batch status** — approval required: **no**
Get the status of a submitted job batch: progress percentage and counts by job state (queued, running, succeeded, failed, dead_letter, ...).
**When to use it.** Poll this after `bulk_submit` to watch a batch progress. Counts are per job
state, so a partly-failed batch is visible without listing every job.
| Parameter | Type | Required | Description |
| --- | --- | --- | --- |
| `batchId` | string | **yes** | batch id returned by bulk\_submit, e.g. batch\_01k3n0m5xrf9pab6t2wqzhkvr3 |
| `organizationId` | string | no | act on this sub-organization instead of your own, e.g. organization\_01h45ytscbebyvny4gc8cr8ma2. It must be a sub-organization of the signed-in account; find its id with the organizations list operation |
Unknown parameters are rejected.
- Read-only: never changes anything in your account.
- Repeating the same call has the same effect.
- Calls the OpusDNS API.
**Example call.**
```json
{
"batchId": "batch_01k3n0m5xrf9pab6t2wqzhkvr3"
}
```
**Example result.**
```json
{
"status": "ok",
"operationId": "get_batch_v1_jobs__batch_id__get",
"httpStatus": 200,
"headers": {
"content-type": "application/json"
},
"data": {
"batch_id": "batch_01k3n0m5xrf9pab6t2wqzhkvr3",
"label": "lock-expiring-com",
"total": 412,
"queued": 0,
"running": 6,
"succeeded": 401,
"failed": 5,
"blocked": 0,
"paused": 0,
"canceled": 0,
"dead_letter": 0,
"progress_percentage": 98
},
"truncated": false
}
```
## job_batch_control
**Control a job batch** — approval required: **yes**
Control a submitted job batch: pause, resume, retry (optionally only a given errorClass), or cancel queued jobs. These are write operations and require explicit user approval before they run.
**When to use it.** Steer a batch that is already running: pause it, resume it, cancel the jobs still
queued, or retry the failures. `retry` with an `errorClass` retries only the jobs
that failed that way — useful after fixing one cause and leaving the rest alone.
| Parameter | Type | Required | Description |
| --- | --- | --- | --- |
| `batchId` | string | **yes** | batch id returned by bulk\_submit, e.g. batch\_01k3n0m5xrf9pab6t2wqzhkvr3 |
| `action` | string | **yes** | one of pause, resume, retry, cancel |
| `confirmationToken` | string | no | token from a prior confirmation\_required response, echoed back to execute the approved action. Omit on the first call |
| `errorClass` | array of string | no | for retry: only retry jobs whose error\_class is one of these, e.g. \["BillingInsufficientFundsError"\]. Omit to retry every failed job in the batch |
| `organizationId` | string | no | act on this sub-organization instead of your own, e.g. organization\_01h45ytscbebyvny4gc8cr8ma2. It must be a sub-organization of the signed-in account; find its id with the organizations list operation |
Unknown parameters are rejected.
- **Can modify or delete data.** Requires your explicit approval before it runs.
- Repeating the call repeats the effect.
- Calls the OpusDNS API.
**Example call.**
```json
{
"batchId": "batch_01k3n0m5xrf9pab6t2wqzhkvr3",
"action": "retry",
"errorClass": [
"BillingInsufficientFundsError"
]
}
```
**Example result.**
```json
{
"status": "ok",
"operationId": "retry_batch_v1_jobs__batch_id__retry_post",
"httpStatus": 200,
"headers": {
"content-type": "application/json"
},
"data": {
"batch_id": "batch_01k3n0m5xrf9pab6t2wqzhkvr3",
"retried_count": 5,
"queued_count": 5,
"blocked_count": 0
},
"truncated": false
}
```
# Portfolio tools
Two reads shaped for large portfolios. `portfolio_summary` is a single small
payload of totals and breakdowns; `portfolio_query` lists domains but projects
only the fields you ask for, so a few thousand domains do not flood the model's
context.
## portfolio_summary
**Summarize the domain portfolio** — approval required: **no**
Return the account domain summary: total counts and breakdowns by status, TLD, and expiry window. Tiny payload — use this before listing individual domains.
**When to use it.** The cheapest way to answer "how many domains do I have, and what is expiring".
Call it before listing individual domains.
| Parameter | Type | Required | Description |
| --- | --- | --- | --- |
| `organizationId` | string | no | act on this sub-organization instead of your own, e.g. organization\_01h45ytscbebyvny4gc8cr8ma2. It must be a sub-organization of the signed-in account; find its id with the organizations list operation |
Unknown parameters are rejected.
- Read-only: never changes anything in your account.
- Repeating the same call has the same effect.
- Calls the OpusDNS API.
**Example call.**
```json
{}
```
**Example result.**
```json
{
"status": "ok",
"operationId": "get_domain_summary_v1_domains_summary_get",
"httpStatus": 200,
"headers": {
"content-type": "application/json"
},
"data": {
"organization_id": "organization_01h45ytscbebyvny4gc8cr8ma2",
"domains": {
"total_count": 1284,
"by_status": {
"ok": 1275,
"pendingDelete": 9
},
"by_tld": {
"com": 612,
"de": 388,
"net": 154,
"org": 92,
"io": 38
},
"by_organization": {
"Acme Labs": 1284
},
"expiring_soon": {
"next_30_days": 41,
"next_60_days": 96,
"next_90_days": 155
}
}
},
"truncated": false
}
```
## portfolio_query
**Query the domain portfolio** — approval required: **no**
List domains matching a selector, projecting only the requested fields so large portfolios do not flood the context. Returns projected results plus pagination metadata.
**When to use it.** Use it instead of `call_operation` on the domains endpoint whenever you only need
a few fields per domain. Ask for the narrowest field list that answers the
question.
| Parameter | Type | Required | Description |
| --- | --- | --- | --- |
| `fields` | array of string | no | which domain fields of the domain record to project (default: name, domain\_id, expires\_on, renewal\_mode, status\_tags). Any field of the domain record can be named, so ask for the ones the question needs — e.g. is\_premium, transfer\_lock, registry\_statuses, tags, nameservers, sld, tld, renewal\_price, created\_on, registered\_on. A field the record does not carry is dropped silently rather than reported |
| `organizationId` | string | no | act on this sub-organization instead of your own, e.g. organization\_01h45ytscbebyvny4gc8cr8ma2. It must be a sub-organization of the signed-in account; find its id with the organizations list operation |
| `page` | integer | no | 1-based page number (default 1) |
| `pageSize` | integer | no | results per page (capped server-side) |
| `selector` | object (any keys) | no | GET /v1/domains filters (tag\_ids, tld, search, expires\_in\_30\_days, ...). tag\_ids takes tag IDs like tag\_01..., NOT labels — resolve a label to its ID via the /v1/tags list operation first. tag\_ids, tld and status\_tags take lists, e.g. tld: \["com", "org"\] |
Unknown parameters are rejected.
- Read-only: never changes anything in your account.
- Repeating the same call has the same effect.
- Calls the OpusDNS API.
**Example call.**
```json
{
"selector": {
"tld": [
"com"
],
"expires_in_30_days": true
},
"fields": [
"name",
"expires_on",
"renewal_mode"
],
"pageSize": 3
}
```
**Example result.**
```json
{
"status": "ok",
"fields": [
"name",
"expires_on",
"renewal_mode"
],
"results": [
{
"name": "acme-labs.com",
"expires_on": "2026-09-03T21:25:00Z",
"renewal_mode": "expire"
},
{
"name": "acme-shop.com",
"expires_on": "2026-09-11T08:00:00Z",
"renewal_mode": "renew"
},
{
"name": "spring-sale-2026.com",
"expires_on": "2026-09-18T12:30:00Z",
"renewal_mode": "renew"
}
],
"pagination": {
"current_page": 1,
"page_size": 3,
"total_items": 41,
"total_pages": 14,
"has_next_page": true,
"has_previous_page": false
}
}
```
# Bulk templates
A bulk template is the shared mutation `bulk_preview` and `bulk_submit` apply to
every domain a selector resolves to. The `templateType` decides which Jobs
command runs and how each instance is addressed — by domain ID, by zone name, or
by hostname.
## Supported templates
The `templateType` is also the name of the Jobs command it runs.
| `templateType` | Instances addressed by |
| --- | --- |
| `domain_update_bulk` | `domain_id` |
| `dns_zone_create_bulk` | `name` |
| `dns_zone_patch_rrsets_bulk` | `zone_name` |
| `dns_zone_update_bulk` | `name` |
| `domain_forward_create_bulk` | `hostname` |
| `domain_forward_delete_bulk` | `hostname` |
| `domain_forward_disable_bulk` | `hostname` |
| `domain_forward_enable_bulk` | `hostname` |
| `domain_forward_update_bulk` | `hostname` |
| `email_forward_create_bulk` | `hostname` |
| `email_forward_delete_bulk` | `hostname` |
| `email_forward_disable_bulk` | `hostname` |
| `email_forward_enable_bulk` | `hostname` |
| `email_forward_update_bulk` | `hostname` |
## Not available through the bulk tools
The Jobs API accepts more bulk commands than these tools expose. They remain
reachable by calling the API directly — see
[Domain commands](/automation/jobs/domain-commands) — but not through a
selector, for the reasons below.
| Jobs command | Why not |
| --- | --- |
| `contact_create_bulk` | creates contacts, not domain-addressed, so there is nothing for a domain selector to resolve |
| `dns_zone_patch_records_bulk` | superseded for MCP callers by dns\_zone\_patch\_rrsets\_bulk, which patches whole RRsets |
| `dns_zone_restamp_vanity_ns_bulk` | vanity-nameserver restamping is an infrastructure operation, not a portfolio-wide edit |
| `domain_create_bulk` | registers new domains, which the selector cannot name (it only resolves domains you already hold) and which is cost-bearing per name |
| `domain_transfer_bulk` | transfers in domains held elsewhere, which the selector cannot name, and needs a per-domain auth code |
| `parking_create_bulk` | parking is not exposed through the MCP tools yet |
| `parking_delete_bulk` | parking is not exposed through the MCP tools yet |
| `parking_disable_bulk` | parking is not exposed through the MCP tools yet |
| `parking_enable_bulk` | parking is not exposed through the MCP tools yet |
# Results and errors
Every tool hands back JSON, twice over: once as a text block and once as `structuredContent`, with the same content. Your client may render either. This page is the reference for the shapes; if you have a symptom rather than a shape, start at [Troubleshooting](/mcp-server/troubleshooting).
## The seven result shapes
| `status` | What it means | Did anything run? |
| ----------------------- | ----------------------------------------------------- | ------------------------- |
| `ok` | The OpusDNS API answered 2xx or 3xx | Yes |
| `api_error` | The OpusDNS API answered 4xx or 5xx | The call reached the API |
| `error` | The MCP server refused the call | No |
| `dry_run` | A `bulk_preview` result | No — nothing is submitted |
| `confirmation_required` | A gated action is waiting for your approval | No |
| `declined` | You declined a gated action | No |
| `not_found` | `describe_operation` does not know that `operationId` | Nothing to run |
A client on protocol revision `2026-07-28` that supports elicitation sees a `resultType` of `input_required` instead of the `confirmation_required` payload — the same approval, asked in the client's own UI. See [Approvals and confirmations](/mcp-server/approvals).
## A successful call
```json
{
"status": "ok",
"operationId": "renew_domain_v1_domains__domain_reference__renew_post",
"httpStatus": 200,
"headers": {
"content-type": "application/json",
"x-server-request-id": "8f3c2e10-1b4a-4c6b-9e77-2a91f5d0c4aa"
},
"data": { "…": "whatever the operation returns" },
"truncated": false
}
```
`headers` is a deliberately short allow-list — `content-type`, `x-request-id`, `x-server-request-id` and `retry-after`, and nothing else.
`headers["x-server-request-id"]` is the one value worth keeping. It identifies the request inside OpusDNS, and quoting it is the fastest way to get a support answer.
`portfolio_query` is the one read that replaces this envelope with its own projection — `status`, `fields`, `results` and `pagination` — because returning whole domain objects is exactly what it exists to avoid. If the page could not be read whole, it hands back the envelope above instead, so `truncated: true` stays visible rather than looking like an empty result.
## An error from the API
An HTTP error from OpusDNS is a **normal tool result**, not a protocol failure. The status code and the API's own problem detail come back intact:
```json
{
"status": "api_error",
"operationId": "renew_domain_v1_domains__domain_reference__renew_post",
"httpStatus": 402,
"headers": { "content-type": "application/problem+json" },
"data": { "detail": "Insufficient funds in wallet" },
"truncated": false
}
```
Read `data` before retrying. A 402, a 409 and a 422 all mean something specific and none of them is fixed by calling again.
Rate limiting arrives the same way: `httpStatus` 429, with `headers["retry-after"]` carrying the number of seconds the API asks you to wait.
## An error from the server
When the MCP server refuses a call before it reaches the API, the result carries a machine-readable `code` beside the message, and the client marks it as an error:
```json
{
"status": "error",
"code": "invalid_request",
"message": "unknown templateType \"domain_renew_bulk\"; allowed: dns_zone_create_bulk, dns_zone_patch_rrsets_bulk, …"
}
```
| `code` | Meaning | What to do |
| ------------------------- | -------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------------- | -------------------------------------------------- |
| `invalid_request` | The arguments do not match the operation — a missing required field, a wrong type, a query or path parameter the operation does not declare (a misspelled selector filter), an unknown `templateType` or `action`, a selector that matched nothing or too much | Fix the arguments. Retrying unchanged fails again |
| `unknown_operation` | No operation in the catalog has that `operationId` | `search_operations` for the right id |
| `authentication_required` | No usable credentials for an API call | Sign in again |
| `upstream_timeout` | The OpusDNS API did not answer in time | Retry once; if it persists, check status |
| `upstream_unavailable` | The OpusDNS API could not be reached, or its response broke off before it was complete | Retry with backoff |
| `request_canceled` | The client gave up on the call before the API answered | Nothing to do; call again if it is still wanted |
| `selector_page_truncated` | One page of the domain list was too large for the response cap while resolving a bulk selector, so the selection could not be resolved completely | Narrow the selector, for example one TLD at a time |
| `tool_error` | Anything else the tool itself rejected | Read the message |
There is no `forbidden` code. Authorization is decided by the OpusDNS API against your account's roles, so a refusal arrives as `api_error` with `httpStatus: 403` and the API's own explanation — not as a server error invented here.
## Endpoint-level errors
These come back as HTTP responses on `/mcp` rather than as tool results, so your client usually surfaces them as a connection problem.
| Response | Body | Meaning |
| ------------------------ | ------------------------------------------------------------------------------------- | -------------------------------------------------------------------- |
| `401` | `{"error":"authentication_required"}` | No credentials were sent |
| `401` | `{"error":"invalid_token","error_description":"Bearer token could not be validated"}` | The token is expired, for the wrong realm, or has the wrong audience |
| `503` + `Retry-After: 1` | `{"error":"too_many_requests","error_description":"Server is busy, retry shortly."}` | The server instance is at its in-flight request cap |
A `401` always carries a `WWW-Authenticate` header pointing at the protected-resource metadata, which is how a client knows where to sign in. See [OAuth details](/mcp-server/connect/oauth).
## When a result is truncated
```json
{ "status": "ok", "truncated": true, "data": "…" }
```
Responses are capped so a single call cannot flood the model's context. Past the cap the body is cut and `truncated` is set — and because the cut lands mid-document, `data` is then a **string**, not parsed JSON.
Do not retry the same call: it will be cut in the same place. Ask for less instead — a narrower filter, a smaller page, or `portfolio_query` with an explicit `fields` list rather than a full domain listing.
## Related
* [Troubleshooting](/mcp-server/troubleshooting) — the same failures, keyed by symptom
* [Approvals and confirmations](/mcp-server/approvals)
* [Tool workflows](/mcp-server/tool-workflows)
# Troubleshooting
Symptom first, in the words the server actually uses. Looking for a shape rather
than a symptom — what `api_error` means, which `code` values exist, what a
truncated result looks like — see
[Results and errors](/mcp-server/results).
## Connecting
### The host cannot be resolved
You used `mcp.opusdns.com`. There is no such host. The endpoint is
`https://api.opusdns.com/mcp`.
### `401` with `{"error":"authentication_required"}`
No bearer token was sent, or you sent an `X-Api-Key`. API keys are not accepted
by the MCP endpoint — complete the OAuth sign-in instead. In Claude Code that is
`/mcp`, or `claude mcp login `. See
[OAuth details](/mcp-server/connect/oauth).
### `401` with `{"error":"invalid_token","error_description":"Bearer token could not be validated"}`
The token was rejected. The usual causes, in order of likelihood: it expired; it
was minted for the wrong realm (a sandbox token against production, or the
reverse); or it lacks the required audience because the `opusdns:mcp` scope was
not requested. Sign out and back in.
### `invalid_scope` during sign-in
Your client asked the authorization server for a scope it was not registered
with. This is the case the resource metadata is deliberately shaped to avoid —
see [Why `offline_access` is
advertised](/mcp-server/connect/oauth#why-offline-access-is-advertised).
### The server never appears in my client
Check the wrapper key and the transport type. VS Code nests servers under
`servers`; Claude Code and Cursor use `mcpServers`. In Claude Code and VS Code an
entry with a `url` and no `"type": "http"` is read as a local command and
skipped. See [Connect Cursor, VS Code, and
ChatGPT](/mcp-server/connect/editors).
### ChatGPT signed in but reports no tools
Developer mode is off, or your plan does not offer it. Without it ChatGPT
surfaces only tools named `search` and `fetch`, and this server exposes neither,
so a connector whose OAuth flow succeeded still looks empty. Developer mode is a
paid-plan feature on the web and does not exist on the free plan — an OpenAI
limitation, not something the server can work around. See
[ChatGPT](/mcp-server/connect/editors#chatgpt).
### `403` from a tool call
Authentication worked; your organization role does not permit that operation.
Approval is not authorization — see [Roles &
permissions](/account/organizations/roles).
### `503` with `Retry-After: 1`
```json
{ "error": "too_many_requests", "error_description": "Server is busy, retry shortly." }
```
The concurrency cap. It counts requests in flight on one server instance across
all callers, not just yours, so it can trip because the service is busy rather
than because of anything you did. Retry after a second.
### I removed the connector but the agent still has access
Removing the server from one client does not invalidate a token another client
already holds, and a `mcp-remote` bridge keeps its own copy on disk. See
[Disconnecting](/mcp-server/connect/disconnect) for what each step stops and
how to cut access off outright.
## Approvals
### Approval keeps being requested
One of:
- The retried call was not byte-identical. The approval binds the path
parameters, the query and the body.
- A bulk selector resolved to a different set of domains than when you approved.
Preview again and approve the new set.
- More than about five minutes elapsed.
- The token had already been used. Each one works once.
- You signed in again, or a different client is doing the retry. The approval
binds the user, the client and the granted scopes.
### The agent says the action was declined
`{"status":"declined"}` means the prompt was declined or dismissed. Nothing ran,
and the token was not consumed — you can still approve the same action until it
expires.
### My client never shows an approval prompt
It is on the text path, and it should be showing you the
`confirmation_required` payload before it retries. If it retries silently, that
is a client behaviour to raise with the client's vendor: the server can verify
that a token matches an action, but not that a human saw it. See [Path
B](/mcp-server/approvals#path-b-the-confirmation-payload).
### I approved it and nothing happened
The approval reached your client but the retry never left it. Nothing was
consumed, so simply ask again. If it repeats with one particular client, that is
a client bug worth reporting — the server cannot retry on its behalf.
## Using the tools
### The agent called one operation per domain instead of one batch
Say so: *"do that as one bulk operation, not one call per domain"*. A loop of
`call_operation` costs an approval per domain and is exactly what
[the bulk tools](/mcp-server/bulk-operations) exist to replace.
### The agent acted on the wrong organization
`organizationId` applies to a **single call**, never to a session. Every call in
a sequence needs it, and a preview and a submit that disagree about it are two
different actions. See [Sub-organizations](/mcp-server/sub-organizations).
### A new tool or a changed parameter is not showing up
Tool lists are cacheable for about fifteen minutes. Reconnect the server in your
client to force a fresh `tools/list`.
### A filter worked but `status_tags` came back `null`
The domain list only populates `tags` and `status_tags` when the request asks
for them. Add `"include": ["tags"]` to the selector.
## Bulk
| Symptom | Cause |
| --- | --- |
| `selector matched no domains; nothing to submit…` | Filters too narrow — or `tag_ids` was given a tag label instead of a tag ID |
| `selector matched 1204 domains, exceeding the limit of 1000…` | One batch is one command, and a command holds 1,000 instances. Narrow the selector and submit in parts |
| `unknown templateType "..."` | The error lists the allowed values. See [Bulk templates](/mcp-server/tools/templates) |
| `hostnamePrefix is only valid for hostname-addressed templates…` | Only the forward templates take a prefix |
| `Invalid query parameter "error_class"` | `errorClass` is a list — `["BillingInsufficientFundsError"]`, not a bare string |
| `"httpStatus": 204` with empty `data` | Success. Pause, resume and cancel return no content |
## Results
### `"truncated": true`
The API response exceeded the per-call size limit and was cut short. Narrow the
request — for `portfolio_query`, ask for fewer `fields` or a smaller `pageSize`.
### `"status": "api_error"`
A normal HTTP error from the OpusDNS API, not a protocol failure. `httpStatus`
carries the status and `data` carries the API's problem detail.
### My client sends numbers as strings and it still works
It does. Common client serialisation quirks — a page number as `"2"`, a list as a
JSON string — are repaired before the request is validated. You do not need to
work around it.
## Getting help
Send an `X-Request-Id` header on your requests and it is echoed back. Results
that came from an OpusDNS API call — anything with an `httpStatus` — also carry
`headers["x-server-request-id"]`, the API's own request ID, when the API sent
one. Quote whichever you have when you contact
[support](https://support.opusdns.com/), and check
[status.opusdns.com](https://status.opusdns.com/) first for anything that looks
like an outage.
# FAQ
Short answers. Each one links to the page that has the detail.
## Getting connected
**Do I need an API key?**
No. The MCP endpoint uses OAuth in your browser and does not accept API keys.
API keys are for direct HTTP calls. See
[Connect your client](/mcp-server/connect).
**Which clients work?**
Anything that speaks remote Streamable HTTP: Claude Code, Claude desktop and
web, Cursor, VS Code, ChatGPT, the OpenAI Responses API. Clients that only speak
stdio need a bridge. ChatGPT is the one exception worth knowing before you
start: it only shows the tools in developer mode, which OpenAI does not offer on
the free plan. See
[Cursor, VS Code, and ChatGPT](/mcp-server/connect/editors).
**Is there a sandbox?**
Yes — `https://sandbox.opusdns.com/mcp`. Separate account, separate sign-in,
free, and fully isolated from production. Start there.
**Is there an `mcp.opusdns.com`?**
No. That hostname does not resolve. The endpoint lives on the API host:
`https://api.opusdns.com/mcp`.
**Does it cost anything to connect?**
No. Registrations, renewals and transfers cost what they always cost; the
connection itself does not.
## What it can do
**Can the model delete or transfer my domains without asking?**
No. Every write, every cost-bearing operation and every deletion or transfer is
blocked before it reaches the OpusDNS API and needs your explicit approval. The
gate is enforced by the server, not by instructions to the model, so a model
cannot talk its way past it. See
[Approvals and confirmations](/mcp-server/approvals).
**How do I know which tools only read?**
Each tool is annotated, and your client shows it. Six of the nine are read-only;
`call_operation`, `bulk_submit` and `job_batch_control` are the three that can
change things. The full list is in the
[Tools reference](/mcp-server/tools).
**How many domains can one bulk change touch?**
1,000. That is the Jobs limit on instances in a single command, and a batch
built from a selector is one command. Split the selector and submit more than
one batch. See [Recipes](/mcp-server/recipes).
**Can it act on my customer's organization?**
Yes, if that organization is below yours. Pass `organizationId` on every call.
It confers no reach your own credentials did not already have. See
[Sub-organizations](/mcp-server/sub-organizations).
**Does it support prompts, resources or sampling?**
No. The server declares tools only.
## While it is working
**Why is it asking me to approve the same thing twice?**
Because the action changed between the two attempts. The approval is bound to
the exact action — including the resolved list of domains for a bulk operation —
so a selector that now matches a different set is a different action. It is also
what happens when an approval expires. See
[Approvals and confirmations](/mcp-server/approvals).
**What happens to a running batch if I close the conversation?**
Nothing. The batch runs inside OpusDNS Jobs and finishes on its own. Reconnect
later and ask for its status by `batch_id`, or steer it from the
[dashboard](/automation/jobs/managing-batches).
**A result came back marked `"truncated": true`. Now what?**
Ask for less — a narrower filter or fewer fields. Retrying the same call cuts it
in the same place. See [Results and errors](/mcp-server/results).
## Data and access
**Does OpusDNS see my prompts?**
No. OpusDNS sees the tool calls your client makes, not the conversation around
them. What your AI provider sees is between you and them. See
[Data handling](/mcp-server/data-handling).
**How do I cut off access?**
Removing the connector stops your client from calling. Signing out invalidates
the session. Disabling the account is the immediate, complete answer. See
[Disconnecting](/mcp-server/connect/disconnect).
**Should I use this or the REST API?**
MCP for interactive work with a person in the loop; the API for unattended
automation, because the approval gate is not optional here. See
[MCP or the REST API?](/mcp-server/mcp-or-api).